
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/happy0717/cve-2023-27703
Android SecurityVulnerability AnalysisWeb Application ExploitationInformation GatheringMobile Security
GitHubhappy0717/cve-2023-27703

CVE-2023-27703

CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability

View Repository
3373 years agoNot yet reviewed
Share

CVE-2023-27703

CVE-2023-27703 An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability

fix at pikpak 1.30.1

[Suggested description] The Android version of pikpak v1.29.2 was discovered to contain an information leak via the debug interface.


[Additional Information] Details link:https://drive.google.com/drive/folders/1Szu9pjivVtG93ceECvnoAjeSABVyfDES?usp=sharing


[Vulnerability Type] Incorrect Access Control


[Vendor of Product] https://mypikpak.com/


[Affected Product Code Base] Android version of pikpak - V1.29.2


[Affected Component] An Android version of pikpak version V1.29.2 element debugging interface leakage vulnerability, which can lead to js code execution(XSS) and information leakage


[Attack Type] Local


[Impact Information Disclosure] true


[Attack Vectors] Details link:https://drive.google.com/drive/folders/1Szu9pjivVtG93ceECvnoAjeSABVyfDES?usp=sharing

a bug in the android version of pikpak,is about element debugging interface leakage vulnerability, which can lead to js code execution and information leakage. The version I am using is:V1.29.2

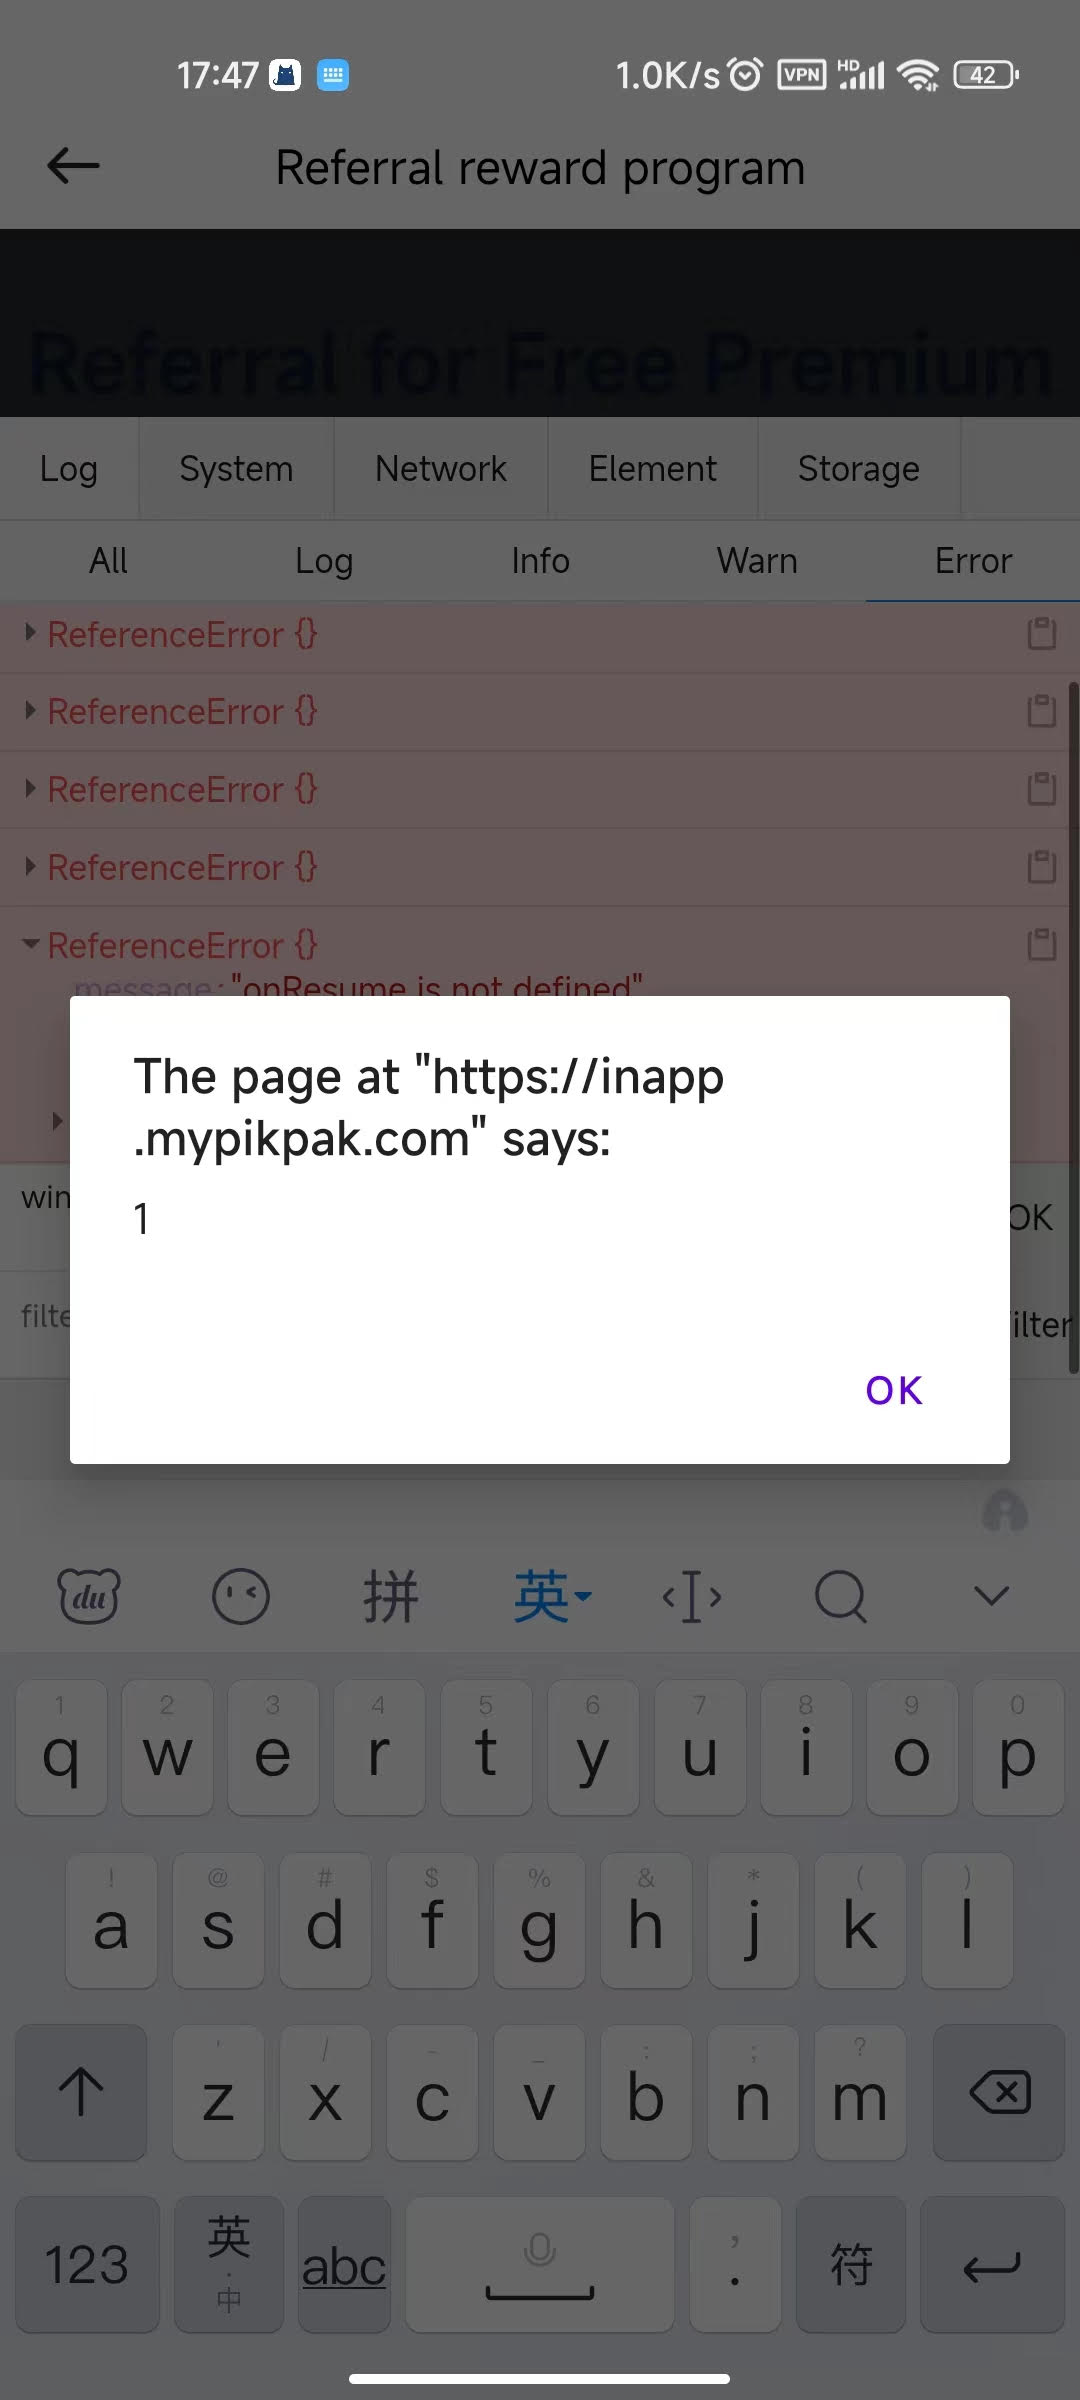
The trigger point of the vulnerability is at enter the invitation code to redeem premium,Enter an error code at will, and then click the redeem now button continuously,need to continue clicking after prompt too many attempts please try again 24 hours.Then vConsole will pop up at the bottom right of the page.
image

I think this problem is caused by entering the wrong code many times,you can see some error messages in the log.

I think the appearance of vConsole is very dangerous,It can lead to user information leakage, network request interface debugging, element code leakage, user information changes, etc.


[Reference] https://drive.google.com/drive/folders/1Szu9pjivVtG93ceECvnoAjeSABVyfDES?usp=sharing


[Discoverer] happy0717

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    640
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    479
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    391
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    335
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    249

Explore all tools

Browse our collection of tools

View all tools →





