
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-46169 — Cacti: Unauthenticated Remote Code Execution Exploit in Ruby | Kitploit

Tools/GitHubGitHub/habib0x0/cve-2022-46169
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthenticationRemote Access Tool
GitHubhabib0x0/cve-2022-46169

CVE-2022-46169

Cacti: Unauthenticated Remote Code Execution Exploit in Ruby
View Repository
1283 years agoNot yet reviewed
Share

Cacti | Auth Bypass | RCE | CVE-2022-46169

Cacti: Unauthenticated Remote Code Execution Exploit in Ruby

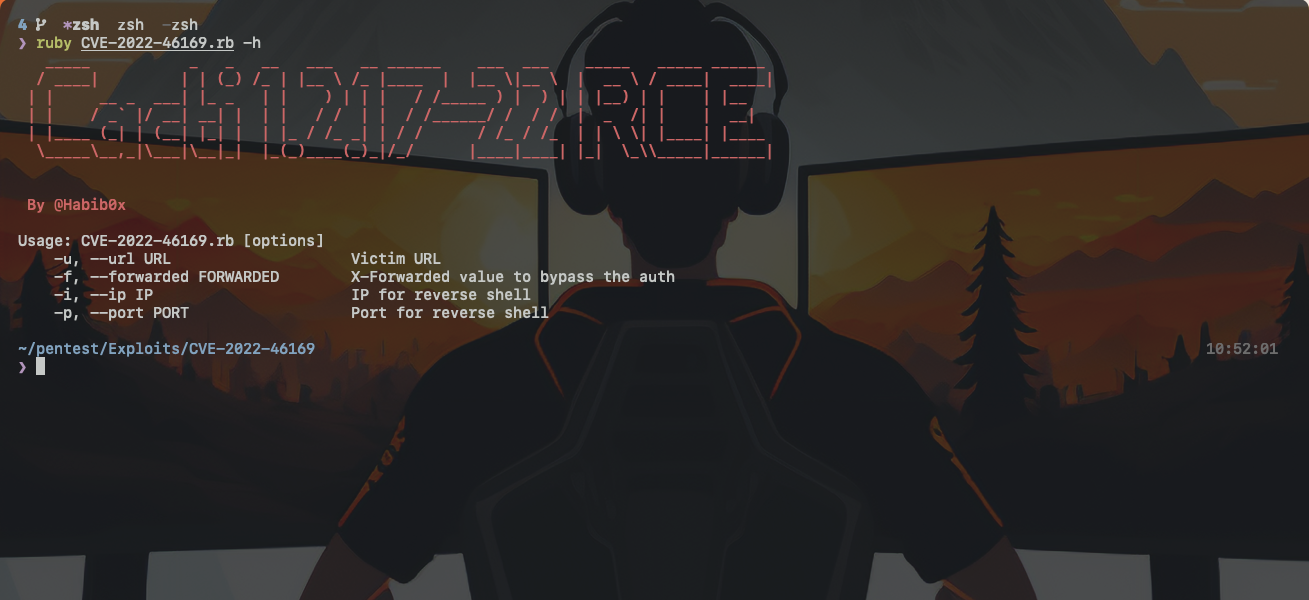
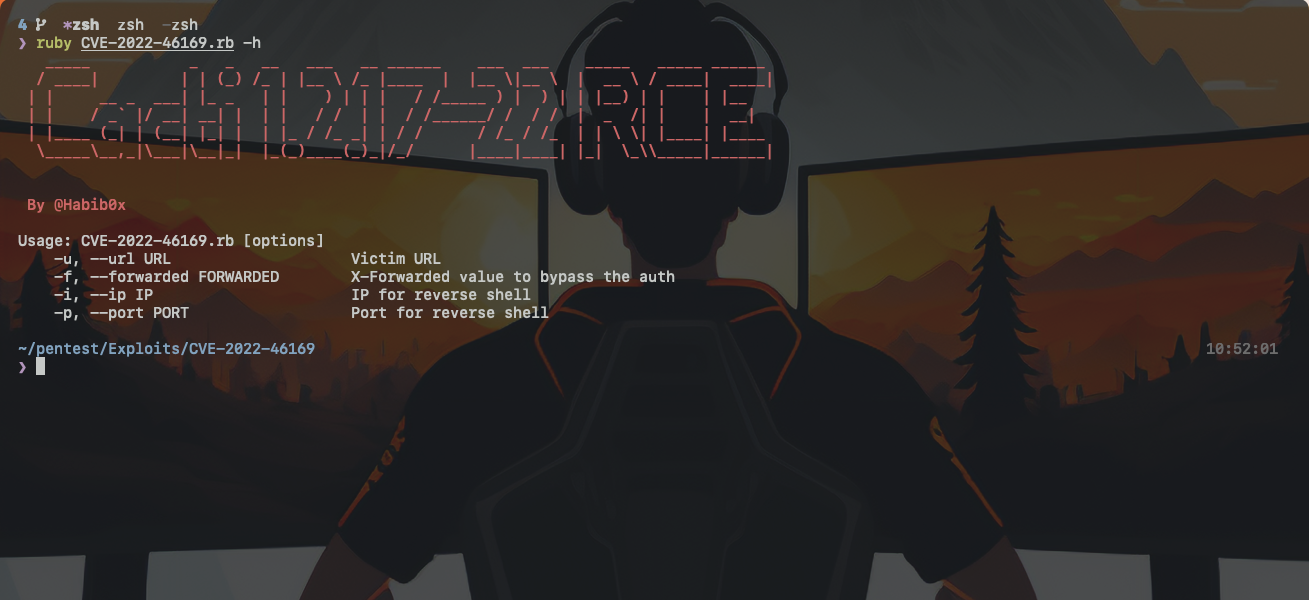
Screenshot 2023-01-16 at 10 52 09 AM

Cacti Docker

This is a dockerized application that is vulnerable to the Cacti RCE vulnerability (CVE-2022-46169). Follow the link to get Cacti running

https://github.com/vulhub/vulhub/tree/master/cacti/CVE-2022-46169

Usage

   _____           _   _   __   ___   __ ______    ___  ___    _____   _____ ______ 
  / ____|         | | (_) /_ | |__ \ /_ |____  |  |__ \|__ \  |  __ \ / ____|  ____|
 | |     __ _  ___| |_ _   | |    ) | | |   / /_____ ) |  ) | | |__) | |    | |__   
 | |    / _` |/ __| __| |  | |   / /  | |  / /______/ /  / /  |  _  /| |    |  __|  
 | |____ (_| | (__| |_| |  | |_ / /_ _| | / /      / /_ / /_  | | \ \| |____| |____ 
  \_____\__,_|\___|\__|_|  |_(_)____(_)_|/_/      |____|____| |_|  \_\\_____|______|
                                                                                    
                                                                                    
 By @Habib0x

Usage: CVE-2022-46169.rb [options]
    -u, --url URL                    Victim URL
    -f, --forwarded FORWARDED        X-Forwarded value to bypass the auth
    -i, --ip IP                      IP for reverse shell
    -p, --port PORT                  Port for reverse shell


https://user-images.githubusercontent.com/24976957/212615669-0dd754de-a57e-4a0d-b37e-dac49a4439b3.mp4

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




