
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-1329-WordPress-Elementor-RCE — Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based vulnerable environment and customizable PHP payload injection. | Kitploit
Tools/GitHubGitHub/grazee/cve-2022-1329-wordpress-elementor-rce
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubgrazee/cve-2022-1329-wordpress-elementor-rce

CVE-2022-1329-WordPress-Elementor-RCE

Proof-of-concept exploit for CVE-2022-1329, a remote code execution vulnerability in WordPress Elementor 3.6.0-3.6.2. Includes Docker-based vulnerable environment and customizable PHP payload injection.

View Repository
41354 years agoNot yet reviewed
Share

CVE-2022-1329-WordPress-Elementor-RCE

This poc is based on the one of AkuCyberSec.

中文版本

Usage

Use docker-compose to start the vuln environment:

docker-compose up -d

Then you can access the WordPress Admin page with URL http://localhost:8000.

Register the admin user, and add a no-admin user in the Users tag. For example, there are two users:

UsernamePasswordRole
wc123456Admin
a2aaaaaaEditor

Log in with the admin account, and install Elementor 3.6.1 with the zip provided.

If you encounter the upload size problem, add php.ini to /var/www/html/ as following and restart the docker server:

upload_max_filesize = 64M
max_execution_time = 0
post_max_size = 150M
file_uploads = on

Edit the poc script with your no-admin user infomation and run the poc script to exploit:

python3 poc.py

NOTE: the script may failed with upload problem, but it's OK, try to refresh the admin page in the browser to see if it works.

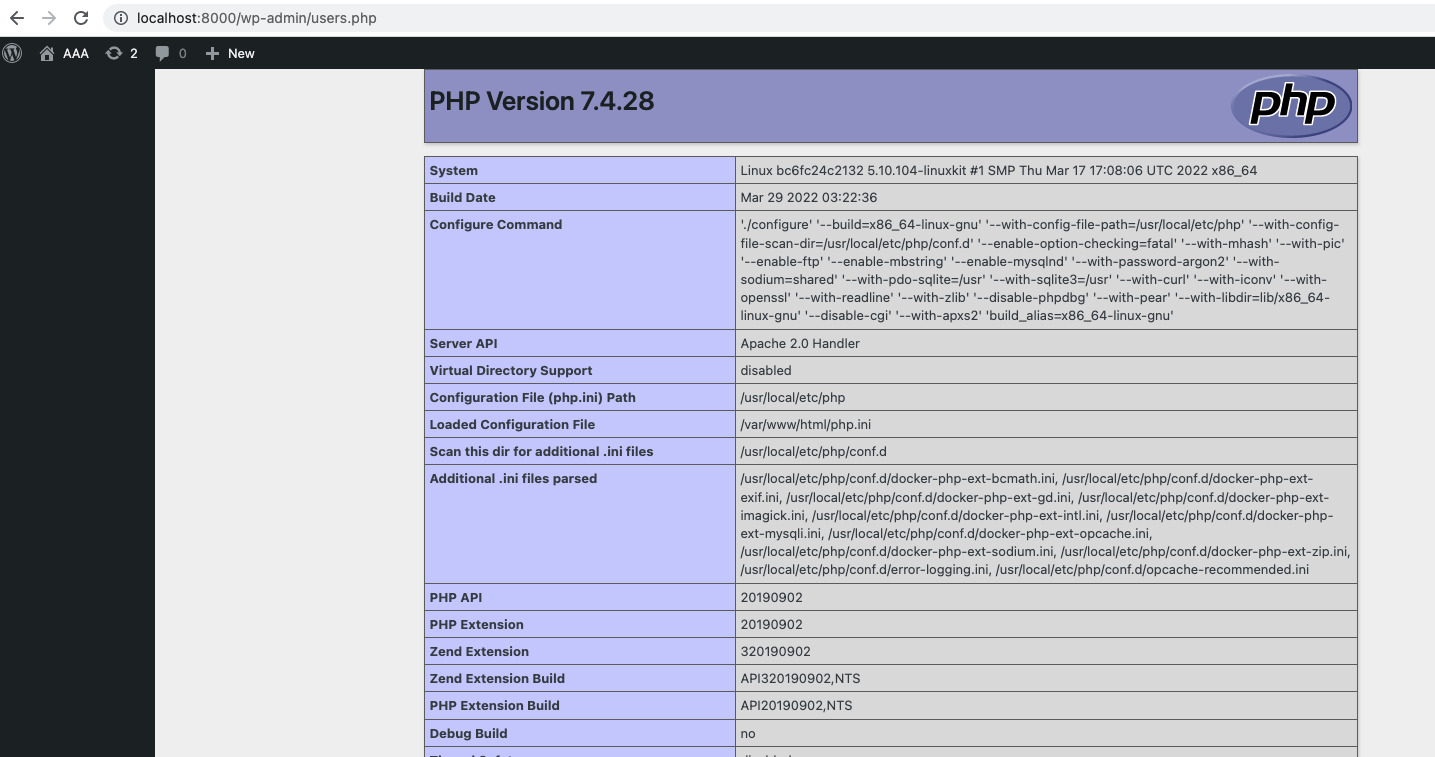
The poc now runs phpinfo(); as it's payload, of course you can edit this, but you need to manual remove the elementor-pro plugin in docker container /var/www/html/wp-content/plugin/elementor-pro:

# Unzip the zip file
unzip elementor-pro.zip

# Edit the main file to put your payload, it's in the begin of the file
nano elementor-pro/elementor-pro.php

# And zip
rm elementor-pro.zip; zip -ry elementor-pro.zip elementor-pro

# exploit again
python3 poc.py
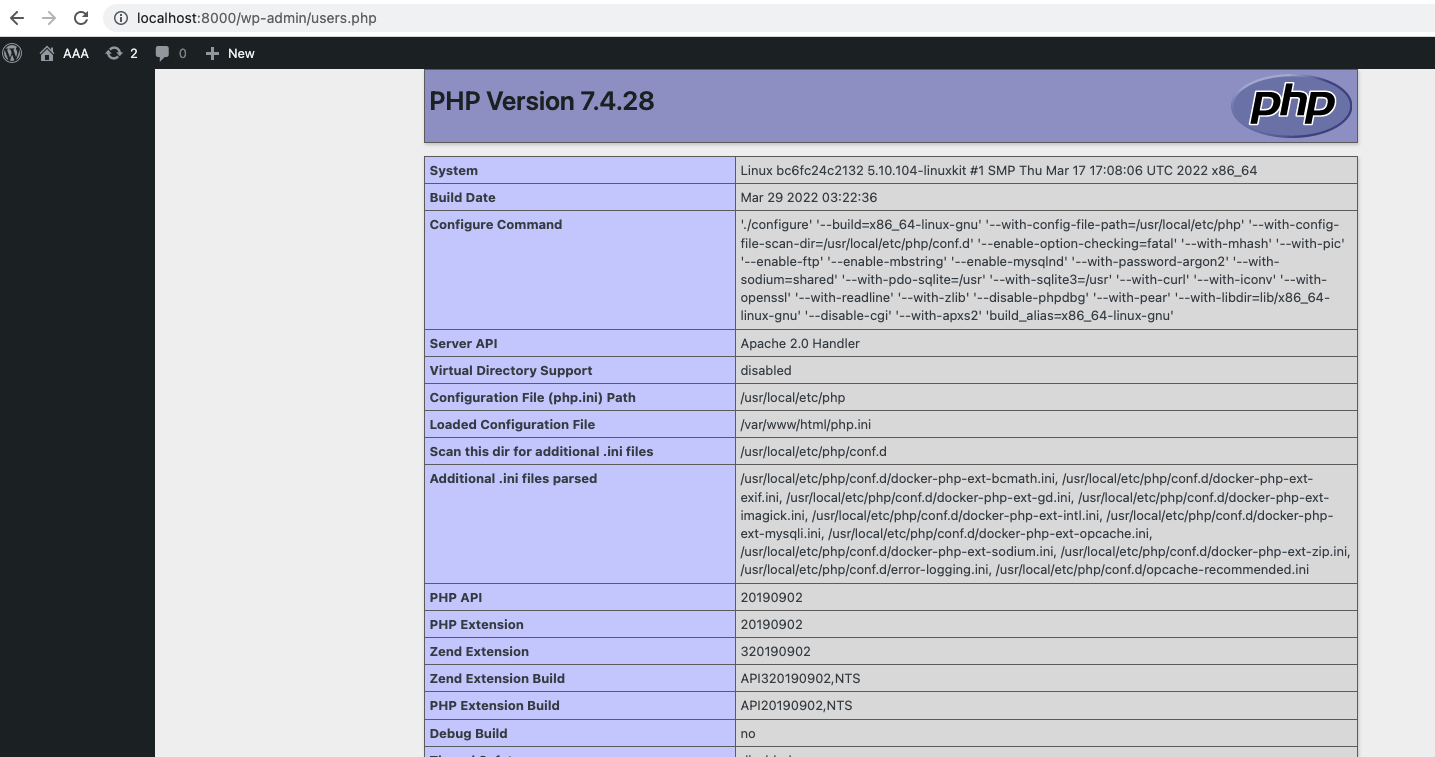

Result

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →





