
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2014-1266-poc — Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy server. | Kitploit
Tools/GitHubGitHub/gabrielg/cve-2014-1266-poc
iOS SecurityVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingMobile Security
GitHubgabrielg/cve-2014-1266-poc

CVE-2014-1266-poc

Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy server.

View Repository
78142412 years agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

OS X/iOS SSL Flaw POC

Overview

This repository contains some Go code that demonstrates the recently discovered SSL verification vulnerability in iOS and OS X.

  • Apple Update Announcement
  • Adam Langley's writeup

Usage

$ git clone https://github.com/gabrielg/CVE-2014-1266-poc.git
$ cd CVE-2014-1266-poc
$ go build main.go
$ ./main

# In another terminal
$ cd CVE-2014-1266-poc
$ go run http_server.go

Then set the proxy on a vulnerable machine to point at port 8080 on the machine running the proxy server. HTTPS requests will be intercepted and redirected to the HTTP server listening on the UNIX domain socket that the proxy makes connections to.
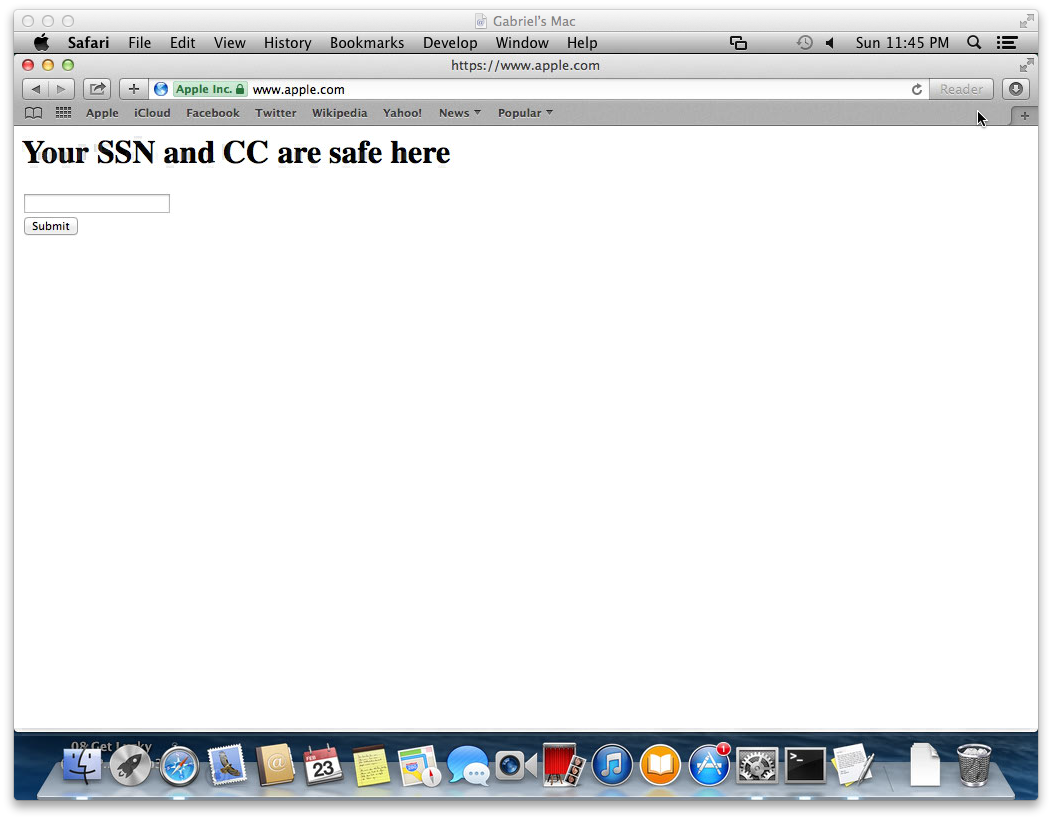
screenshot


Pass the time with some reading over at gironda.org.

Download Tool