Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
log4j2burpscanner — CVE-2021-44228 Log4j2 BurpSuite Scanner,Customize ceye.io api or other apis,including internal networks | Kitploit
Tools/GitHubGitHub/f0ng/log4j2burpscanner
Vulnerability ScannersExploitationWeb Application ExploitationPenetration TestingDNS Analysis
GitHubf0ng/log4j2burpscanner

log4j2burpscanner

CVE-2021-44228 Log4j2 BurpSuite Scanner,Customize ceye.io api or other apis,including internal networks

View Repository
840107343 years agoReviewed by Kitploit
Website
Share

JUST FOR TESTING,DON'T ATTACK ANYONE

JUST FOR TESTING,DON'T ATTACK ANYONE

JUST FOR TESTING,DON'T ATTACK ANYONE

交流群

image

二维码失效请加微信f-f0ng、备注log4j2burpscanner交流

关注主页公众号(only security),回复log4j2burpscanner获取下载地址】

FAQ Frequently Asked Questions

how to use? releases download the latest plugin

简体中文|English

default dnslog https://dns.xn--9tr.com/ github: DNSLog-Platform-Golang

0.25.0 update

2023-4-26

1.fix bugs

0.24.0 update

2023-3-20

  1. Adapt the selistener tool for intranet vulnerability detection

0.23.0 update

2023-3-10

  1. set normal payload as preferred
  2. add the vulnerability display of payload containing variables
  3. optimize the problem of not displaying vulnerability points

0.22.0 update

2023-2-14

  • fix problem

0.21.0 update

2022-12-9

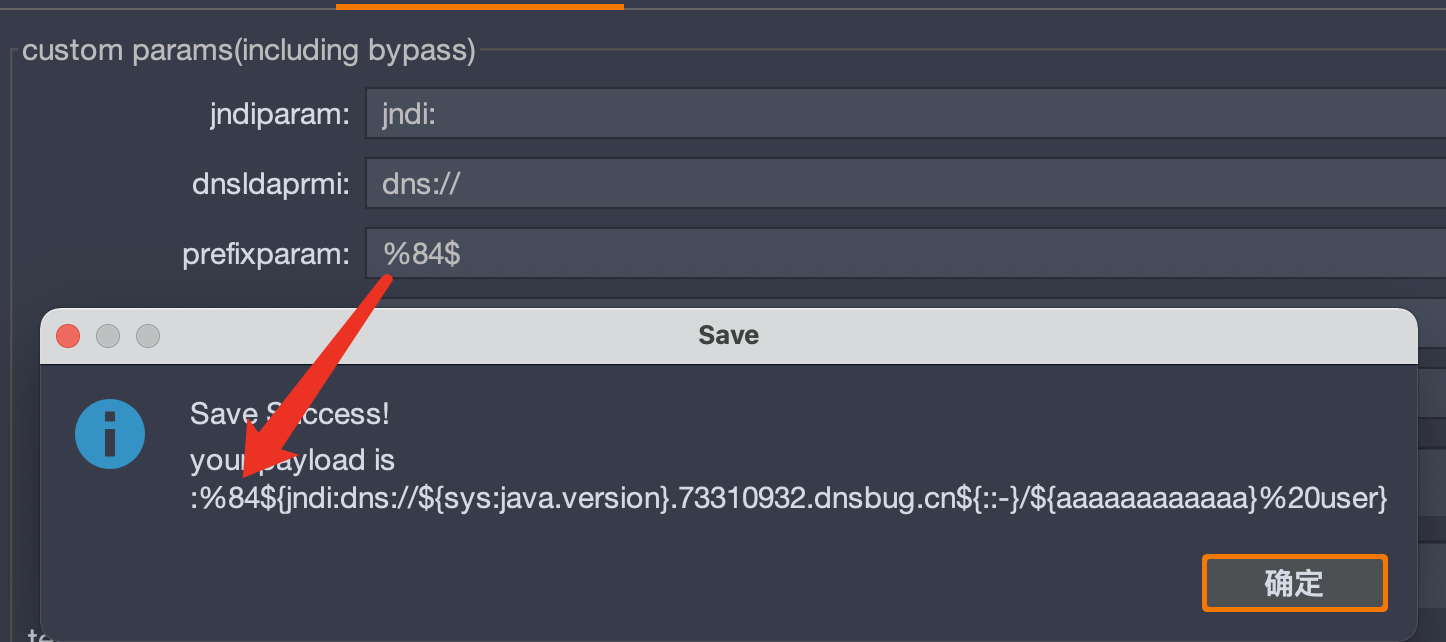
  1. add prefixparam image

0.20.0 update

2022-11-22

  1. add suffixparam
  2. change the path to full spelling
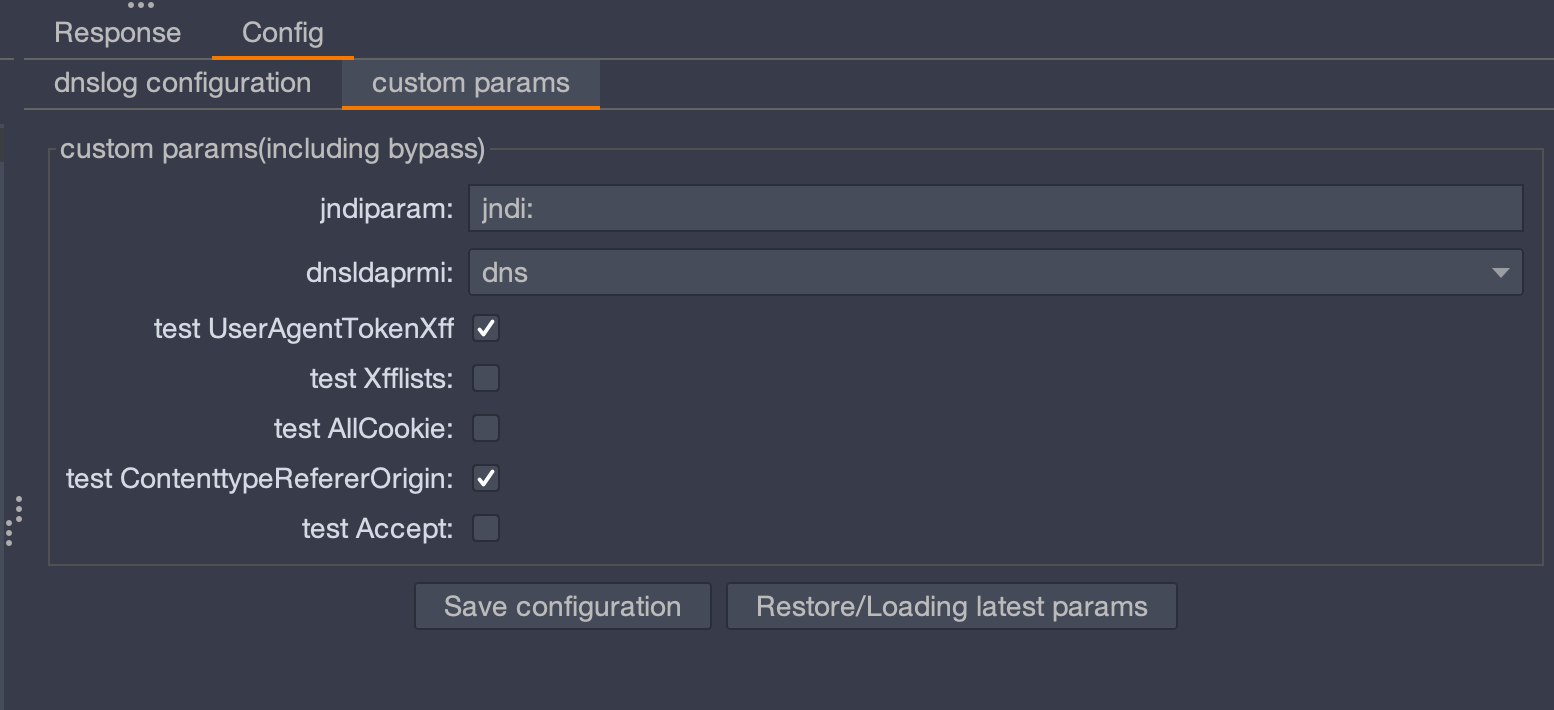
  3. delete isusepointBypas,change to custom param
image

0.19 update

2022-05-02

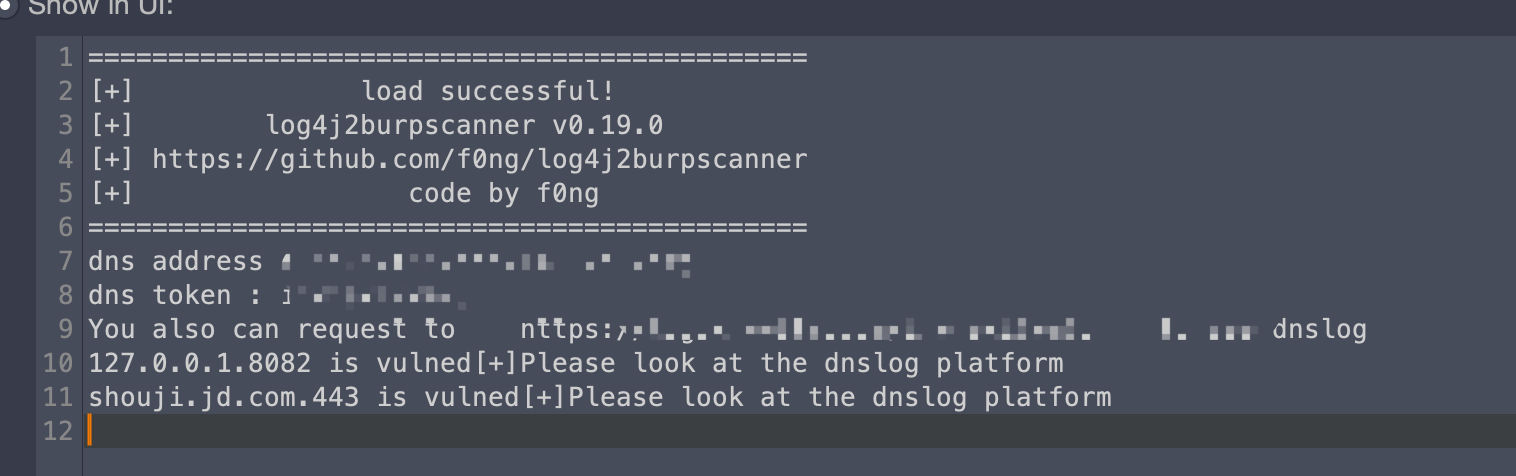
1.add polling dnslog query including active scanning and passive scanning image
0.18 update

2021-12-25

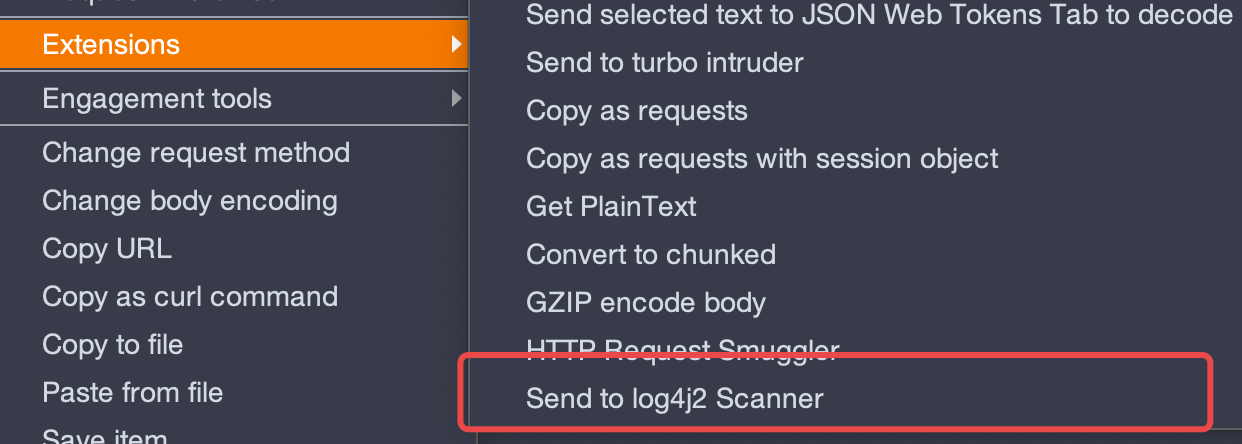
1.Send to log4j2 Scannerthe bypass payload of jndi: is used for testing. at now it includes the following three typesj${::-n}di:、 jn${env::-}di:、j${sys:k5:-nD}${lower:i${web:k5:-:}}

0.17 update

2021-12-19

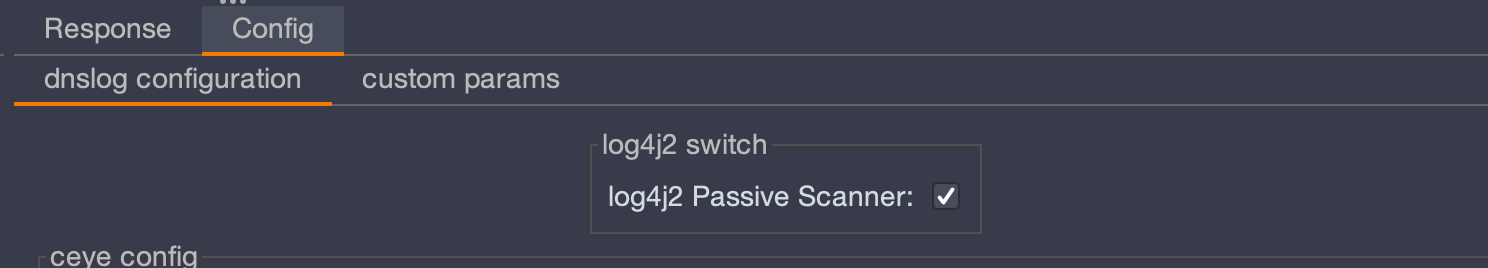
1.add passive switch log4j2 Passive Scanner,add log4j2 Scanner menu button Send to log4j2 Scanner
2.update payload param,add random character string,distinguish between the same site and the same path, optimization %20 problem

3.recognize multipart/form-data type、xml type

fix parameter issue for creating initial properties file

0.16 update

2021-12-15

1.change the UI page

2.add isip param(for the case that there is no domain name and only IP detection in the intranet) but this kind of test has no parameter point digital ID and no host

If there are no other good intranet dnslog tools to replace, you can link the tools of KpLi0rn https://github.com/KpLi0rn/Log4j2Scan

0.15 update

2021-12-14

1.add dnsldaprmi param (dns、ldap、rmi) default dns

2.add isContenttypeRefererOrigin param 、isAccept param

isContenttypeRefererOrigin param(whether test Content-Type、Referer、Origin)default off

isAccept param(whether test Accept-Language、Accept、Accept-Encoding)default off

3.add bypass jndi: ,but the effect is not good,use with caution

jndi: bypass methods https://twitter.com/ymzkei5/status/1469765165348704256

  • jn${env::-}di:
  • jn${date:}di${date:':'}
  • j${k8s:k5:-ND}i${sd:k5:-:}
  • j${main:\k5:-Nd}i${spring:k5:-:}
  • j${sys:k5:-nD}${lower:i${web:k5:-:}}
  • j${::-nD}i${::-:}
  • j${EnV:K5:-nD}i:
  • j${loWer:Nd}i${uPper::}

4.add log.xn--9tr.com to the white list
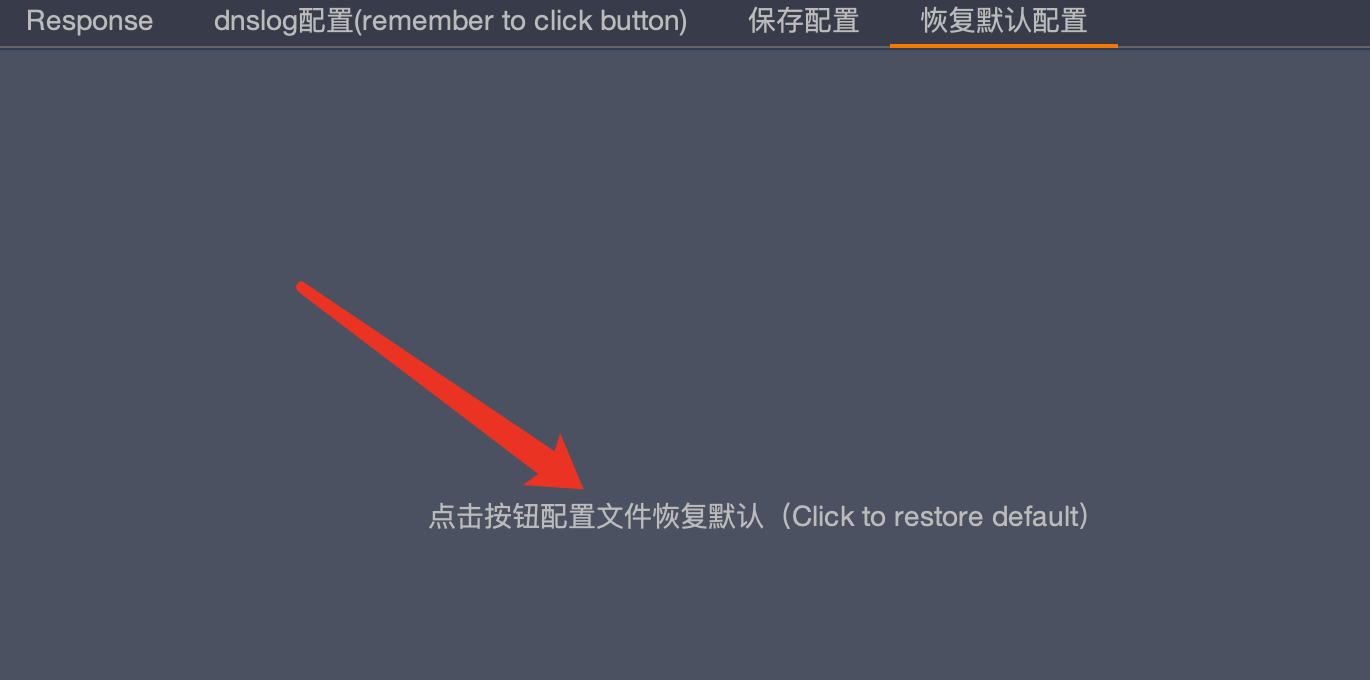
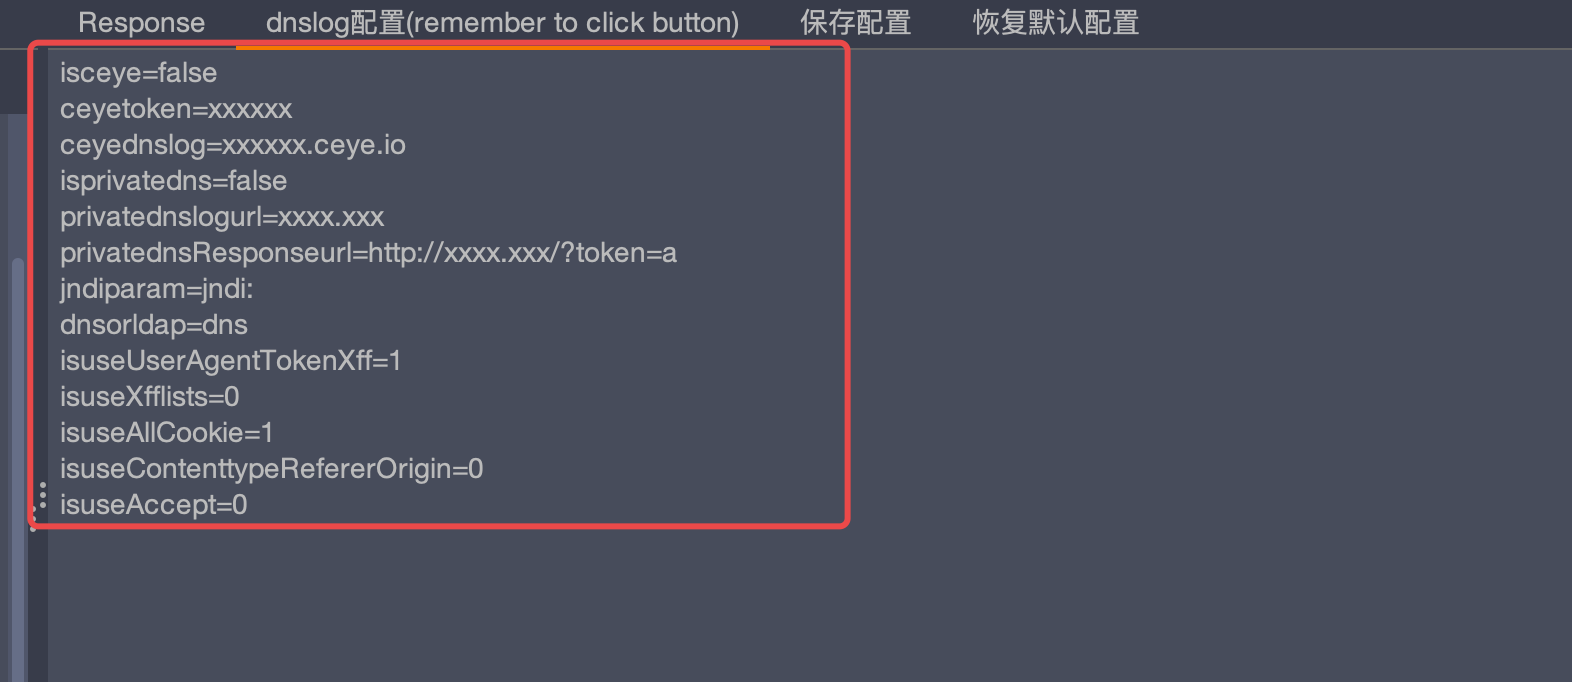
In addition, you need to click this button to obtain the latest configuration parameters

0.14 update

2021-12-13

1.add bypass rc1,add space to the payload

2.more accurate

3.add Intranet dnslog api,can customize the ceye.io api or other apis,including internal networks

Param 1:isprivatedns(whether to use private dns api)

Param 2:privatednslogurl(internal dnslog address)

Param 3:privatednslogurl(internal dnslog response address)

4.add controllable params to control the payload

Param 4:isuseUserAgenttokenXff(whether test User-agent、token、X-Forward-for、X-Client-IP) default on

Param 5:isuseXfflists(whether test xff lists,including others xff)default off

Param 6:isuseAllCookie(whether test all cookie)default on

Remember to click restore default button to get the latest dnslog params

0x01 More accurate

0x02 Add Intranet dnslog api,can customize the ceye.io api or other apis,including internal networks

Since I don't have an intranet dnslog address,here I use ceye.io to test

Just ensure the connectivity between intranet and Intranet dnslog address, intranet and dnslog response address
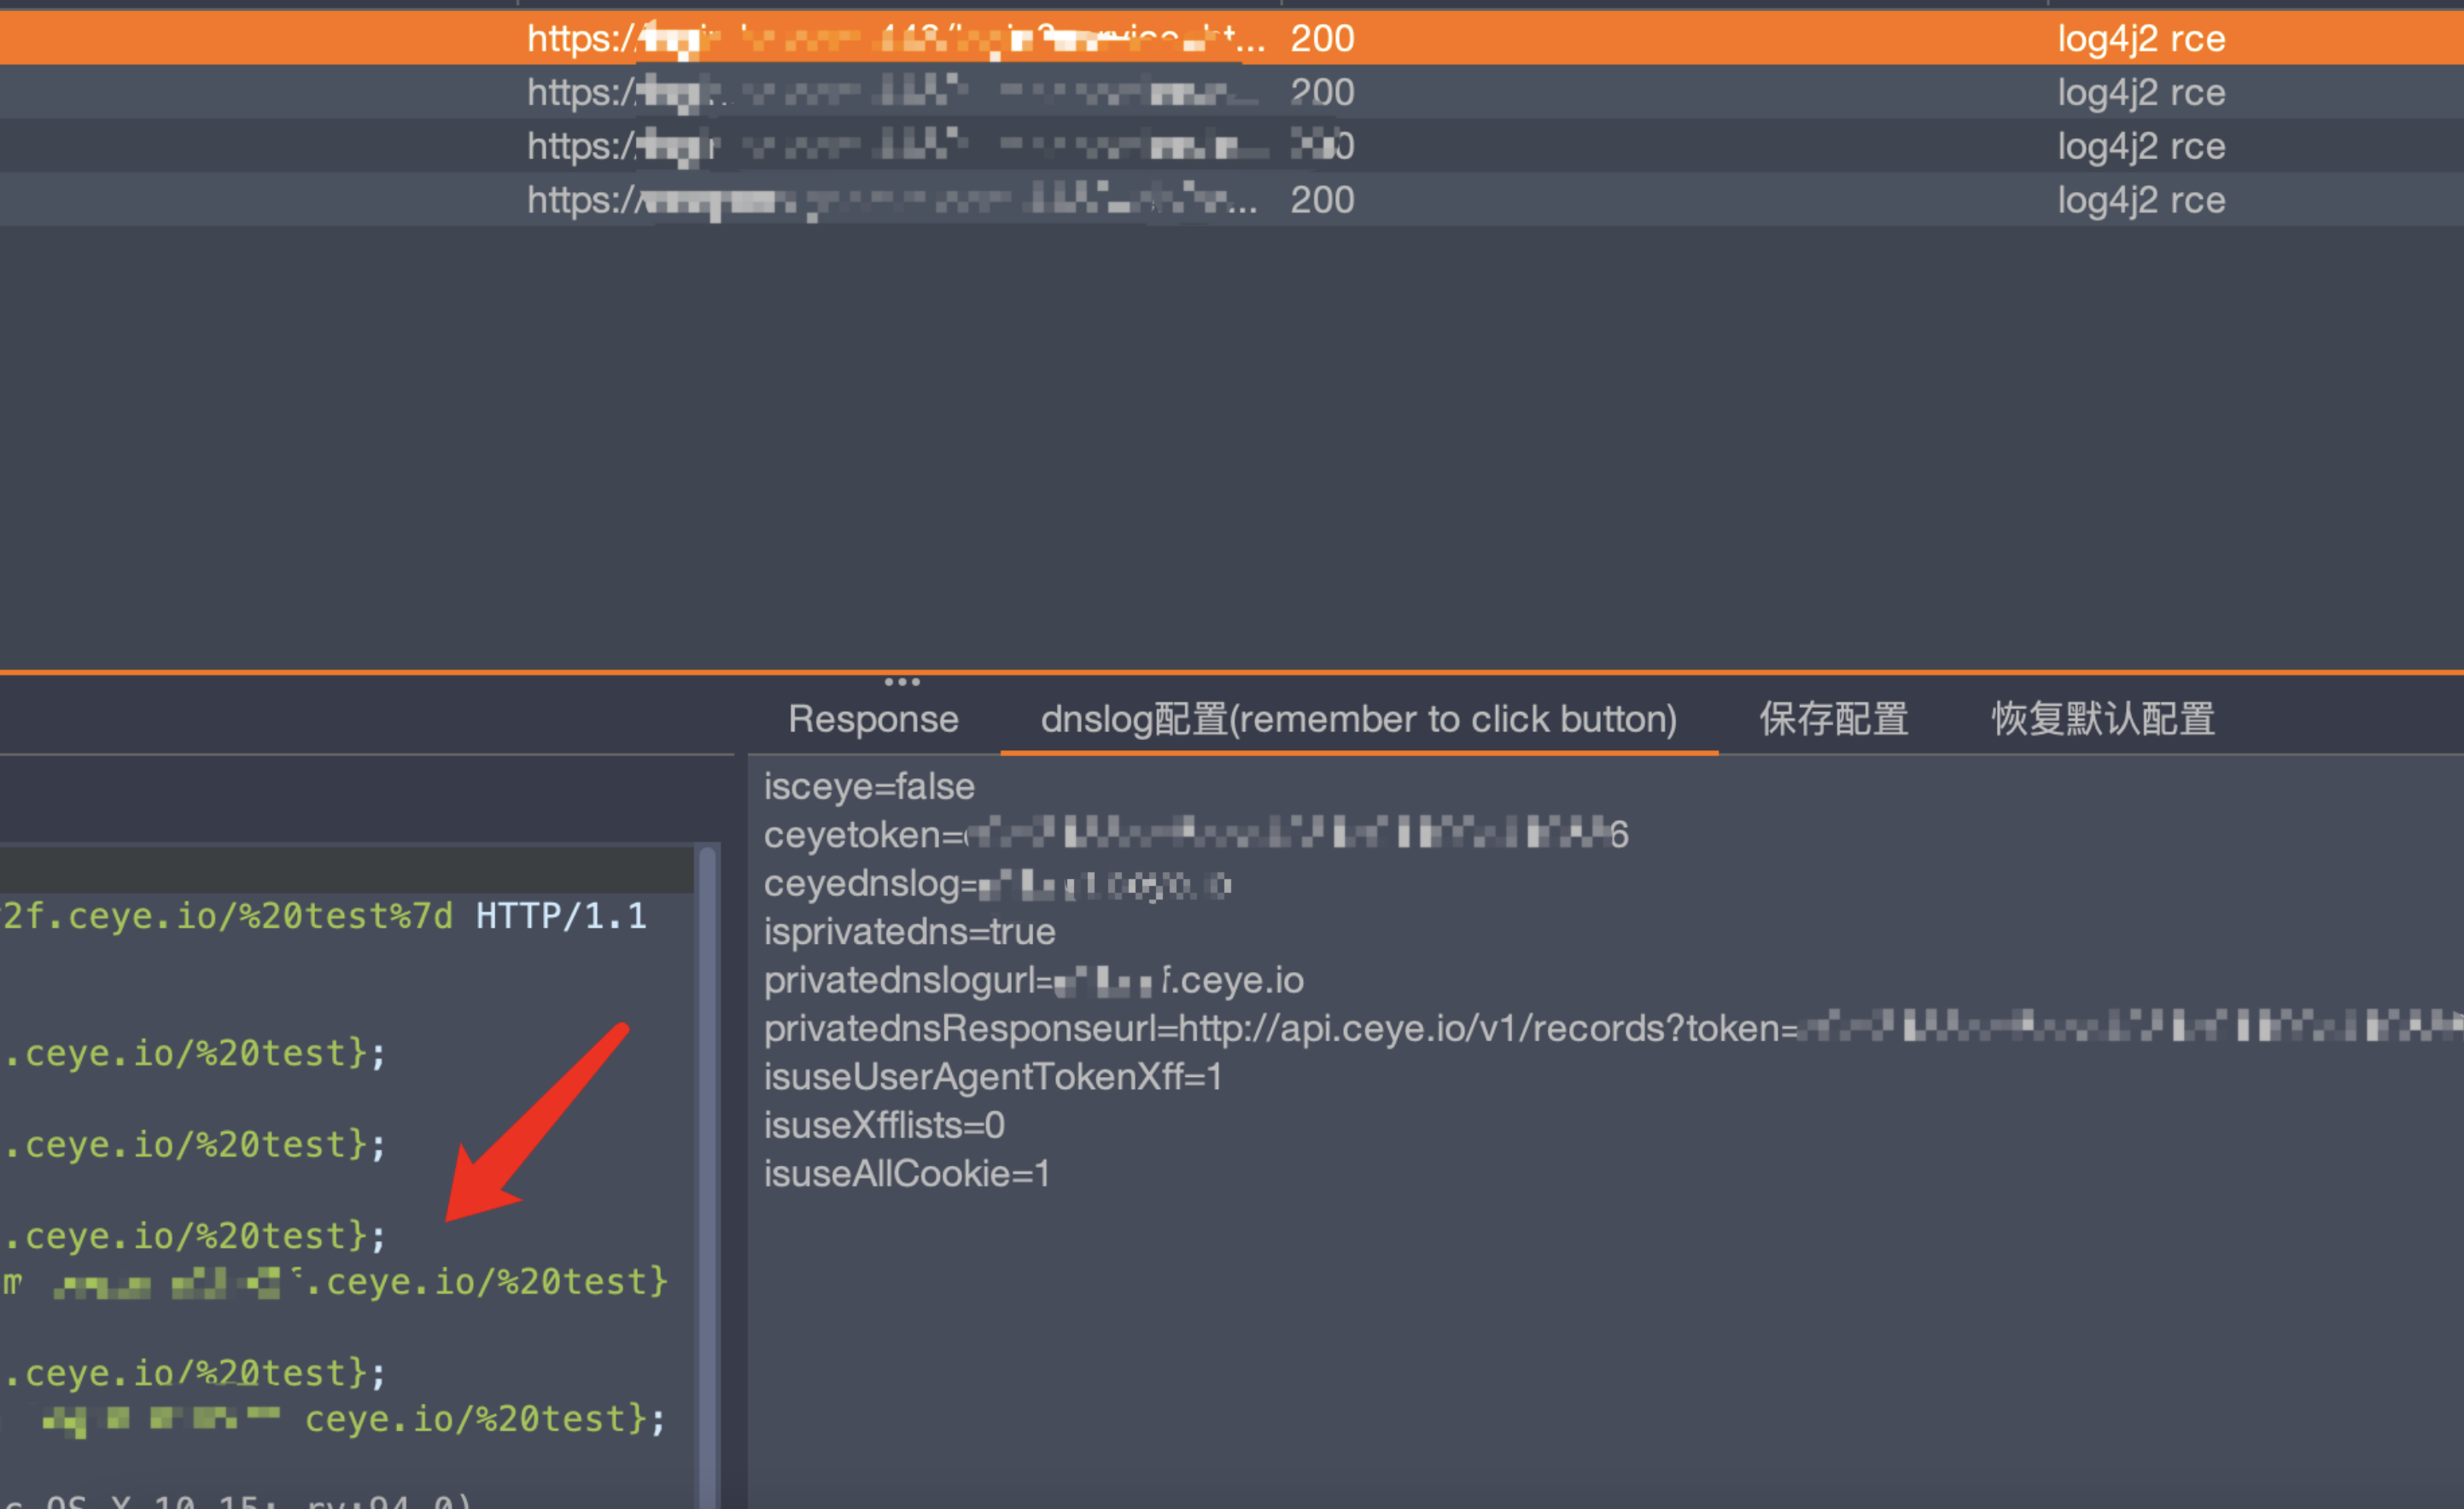
0x03 Add controllable params to control the payload

Fix problem: Due to the vulnerability of the sub domain name, the primary domain name will also report the vulnerability

0.13 update

1.add request headers

["X-Forwarded-For","X-Forwarded","Forwarded-For","Forwarded","X-Requested-With","X-Requested-With", "X-Forwarded-Host","X-remote-IP","X-remote-addr","True-Client-IP","X-Client-IP","Client-IP","X-Real-IP","Ali-CDN-Real-IP","Cdn-Src-Ip","Cdn-Real-Ip","CF-Connecting-IP","X-Cluster-Client-IP","WL-Proxy-Client-IP", "Proxy-Client-IP","Fastly-Client-Ip","True-Client-Ip","X-Originating-IP", "X-Host","X-Custom-IP-Authorization","X-original-host","If-Modified-Since"]

0.12 update

1.add recognizable format

body={"a":"1","b":"22222"}

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →