

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
lsm_bpf_check_argc0 — LSM BPF module to block pwnkit (CVE-2021-4034) like exploits | Kitploit

Tools/GitHubGitHub/evdenis/lsm_bpf_check_argc0
Defensive ToolsArchived
GitHubevdenis/lsm_bpf_check_argc0

lsm_bpf_check_argc0

LSM BPF module to block pwnkit (CVE-2021-4034) like exploits

View Repository
21364 years agoReviewed by Kitploit
Share

BUILD

Check ARGC0 LSM BPF

Simple LSM BPF program to prevent program executions with argc == 0, e.g. pwnkit (CVE-2021-4034). It does nothing more than a simple check that all exec*() system calls are called with argc >= 1. The check is based on Ariadne Conill's patch.
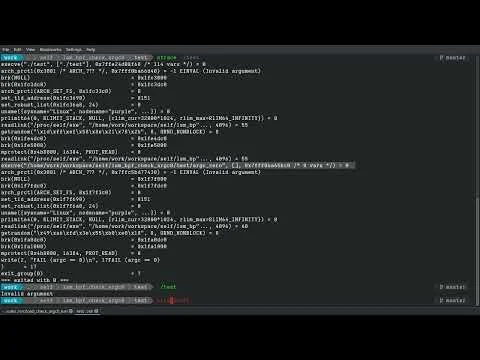
LSM BPF demonstration

How to build

# On Ubuntu
$ sudo apt-get install libc6-dev-i386 libbpf0 libbpf-dev

# On Fedora 35
$ sudo dnf install clang bpftool libbpf-devel glibc-devel.i686 glibc-devel.x86_64

$ make

How to install

Run:

$ sudo make DESTDIR=/usr install
# will execute following commands
# sudo cp src/load_check_argc0_lsm /usr/sbin
# sudo cp share/check_argc0_lsm.service /etc/systemd/system/

# After that you can enable the service with
$ sudo systemctl daemon-reload
$ sudo systemctl enable check_argc0_lsm.service
$ sudo systemctl start check_argc0_lsm.service

Test:

$ strace ./test/trigger
...
execve("/usr/bin/pkexec", NULL, NULL)   = -1 EINVAL (Invalid argument)


$ sudo journalctl -u check_argc0_lsm.service
Feb 10 13:27:08 purple systemd[1]: Started LSM BPF protection for argc == 0 execs.
Feb 10 13:27:13 purple load_check_argc0_lsm[89177]: TIME     PID     PROCESS          CALLING
Feb 10 13:27:13 purple load_check_argc0_lsm[89177]: 13:27:13 89194   trigger          /usr/bin/pkexec

How to test

Linux kernel >= 5.8 required for BPF LSM (5.7) and BPF rignbuf (5.8).

# The program will start, attach an LSM BPF, and monitor the log
$ sudo ./src/load_check_argc0_lsm
TIME     PID     PROCESS          CALLING
12:59:21 85689   trigger          /usr/bin/pkexec

One can use the trigger program to test that everything works:

$ strace ./test/trigger
...
execve("/usr/bin/pkexec", NULL, NULL)   = -1 EINVAL (Invalid argument)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →



