Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2020-35391-POC — Tenda N300 Authentication Bypass via Malformed HTTP Request Header | Kitploit

Tools/GitHubGitHub/dumitory-dev/cve-2020-35391-poc
Authentication & AuthorizationIoT SecurityVulnerability AnalysisExploitationWeb Application ExploitationPenetration Testing
GitHubdumitory-dev/cve-2020-35391-poc

CVE-2020-35391-POC

Tenda N300 Authentication Bypass via Malformed HTTP Request Header

View Repository
22333 years agoNot yet reviewed
Share

Welcome to CVE-2020-35391-POC 👋

Original Documentation License: MIT Pylint

Tenda N300 Authentication Bypass via Malformed HTTP Request Header Python POC

Tenda N300 F3 12.01.01.48 devices allow remote attackers to obtain sensitive information (possibly including an http_passwd line) via a direct request for cgi-bin/DownloadCfg/RouterCfm.cfg, a related issue to CVE-2017-14942. NOTE: the vulnerability report may suggest that either a ? character must be placed after the RouterCfm.cfg filename, or that the HTTP request headers must be unusual, but it is not known why these are relevant to the device's HTTP response behavior.

Original PoC Author: Michelle Bonilla
After so much time since this CVE was published, the vulnerability has still not been fixed! (Last Firmware Version: V12.01.01.42_multi)

Usage

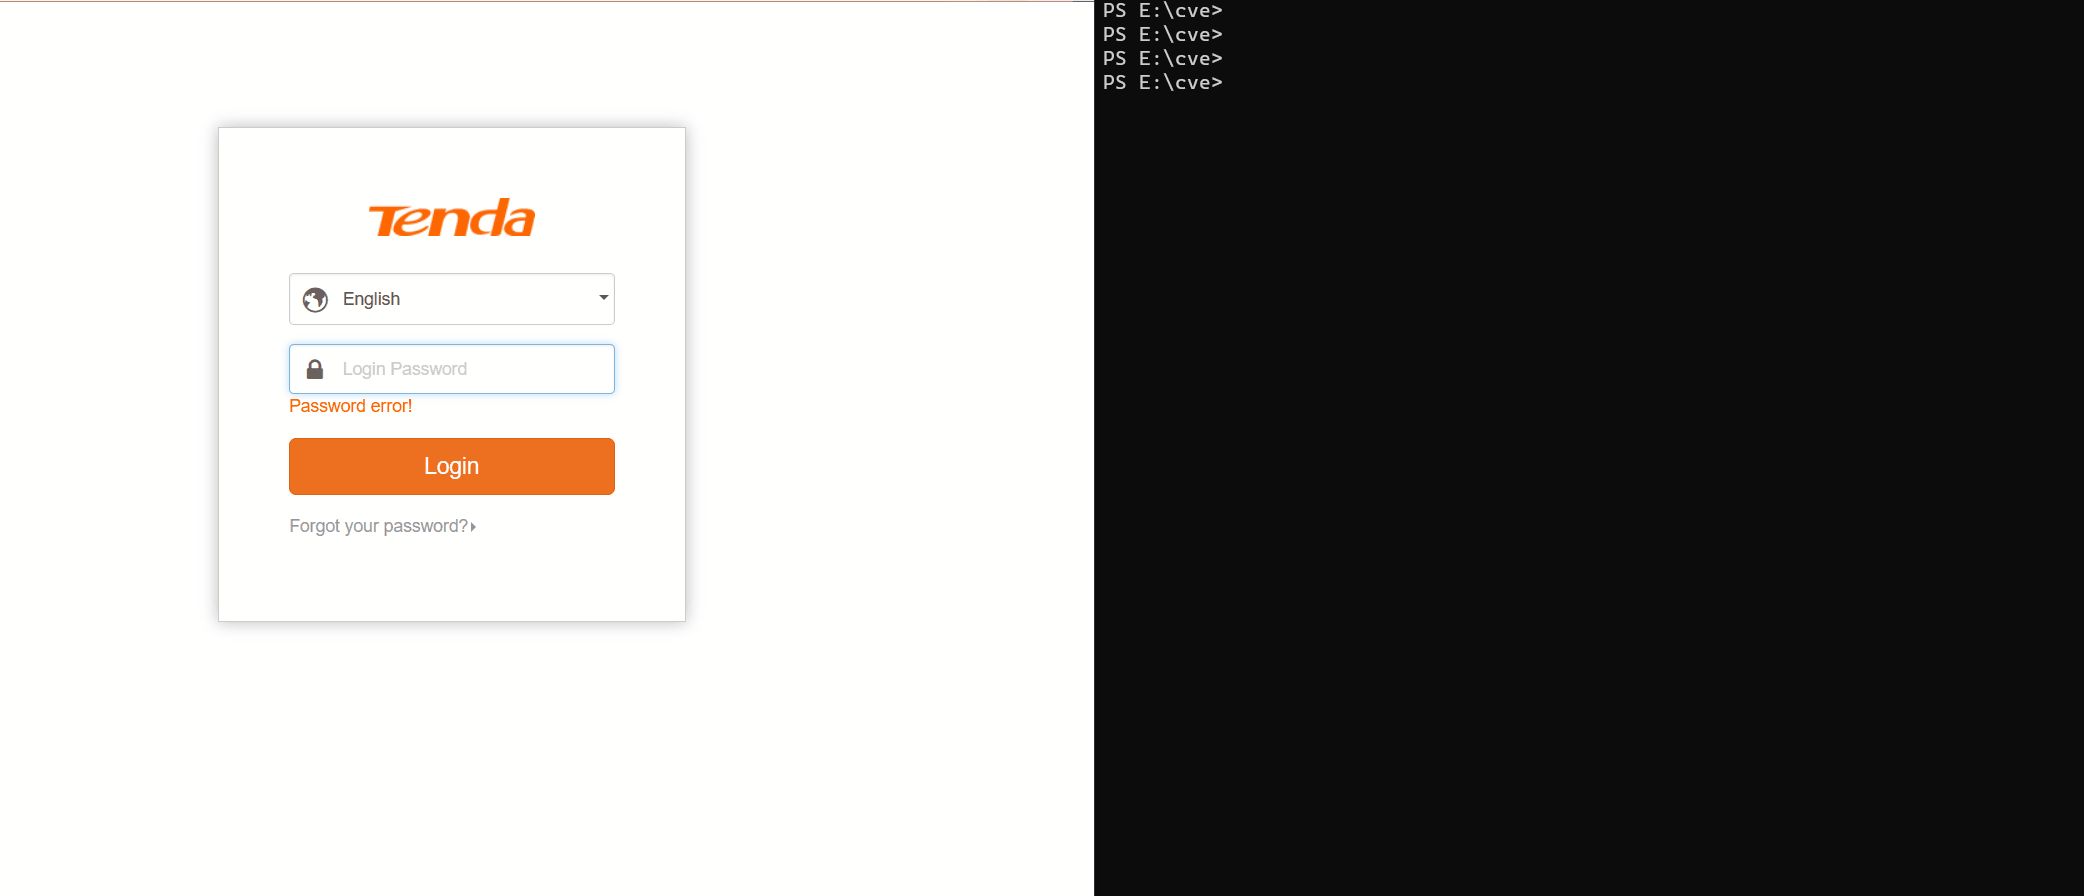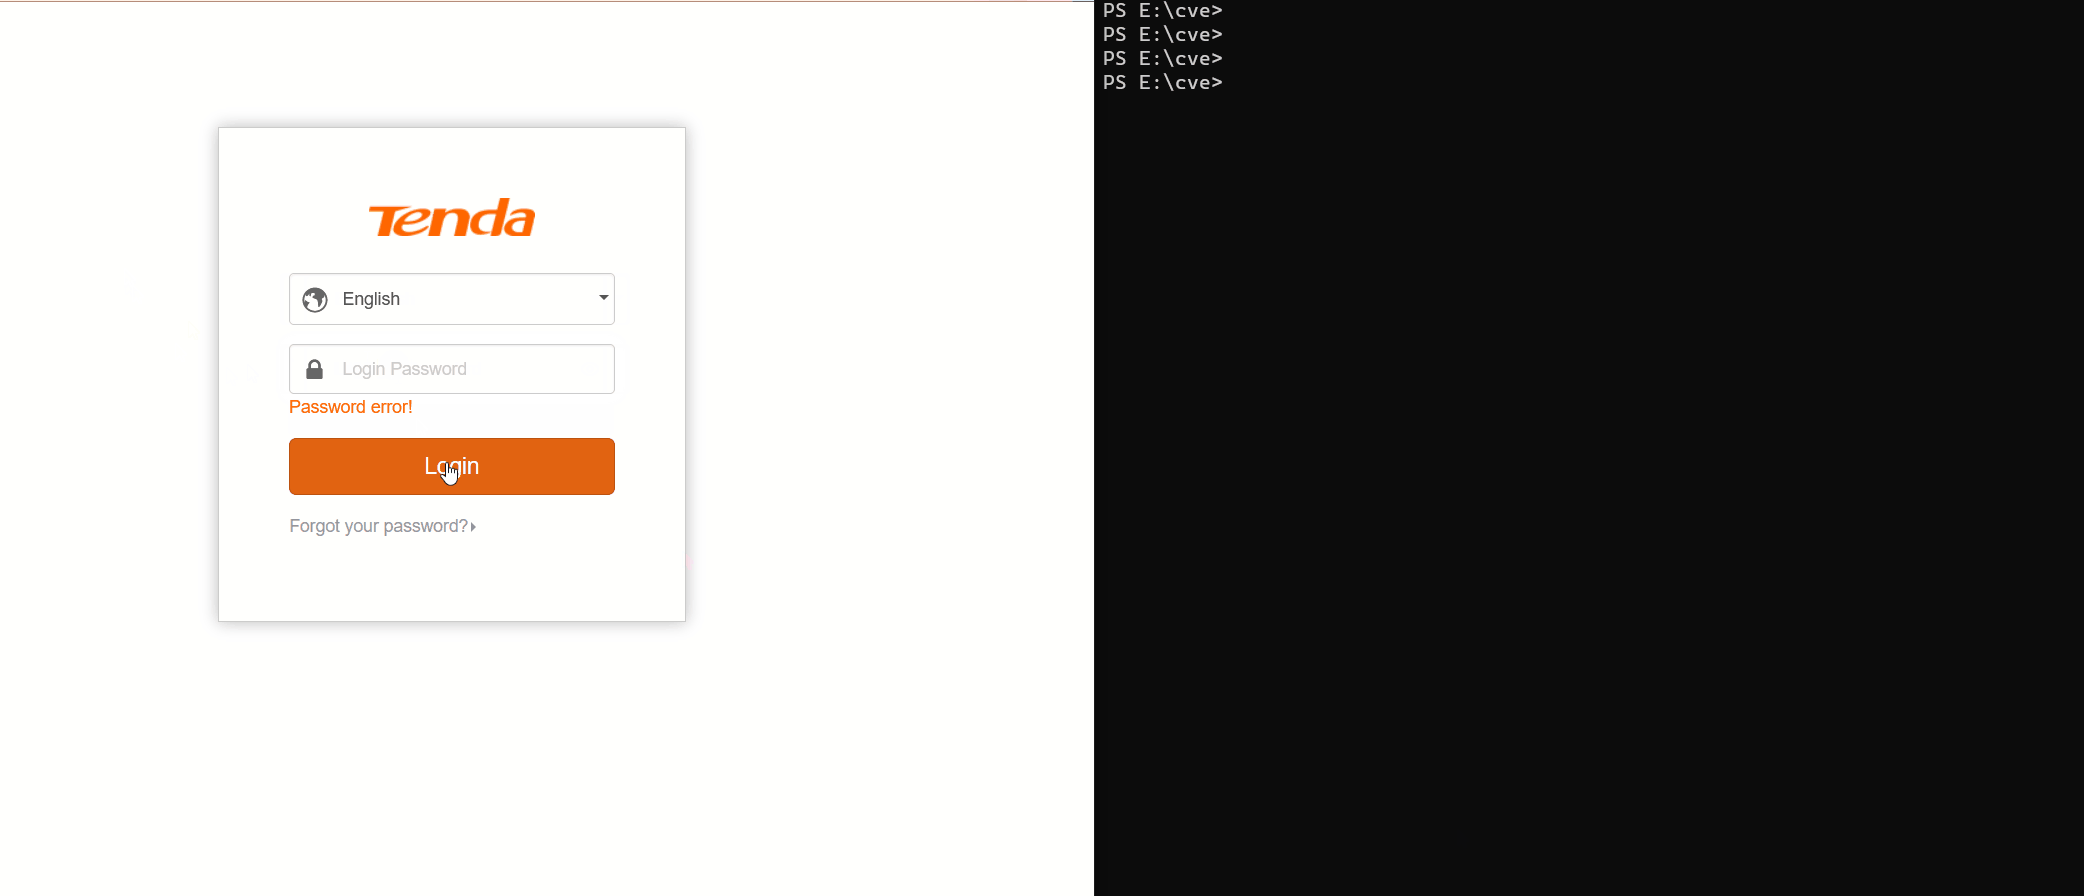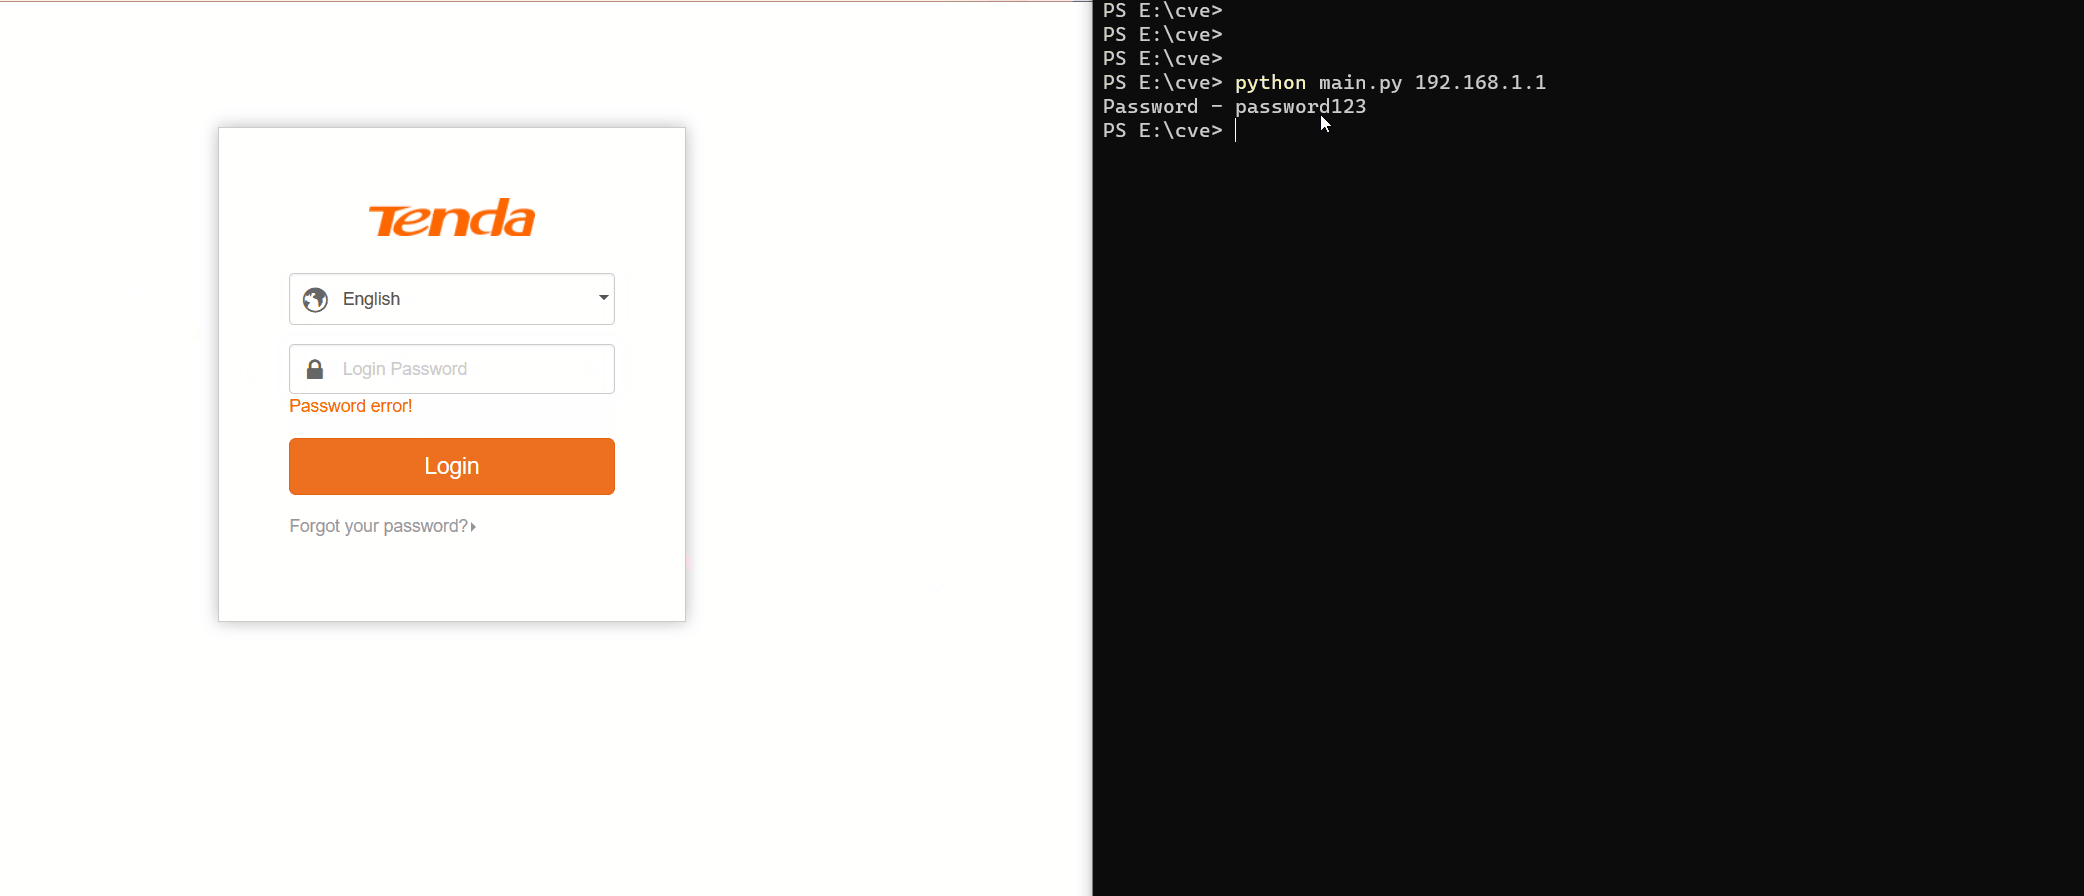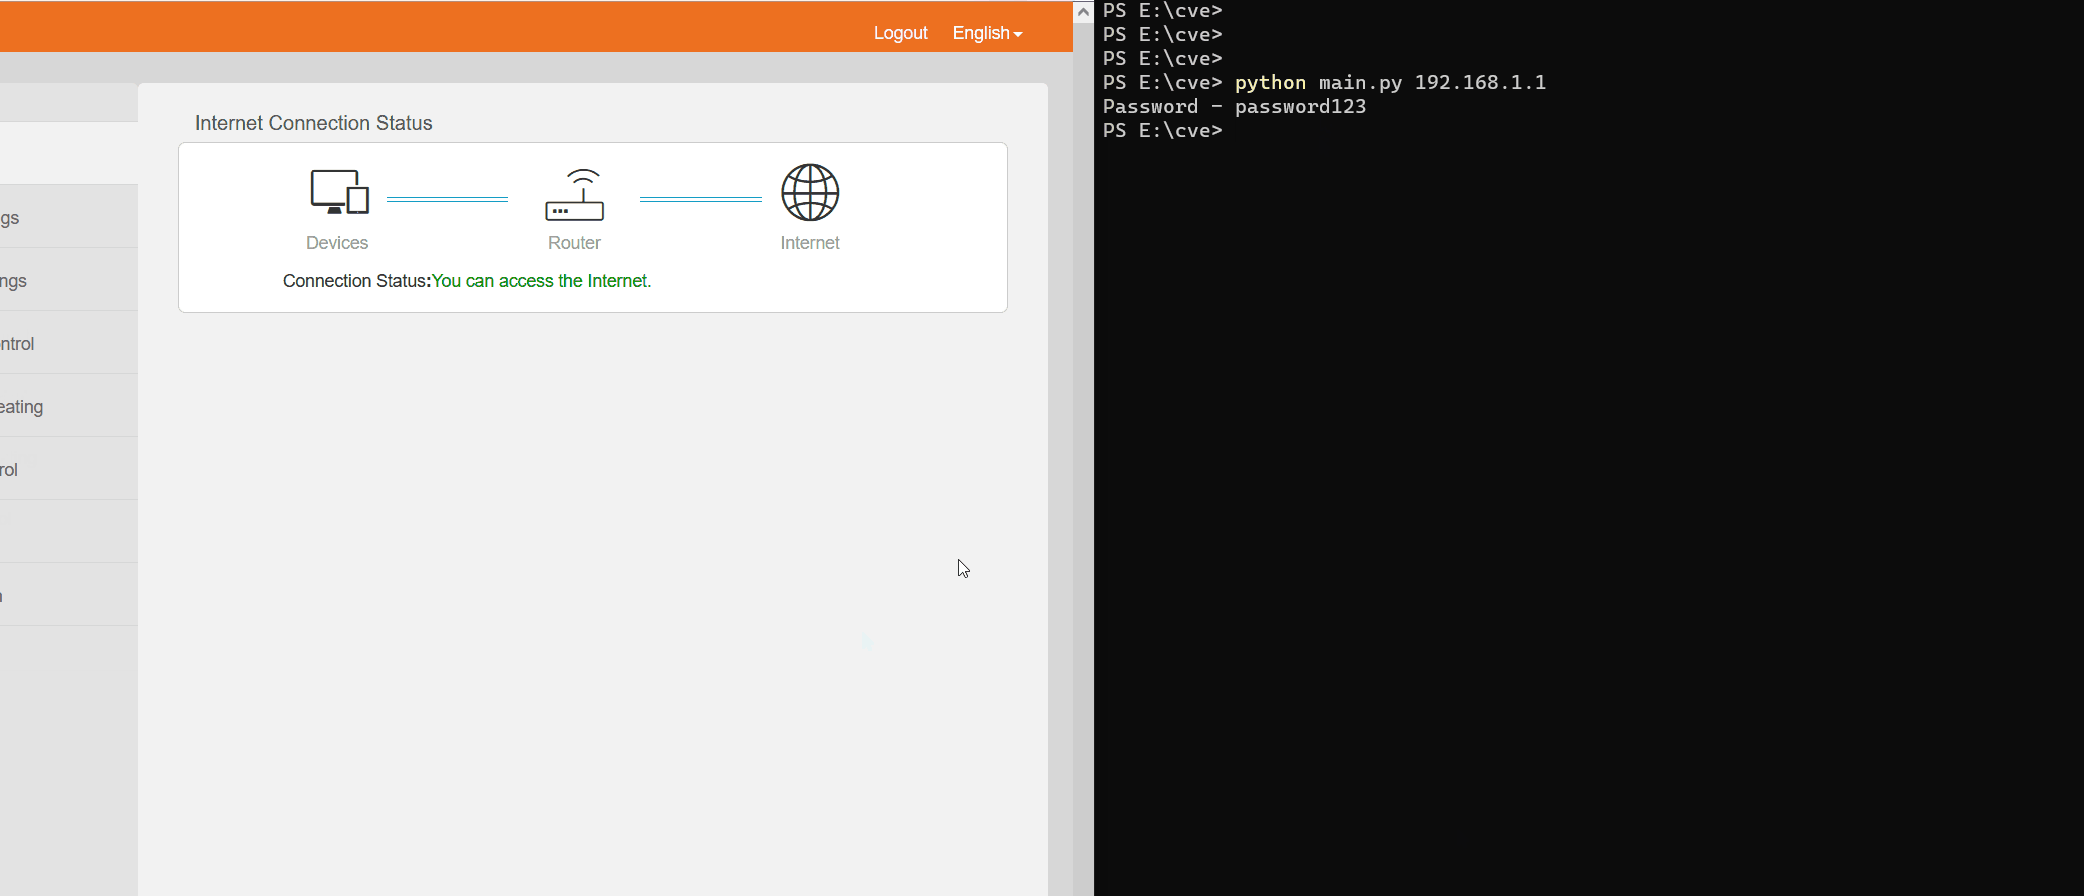
python3 main.py <router ip>

Work example

Author

👤 dumitory-dev

Show your support

Give a ⭐️ if this project helped you!

📝 License

This project is MIT licensed.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →