demining/phoenix-rowhammer-attack-cve-2025-6202
Phoenix Rowhammer Attack: Systemic Risk of Bitcoin Wallet Private Key Compromise in Global Blockchain Infrastructure Due to a Critical SK Hynix DDR5 Vulnerability (CVE-2025-6202)

This article examines the systemic cryptographic security threats posed by the Phoenix Rowhammer attack (CVE-2025-6202), which can extract private keys from DDR5 RAM through hardware-level bit manipulation. In recent years, the dynamic development of cryptocurrency technologies has led to an increased dependence of digital asset ecosystems on hardware and microchip components that store and process cryptographic data. Against this backdrop, hardware-level vulnerabilities that can lead to the direct compromise of private keys in cryptocurrency wallets are becoming a growing risk factor. One of the most dangerous threats today is attacks on RAM, in particular, advanced variants of Rowhammer exploits that affect the physical properties of DRAM cells. These attacks allow attackers to modify individual data bits and gain access to confidential information, including private keys for Bitcoin and Ethereum wallets.
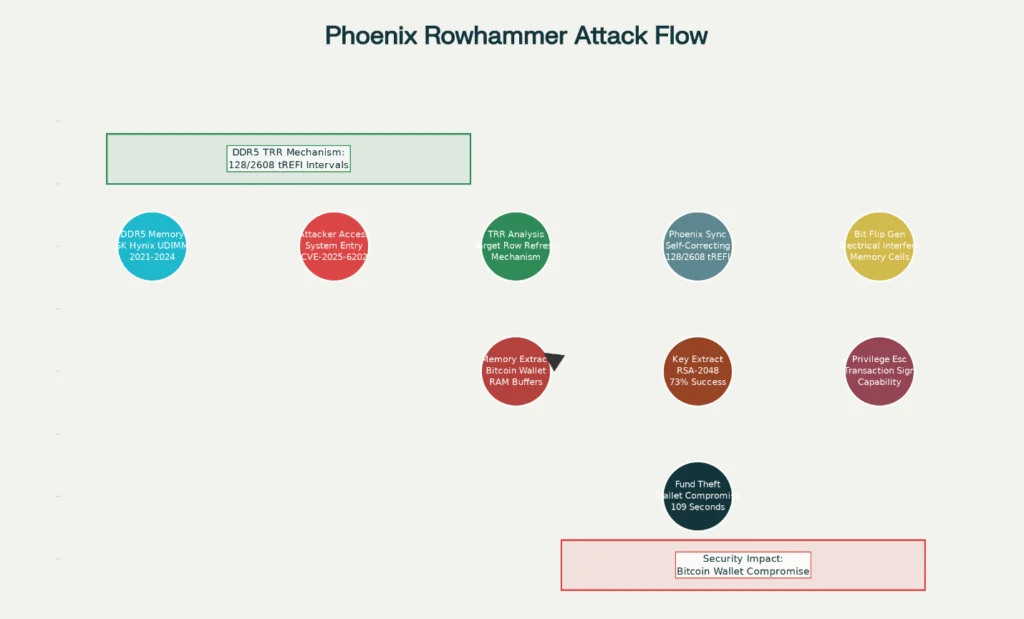
Among the critical examples of this class of threats, vulnerability CVE-2025-6202 , discovered in SK Hynix’s DDR5 memory, stands out . The Phoenix Rowhammer attack, which relies on this vulnerability, demonstrates the ability to bypass modern Target Row Refresh (TRR) memory protection mechanisms, creating so-called “blind spots” that enable controlled data corruption at the hardware level. Such flaws can be exploited to extract private keys from RAM, compromise cryptographic libraries, and modify system processes that secure digital wallets.
Furthermore, cryptographic security research shows that the combination of Phoenix Rowhammer with other types of attacks, such as the BitShredder Attack , Memory Phantom (CVE-2025-8217) , and Artery Bleed (CVE-2023-39910) , creates a multi-vector threat model in which an attacker can recover seed phrases, private keys, and passwords even after cryptographic operations are completed. The systemic nature of these vulnerabilities makes it impossible to completely mitigate the risk with software and highlights the need to develop new principles for hardware-based memory protection.
Thus, modern cryptocurrency wallets and digital asset infrastructure are under increasing pressure from hardware attacks previously considered theoretical. The importance of studying these attacks and developing countermeasures is fundamental to ensuring the integrity and resilience of the Bitcoin and other cryptocurrency ecosystems in the face of evolving next-generation threats.
Recent research conducted by the Computer Security Group (COMSEC) at ETH Zurich, in collaboration with Google, has identified a critical hardware vulnerability in DDR5 memory modules manufactured by SK Hynix, designated CVE-2025-6202 . The Phoenix Rowhammer attack poses an unprecedented threat to the security of Bitcoin cryptocurrency wallets, as it allows attackers to extract private keys from DDR5 memory by manipulating bits at the hardware level. The research demonstrated that all 15 tested SK Hynix DDR5 modules manufactured between 2021 and 2024 are vulnerable to this attack, posing a systemic threat to the security of cryptocurrency assets worldwide. thehackernews