
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-Tracker — With the help of this automated script, you will never lose track of recently released CVEs. | Kitploit
Tools/GitHubGitHub/cyb3r-techie/cve-tracker
Vulnerability AnalysisScripting & AutomationInformation Gathering
GitHubcyb3r-techie/cve-tracker

CVE-Tracker

With the help of this automated script, you will never lose track of recently released CVEs.

View Repository
5211444 years agoReviewed by Kitploit
Share

CVE-Tracker

With the help of this automated script, you will never lose track of newly released CVEs. What does this powershell script do is exactly running the Microsoft Edge at system startup, navigate to 2 URLs ,and then put the browser in to full screen mode.

As ethical hackers, it's vital that we keep track of the recently released CVEs in order to be fully aware of new threats or vulnerabilities out there in the Internet. Actually, it's a routine task in our day to day lives. So why don't we just automate the whole procedure of opening a browser and navigate to our sources for cheking the new CVEs? The purpose of this tool is to basically, automate the mentioned procedure with the help of powershell scripting.

Among all the online sources that are available which publish new CVEs, I've chosen the following 2 URLs and leveraged them in the script.

URLs
https://cvetrends.com/
https://cve.circl.lu/

If you want to change these URLs to your desired ones, you can simply open the cve.ps1 file with an editor and change the URLs there! Also remember that you can even add more URLs to the file.

Usage:

Download the zip file and unzip it on your system
If you haven't bypassed the script execution on your system, please do so with the command "Set-ExecutionPolicy -ExecutionPolicy Bypass" 
[Note: it needs to be run as administrator]
.\CVE_Track.ps1

Also, keep in mind the changes that are made to your system can easily be undone, by running the command .\undo.ps1

Technical Analysis:

At first, when you run the script, it will create a *.bat file (CVE_Track.bat) in the following directory that literally allows the automation procedure that we aim for. C:\Users\<UserName>\\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\ .

Also the file "cv.ps1" is coppied to the directory C:\Users\<UserName>\ and every time the system starts, it will be executed.

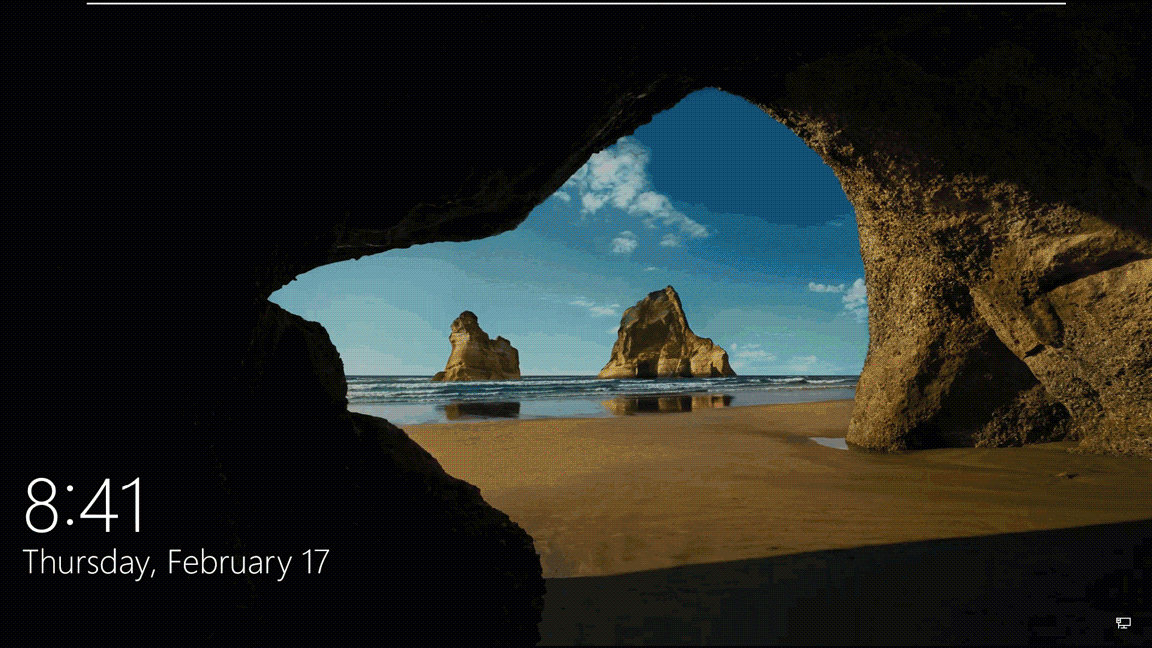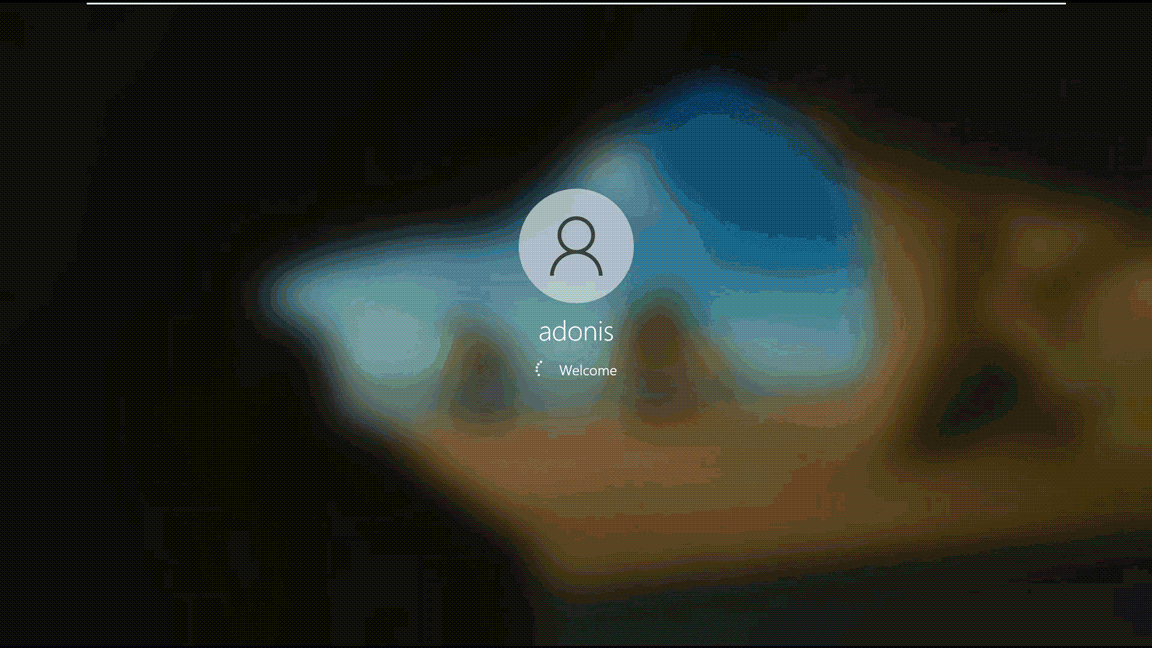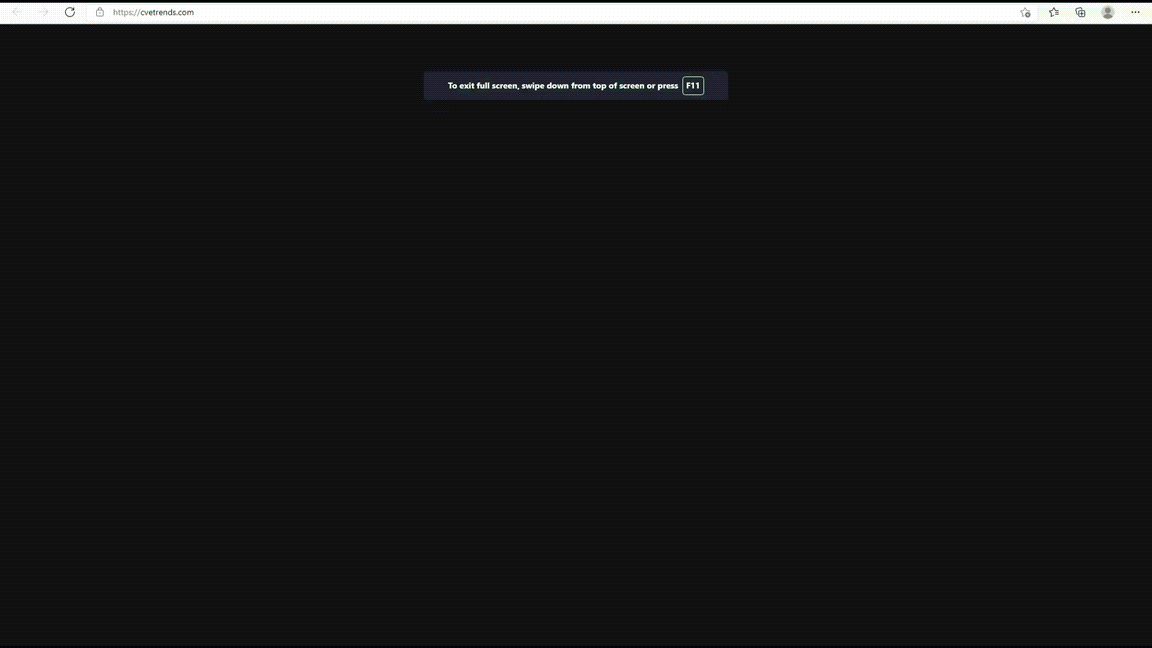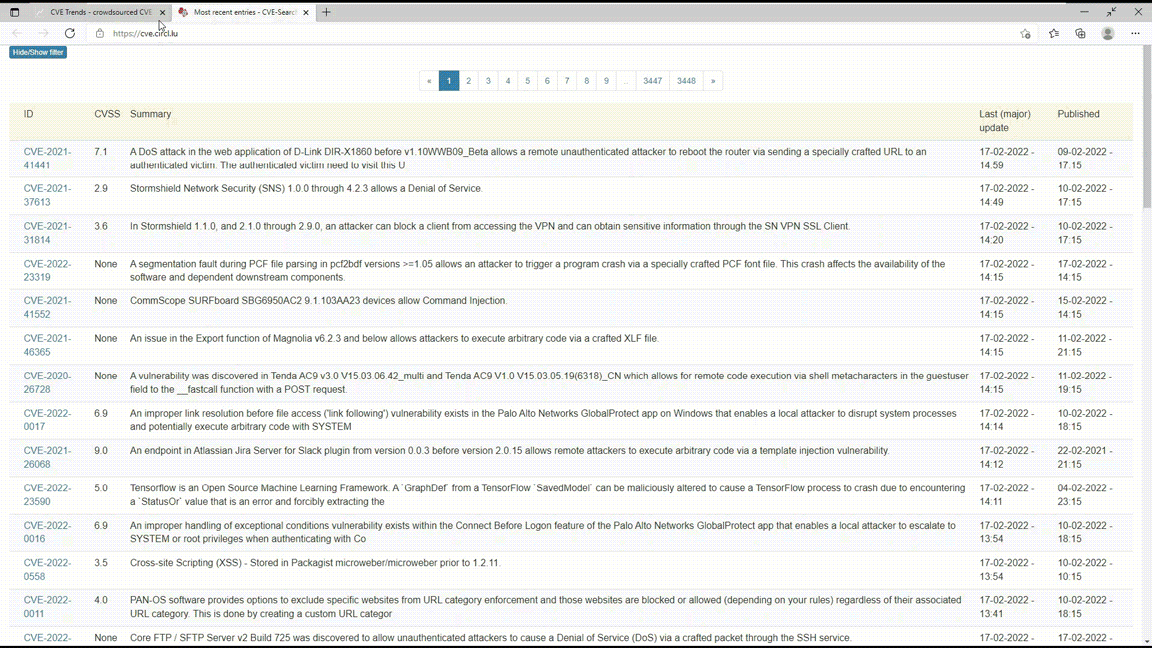
The script in action

After you've run the script, this is how it would look like when you login to your system after a restart.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools →






