
 completetech-security/sonicwall-sma1000-cve-2026-102258-check
Offline SonicWall SMA1000 evidence checker for CVE-2026-102258. Reported build and configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Standalone, offline checker for CVE-2026-102258: stored cross-site scripting in the AMC of SonicWall SMA1000 appliances (models 6210, 7210 and 8200v).
The checker reads builds and inventories that you supply and compares them with the vendor's published version table. It never contacts a target and never sends exploit payloads. Missing, qualified, custom, conflicting and uncovered evidence remains unknown.
Run these from a clone of the repository:
# Classify one reported build (prints JSON; exits 1 because this build is potentially affected)
python sonicwall_sma1000_cve_2026_102258_check.py --version 12.4.3-03526

# Assess the synthetic inventory and write a script-free HTML report
python sonicwall_sma1000_cve_2026_102258_check.py --inventory examples/inventory.example.json --format html --output report.html

# Show all options
python sonicwall_sma1000_cve_2026_102258_check.py --help

# Run the local-only test suite
python -m unittest -v
The synthetic inventory deliberately includes findings and unknowns, so its example command exits 1. --output refuses to overwrite an existing report.html unless --force is added.
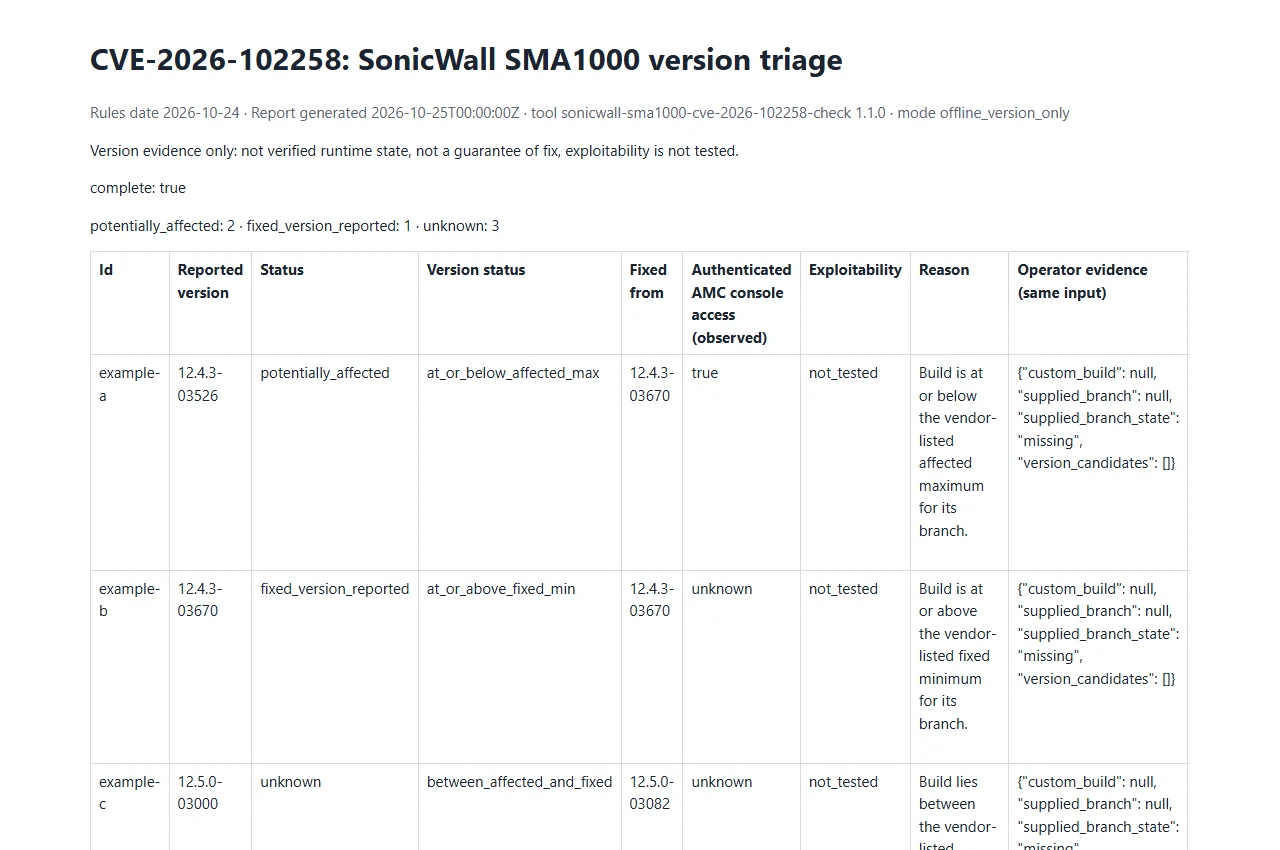
Open the synthetic example report. Example data only; this is not a live assessment.
Rules are dated 2026-10-24 and come from SonicWall's product notice (SNWLID-2026-0017).
| Branch | Affected through | Fixed from |
|---|---|---|
| 12.4.3 | 12.4.3-03526 | 12.4.3-03670 |
| 12.5.0 | 12.5.0-02952 | 12.5.0-03082 |
unknown, as are other branches and every value that cannot be parsed.12.4.3-3526 are read by build number. See the reference for details.python sonicwall_sma1000_cve_2026_102258_check.py [--version BUILD] [--branch BRANCH] [--model MODEL]
[--authenticated-console-access true|false|unknown] [--inventory FILE] [--csv-list FILE]
[--format json|csv|html] [--output FILE] [--force] [--strict]
At least one of --version, --inventory or --csv-list is required; otherwise the run is an operational error.
| Option | Purpose |
|---|---|
--version BUILD | A reported build in the strict form <major>.<minor>.<patch>-<build> (repeatable). |
--branch BRANCH | Optional branch cross-check for --version values. A branch that disagrees with the build gives unknown. |
--model MODEL | Optional model (6210, 7210 or 8200v) for --version values. An uncovered model gives unknown. |
--authenticated-console-access | Operator observation (true, false or unknown, default unknown) for --version values. It never changes the version assessment. |
--inventory FILE | JSON inventory: an object or array of entries with schema_version: 1 (repeatable). |
--csv-list FILE | CSV list with a header that includes version (repeatable). |
--format | json (default), csv or html. |
--output FILE | Write the report to a file instead of stdout. An existing file is not overwritten unless --force is given. |
--force | Allow --output to overwrite an existing file. |
--strict | Count unknown results as findings for the exit status. |
Input rules, in brief (the reference has the complete schema):
v, prerelease or vendor suffix. Only ASCII space, tab, CR and LF are trimmed.id (or label), version, version_candidates, branch, model, authenticated_console_access and custom_build. Wrong types or schema versions are operational errors.unknown.--force; use a new output path.Keep real inventories, reports and targets outside version control.
Each result carries a status:
status | Meaning |
|---|---|
potentially_affected | At or below the listed affected maximum for a listed branch. Not confirmed exploitability. |
fixed_version_reported | At or above the listed fixed minimum. Not a guarantee of patch state. |
unknown | Everything else. Never safe. |






