
 completetech-security/node-cve-2026-58039-check
Offline Node.js evidence checker for CVE-2026-58039: Permission Model process-report filesystem bypass. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline version-evidence checker for CVE-2026-58039 — Node.js: Permission Model process-report filesystem bypass.
It compares Node.js versions that an operator reports against the fixed releases named in the Node.js advisory, and writes a CSV, JSON or HTML report. It is a triage aid for version evidence, not a vulnerability scanner or an exploit tool.
unknown.exploitability: not_tested. A potentially_affected result is not confirmed exploitability, and fixed_version_reported is neither a safety guarantee nor deployed-patch attestation.node_cve_2026_58039_check.py can be copied on its own.# Assess one reported version and print JSON
python node_cve_2026_58039_check.py --version 22.23.2 --format json
# Assess an inventory and write an HTML report to a new file
python node_cve_2026_58039_check.py --inventory examples/inventory.example.json --format html --output report.html
# Assess a CSV list; exit 1 if any result is a finding
python node_cve_2026_58039_check.py --csv-list inventory.csv --fail-on-finding
# Help and tests
python node_cve_2026_58039_check.py --help
python -m unittest -v
At least one of --version, --inventory or --csv-list is required. Without --output, the report goes to stdout; the default format is csv.
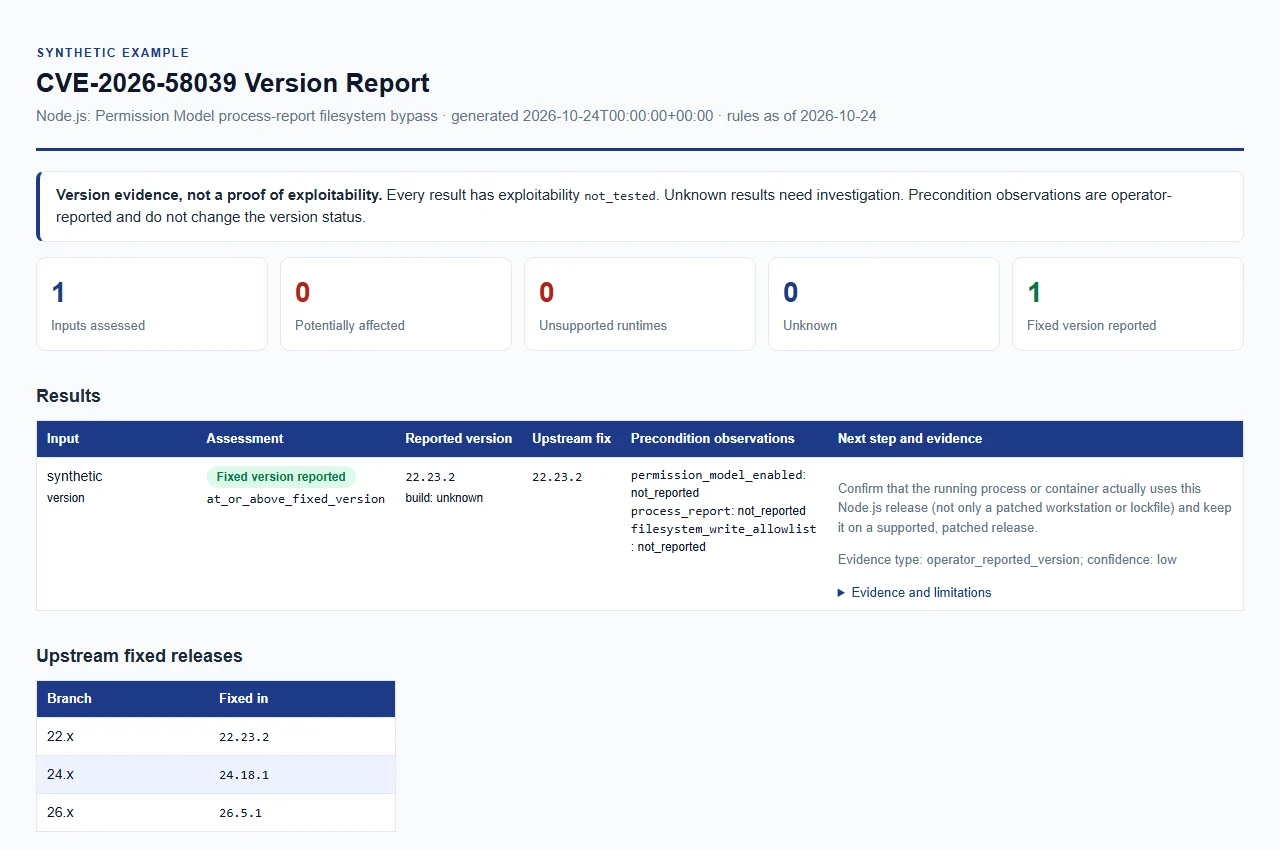
Open the synthetic example report. Example data only; this is not a live assessment.
| Option | Meaning |
|---|---|
--version VERSION (alias --node-version) | Assess an explicitly supplied Node.js version; a leading v is accepted. Repeatable; each value describes a separate runtime. |
--build-source SOURCE | Provenance of the --version builds, at most 512 characters. unknown (default), upstream, official and official_upstream (or an empty value) are compared as upstream builds; any other value is treated as a vendor or custom build and stays unknown. |
--permission-model-enabled, --process-report, --filesystem-write-allowlist | Each takes true or false. Operator observation applied to the --version inputs; it does not change the version result. |
--inventory FILE | JSON inventory (see Inventory formats). Repeatable. |
--csv-list FILE | CSV inventory. Repeatable. |
--format {csv,json,html} | Output format; default csv. All formats carry the same evidence. |
--output FILE | Write the report to a new file instead of stdout. The directory must already exist. |
--force | Replace an existing output file. Without it, existing reports are protected. Input files are never overwritten, even with --force. |
--brand NAME | Organization name shown in the HTML report, at most 512 characters; default CompleteTech LLC. |
--fail-on-finding | Exit 1 when any result is potentially_affected or unsupported_runtime. |
--tool-version | Print the checker name and version. Note that --version is the Node.js version to assess, not the checker version. |
Reviewed 2026-10-24 against the official release advisory and the linked fixed releases.
| Node.js major | Fixed version |
|---|---|
| 22.x | 22.23.2 |
| 24.x | 24.18.1 |
| 26.x | 26.5.1 |
The vendor does not specify an introduced version in the release advisory. For each listed major, versions below its fixed version require remediation. Unlisted, custom/backported and prerelease builds need explicit evidence; do not label unknown builds safe.
| Status | Meaning |
|---|---|
potentially_affected | A reported plain version is below the fixed version of its listed major. It needs remediation review. |
fixed_version_reported | The reported plain version is the listed fixed version or a later one on the same major. This is a reported version, not deployed-patch attestation. |
unsupported_runtime | The reported major is end-of-life in the Node.js release schedule (majors 0, 4–21, 23 and 25 as reviewed 2026-10-24; major 0 is an inference). This is upgrade guidance, not a claim that this particular flaw exists in every historical build. |
unknown | Evidence is missing or unclassifiable: no version, conflicting versions, prerelease or otherwise qualified versions, vendor/backported/custom builds (which require vendor evidence), or active/future majors not covered by this rule snapshot. |
Each result also carries a more specific version_status: below_fixed_version, at_or_above_fixed_version, unsupported_release_line, release_line_not_in_rules, vendor_build_unverified, qualified_version_unverified, unrecognized_or_partial_version, conflicting_versions or version_not_disclosed. A reported vendor or custom build source takes precedence: it yields unknown even when the version number would otherwise classify.
Operator-supplied observations never change the version result or establish reachability. They are recorded as reported_true, reported_false or not_reported.






