
 completetech-security/node-cve-2026-106071-check
Offline Node.js evidence checker for CVE-2026-106071: Permission Model wildcard path over-grant. Single-file Python; JSON/CSV/HTML reports; no exploit payloads.





Offline evidence checker for CVE-2026-106071 — Node.js: Permission Model wildcard path over-grant. It compares operator-reported Node.js versions with the fixed release named in the vendor advisory and reports what that evidence does and does not support.
unknown. A public URL is not an inventory.exploitability: not_tested.Requirements: Python 3.10 or newer. Nothing needs to be installed.
Supply an exact version taken from the deployed process (for example from the running container or service), not from a workstation or lockfile:
python node_cve_2026_106071_check.py --version 26.12.1 --format json
Assess a JSON inventory and write an HTML report, or fail a pipeline on findings:
python node_cve_2026_106071_check.py --inventory examples/inventory.example.json --format html --output report.html
python node_cve_2026_106071_check.py --csv-list inventory.csv --fail-on-finding
Show all options and run the local-only test suite:
python node_cve_2026_106071_check.py --help
python -m unittest -v
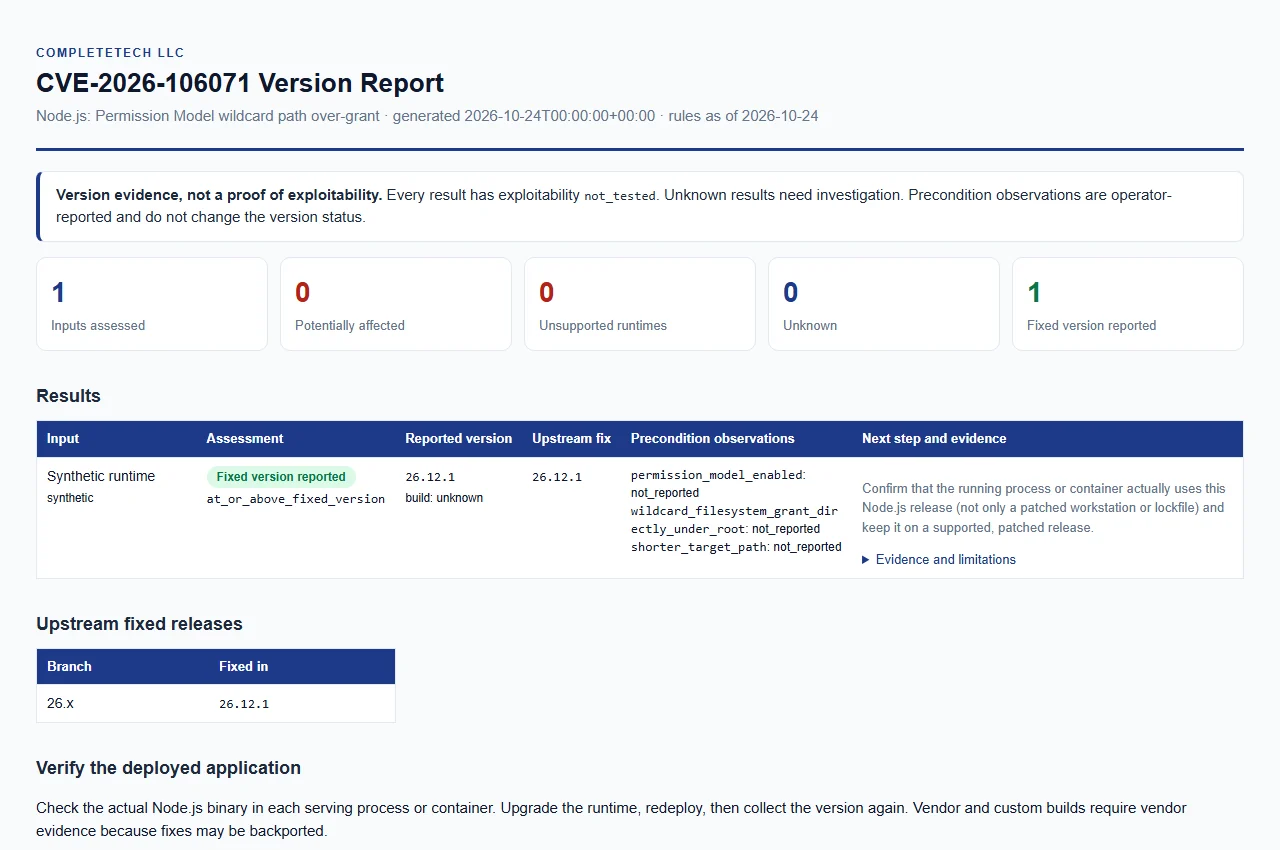
Open the synthetic example report. Example data only; this is not a live assessment.
Reviewed 2026-10-24 against the official release advisory and the linked fixed release. The rule snapshot date is reported as rules_as_of.
| Node.js major | Fixed version |
|---|---|
| 26.x | 26.12.1 |
How a plain, official-upstream version (an optional leading v is accepted) is classified:
| Reported version | Status |
|---|---|
| Below the fixed version on a listed major | potentially_affected |
| The fixed version or a later plain version on the same listed major | fixed_version_reported |
| A major past end-of-life in the Node.js release schedule | unsupported_runtime |
| Any other major, or missing, malformed, prerelease, conflicting or vendor/custom/backported evidence | unknown |
potentially_affected.unsupported_runtime is upgrade guidance for end-of-life lines. It is not a claim that this particular flaw exists in every historical build. The end-of-life list comes from the Node.js release schedule, reviewed 2026-10-24.unknown.build_source other than blank, unknown, upstream, official or official_upstream (for example a distribution or vendor name) yields unknown. Vendor, backported and custom builds need vendor evidence.| Status | Meaning |
|---|---|
potentially_affected | The reported version needs remediation review. It is not confirmed exposure or exploitability. |
fixed_version_reported | The reported version is at or above the upstream fixed release. This is a reported version, not deployed-patch attestation or a safety guarantee. |
unsupported_runtime | The major is end-of-life; migrate to a supported, fixed release. |
unknown | Evidence is missing or unclassifiable. Missing metadata does not show a runtime is unaffected. |
Each result also has a more specific version_status, evidence_type: operator_reported_version, and a low (or, for unknown, insufficient) evidence_confidence. Version metadata is not a patch or build signature.
You may record three operator-supplied observations alongside a version. They are kept separate: they never change the version result and never establish reachability.
| Observation | Meaning |
|---|---|
permission_model_enabled | permission model enabled |
wildcard_filesystem_grant_directly_under_root | wildcard filesystem grant directly under root |
shorter_target_path | shorter target path |
Each is true, false or not reported, and appears in reports as reported_true, reported_false or not_reported.
There is no automatic scan. Provide at least one of --version, --inventory or --csv-list.






