Offline NetScaler ADC / Gateway evidence checker for CVE-2026-19489. Reported firmware and configuration evidence. Standalone Python; JSON/CSV/HTML reports; no exploit payloads.





Offline triage of operator-reported NetScaler builds against CVE-2026-19489 (NetScaler ADC / Gateway: LSN SIP ALG memory corruption). The checker compares build, variant and configuration evidence that you supply with the vendor's fixed builds. It is a single standalone Python 3.10+ script using only the standard library.
It is fully offline: there is no appliance access, application execution, exploit payload or network mode. Passive network metadata cannot establish a running firmware build or configuration, so a network mode is deliberately omitted.
This repository covers CVE-2026-19489 only, following the reporting conventions of node2shell-check and php2shell-check.
potentially_affected is not confirmed exploitability.fixed_version_reported reports a version at or above the vendor's fixed build. It is not a verified deployed patch or a safety guarantee.unknown is never safe. Missing, malformed or conflicting evidence stays unknown.exploitability: not_tested. Nothing is exploited or tested, and no deployed appliance was assessed.Python 3.10 or later. No installation or third-party dependencies are required; use python3 where that is your interpreter name.
# One reported build (JSON to stdout)
python netscaler_cve_2026_19489_check.py --version 14.1-73.31 --variant standard

# The synthetic example inventory as an HTML report
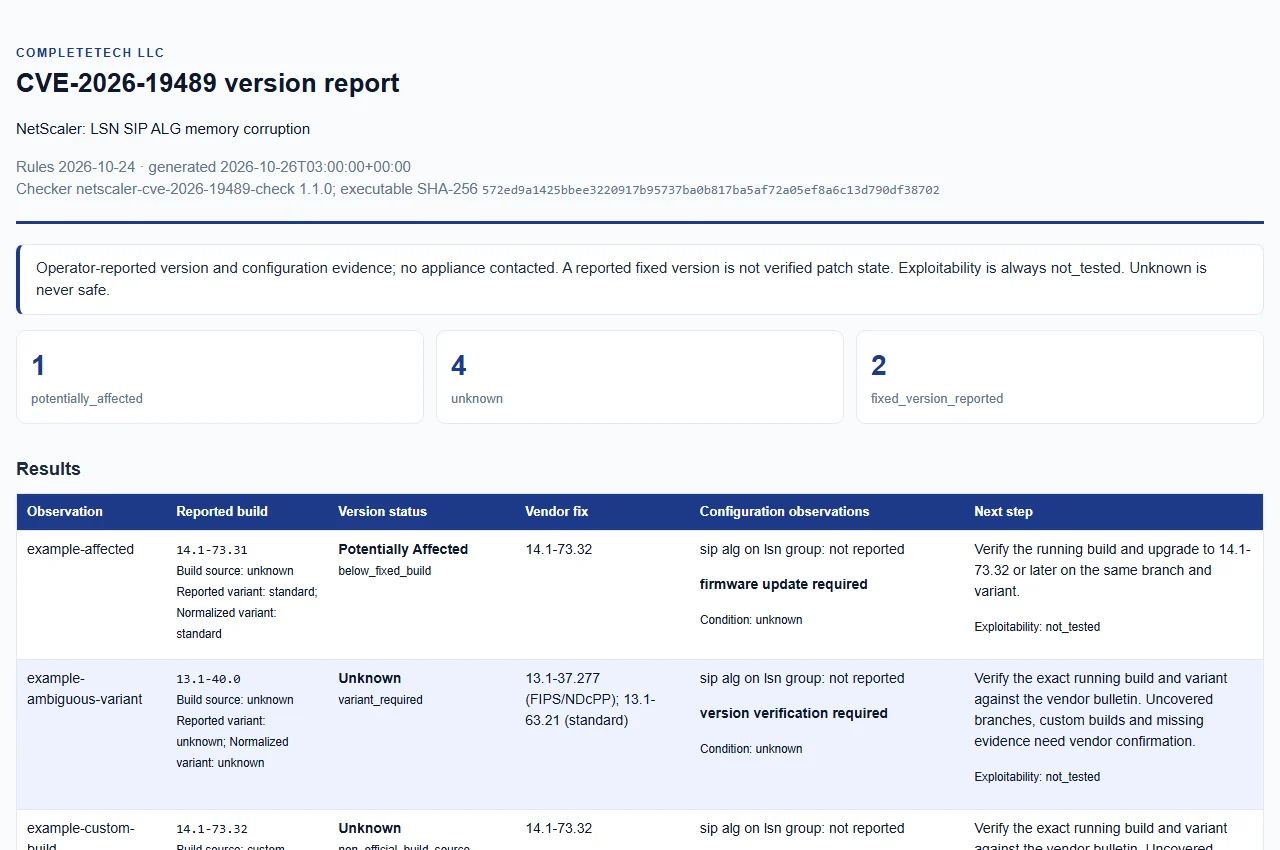
python netscaler_cve_2026_19489_check.py --inventory docs/example-inventory.json --format html --output report.html

# A CSV inventory as JSON, exiting 1 if any firmware is potentially affected
python netscaler_cve_2026_19489_check.py --csv-list inventory.csv --format json --fail-on-finding
--help lists every option and --tool-version prints the checker version. Inputs (--version, --inventory, --csv-list) can be combined and repeated. Reports go to stdout unless --output FILE is given; an existing report is refused unless --force is supplied.
Affected means strictly before the fixed build for the same branch and variant. No lower bound or lifecycle conclusion is invented.
| Branch and variant | Vendor fixed build |
|---|---|
| 14.1 standard | 14.1-73.32 |
| 13.1 standard | 13.1-63.21 |
| 14.1 FIPS | 14.1-73.32 |
| 13.1 FIPS/NDcPP | 13.1-37.277 |
unknown.unknown where the standard and FIPS/NDcPP comparisons disagree; the fixed-build field then lists each variant's threshold.unknown.Accepted build spellings include 14.1-73.37, 14.1.73.37 and NS14.1: Build 73.37.nc, optionally marked FIPS or NDcPP before an optional nc marker. Supply only the build text, not a full show version line.
| Input | Use |
|---|---|
--version BUILD | A reported build; repeatable. --variant standard|fips|ndcpp and --build-source apply to every CLI build. |
--inventory FILE | Strict UTF-8 JSON object or non-empty array; repeatable. Requires integer schema_version: 1 and string version (empty is unknown). Optional: label, variant, build_source, version_candidates (at most 16 strings; disagreement is unknown) and observation fields. |
--csv-list FILE | UTF-8 CSV with a required version header; repeatable. Optional label, variant, build_source and observation columns. schema_version and version_candidates are JSON-only. |
Only empty, unknown, official and citrix build provenance allow a comparison; any other provenance yields unknown. Extra fields, duplicate keys, wrong types, ragged CSV rows and malformed quoting are errors. A run accepts up to 100 input files, 10,000 observations, 4 MiB per file and 512 characters per string. Inputs must be regular files; archives and directory trees are never opened. The reference defines the full input contract, parser rules and limits.
Supply explicit observations as true, false or unknown CLI flags, JSON booleans/null or documented CSV values. They remain separate from version status, never change it, and do not prove reachability. No local configuration or process data is collected.
| CLI observation | Meaning | Exposure condition expects |
|---|---|---|
--sip-alg-on-lsn-group | SIP ALG is enabled on an LSN group | true |
precondition_status summarizes only these operator observations (conditions_observed, condition_not_observed or unknown) and is never a verified exposure or a clean result.
Choose --format json (default), csv or html. HTML is a self-contained, escaped, script-free document with no remote assets. CSV is formula-safe, with a record_type column that distinguishes result rows from the summary row emitted for a zero-result report. A synthetic example input and generated report describe no real systems.