
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/brunoteixeira1996/cve-2023-36250
Vulnerability AnalysisExploitationWeb Application ExploitationPapers & ResearchLearning & Education
GitHubbrunoteixeira1996/cve-2023-36250

CVE-2023-36250

Proof-of-concept for CSV injection in GNOME Time Tracker 3.0.2, demonstrating arbitrary code execution via crafted .tsv files and formula injection.

View Repository
31253 years agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    546
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    377
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    324
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    269
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    252

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2023-36250

CSV Injection vulnerability in GNOME time tracker version 3.0.2, allows local attackers to execute arbitrary code via crafted .tsv file when creating a new record.

Vulnerability Type

CSV Injection

Discoverer

Bruno Teixeira

Reference

http://gnome.com

Affected Product Code Base

GNOME time tracker v3.0.2

PoC

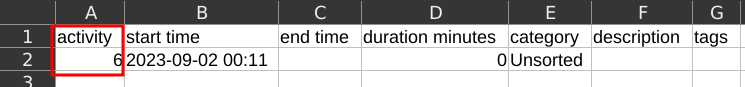
Creating a new record using a fomrula (=3+3) in the cmdline field, creates a way to inject formulas when exporting to .tsv. With this, when someone extract this .tsv file, the sheet software will evaluate as a valid formula and it will execute it. Note that this is just a sum operation but it's possible to load software that resides on the victim machine, or even create a malicious hyperlink.

image

image

Download Tool






