

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-21962 β€” Advisory for CVE-2026-21962, a critical unauthenticated authentication bypass in Oracle HTTP Server and WebLogic proxy plug-ins, with affected versions, detection indicators, and mitigation guidance. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-21962
Defensive ToolsVulnerability AnalysisWeb SecurityThreat IntelligenceAuthentication
GitHubashrafzaryouh/cve-2026-21962

CVE-2026-21962

Advisory for CVE-2026-21962, a critical unauthenticated authentication bypass in Oracle HTTP Server and WebLogic proxy plug-ins, with affected versions, detection indicators, and mitigation guidance.

Share
View Repository
216 months agoNot yet reviewed

🚨 CVE-2026-21962 - Critical Authentication Bypass Vulnerability

Oracle_logo svg

CVE Severity CVSS Attack Vector Privileges User Interaction

🧾 Summary

πŸ”₯ A maximum severity (10.0) vulnerability enabling unauthenticated remote access to Oracle middleware systems.


CVE ID        : CVE-2026-21962
Severity      : CRITICAL
Published     : 2026-01-20
Category      : Authentication Bypass
CWE           : CWE-284 (Improper Access Control)


🧠 Technical Insight

- Authentication boundary is improperly enforced
- Crafted HTTP requests bypass access control
+ Direct access to protected backend resources

⚑ No login required β€” attacker interacts directly with exposed services.
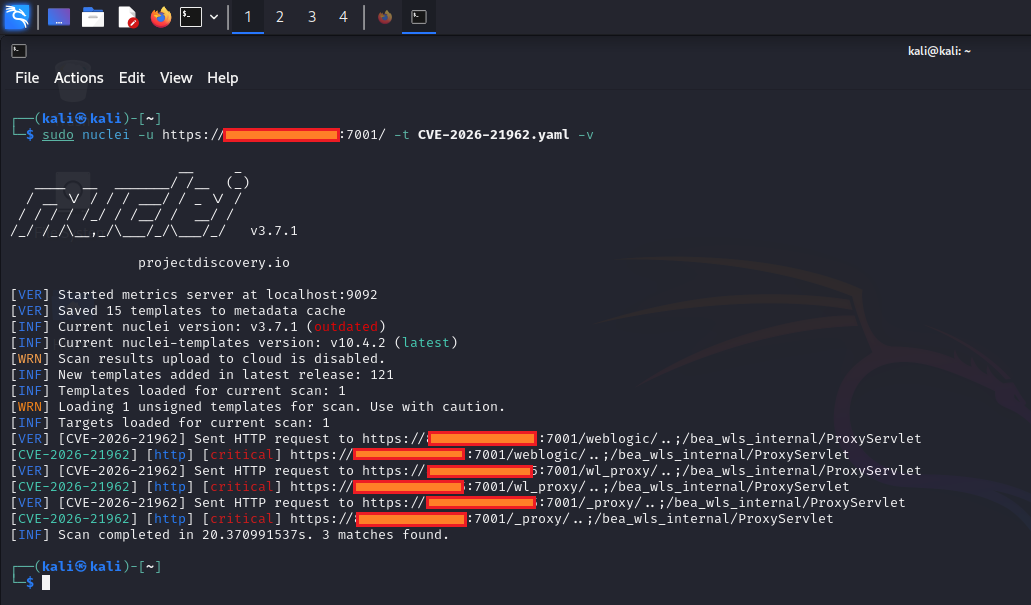
CVE-2026-21962

⚠️ Impact

+ Full unauthorized access to application data
+ Data tampering or deletion
+ Backend system exposure through proxy chain
+ Potential lateral movement across services

🌐 Attack Profile

AttributeValue
🌍 VectorNetwork
βš™οΈ ComplexityLow
❌ Privileges RequiredNone
πŸ‘€ User InteractionNone
πŸ”„ ScopeChanged

πŸ“¦ Affected Systems

πŸ“‚ Click to expand

πŸ–₯️ Oracle HTTP Server

  • 12.2.1.4.0
  • 14.1.1.0.0
  • 14.1.2.0.0

πŸ”Œ WebLogic Proxy Plug-in

Apache

  • 12.2.1.4.0
  • 14.1.1.0.0
  • 14.1.2.0.0

IIS

  • 12.2.1.4.0

πŸ›‘οΈ Mitigation Strategy

βœ… Primary Fix

+ Apply latest Oracle Critical Patch Update (Jan 2026)

🧯 Defense-in-Depth

# Reduce exposure
- Restrict proxy endpoints
- Limit external access
- Enforce network segmentation

# Detection & monitoring
- Enable HTTP request inspection
- Log and analyze anomalies
- Deploy WAF protections

πŸ” Detection Indicators

+ Unexpected HTTP requests to proxy endpoints
+ Access without authentication tokens
+ Irregular request patterns or headers
+ Sudden spikes in backend responses

πŸ“Š Risk Matrix

FactorRating
πŸ”₯ SeverityCRITICAL
⚑ ExploitabilityHIGH
πŸ’₯ ImpactMAXIMUM

🧬 Exploit Characteristics

Entry Point   : HTTP Request
Attack Type   : Remote
Auth Needed   : No
Skill Level   : Low

⚑ TL;DR

🚨 Internet-exposed systems are at immediate risk. πŸ”“ Authentication can be completely bypassed. πŸ› οΈ Patch immediately or isolate affected services.


🧩 Visual Threat Flow

[ Attacker ]
      β”‚
      β–Ό
[ Crafted HTTP Request ]
      β”‚
      β–Ό
[ Proxy Bypass ]
      β”‚
      β–Ό
[ Backend Access ]
      β”‚
      β–Ό
[ Data Compromise ]

🏁 Final Note

- This vulnerability requires immediate attention
- Delayed patching significantly increases risk
+ Treat as actively exploitable in real-world scenarios

Download Tool

Most Popular

View all β†’

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurityβ€”where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

Explore all tools

Browse our collection of tools

View all tools β†’





