 ashrafzaryouh/cve-2026-114595
Advisory for CVE-2026-114595, a critical integer overflow in EPICS Base (≤7.0.10) enabling memory corruption, DoS, and potential unauthenticated RCE; includes CVSS details and fixes.

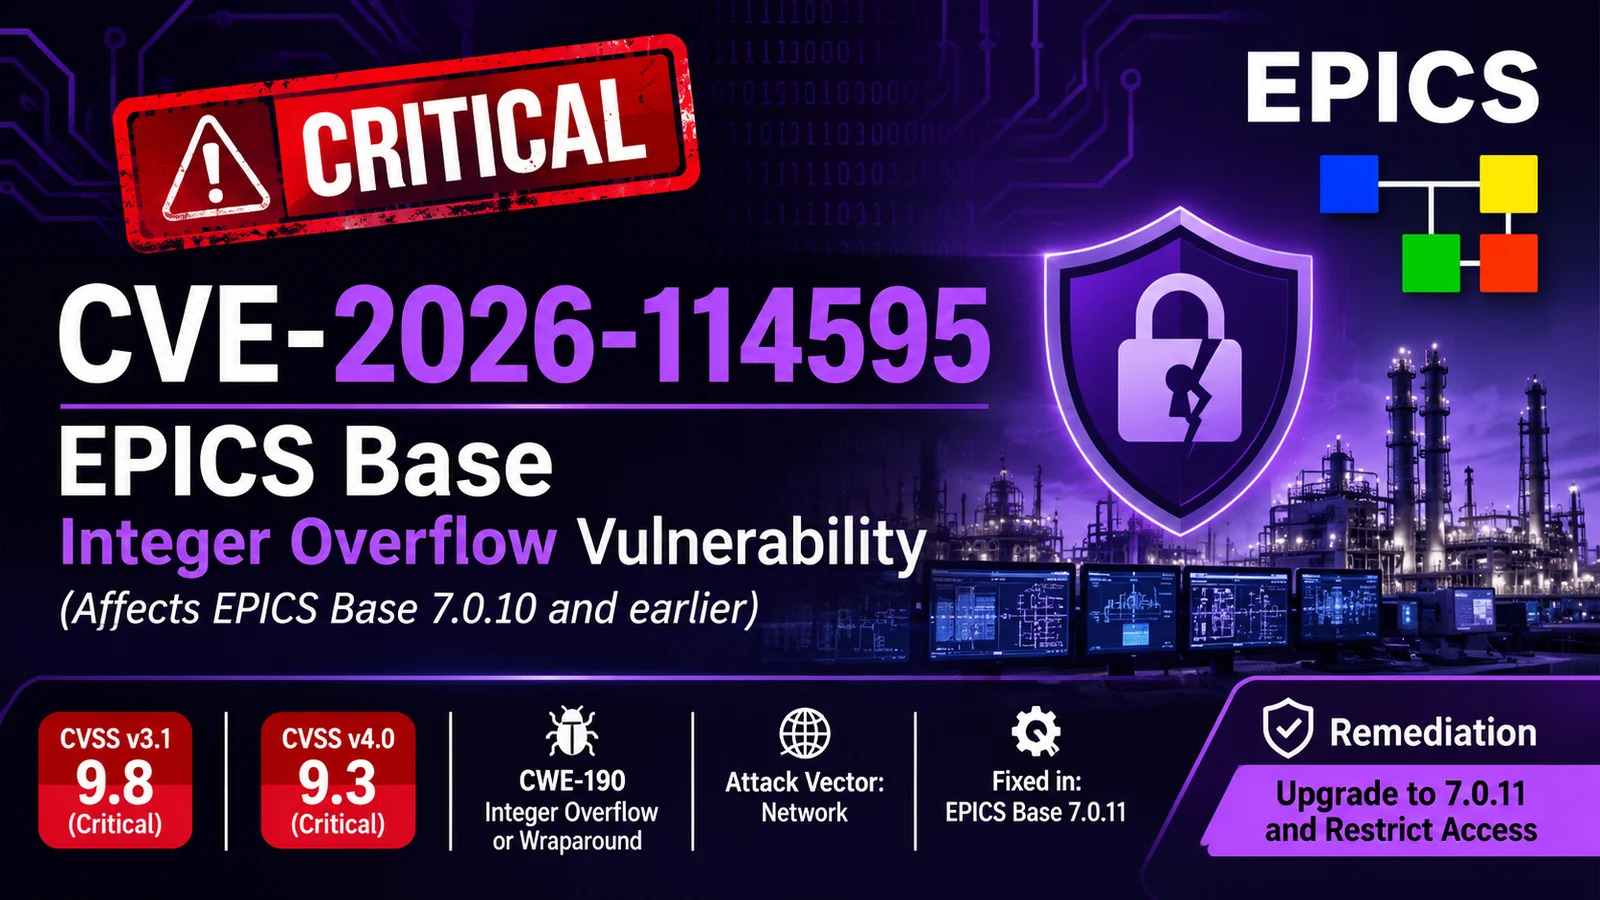


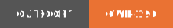
An overview, advisory details, and mitigation guidelines for CVE-2026-114595, a critical integer overflow vulnerability in EPICS Base (Experimental Physics and Industrial Control System).
In EPICS Base release 7.0.10 and prior, an integer overflow in network request processing can cause memory to be allocated with an incorrect size. Subsequent handling of attacker-supplied data may result in memory corruption, denial of service, or potential remote code execution.
This vulnerability is remotely exploitable over the network with no authentication or user interaction required.
| Vendor | Product | Affected Versions | Fixed Version |
|---|---|---|---|
| The EPICS Community | EPICS Base | ≤ 7.0.10 (all prior) | 7.0.11 |
EPICS (Experimental Physics and Industrial Control System) is a widely used open-source toolkit for building distributed control systems. It powers major scientific facilities worldwide, including particle accelerators, synchrotrons, and fusion experiments (e.g., ITER).
An attacker who can send crafted network requests to an EPICS Base process can trigger an integer overflow during request size calculation. This leads to an undersized memory allocation, enabling subsequent out-of-bounds writes when attacker-controlled data is processed.
| Version | Score | Severity | Vector String |
|---|---|---|---|
| 3.1 | 9.8 | Critical | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H |
| 4.0 | 9.3 | Critical | CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N |
Successful exploitation may allow a remote unauthenticated attacker to:
Because EPICS is used in critical scientific and industrial control environments, successful attacks could disrupt experiments or affect operational safety.
Upgrade to EPICS Base 7.0.11 or later.
The EPICS Community has released fixes in the official repositories:
For additional guidance, contact the EPICS Controls support team.
This CVE is part of a set of four issues disclosed in CISA advisory ICSA-26-300-01:
| CVE | Severity | Description |
|---|---|---|
| CVE-2026-114595 | Critical (9.8) | Integer overflow → potential RCE |
| CVE-2026-114596 | High (8.2) | Improper message length validation |
| CVE-2026-114597 | High (7.5) | Insufficient bounds checking |
| CVE-2026-114598 | High (7.5) | Type confusion |
All are fixed in EPICS Base 7.0.11.
| Date | Event |
|---|---|
| 2026-10-27 | CISA publishes ICSA-26-300-01 |
| 2026-10-27 | EPICS Base 7.0.11 released with fixes |
| 2026-10-27 | CVE-2026-114595 published |
This document is provided for informational and educational purposes. Always verify details against official sources (CISA, NVD, EPICS Community) before taking action in production environments.
Last updated: October 28, 2026






