
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-54880 — CVE-2024-54880 | Kitploit
Tools/GitHubGitHub/ailenye/cve-2024-54880
Vulnerability AnalysisWeb Application ExploitationPenetration TestingAuthenticationLearning & Education
GitHubailenye/cve-2024-54880

CVE-2024-54880

CVE-2024-54880

View Repository
611 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

I. Project overview

itemcontentremark
Authorized penetration rangehttp://192.168.88.141/Local test
Source code downloadhttps://www.seacms.net/SeaCMS_V13.1_install_f.zipOpen source project
Scope of vulnerabilitySeaCMS_V13.1

I. Vulnerability description

1. Logic vulnerability - Registering accounts in bulk

categorycontentremark
Vulnerability location (URL)http://192.168.200.141/reg.php?action=reg
Vulnerability typeLogic flaw
Vulnerability descriptionSeaCMS has a logical flaw that could be exploited by an attacker to allow any user to register accounts in bulk

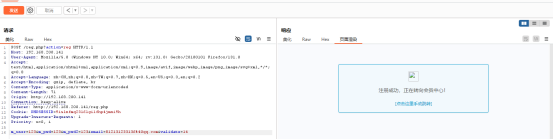
Visit the registration page and click Register to capture the request (this is a screenshot added later)
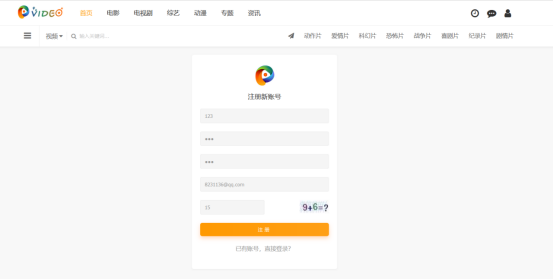
image-20241228231116461

*The verification code here is 14*

image-20241228231126473

*Change the account number and email address*
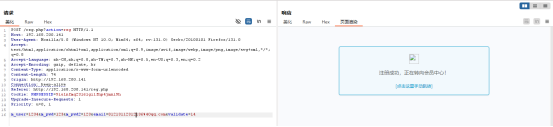
image-20241228231135449

*Try logging in to the first account here*
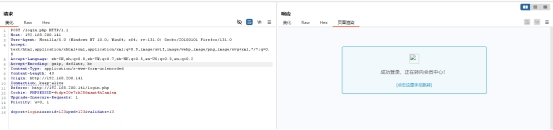
img

*Try to log in to the second account*
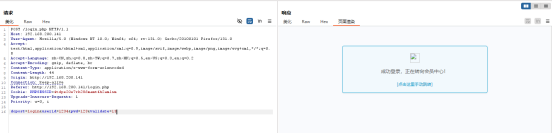
image-20241228231151045

Download Tool