
 #1
Tools for testing, exploiting, and securing web applications and APIs.
Kitploit recommended
 jas502n/cve-2018-3191
Exploit for CVE-2018-3191 targeting Oracle WebLogic Server via T3 protocol, enabling unauthenticated remote code execution with JNDI payload…
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 vainlystrain/vailyn
A phased, evasive Path Traversal + LFI scanning & exploitation tool in Python
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 malwaretech/citrixhoneypot
Detect and log CVE-2019-19781 scan and exploitation attempts.
 theblackturtle/fprobe
Take a list of domains/subdomains and probe for working http/https server.
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 dsecuredcom/ffufpostprocessing
Golang tool which helps dropping the irrelevant entries from your ffuf result file.
 jimywork/certstreamcatcher
This tool is based on regex with effective standards for detecting phishing sites in real time using certstream and can also detect punycode (IDNA)…
 svdwi/oswe-labs-poc
Dockerized labs For Web Expert (OSWE) certification. Preparation for coming AWAE Training ...
 malqr/malqr.github.io
MalQR is a collection of malicious QR Codes and Barcodes you can use to test the security of your scanners.
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 trufflesecurity/of-cors
Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.
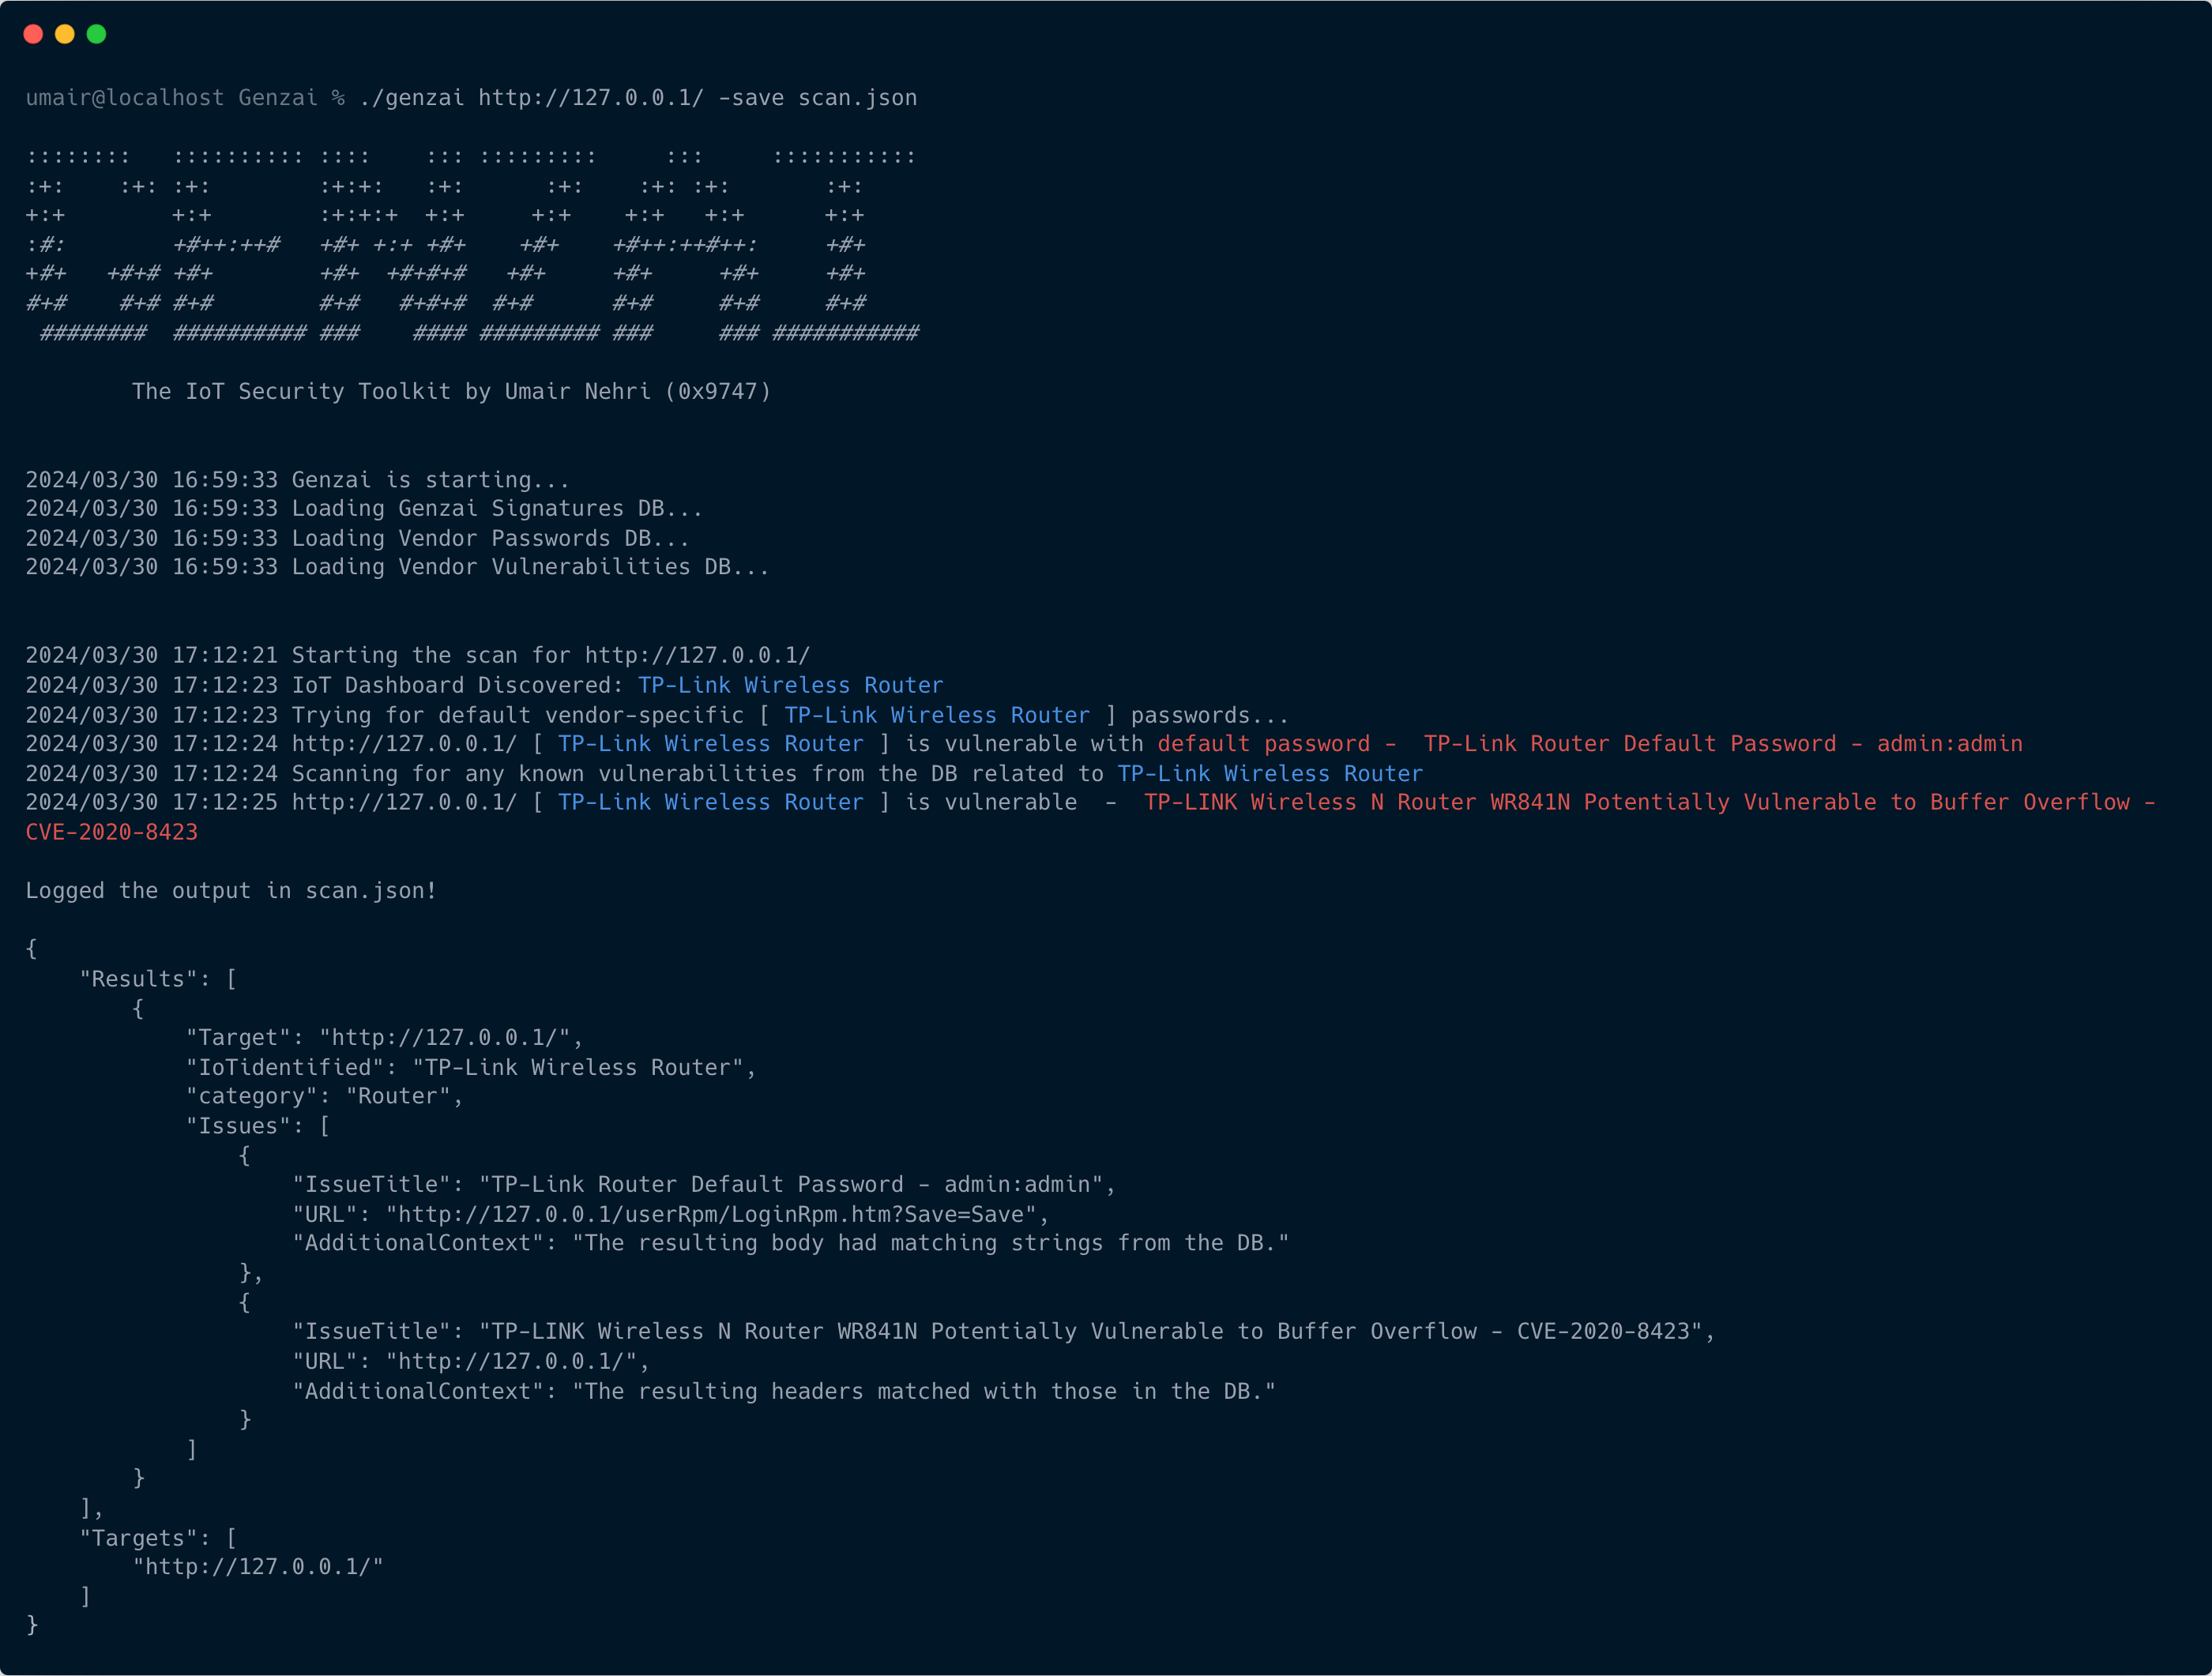 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 0xdevrel/easyscan
Python-based web security scanner that analyzes HTTP headers, SSL/TLS, DNS records, and common misconfigurations to generate a scored security report…
 huntergregal/scansploit
Exploit using barcodes, QRcodes, earn13, datamatrix








