
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 hancheng-lei/hacking-vulnerability-cve-2020-1938-ghostcat
Case study and exploit demonstration for CVE-2020-1938 (Ghostcat) Apache Tomcat vulnerability, including analysis and proof-of-concept code.
 3ndg4me/cve-2020-3452-exploit
Just basic scanner abusing CVE-2020-3452 to enumerate the standard files accessible in the Web Directory of the CISCO ASA applicances.
 fairyming/cve-2020-9548
CVE-2020-9548:FasterXML/jackson-databind 远程代码执行漏洞
 bmth666/geoserver-tools-cve-2024-36401
CVE-2024-36401 图形化利用工具,支持各个JDK版本利用以及回显、内存马实现
 1337g/cve-2017-17215
CVE-2017-17215 HuaWei Router RCE (NOT TESTED)
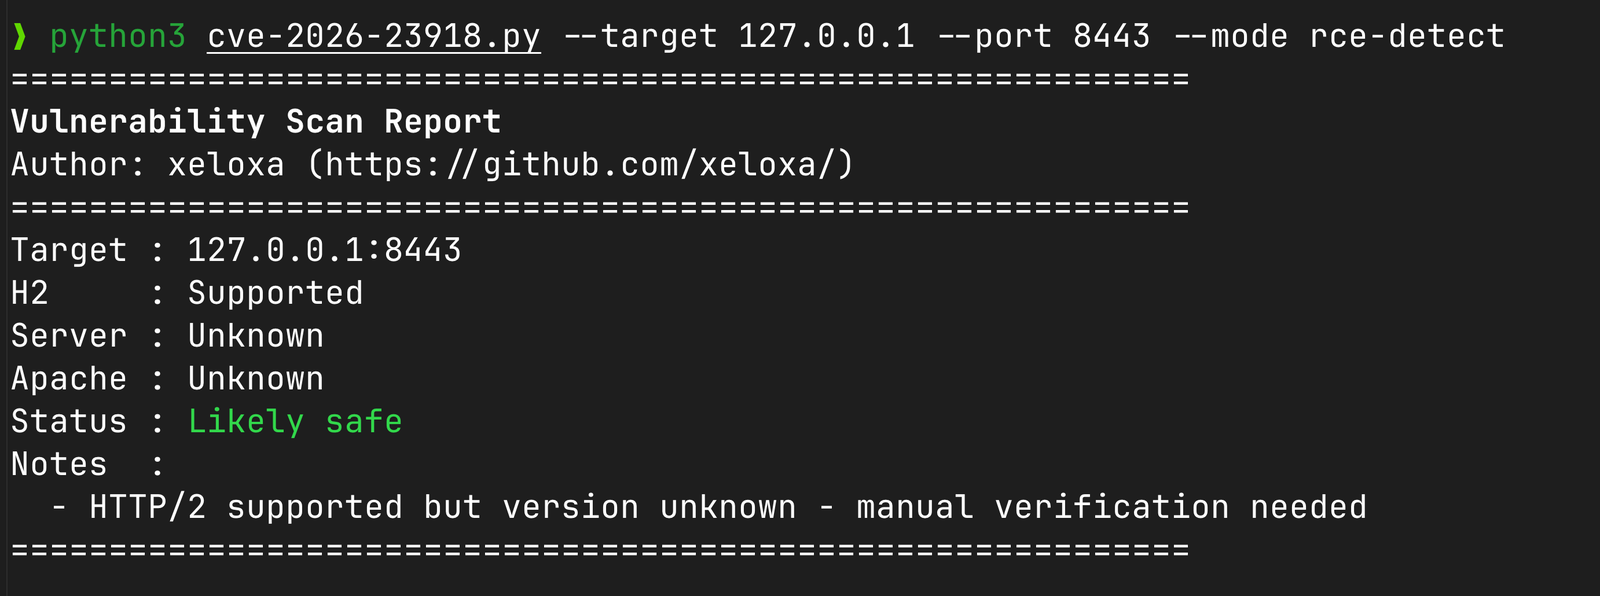 xeloxa/cve-2026-23918-apache-h2-poc
Proof-of-Concept exploit for CVE-2026-23918 (Apache mod_http2 double-free). Features multi-mode DoS (Rapid-RST, Slow-Drip) and passive…
 nccgroup/readable-thrift
Human-friendly Thrift encoder/decoder
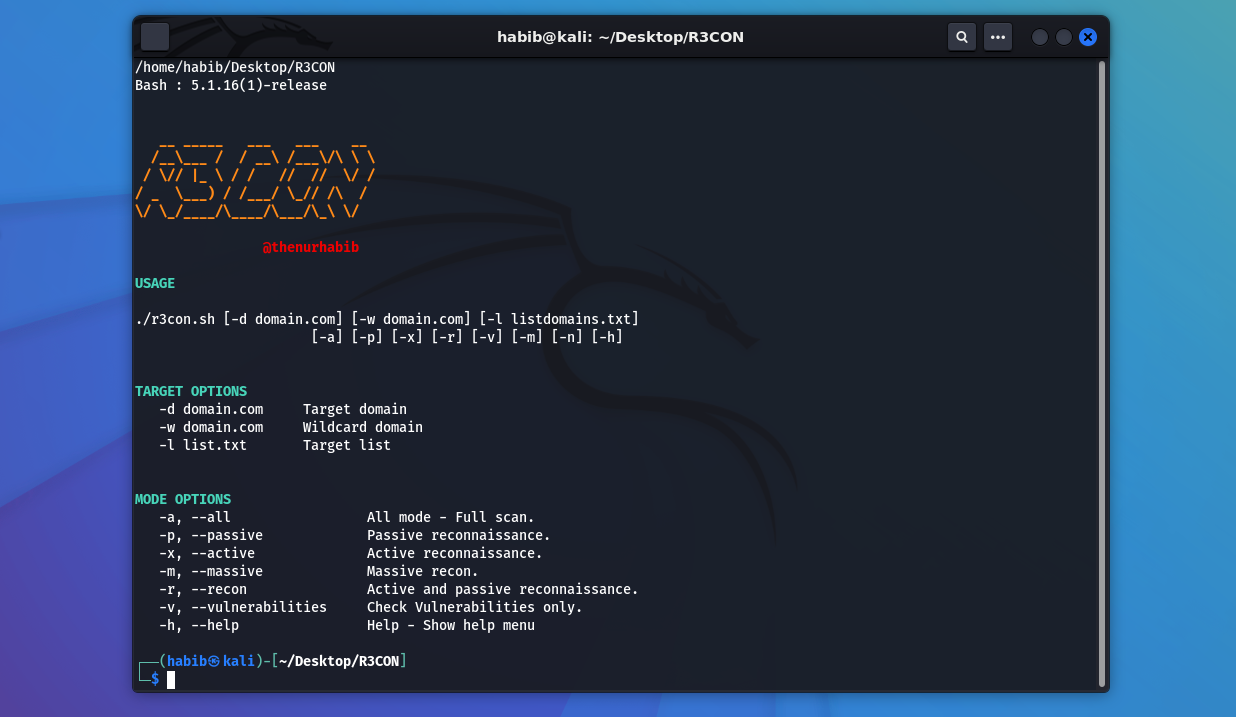 thenurhabib/r3con
Multi-functional Web Recon & Vulnerability Scanner Tool
 invicti-security/web-inf-path-trav
Tool for helping in the exploitation of path traversal vulnerabilities in Java web applications
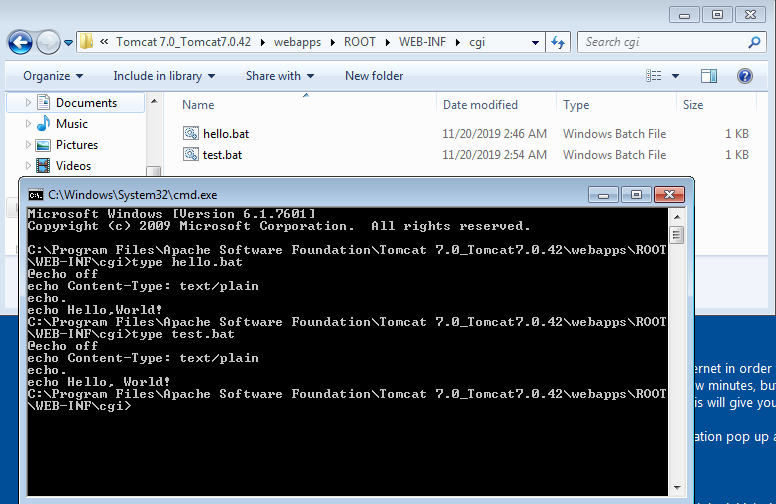 setrus/cve-2019-0232
CVE-2019-0232-Remote Code Execution on Apache Tomcat 7.0.42
 al1ex/cve-2020-17530
S2-061 CVE-2020-17530
 w0rty/cve-2021-39165
Github repository which contains a functional exploit for CVE-2021-39165
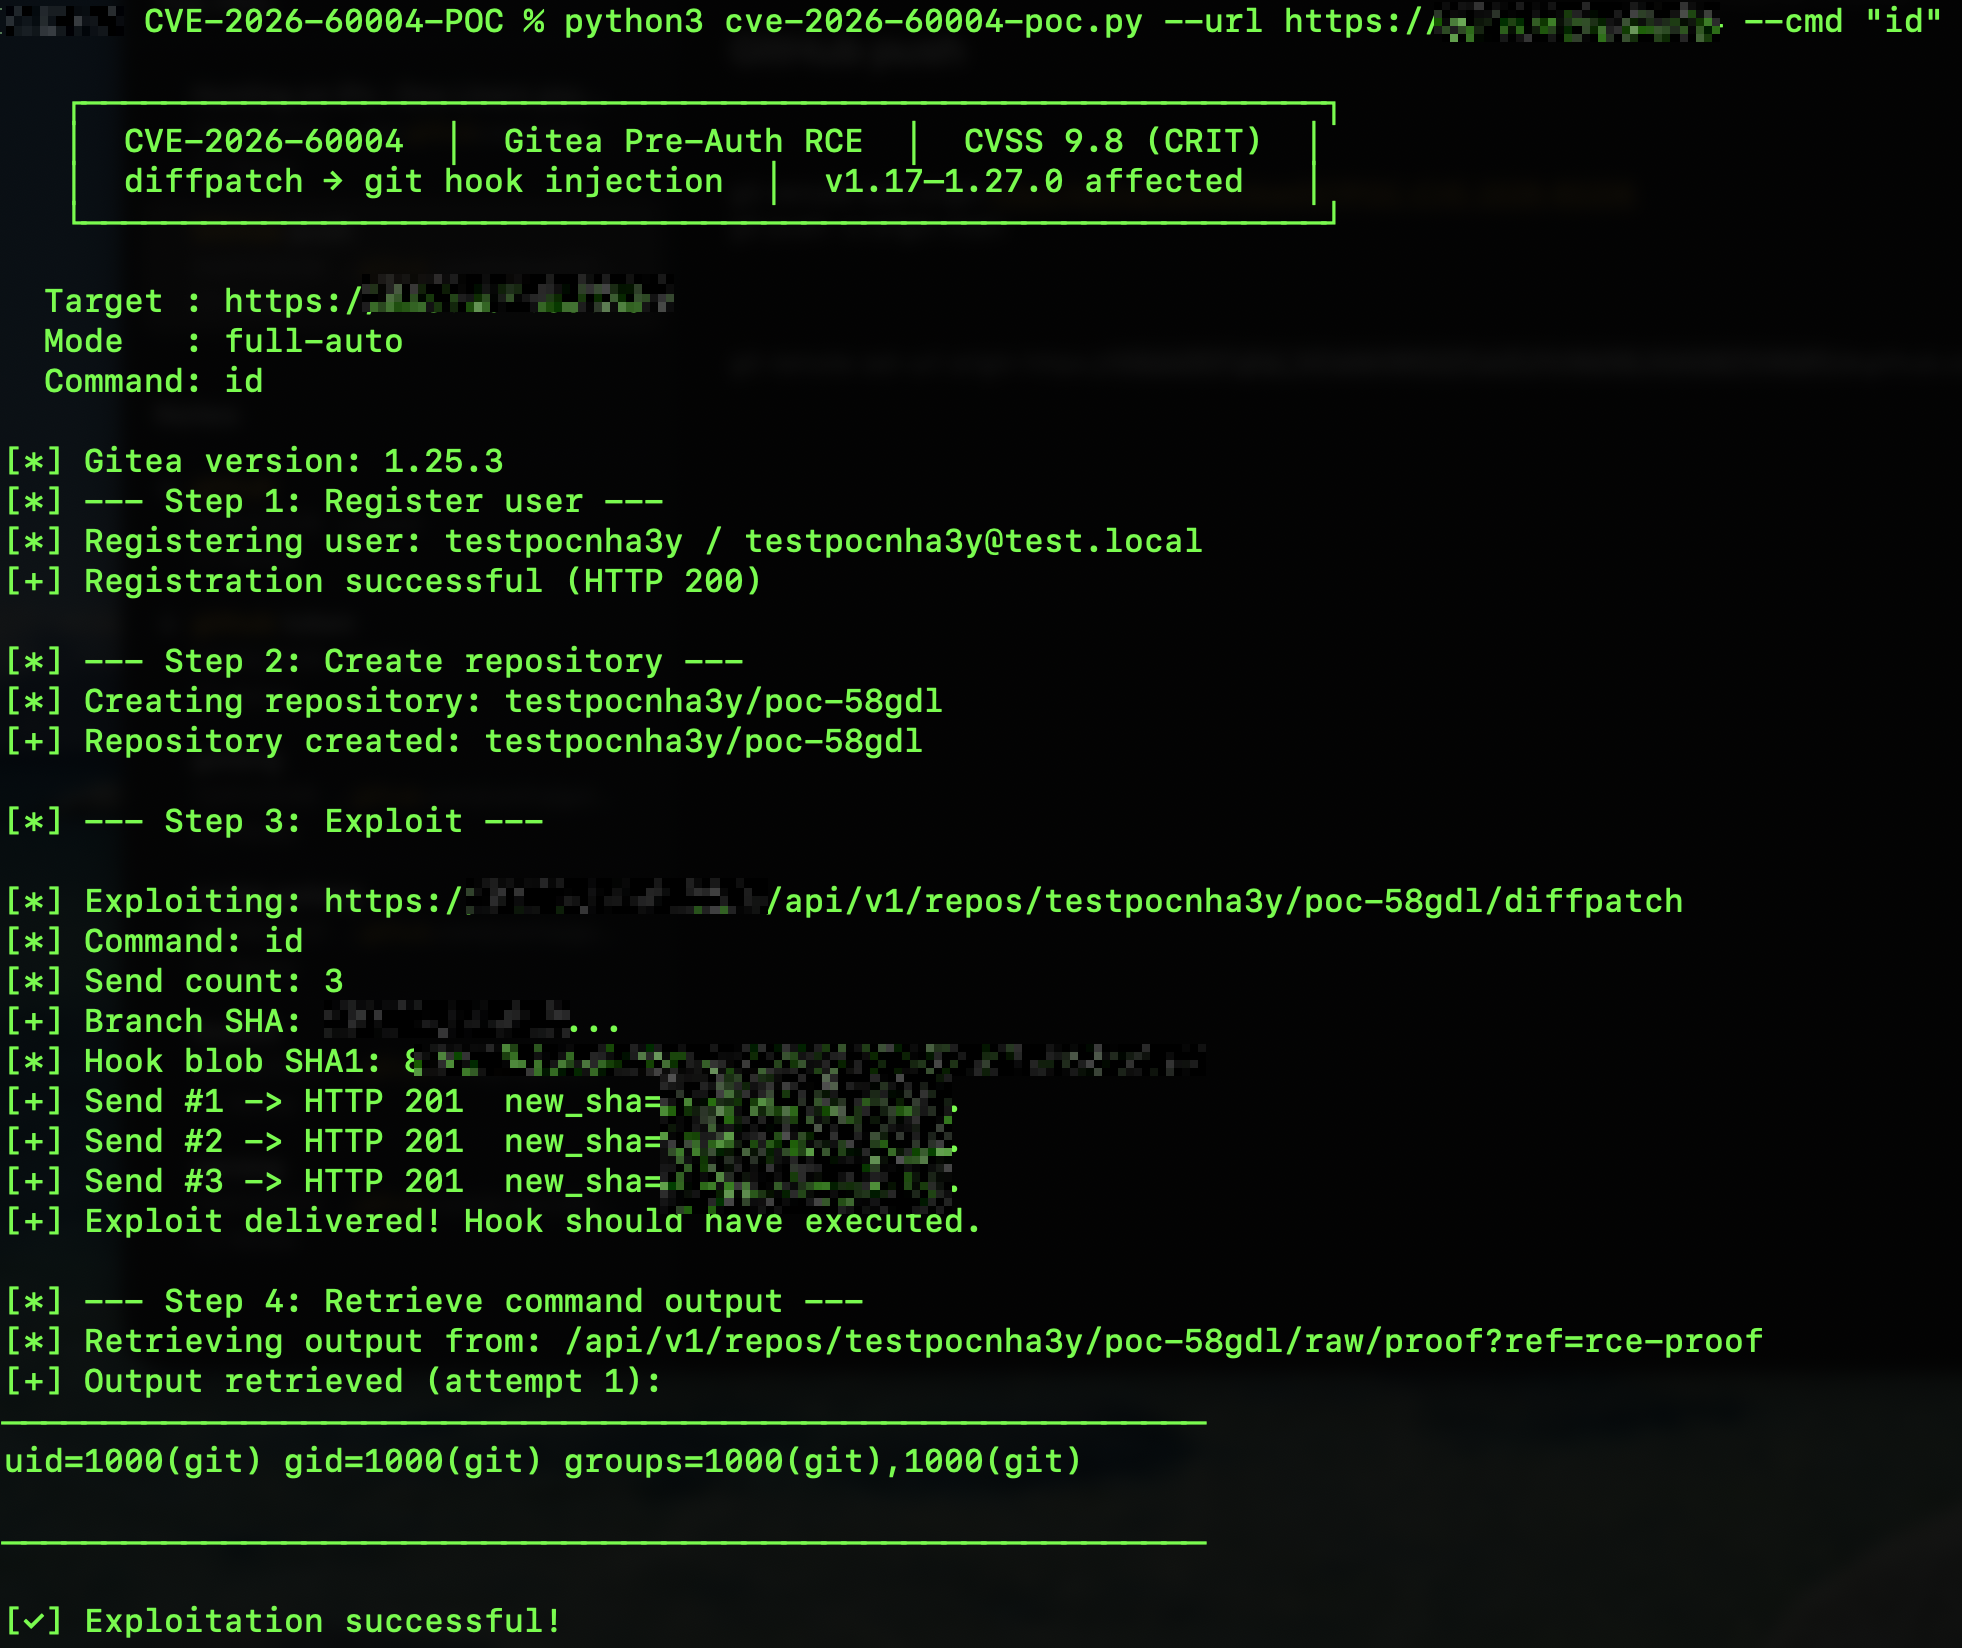 imbas007/cve-2026-60004-poc
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
 zi0black/poc-cve-2018-0114
This repository contains the POC of an exploit for node-jose < 0.11.0
 snyk-labs/pdfjs-vuln-demo
This project is intended to serve as a proof of concept to demonstrate exploiting the vulnerability in the PDF.js (pdfjs-dist) library reported in…
 tc4dy/cve-2026-87902-toolkit
WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…
 mistymntncop/cve-2024-7971
Proof-of-concept writeup for CVE-2024-7971, detailing the vulnerability discovery process and providing a functional POC for security researchers and…








