
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 ltmthink/cve-2024-21733
一个验证对CVE-2024-21733
 mayaseven/cve-2016-6662
From SQL injection to root shell with CVE-2016-6662 by MaYaSeVeN
 k3rwin/spring-core-rce
spring框架RCE漏洞 CVE-2022-22965
 nu11secur1ty/xssight
Educational resource on Cross-site Scripting (XSS) attack techniques, covering non-persistent, persistent, and DOM-based vectors with practical…
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 yuriisanin/cve-2022-24342
PoC for CVE-2022-24342: account takeover via CSRF in GitHub authentication
 gylq/cve-2021-45232-rce
Multithreaded batch vulnerability scanner for CVE-2021-45232, targeting Apache APISIX Dashboard RCE with FOFA query support.
 sfewer-r7/cve-2026-63077
Unauthenticated Remote Code Execution in JetBrains TeamCity (CVE-2026-63077)
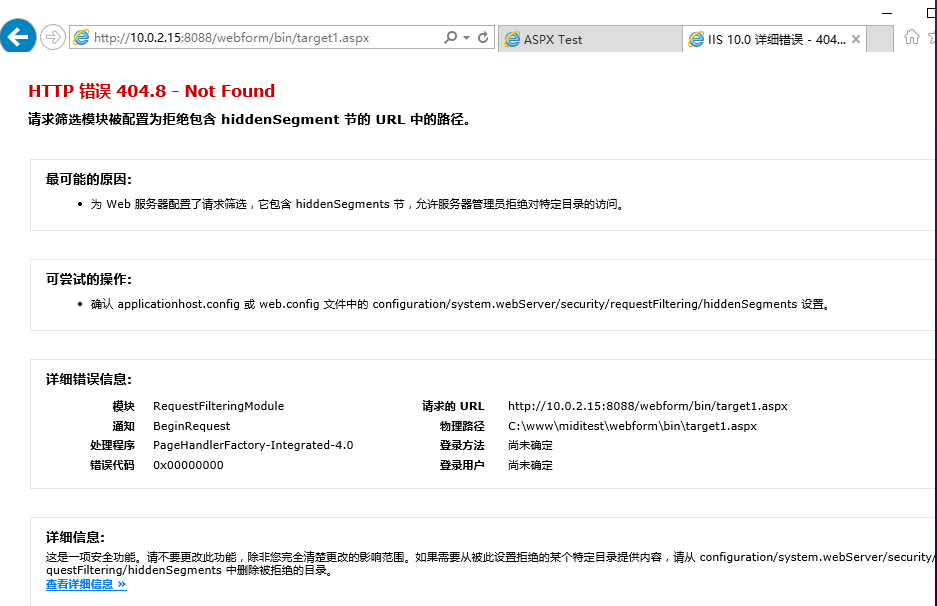 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 karthikuj/cve-2022-31101
Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)
 dpgg101/cve-2019-10945
Joomla! Core 1.5.0 - 3.9.4 - Directory Traversal / Authenticated Arbitrary File Deletion in Python3
 liamg/cve-2025-48384
Proof-of-concept exploit demonstrating remote code execution via a crafted git submodule during clone with --recurse-submodules. Targets…
 jonirinta-kahila/wpcracker
WordPress pentest tool
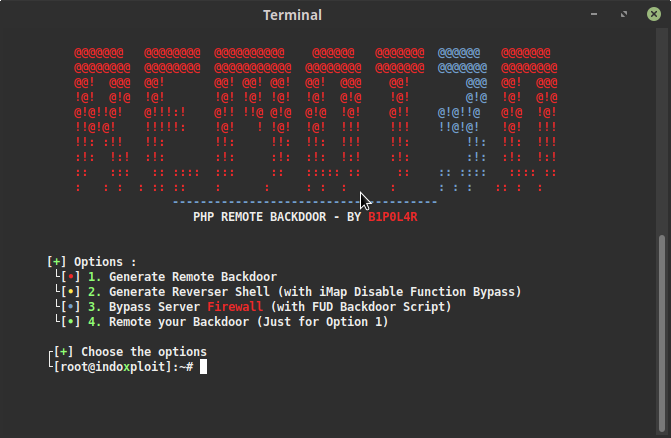 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 brucessking/cve-2021-36749
Apache Druid 任意文件读取
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
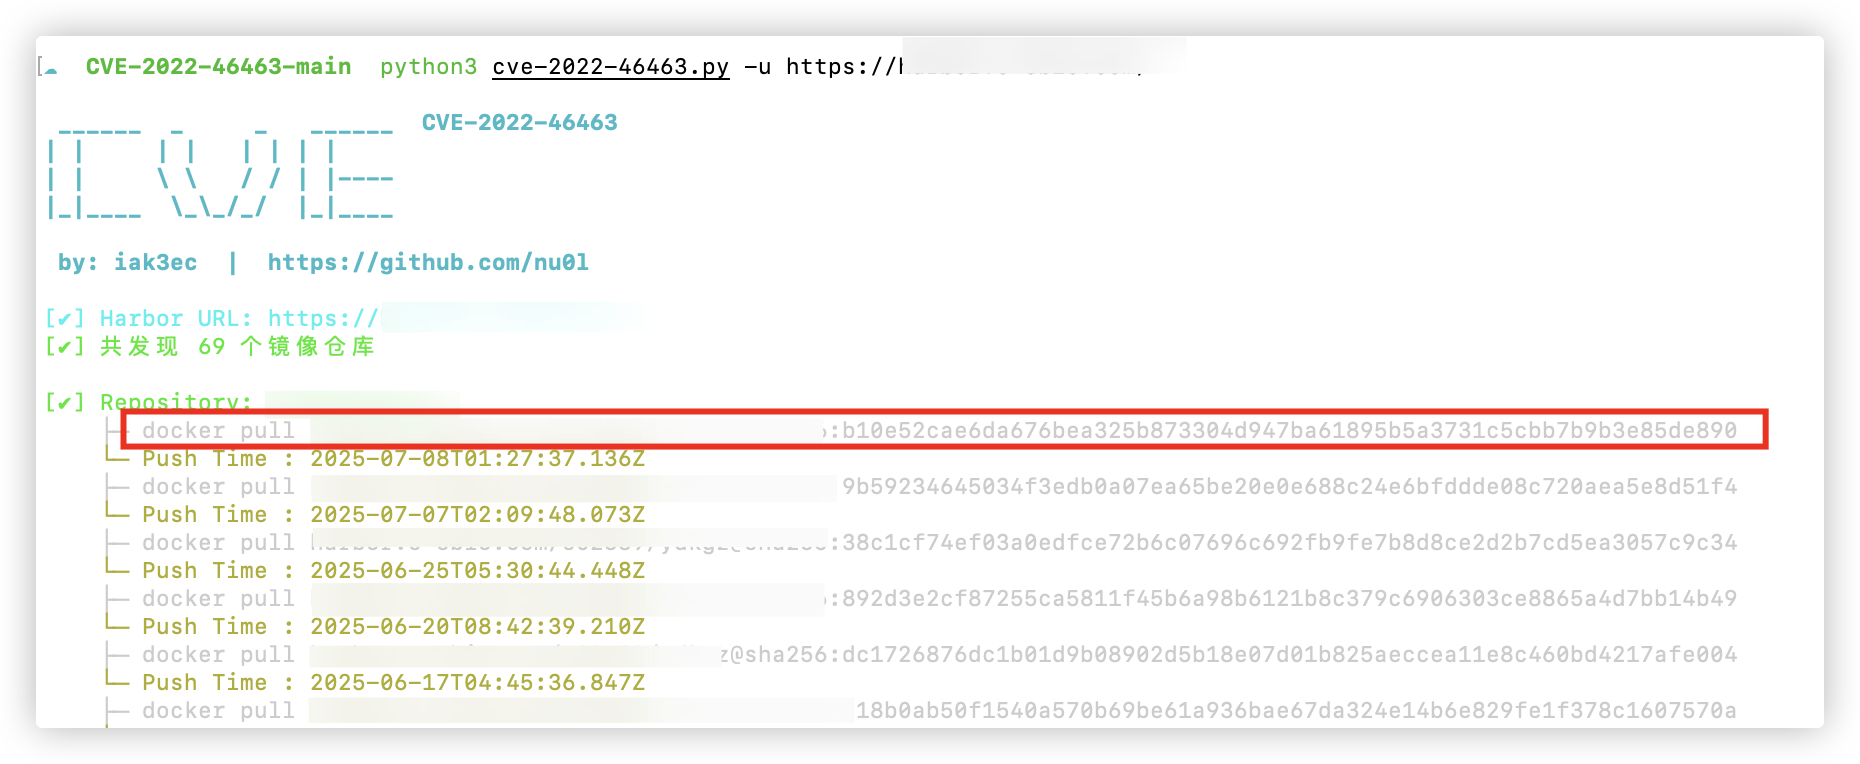 nu0l/cve-2022-46463
CVE-2022-46463(Harbor 未授权)
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities








