
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
GeoServer-Tools-CVE-2024-36401 — CVE-2024-36401 图形化利用工具,支持各个JDK版本利用以及回显、内存马实现 | Kitploit

Tools/GitHubGitHub/bmth666/geoserver-tools-cve-2024-36401
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingRed TeamingPayload Development
GitHubbmth666/geoserver-tools-cve-2024-36401

GeoServer-Tools-CVE-2024-36401

CVE-2024-36401 图形化利用工具,支持各个JDK版本利用以及回显、内存马实现

View Repository
442366 months agoReviewed by Kitploit
Share

GeoServer-Tools-CVE-2024-36401

CVE-2024-36401 Graphical Exploitation Tool, supports exploitation across various JDK versions, as well as echo and memory shell implementation.

Affected versions:

GeoServer < 2.23.6

2.24.0 <= GeoServer < 2.24.4

2.25.0 <= GeoServer < 2.25.2

Recently during HW (Red/Blue team exercises), this vulnerability was found to be quite common, but there hasn't been a handy tool. Here, by referencing the approach of https://github.com/whitebear-ch/GeoServerExploit, this tool was rewritten.
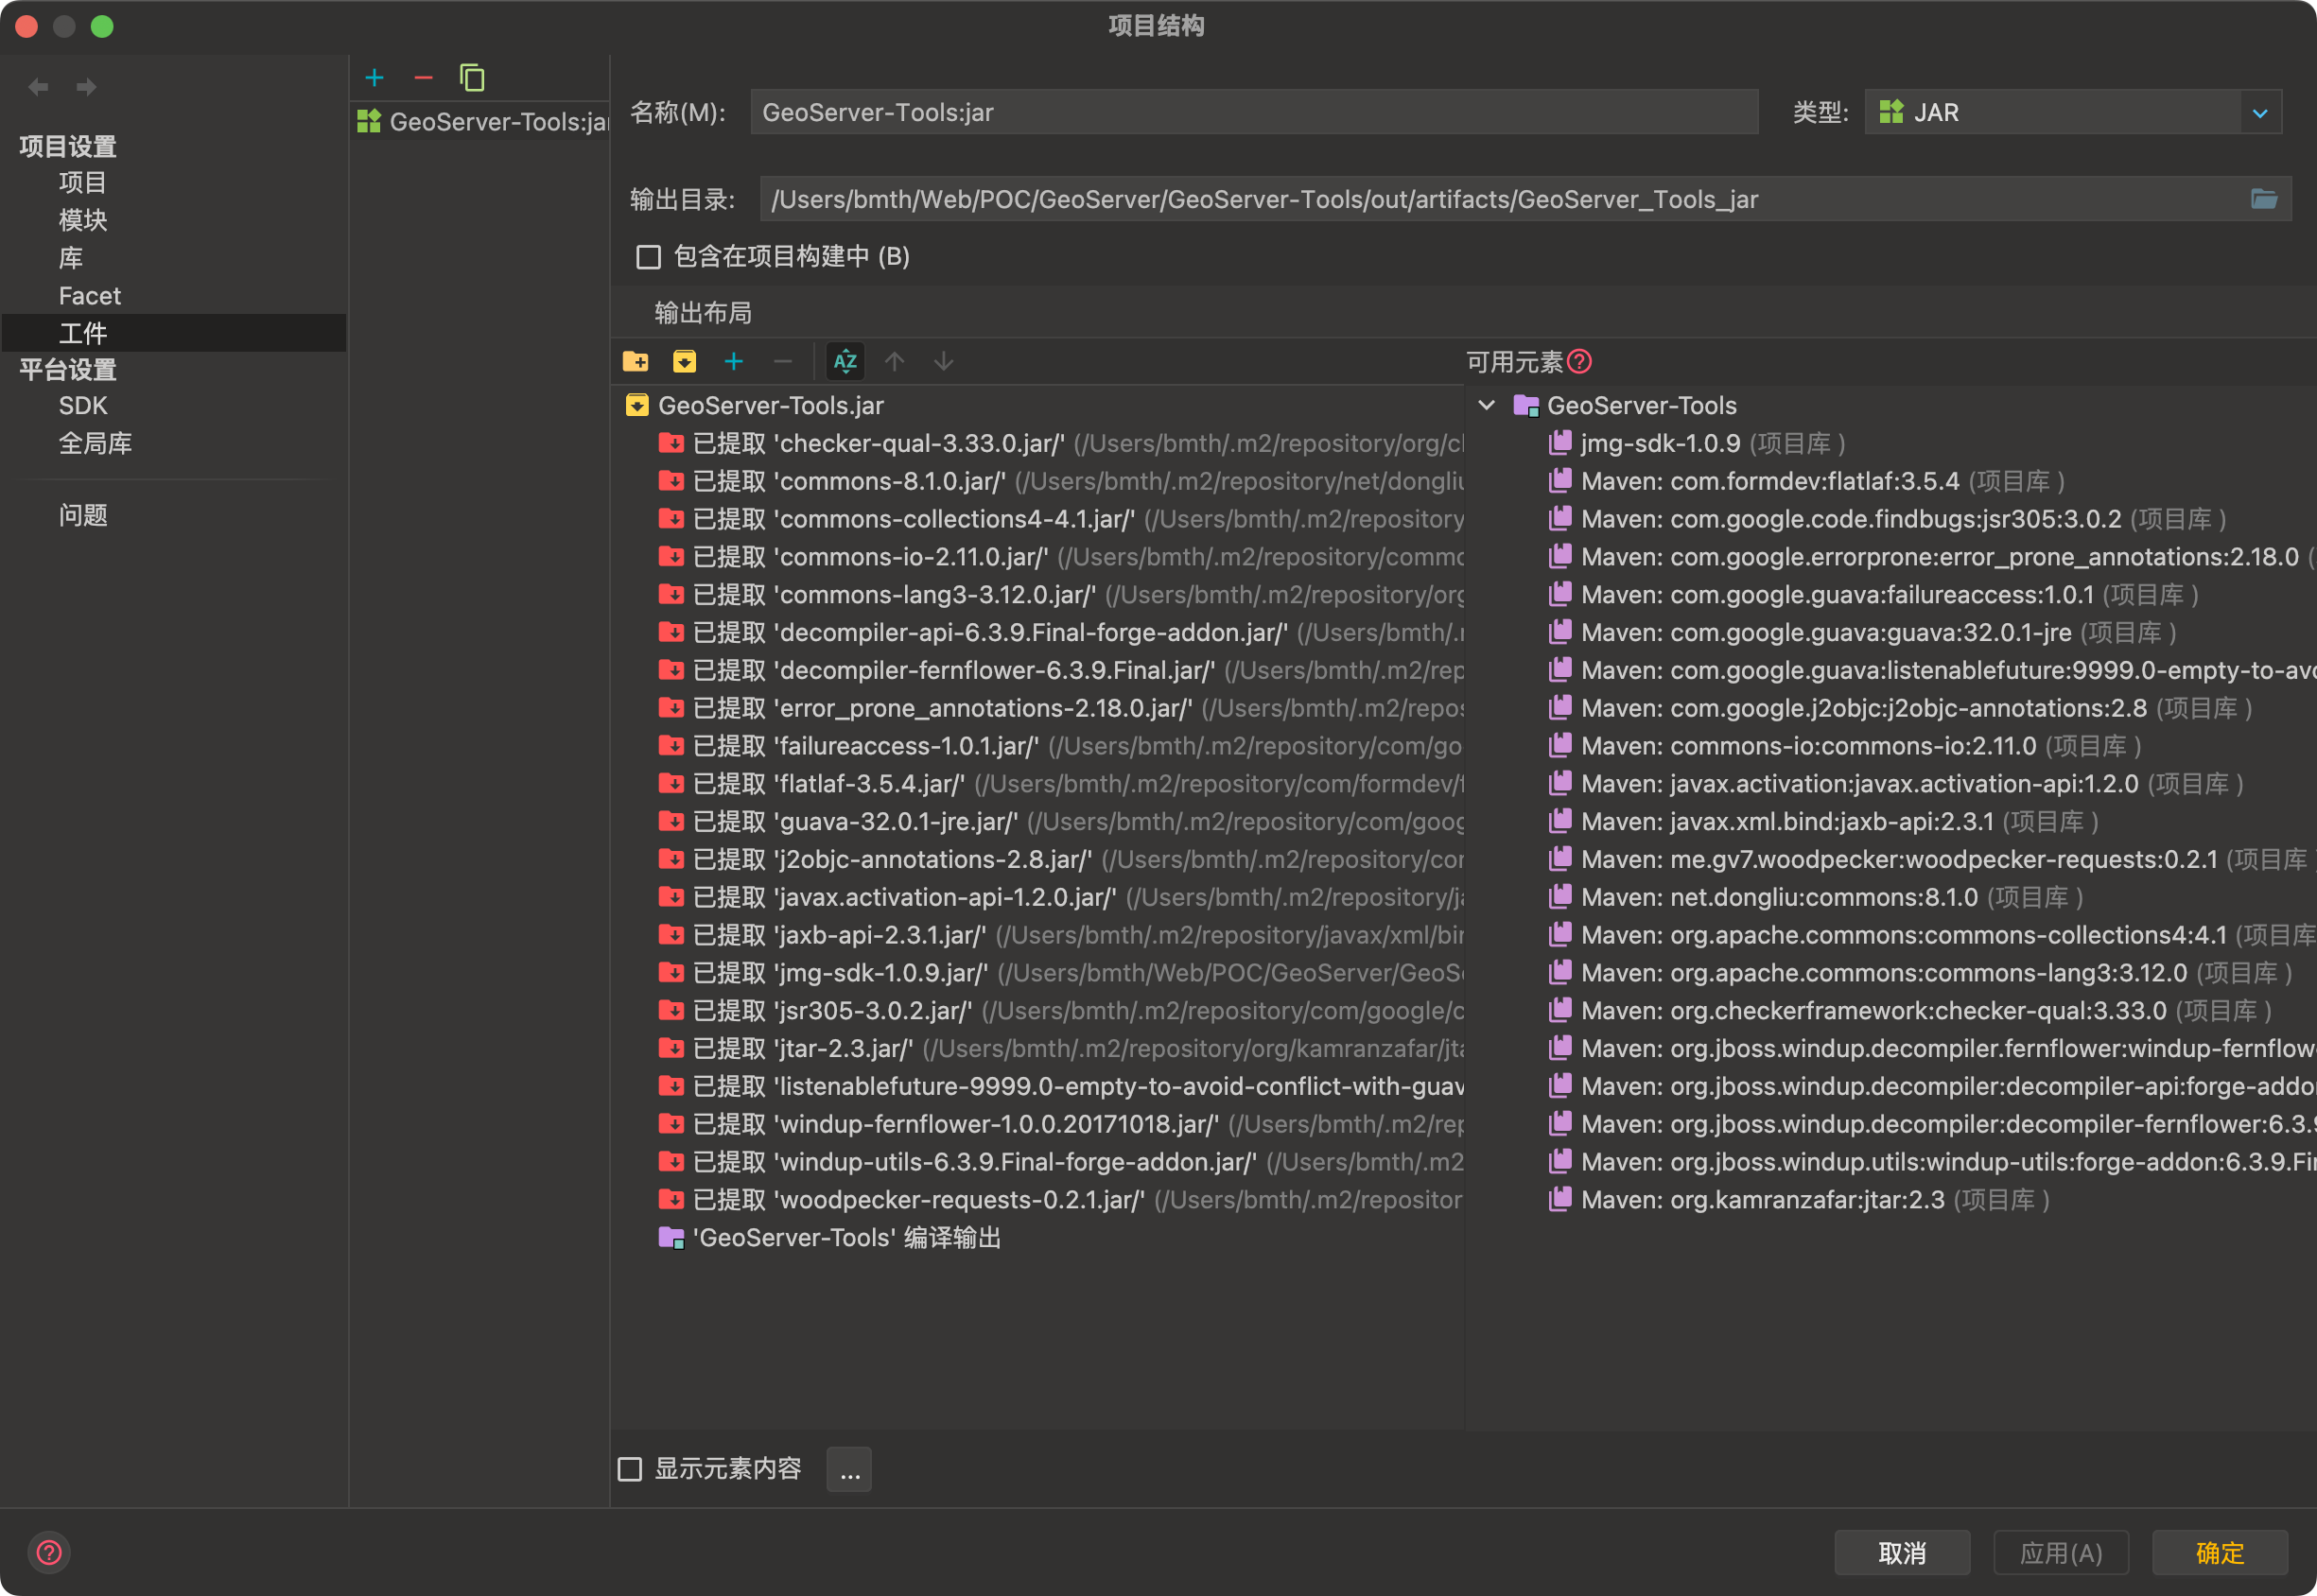
0x01 Installation

image-20250411124904054

Just build the artifact.

0x02 Usage

Launch with JDK8: java -jar GeoServer-Tools.jar
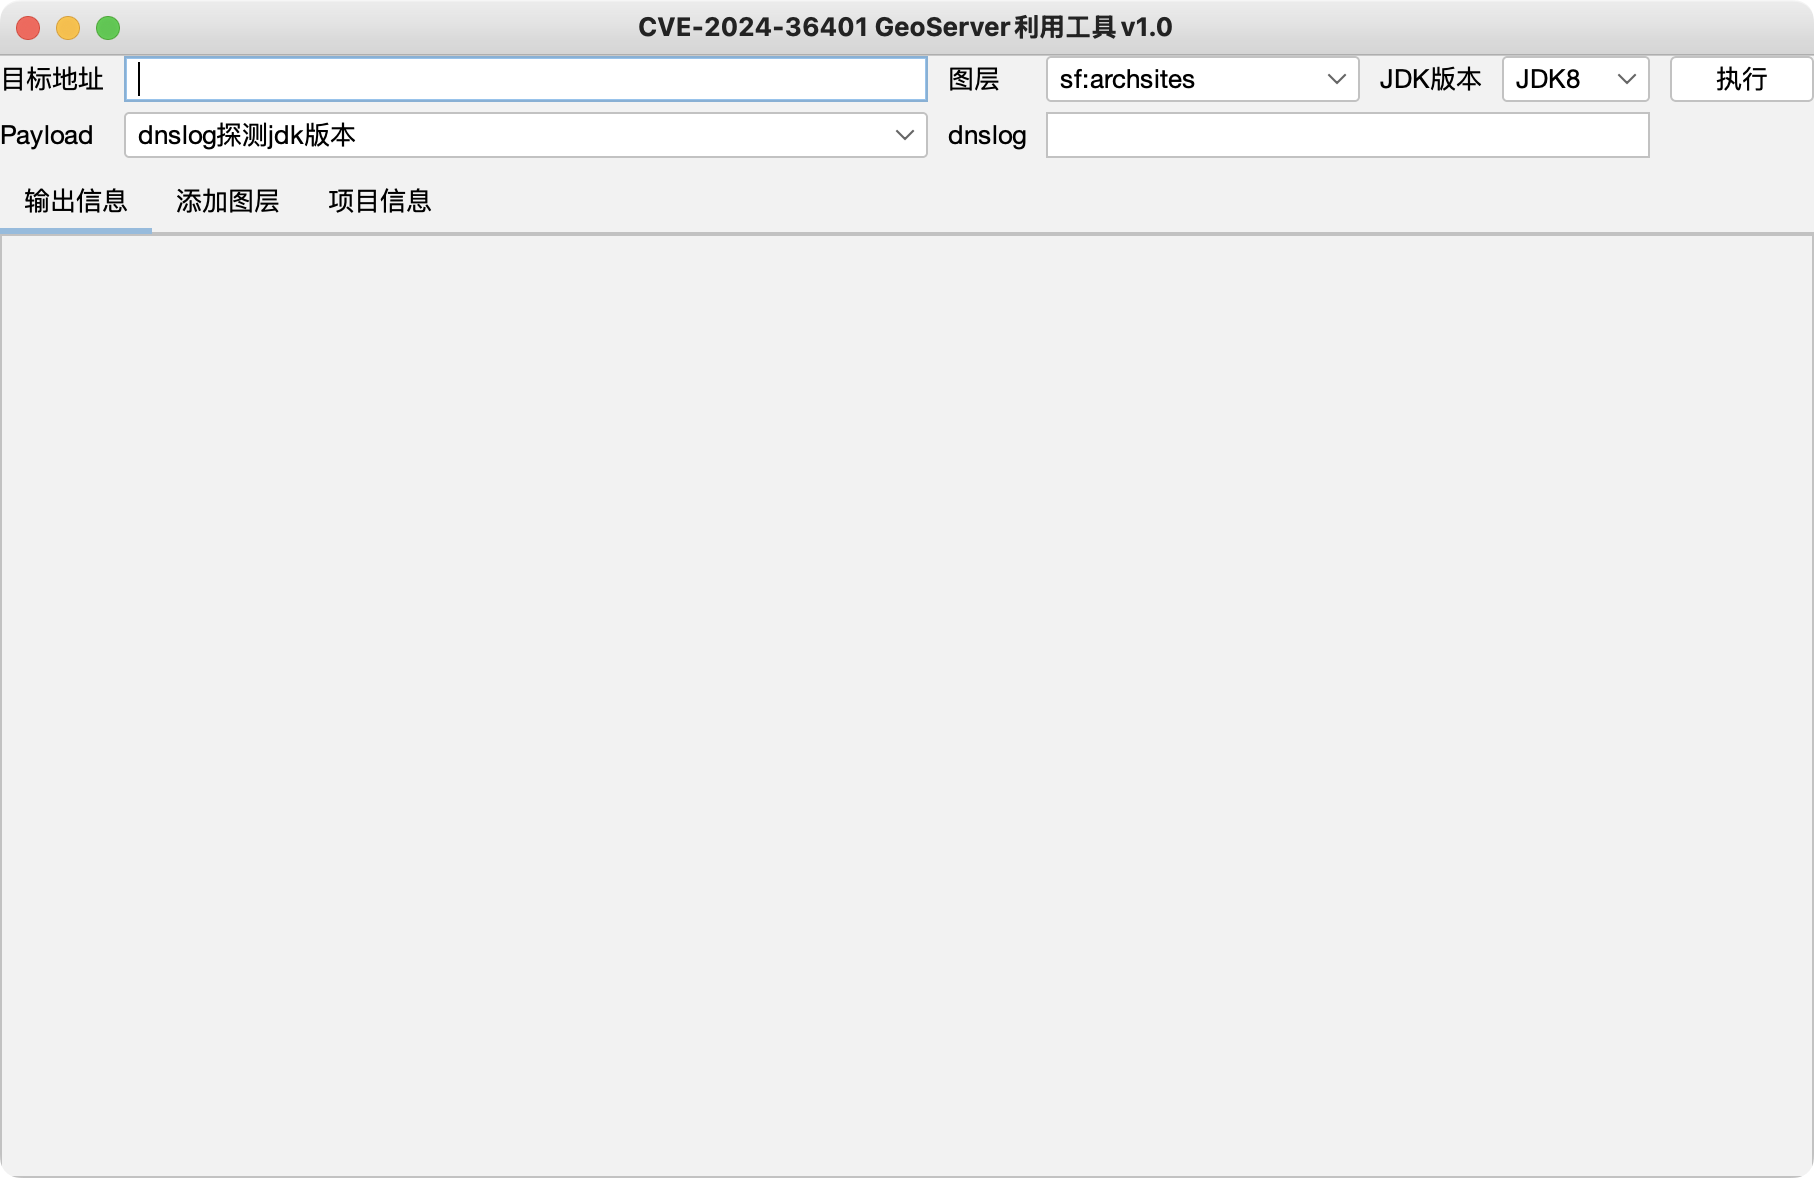
image-20250411125025482

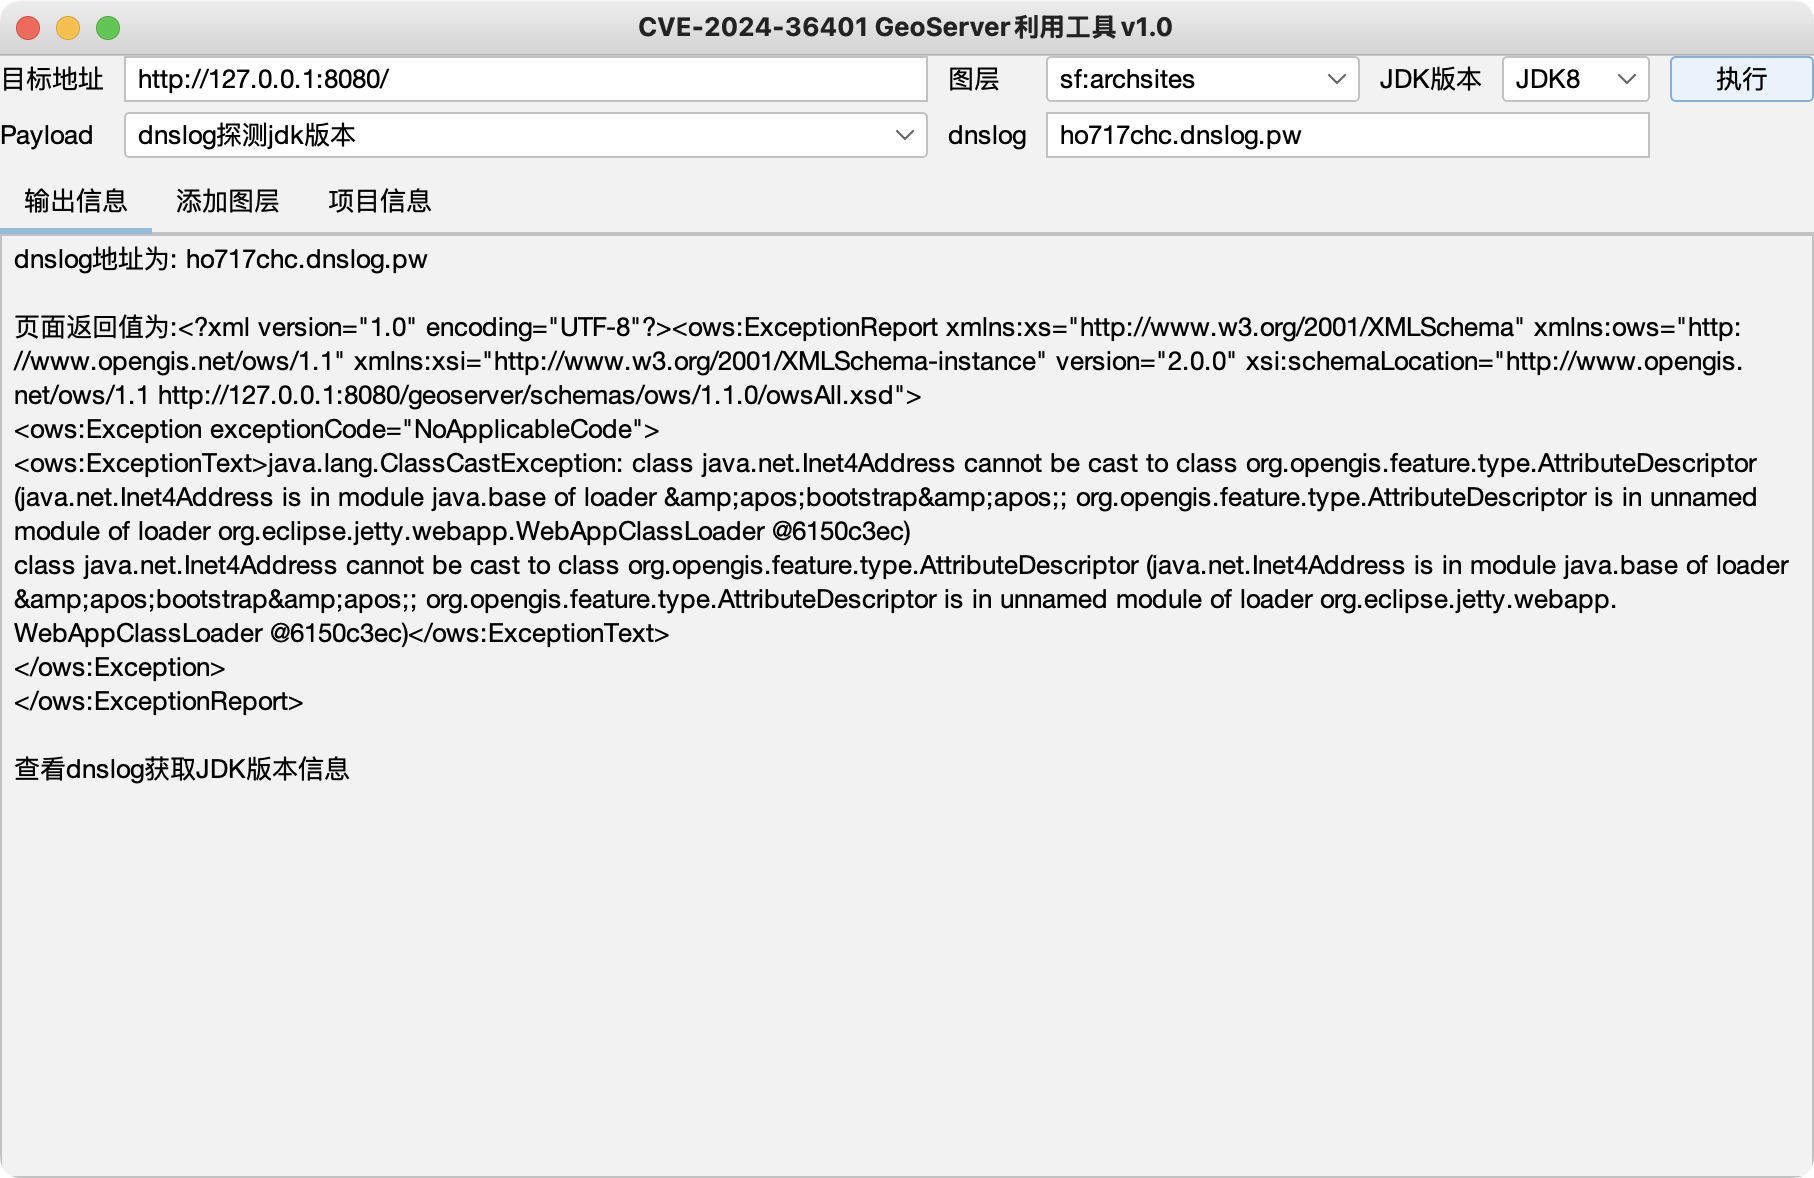
dnslog (JDK version independent):

image-20250411125210164

image-20250411125231103

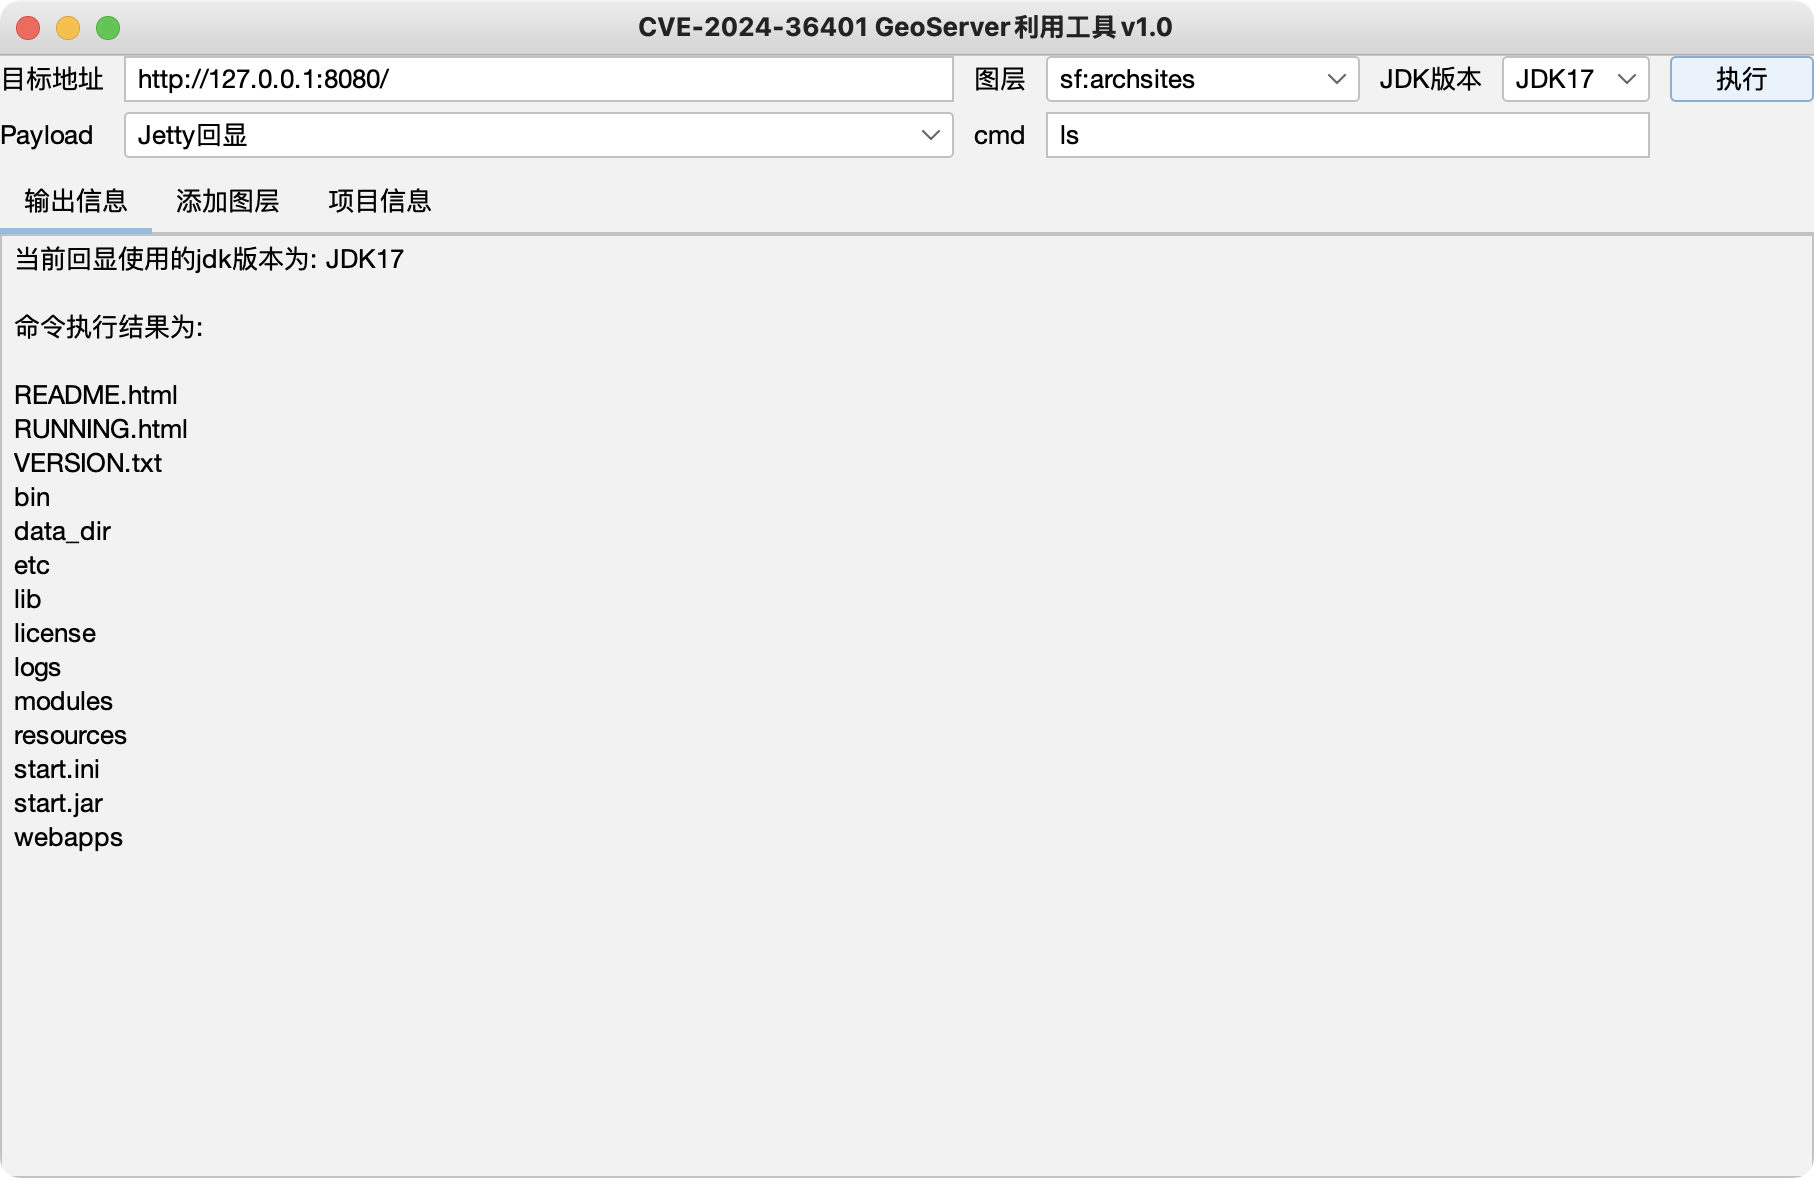
Echo:

image-20250411125857883

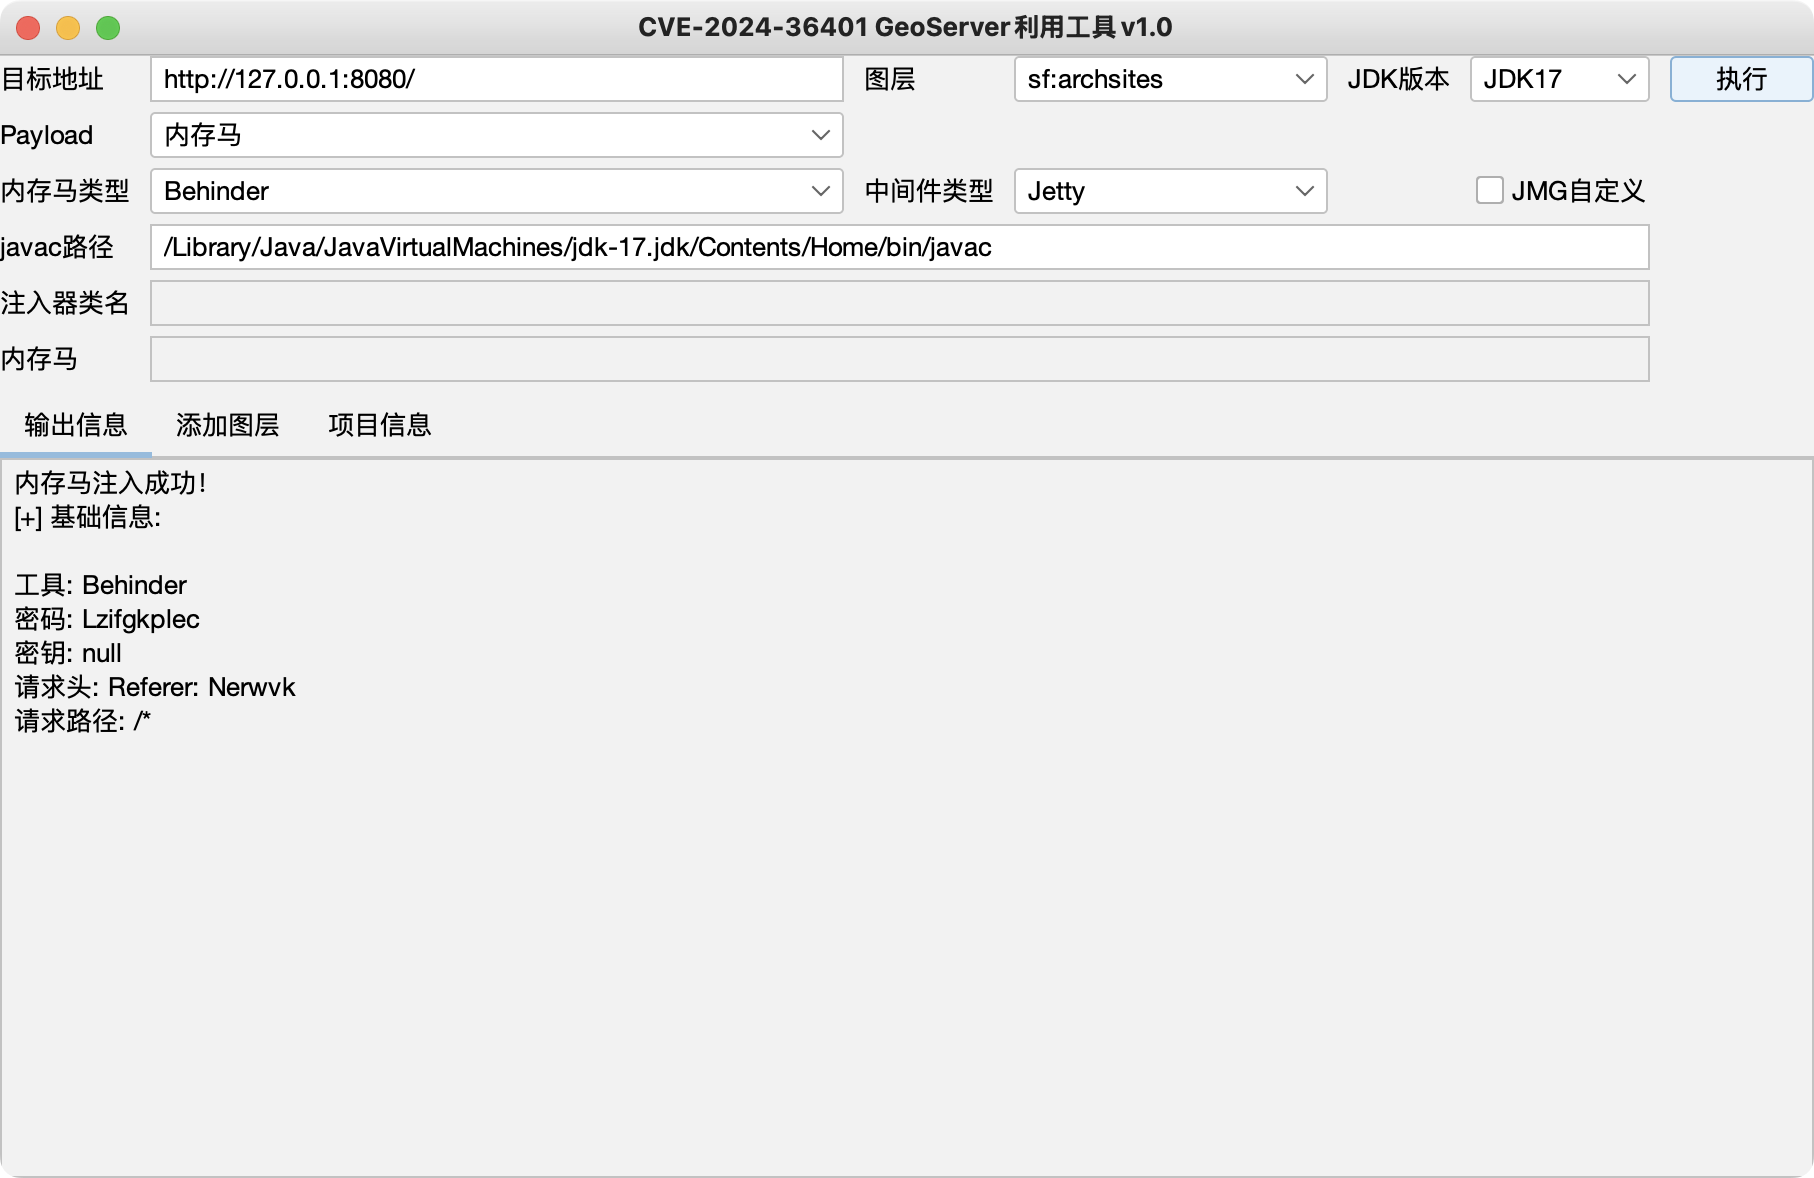
Memory Shell:

image-20250411130004637

image-20250411130131602

My test environment uses vulhub (JDK17) and the Windows version (JDK8) from: https://master.dl.sourceforge.net/project/geoserver/GeoServer/2.15.0/geoserver-2.15.0.exe?viasf=1

Actual environments may vary; please test on your own.

The Godzilla memory shell on JDK17 is likely too long to be successfully injected; it is recommended to use Behinder or AntSword.

0x03 Disclaimer

For technical research and authorized offensive/defensive projects only. Users must comply with the "Cybersecurity Law of the People's Republic of China". Do not use for any illegal activities. If the tool is used for other purposes, the user shall bear all legal and joint liabilities. The author and publisher assume no legal or joint liability!

0x04 References/Acknowledgments

https://mp.weixin.qq.com/s/beRJ8-HOMJbA43jYMMS0Pg

https://mp.weixin.qq.com/s/1mW3rLvZc0RL4nr25BLT7A

https://mp.weixin.qq.com/s/jCOp9A-qO8ViqLx3ui0XHg

https://github.com/whitebear-ch/GeoServerExploit

https://github.com/pen4uin/java-memshell-generator

https://github.com/vulhub/vulhub

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    851
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    538
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    420
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    357
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    297
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →