
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 sirpedrotavares/proxylogon-exploit
proxylogon exploit - CVE-2021-26857
 jas502n/cve-2018-3191
Exploit for CVE-2018-3191 targeting Oracle WebLogic Server via T3 protocol, enabling unauthenticated remote code execution with JNDI payload…
 vainlystrain/vailyn
A phased, evasive Path Traversal + LFI scanning & exploitation tool in Python
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 horizon3ai/proxyshell
Proof of Concept for CVE-2021-34473, CVE-2021-34523, and CVE-2021-31207
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 svdwi/oswe-labs-poc
Dockerized labs For Web Expert (OSWE) certification. Preparation for coming AWAE Training ...
 horizon3ai/cve-2022-47966
Proof-of-concept exploit for CVE-2022-47966, a pre-authentication remote code execution vulnerability in multiple ManageEngine products via SAML…
 w01fh4cker/screenconnect-authbypass-rce
Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user…
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 saelo/jscpwn
PoC exploit for CVE-2016-4622
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
 arthurgervais/mapta
Multi-agent LLM system that autonomously assesses web application security, orchestrating tool-grounded execution and validating exploits end to end.
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…
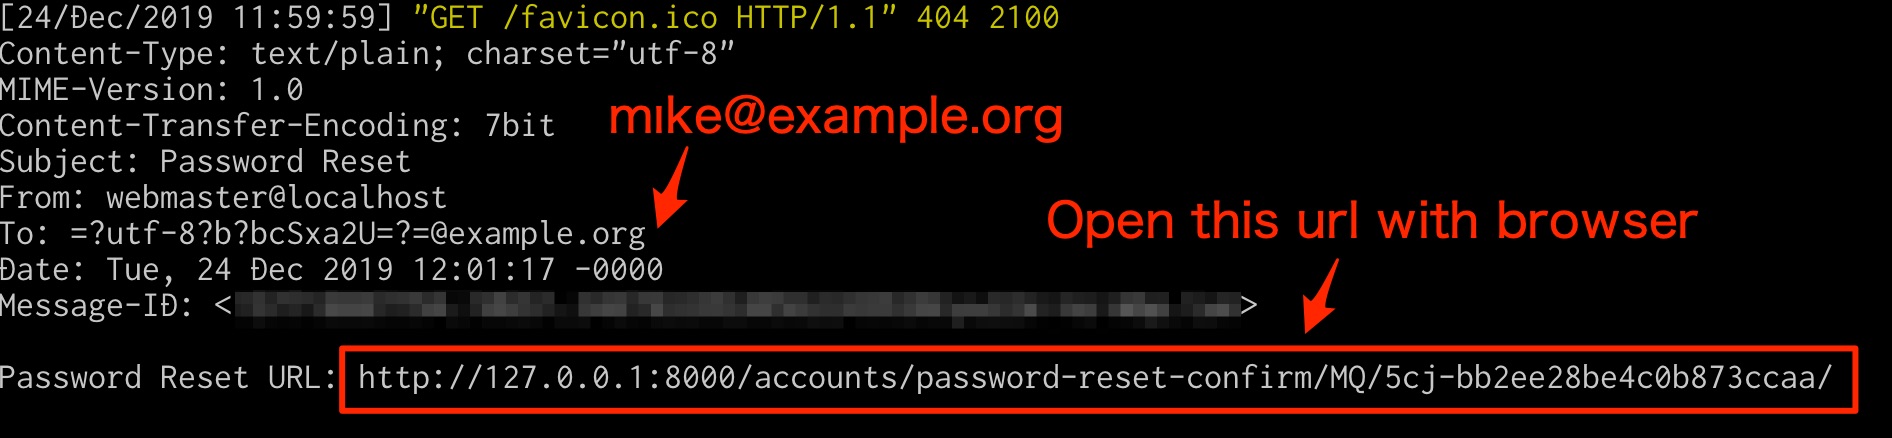 ryu22e/django_cve_2019_19844_poc
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)
 jas502n/kibana-rce
kibana < 6.6.0 未授权远程代码命令执行 (Need Timelion And Canvas),CVE-2019-7609
 w01fh4cker/cve-2024-21683-rce
CVE-2024-21683 Confluence Post Auth RCE








