
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 giterlizzi/nmap-log4shell
Nmap NSE script for detecting Apache Log4j RCE (CVE-2021-44228) by injecting JNDI exploit payloads via HTTP headers or TCP/UDP sockets across…
 fsecurelabs/cve-2018-4121
macOS 10.13.3 (17D47) Safari Wasm Exploit
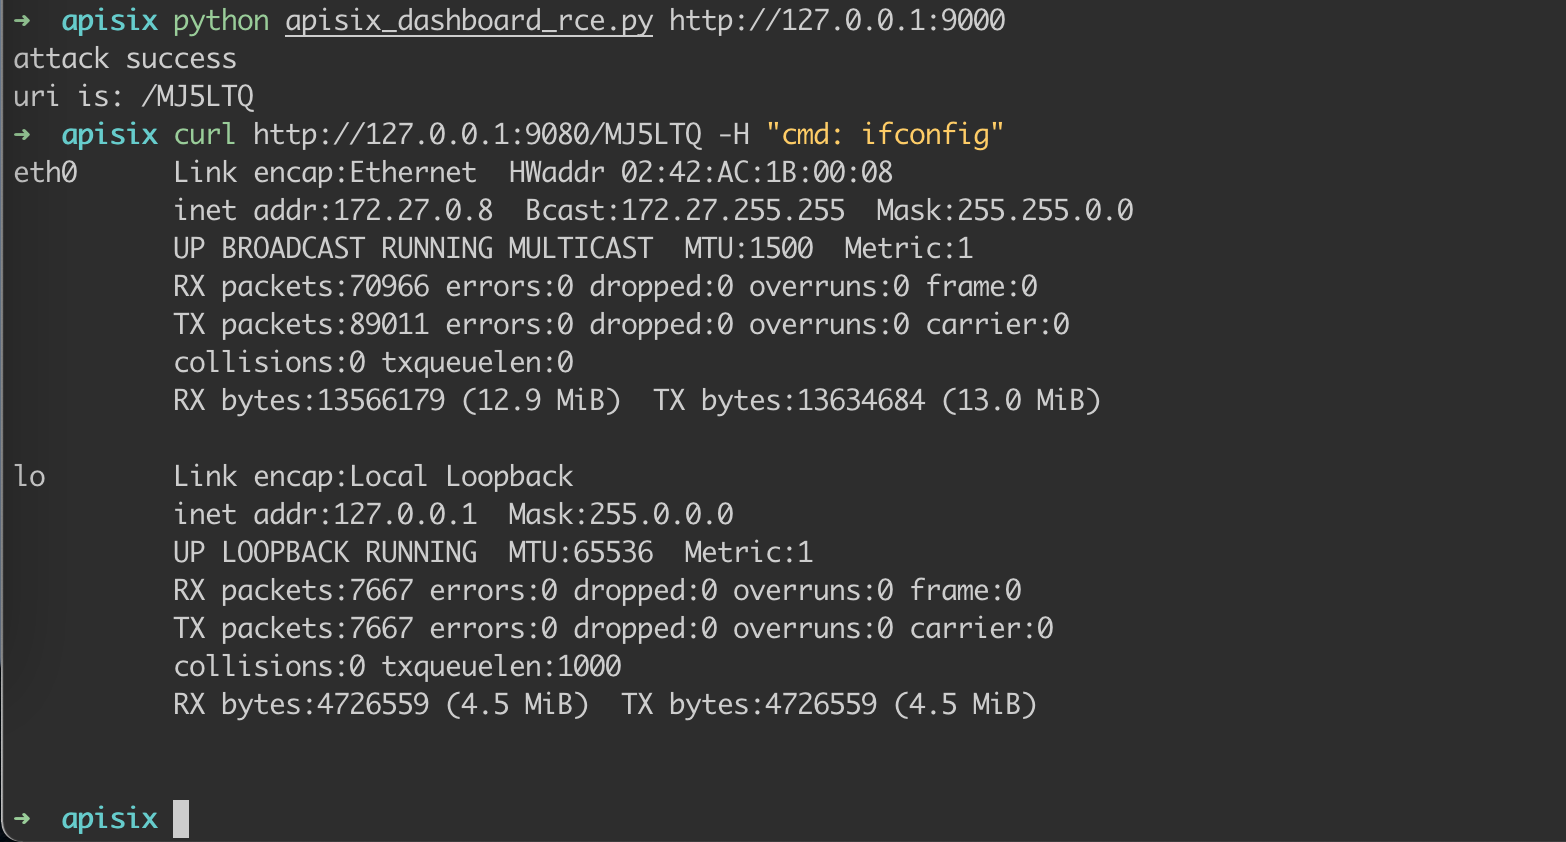 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…
 synacktiv/laravel-crypto-killer
A tool designed to exploit bad implementations of decryption mechanisms in Laravel applications.
 doyensec/csptplayground
CSPTPlayground is an open-source playground to find and exploit Client-Side Path Traversal (CSPT).
 mistymntncop/cve-2023-3079
Proof-of-concept exploit for CVE-2023-3079, a Chrome V8 type confusion vulnerability, with curated writeups and root cause analysis resources.
 tam-k592/cve-2024-40725-cve-2024-40898
CVE-2024-40725 and CVE-2024-40898, affecting Apache HTTP Server versions 2.4.0 through 2.4.61. These flaws pose significant risks to web servers…
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618/109619 — PHP session.upload_progress pre-auth RCE. Exploit research: remote ASLR chain, PoC & patch analysis.
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 h4x0r-dz/cve-2024-21893.py
CVE-2024-21893: SSRF Vulnerability in Ivanti Connect Secure
 jas502n/cve-2019-19781
Python exploit for CVE-2019-19781 targeting Citrix ADC with template injection to achieve remote code execution on vulnerable gateways.
 kingsabri/godofwar
GodOfWar - Malicious Java WAR builder with built-in payloads
 payatu/cve-2015-6086
PoC for CVE-2015-6086
 xteam-wing/cve-2021-22205
Pocsuite3 For CVE-2021-22205
 jburgess-r7/cve-2026-97229-poc
GitLab CI lint integer-overflow RCE PoC for CVE-2026-97229, validated against the official 19.4.1 CE amd64 image
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
 gobysec/weblogic
WebLogic vulnerability exploration from beginner to expert.
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…








