
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 euphrat1ca/cve-2020-0618
SQL Server Reporting Services(CVE-2020-0618)中的RCE
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 exodusintel/chromium-941743
Chrome v8 1Day Exploit by István Kurucsai
 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 s0md3v/shiva
Improved DOS exploit for wordpress websites (CVE-2018-6389)
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
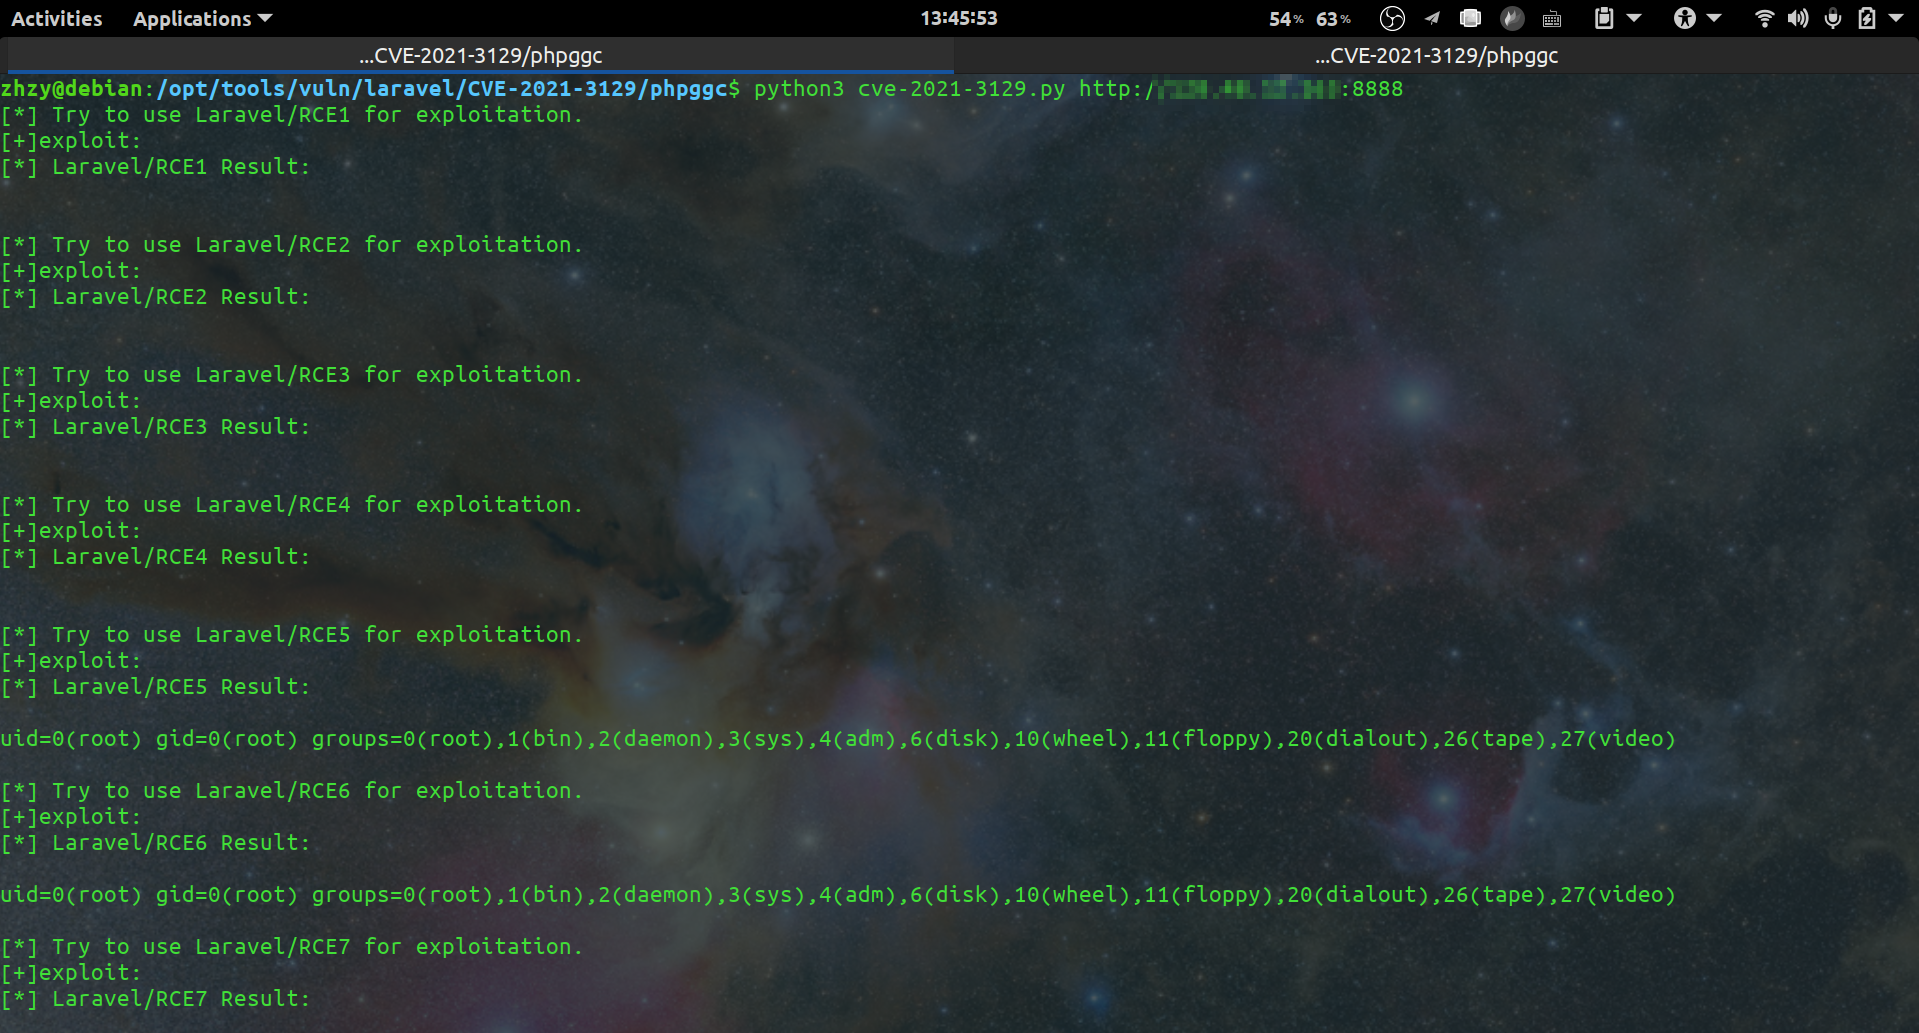 zhzyker/cve-2021-3129
Laravel <= v8.4.2 debug mode: Remote code execution (CVE-2021-3129)
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 zapstiko/bug-bounty
Here Are Some Bug Bounty Resource From Twitter
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 daxakahackerman/xss-catcher
A blind XSS detection and XSS data capture framework
 jas502n/cve-2019-12409
Apache Solr RCE (ENABLE_REMOTE_JMX_OPTS="true")
 thegejr/springshell
Spring4Shell - Spring Core RCE - CVE-2022-22965
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.








