
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended

 coffinxp/img-payloads
Curated collection of image-based payloads for authorized red-team testing and security education, with HTML examples for generating or embedding web…
 y4er/cve-2020-2555
Weblogic com.tangosol.util.extractor.ReflectionExtractor RCE
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 csenox/cve-2022-2992
Authenticated Remote Command Execution in Gitlab via GitHub import
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 secmob/badkernel
Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016
 whxitte/white-deface
This is a simple python tool to automatically deface webdav vulnerable websites.
 gotr00t0day/forbiddenpass
Multi-domain HTTP 403 bypass scanner that tests header manipulation techniques to discover hidden access paths on web servers, supporting bulk domain…
 whwlsfb/cve-2022-22947-godzilla-memshell
CVE-2022-22947 注入Godzilla内存马
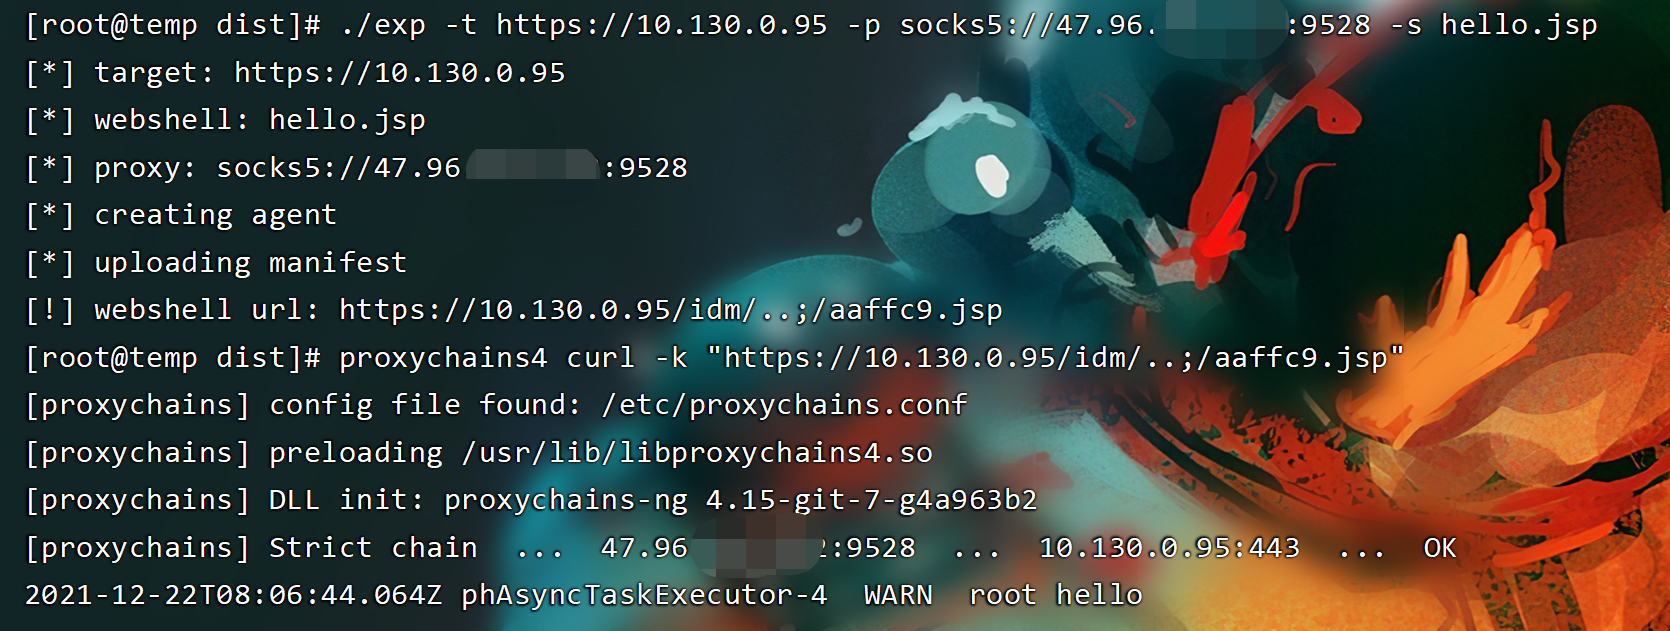 shmilylty/cve-2021-22005-exp
Exploit for CVE-2021-22005, a pre-auth arbitrary file upload vulnerability in VMware vCenter Server, enabling remote code execution via webshell…
 hellsender01/llmmap
Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 pyn3rd/cve-2019-0232
Apache Tomcat Remote Code Execution on Windows
 threedr3am/tomcat-cluster-session-sync-exp
tomcat使用了自带session同步功能时,不安全的配置(没有使用EncryptInterceptor)导致存在的反序列化漏洞,通过精心构造的数据包, 可以对使用了tomcat自带session同步功能的服务器进行攻击。PS:这个不是CVE-2020-9484,9484是session持久化的洞…
 absholi7ly/poc-cve-2025-24813
his repository contains an automated Proof of Concept (PoC) script for exploiting **CVE-2025-24813**, a Remote Code Execution (RCE) vulnerability in…
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…








