
 #1
Automated tools for detecting known vulnerabilities in systems and applications.
Kitploit recommended

 smaranchand/bucky
Bucky (An automatic S3 bucket discovery tool)
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 splunk/shellsweep
ShellSweeping the evil.
 vulncheck-oss/cli
VulnCheck's official command line tool
 tkcert/mail-security-tester
A testing framework for mail security and filtering solutions.
 ostesayed/oste-meta-scan
Multi-engine DAST scanner aggregating Nikto, ZAP, Nuclei, SkipFish, and Wapiti for automated web injection vulnerability detection with consolidated…
 ethicalhackingplayground/bxss
Blind XSS Scanner is a tool that can be used to scan for blind XSS vulnerabilities in web applications.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 noxxi/p5-ssl-tools
Perl scripts for SSL/TLS analysis: check protocol and cipher support, verify certificates, test OCSP, and detect Heartbleed across SMTP, HTTPS, and…
 node9-ai/node9-proxy
Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
 joasasantos/php2shell-scanner
Non-destructive scanner for CVE-2026-109618 / CVE-2026-109619 (PHP core RCE). Subdomain recon via crt.sh + subfinder, robust banner grabbing,…
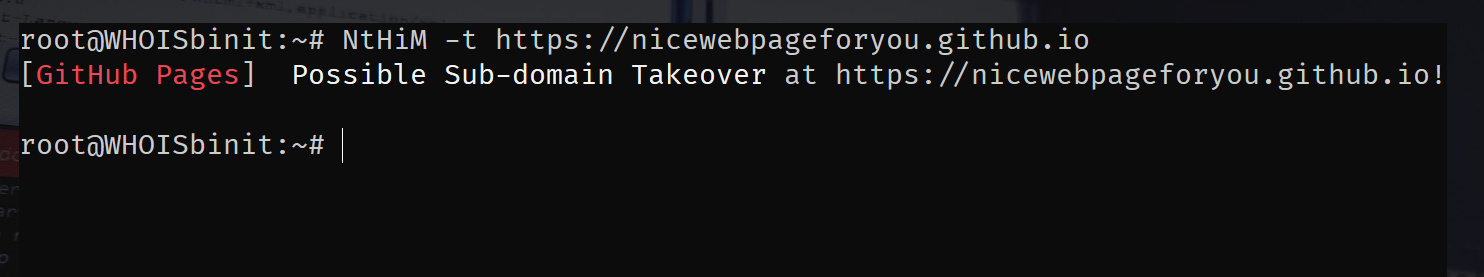 thebinitghimire/nthim
Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
 mhmdiaa/second-order
Crawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…








