
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended

 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 sooryathejas/metatron
AI-powered penetration testing assistant using local LLM on linux (Parrot OS)
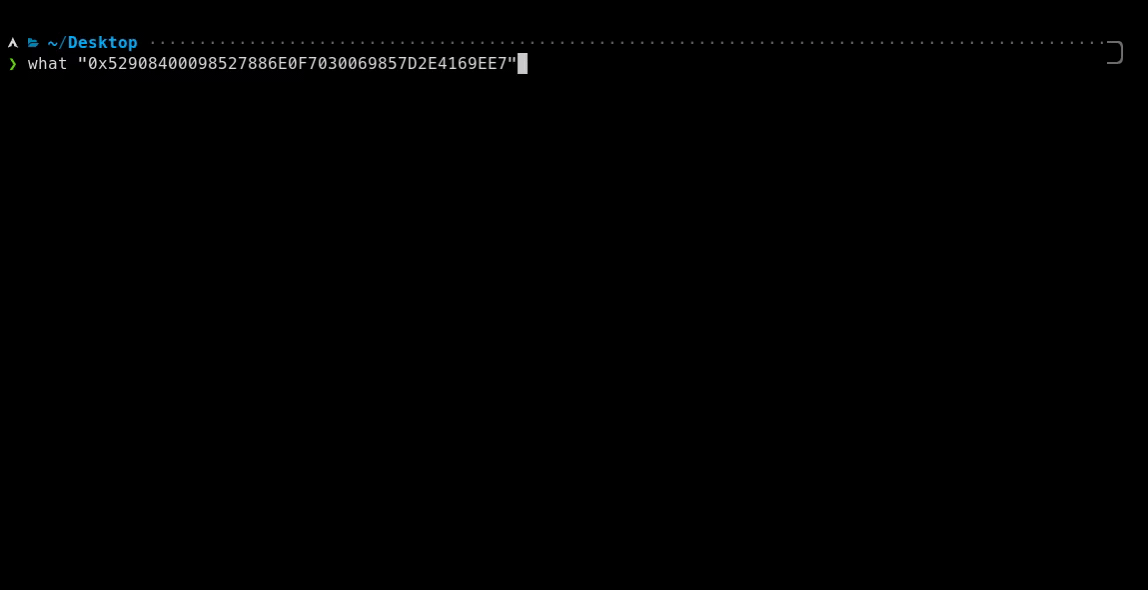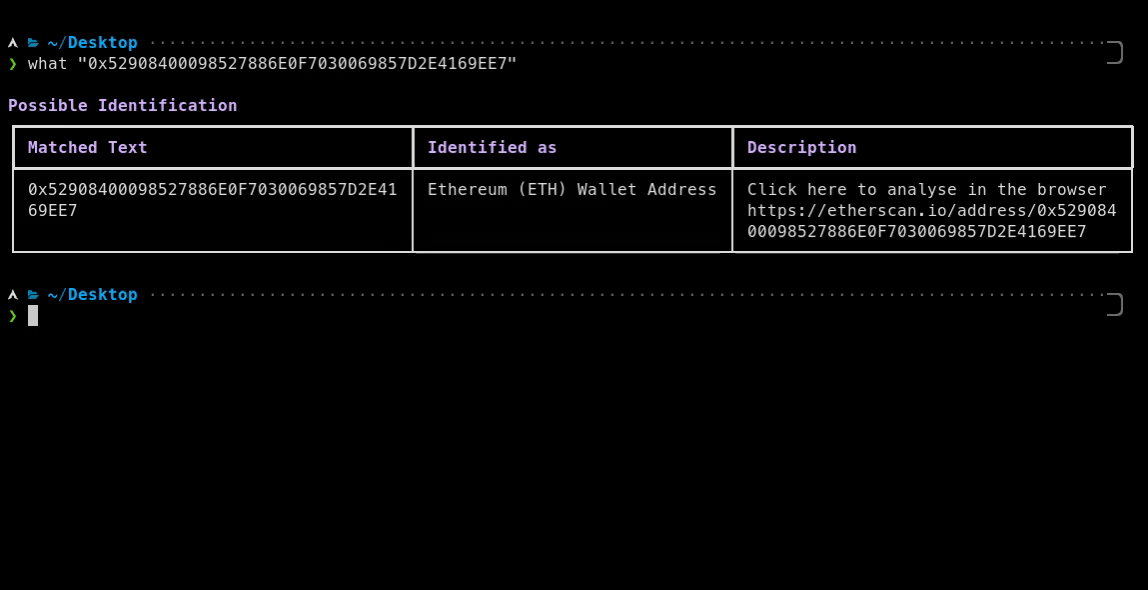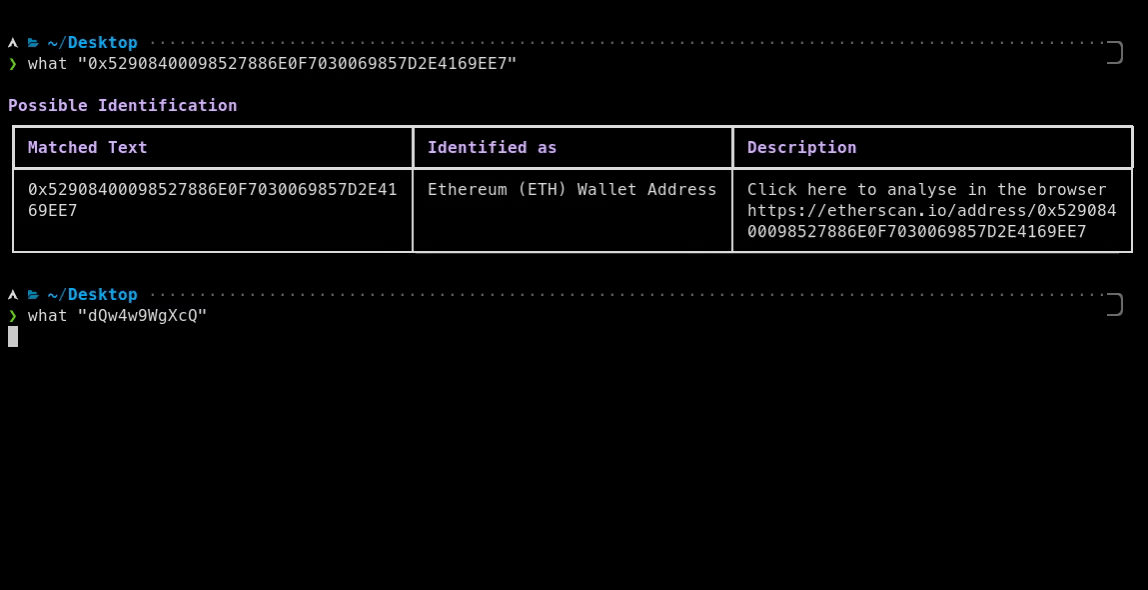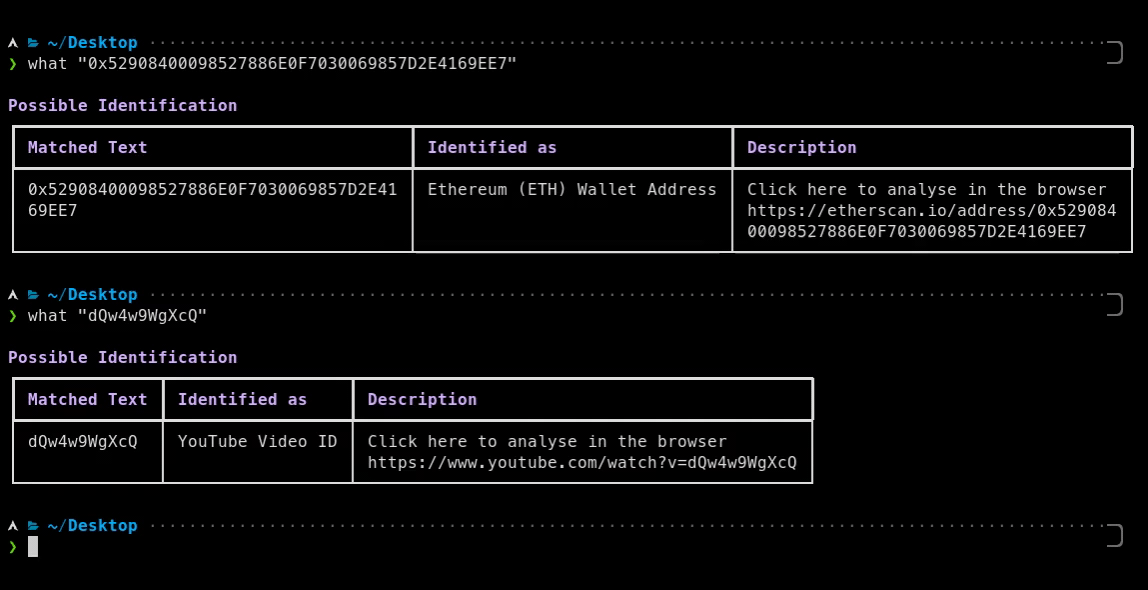 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 retirejs/retire.js
scanner detecting the use of JavaScript libraries with known vulnerabilities. Can also generate an SBOM of the libraries it finds.
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform
 jasonxtn/argus
The Ultimate Information Gathering Toolkit
 urbanadventurer/whatweb
Next generation web scanner
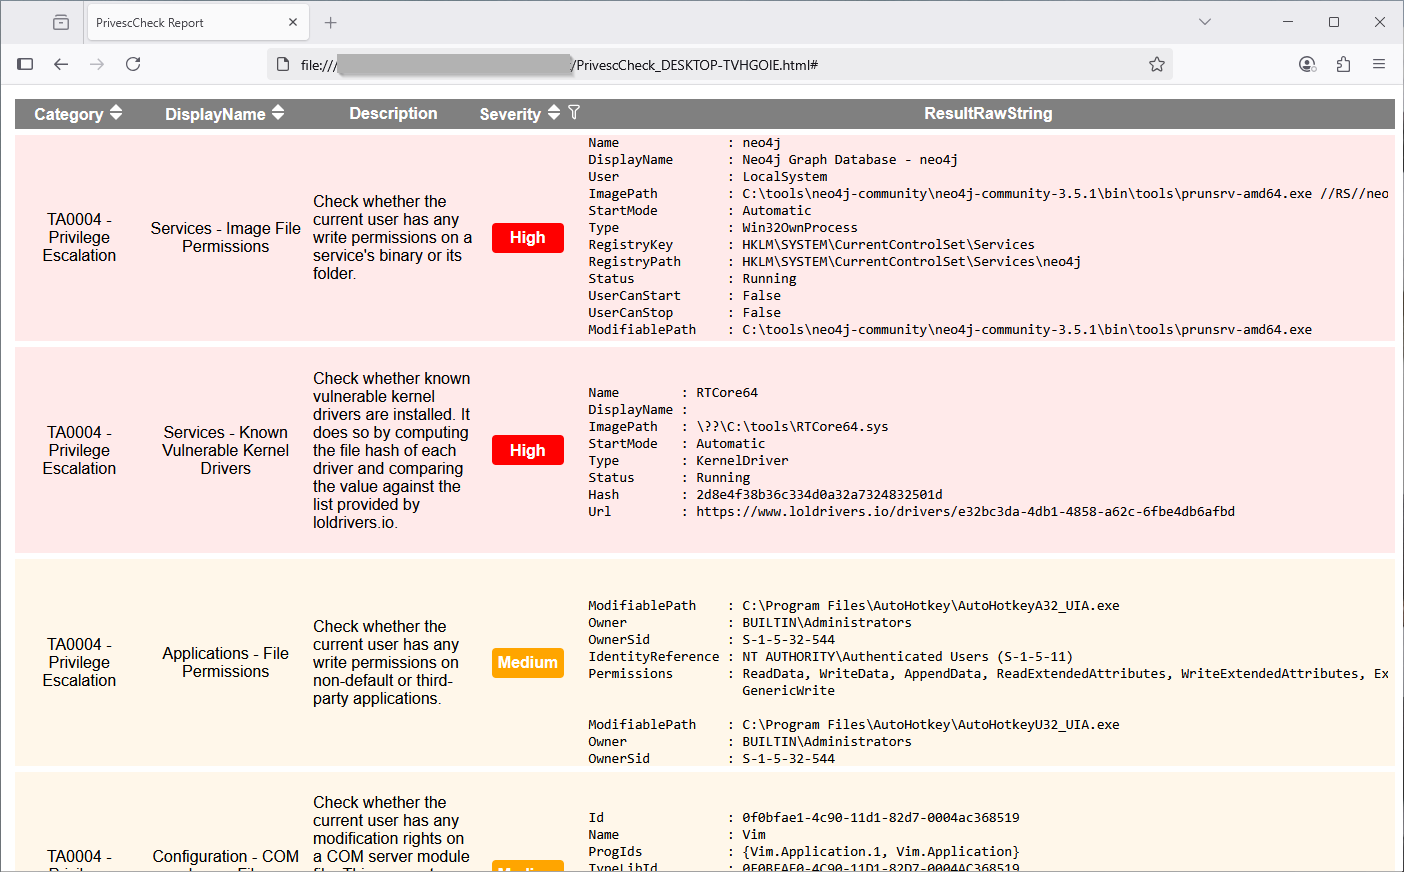 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
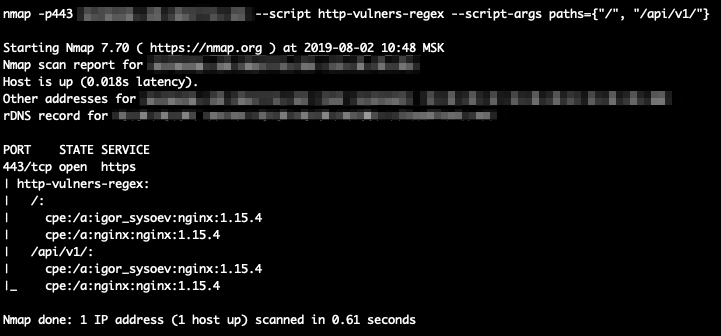 vulnerscom/nmap-vulners
Nmap NSE script that queries the Vulners API to identify known vulnerabilities (CVEs) for detected network services, enhancing standard port scanning…
 lefayjey/linwinpwn
Bash script wrapping Active Directory tools for automated enumeration, vulnerability checks, exploitation, and password dumping via LDAP, RPC,…
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 cmu-sei/pharos
Automated static analysis tools for binary programs








