
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/secureml
SecureML - Securing and Watermarking AL models
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 logpresso/cve-2021-44228-scanner
Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
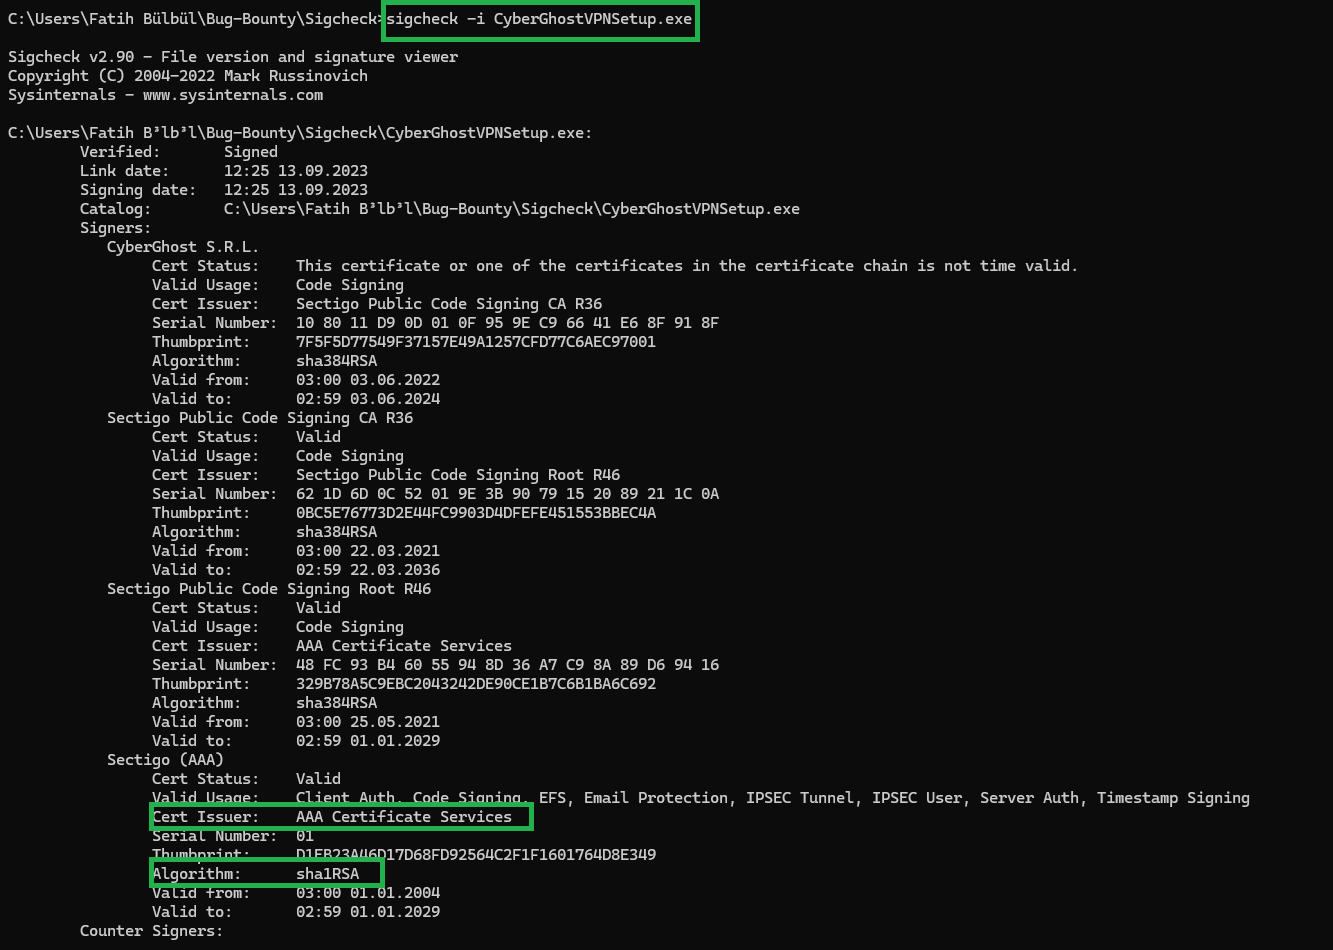 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
 nanopathi/external_expat_aosp10_r33_cve-2022-22822tocve-2022-22827
Patched version of the Expat XML parser library addressing multiple CVEs (CVE-2022-22822 through CVE-2022-22827) for AOSP 10 r33, providing…
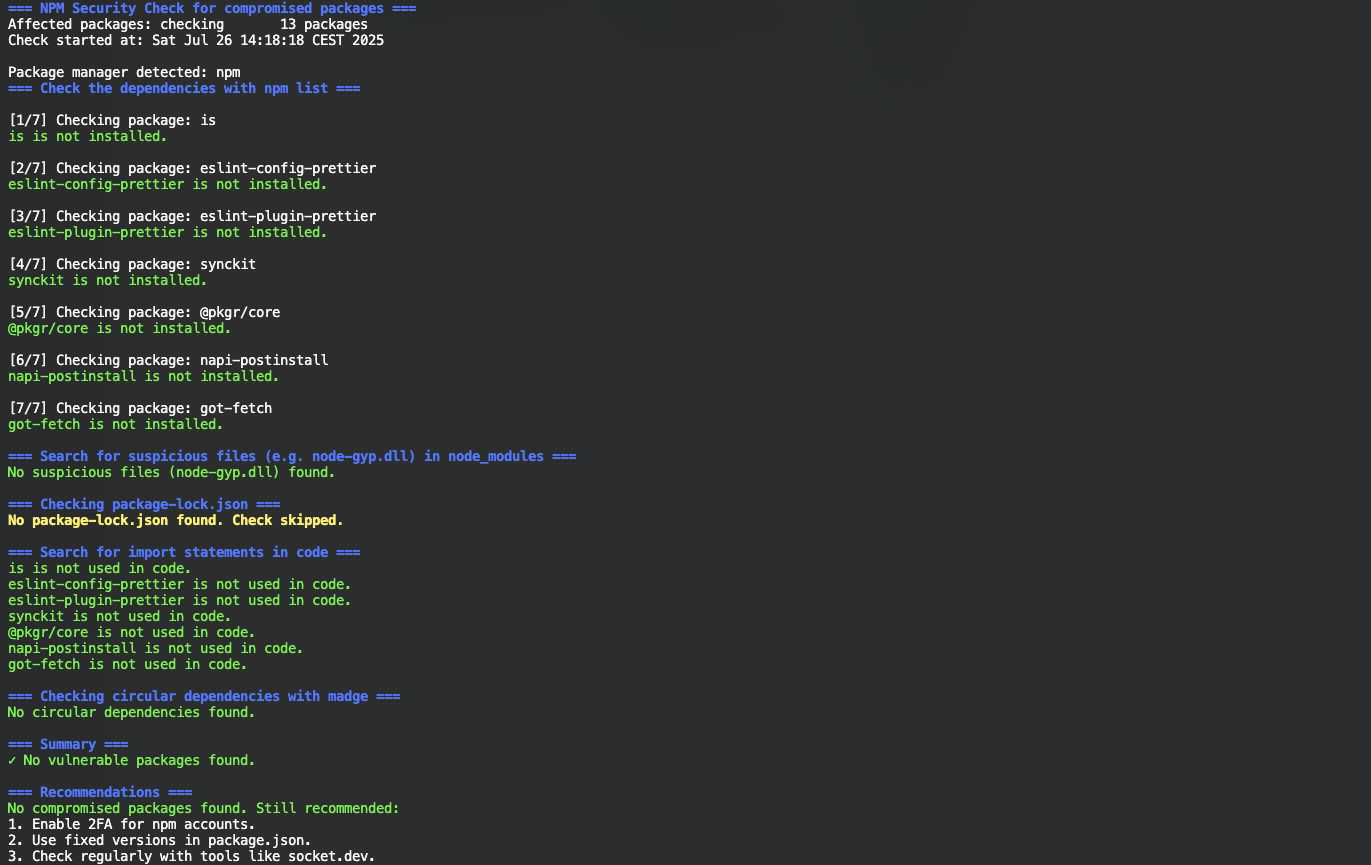 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 nxgn-kd01/react2shell-scanner
Detect CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Fast, accurate scanner with zero false positives.
 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
 putget/cve-2024-38526
CVE-2024-38526 - Polyfill Scanner
 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094








