
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended
 cellebrite-labs/pplorer
IDA plugin that resolves PPL calls to the actual underlying PPL function.
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 n7on/dllspy
Discover input surfaces and security issues in compiled .NET assemblies — without running them.
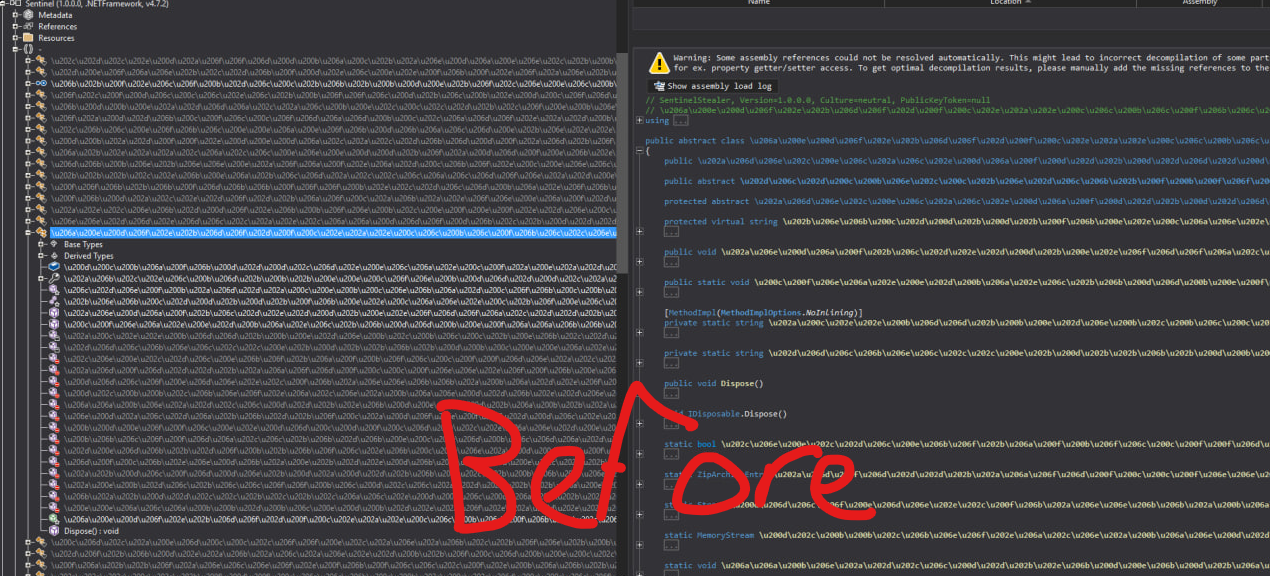 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 ga1ois/blackhat-europe-2022
Select Bugs From Binary Where Pattern Like CVE-1337-Days
 emicoecommerce/magento-apsb22-48-security-patches
This repository contains potential security patches for the Magento APSB22-48 and CVE-2022-35698 security vulnerability
 hackinglz/svg_phishing_tools
SVG Analysis and generation tools for commonly seen SVG attachment phishing
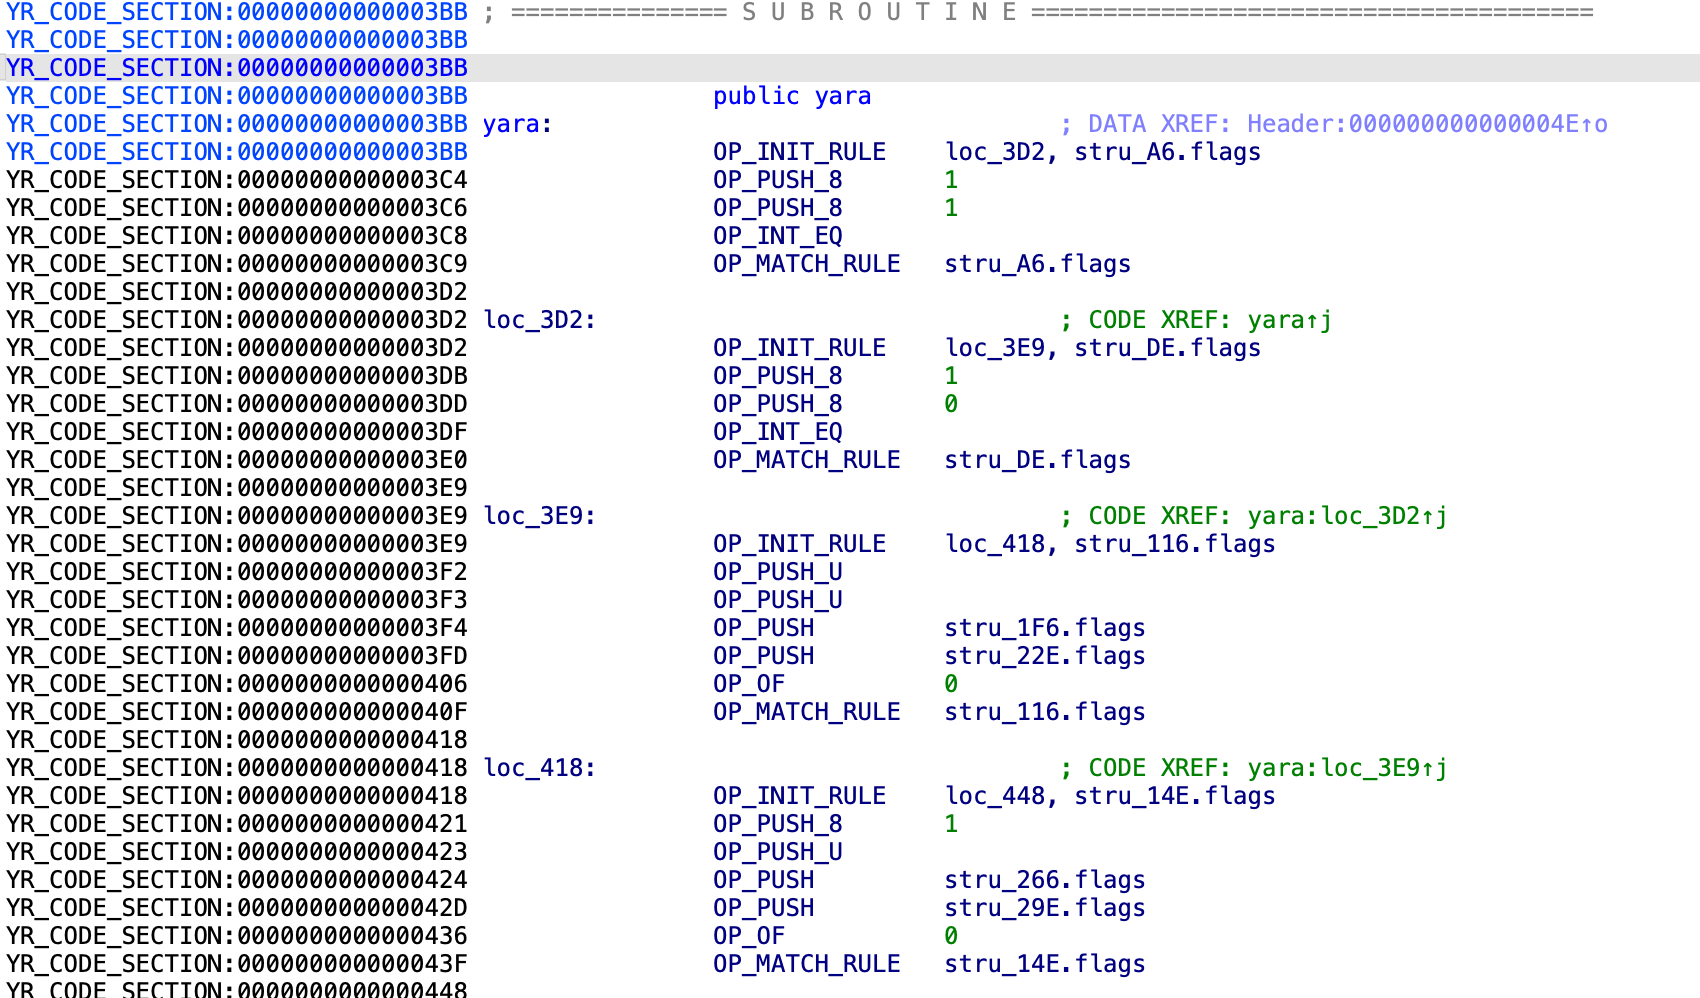 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 dr4k0nia/tooling-playground
A collection of small scripts and tools for deobfuscation and malware analysis.
 mucoze/umay
IoT Malware Similarity Analysis Platform
 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
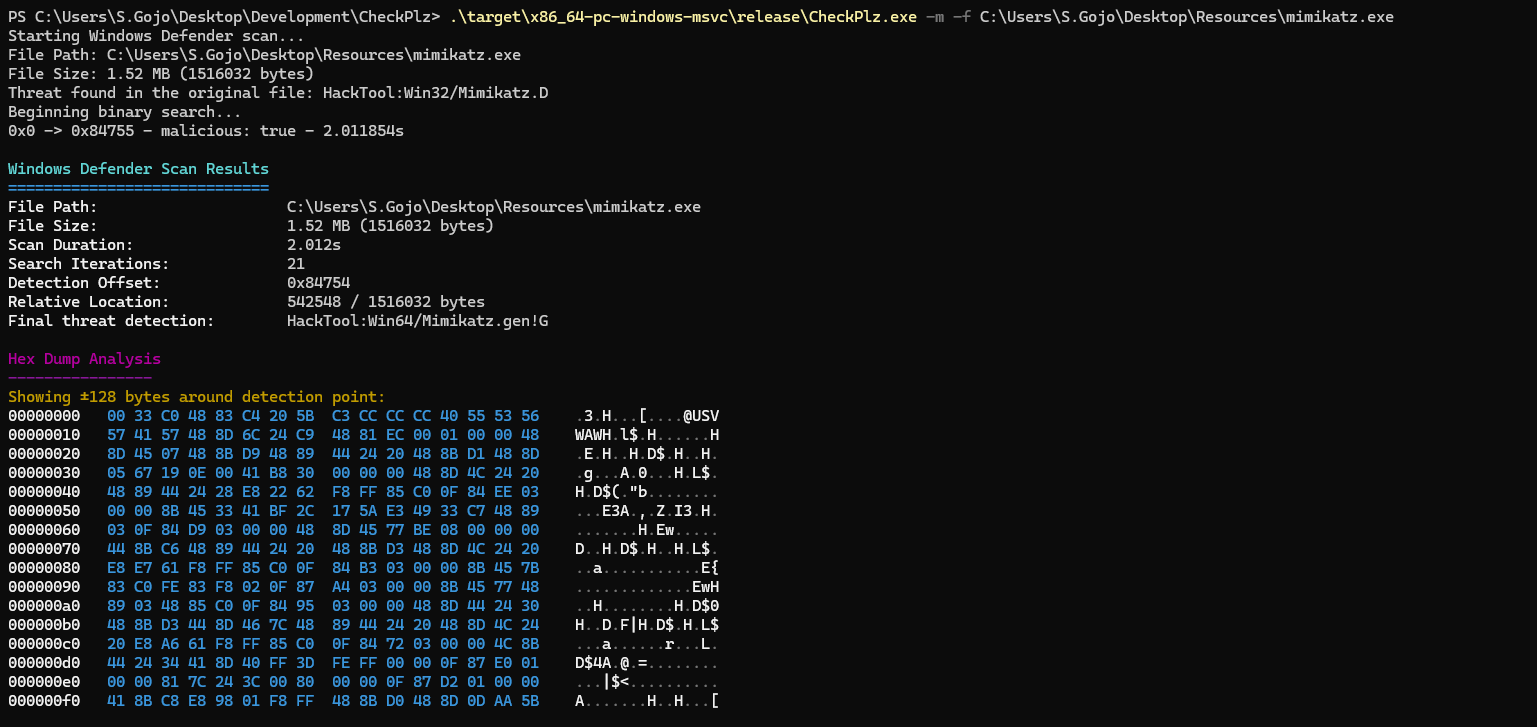 blacksnufkin/checkplz
Scan files for potential threats while leveraging AMSI (Antimalware Scan Interface) and Windows Defender. By isolating malicious content.
 reverserid/jurig
a fully autonomous AI agent for reverse engineering








