
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 sslmate/go-pkcs12
Go library for encoding and decoding PKCS#12 files
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
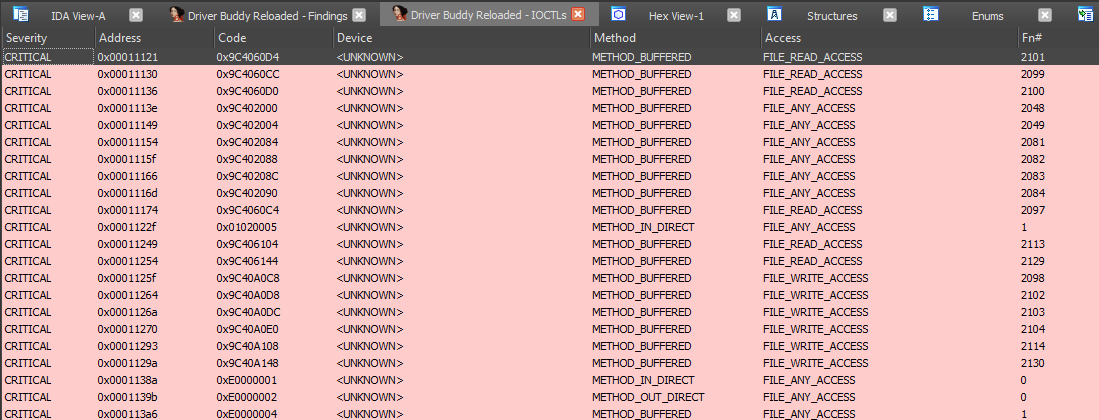 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
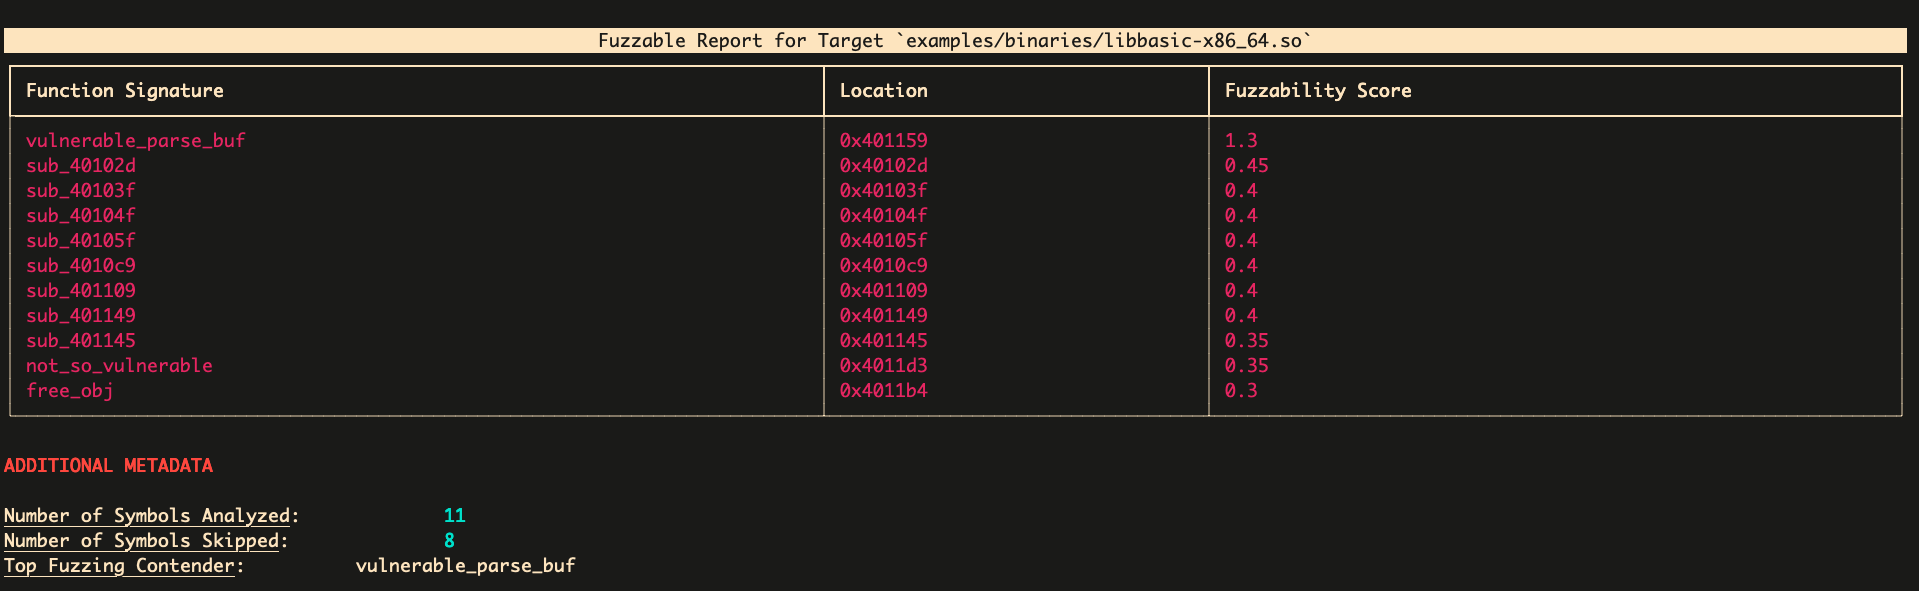 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 check-spelling/check-spelling
Spelling checker action to check spelling in repositories / pull requests / commits
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
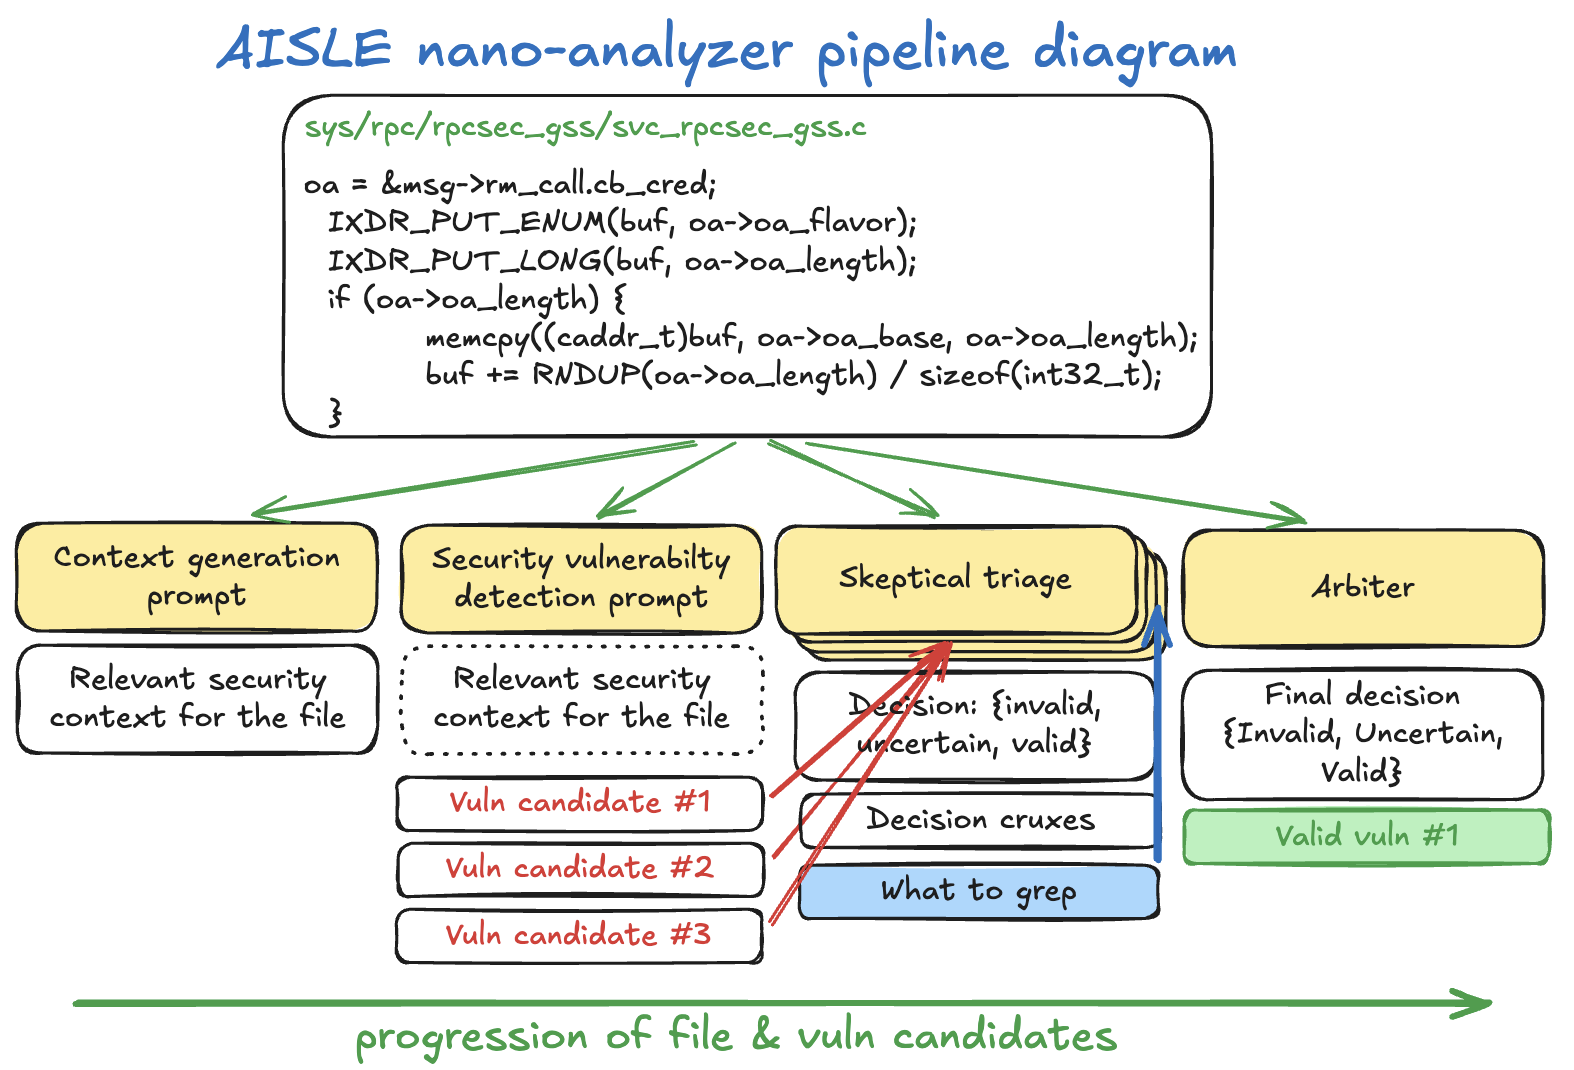 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
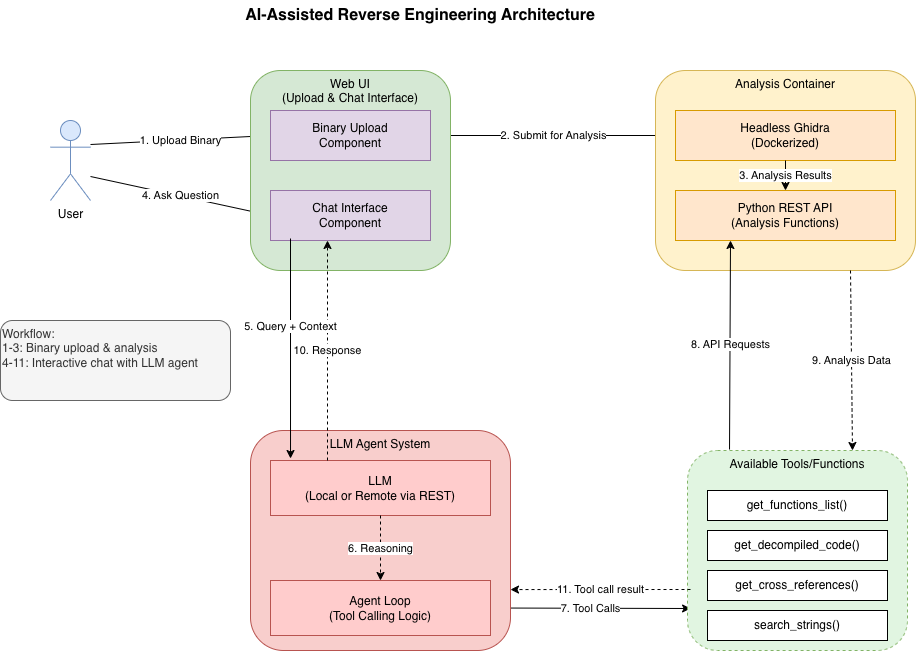 biniamf/ai-reverse-engineering
AI-Assisted Reverse Engineering with Ghidra
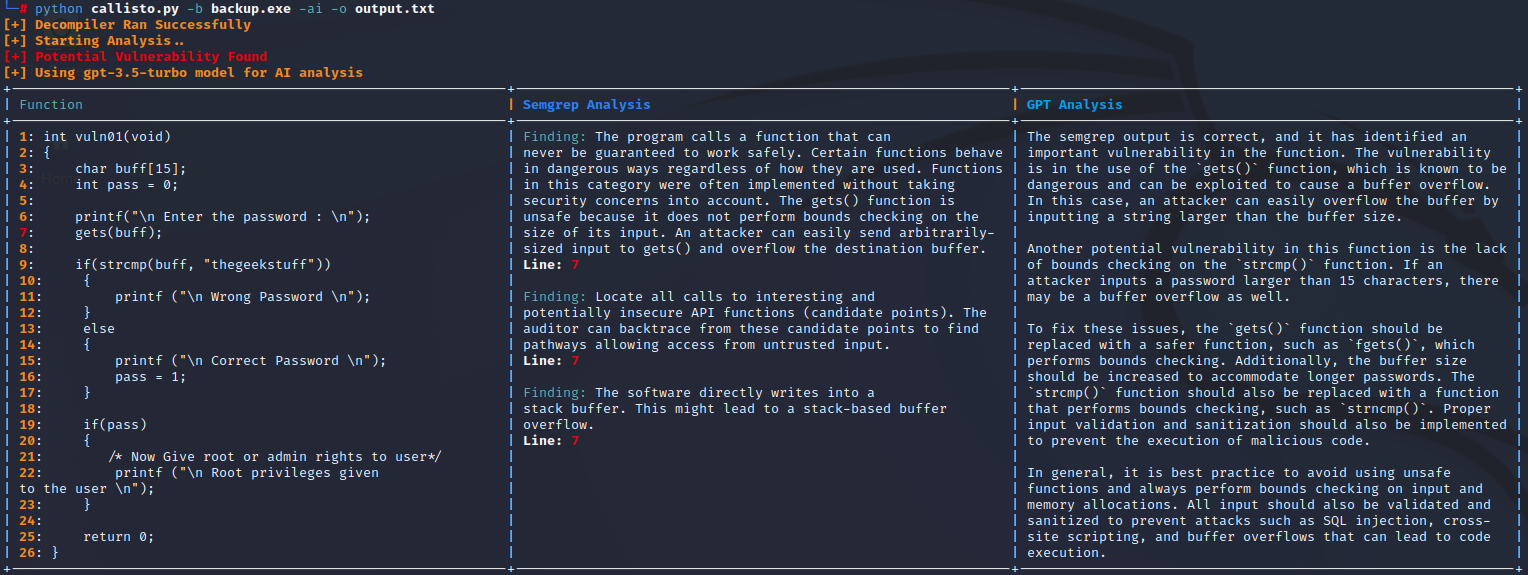 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
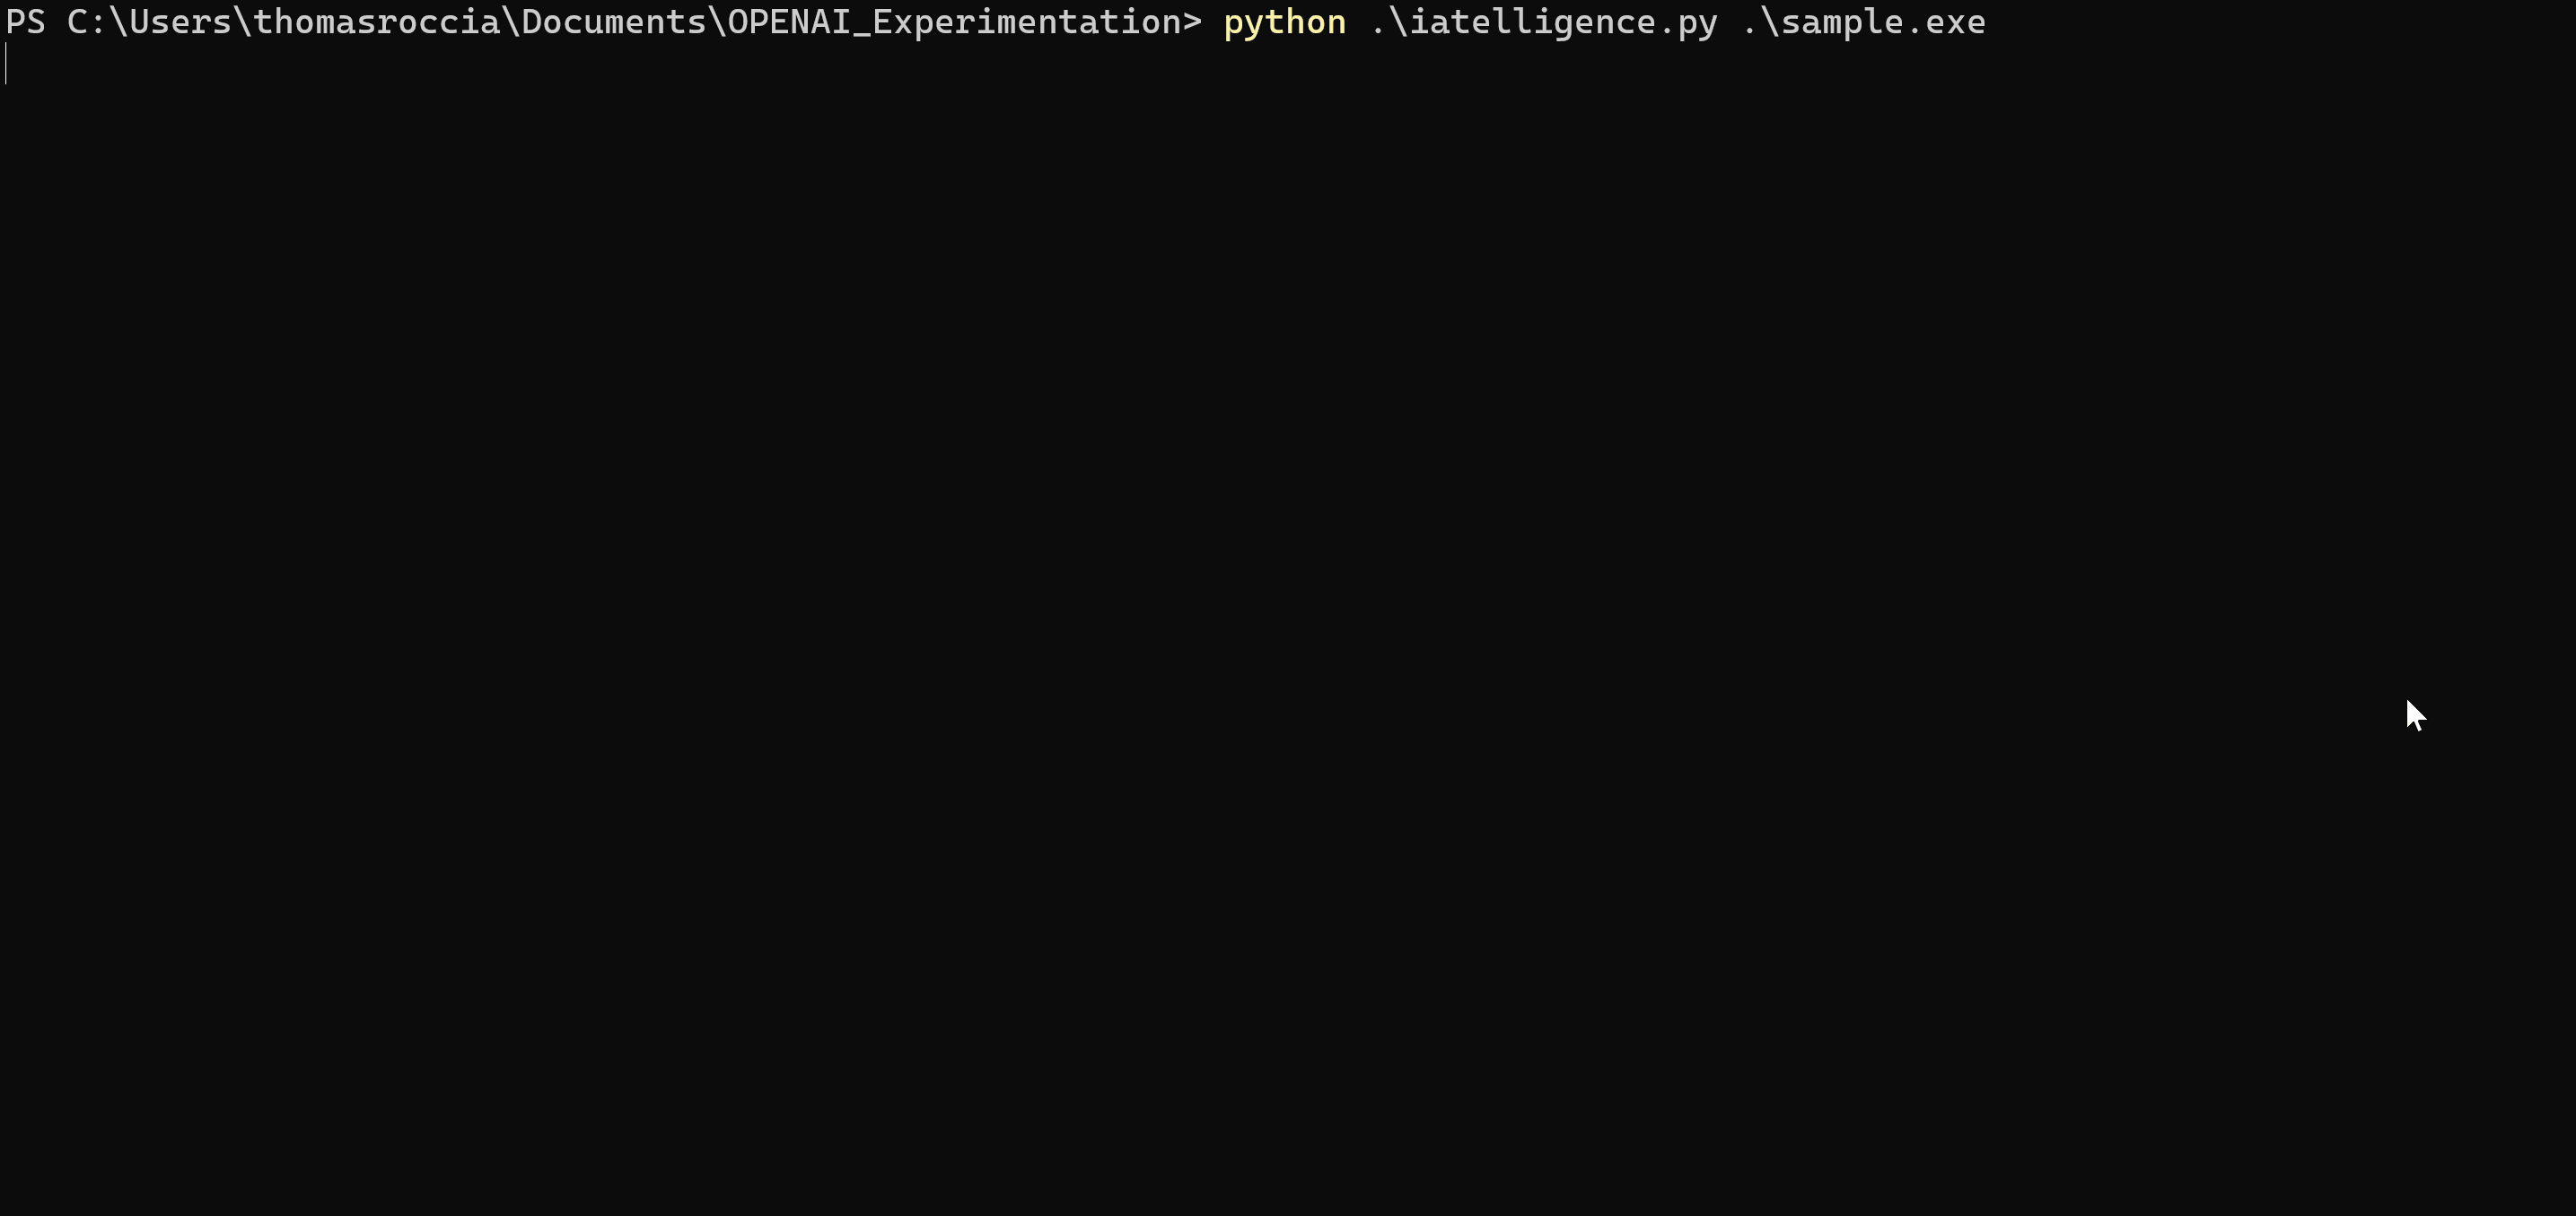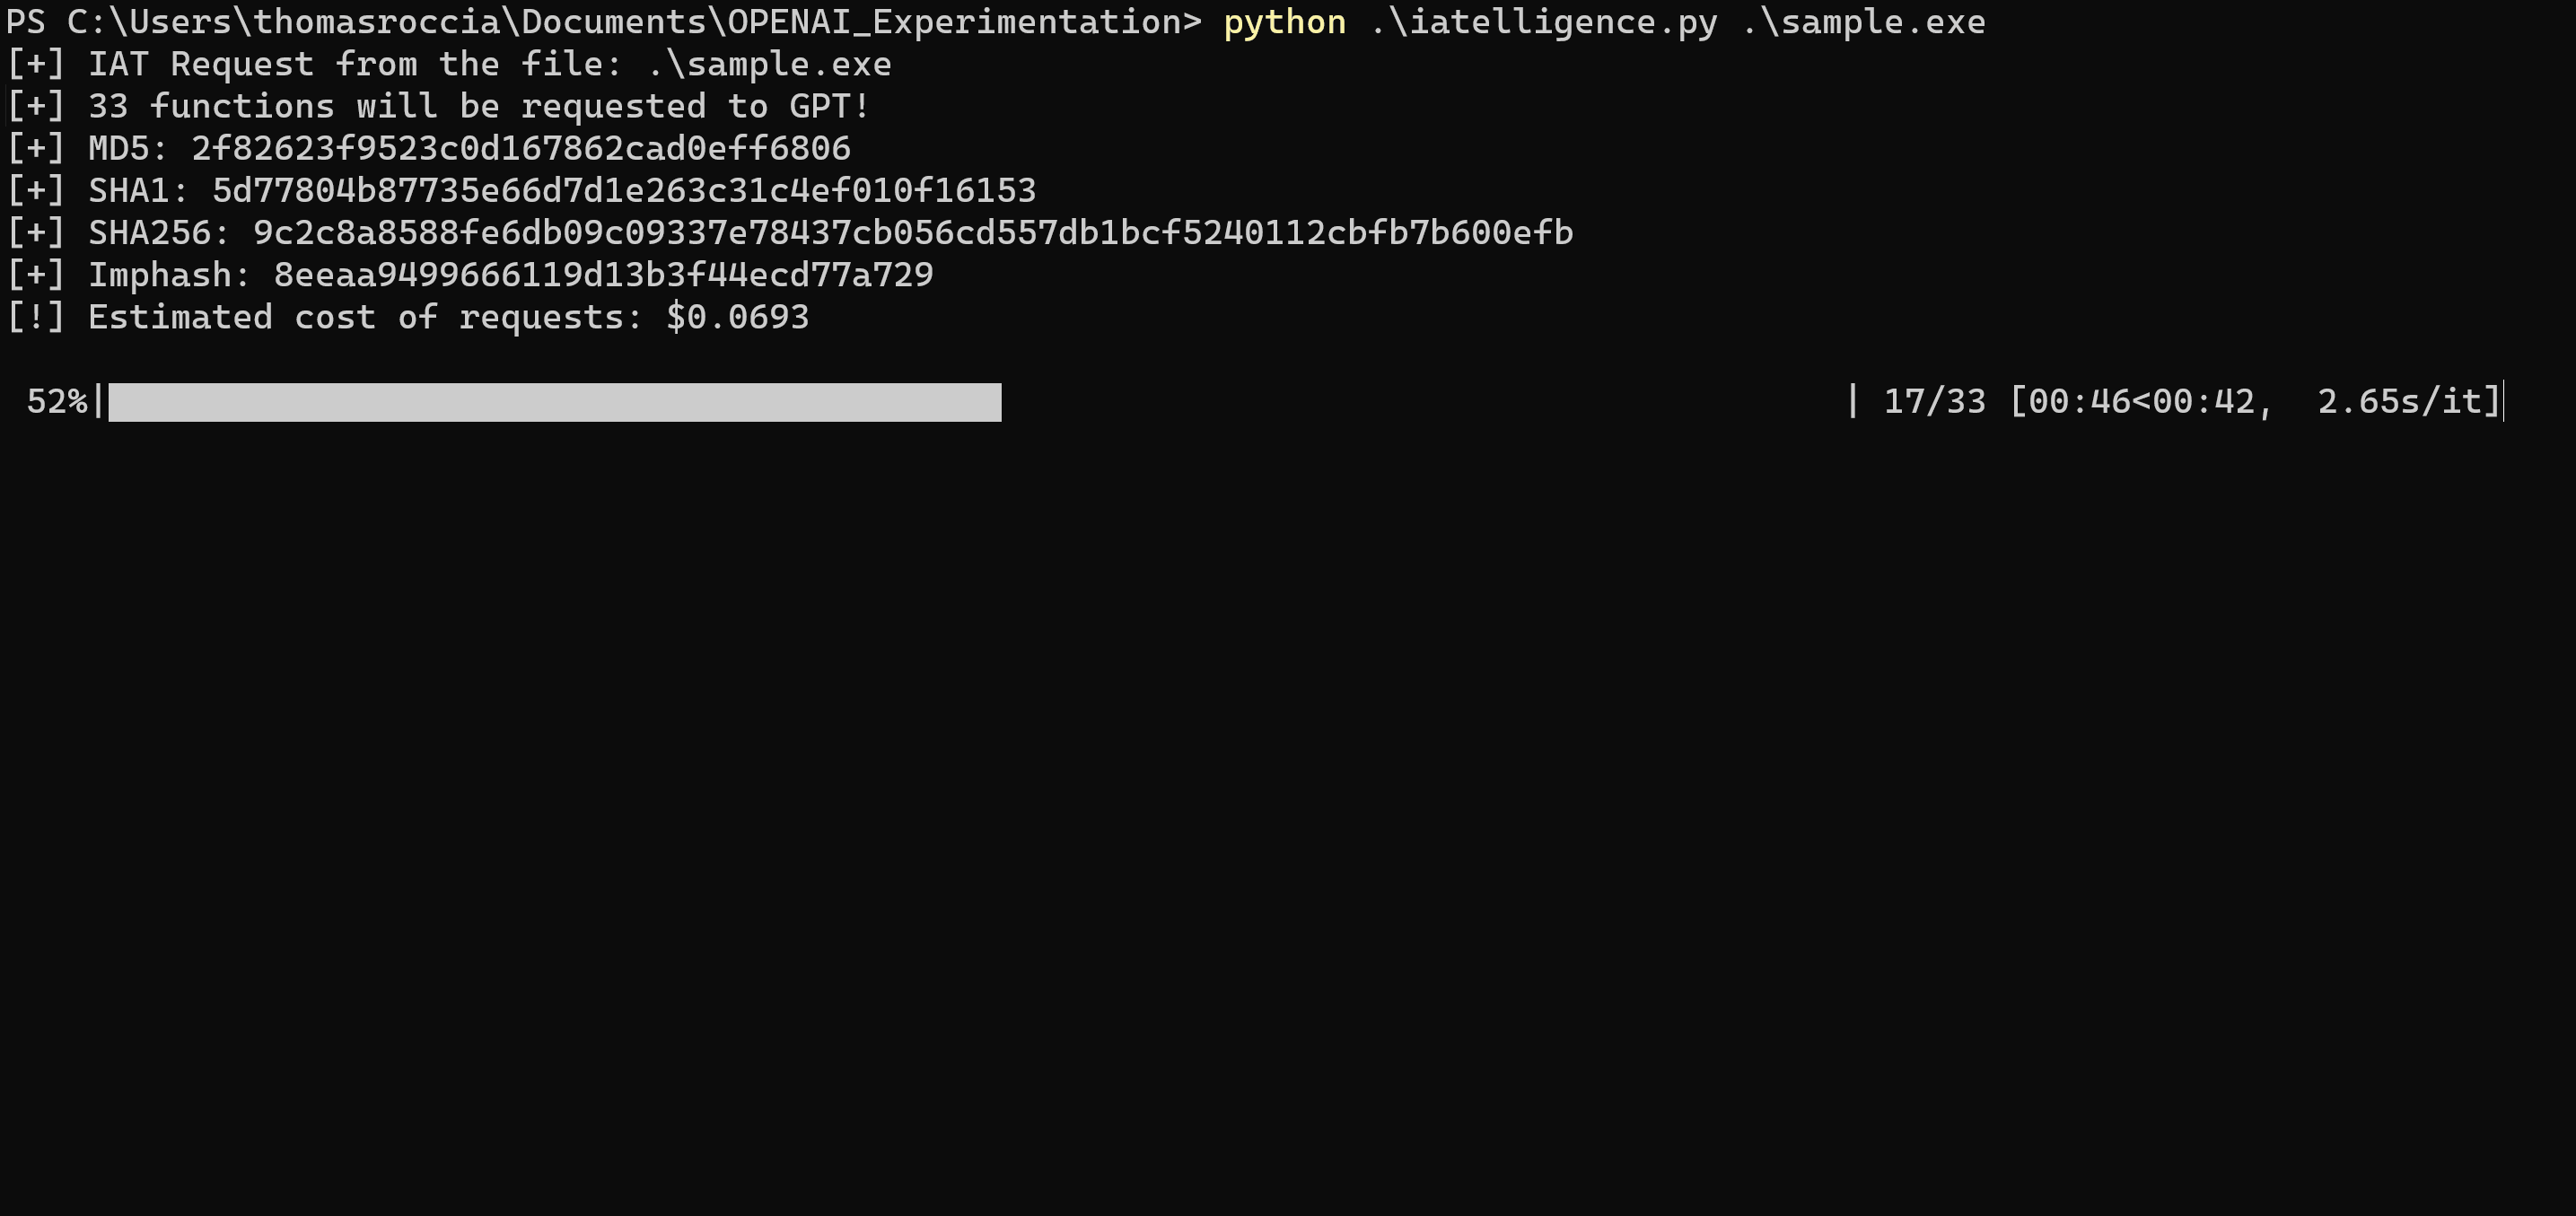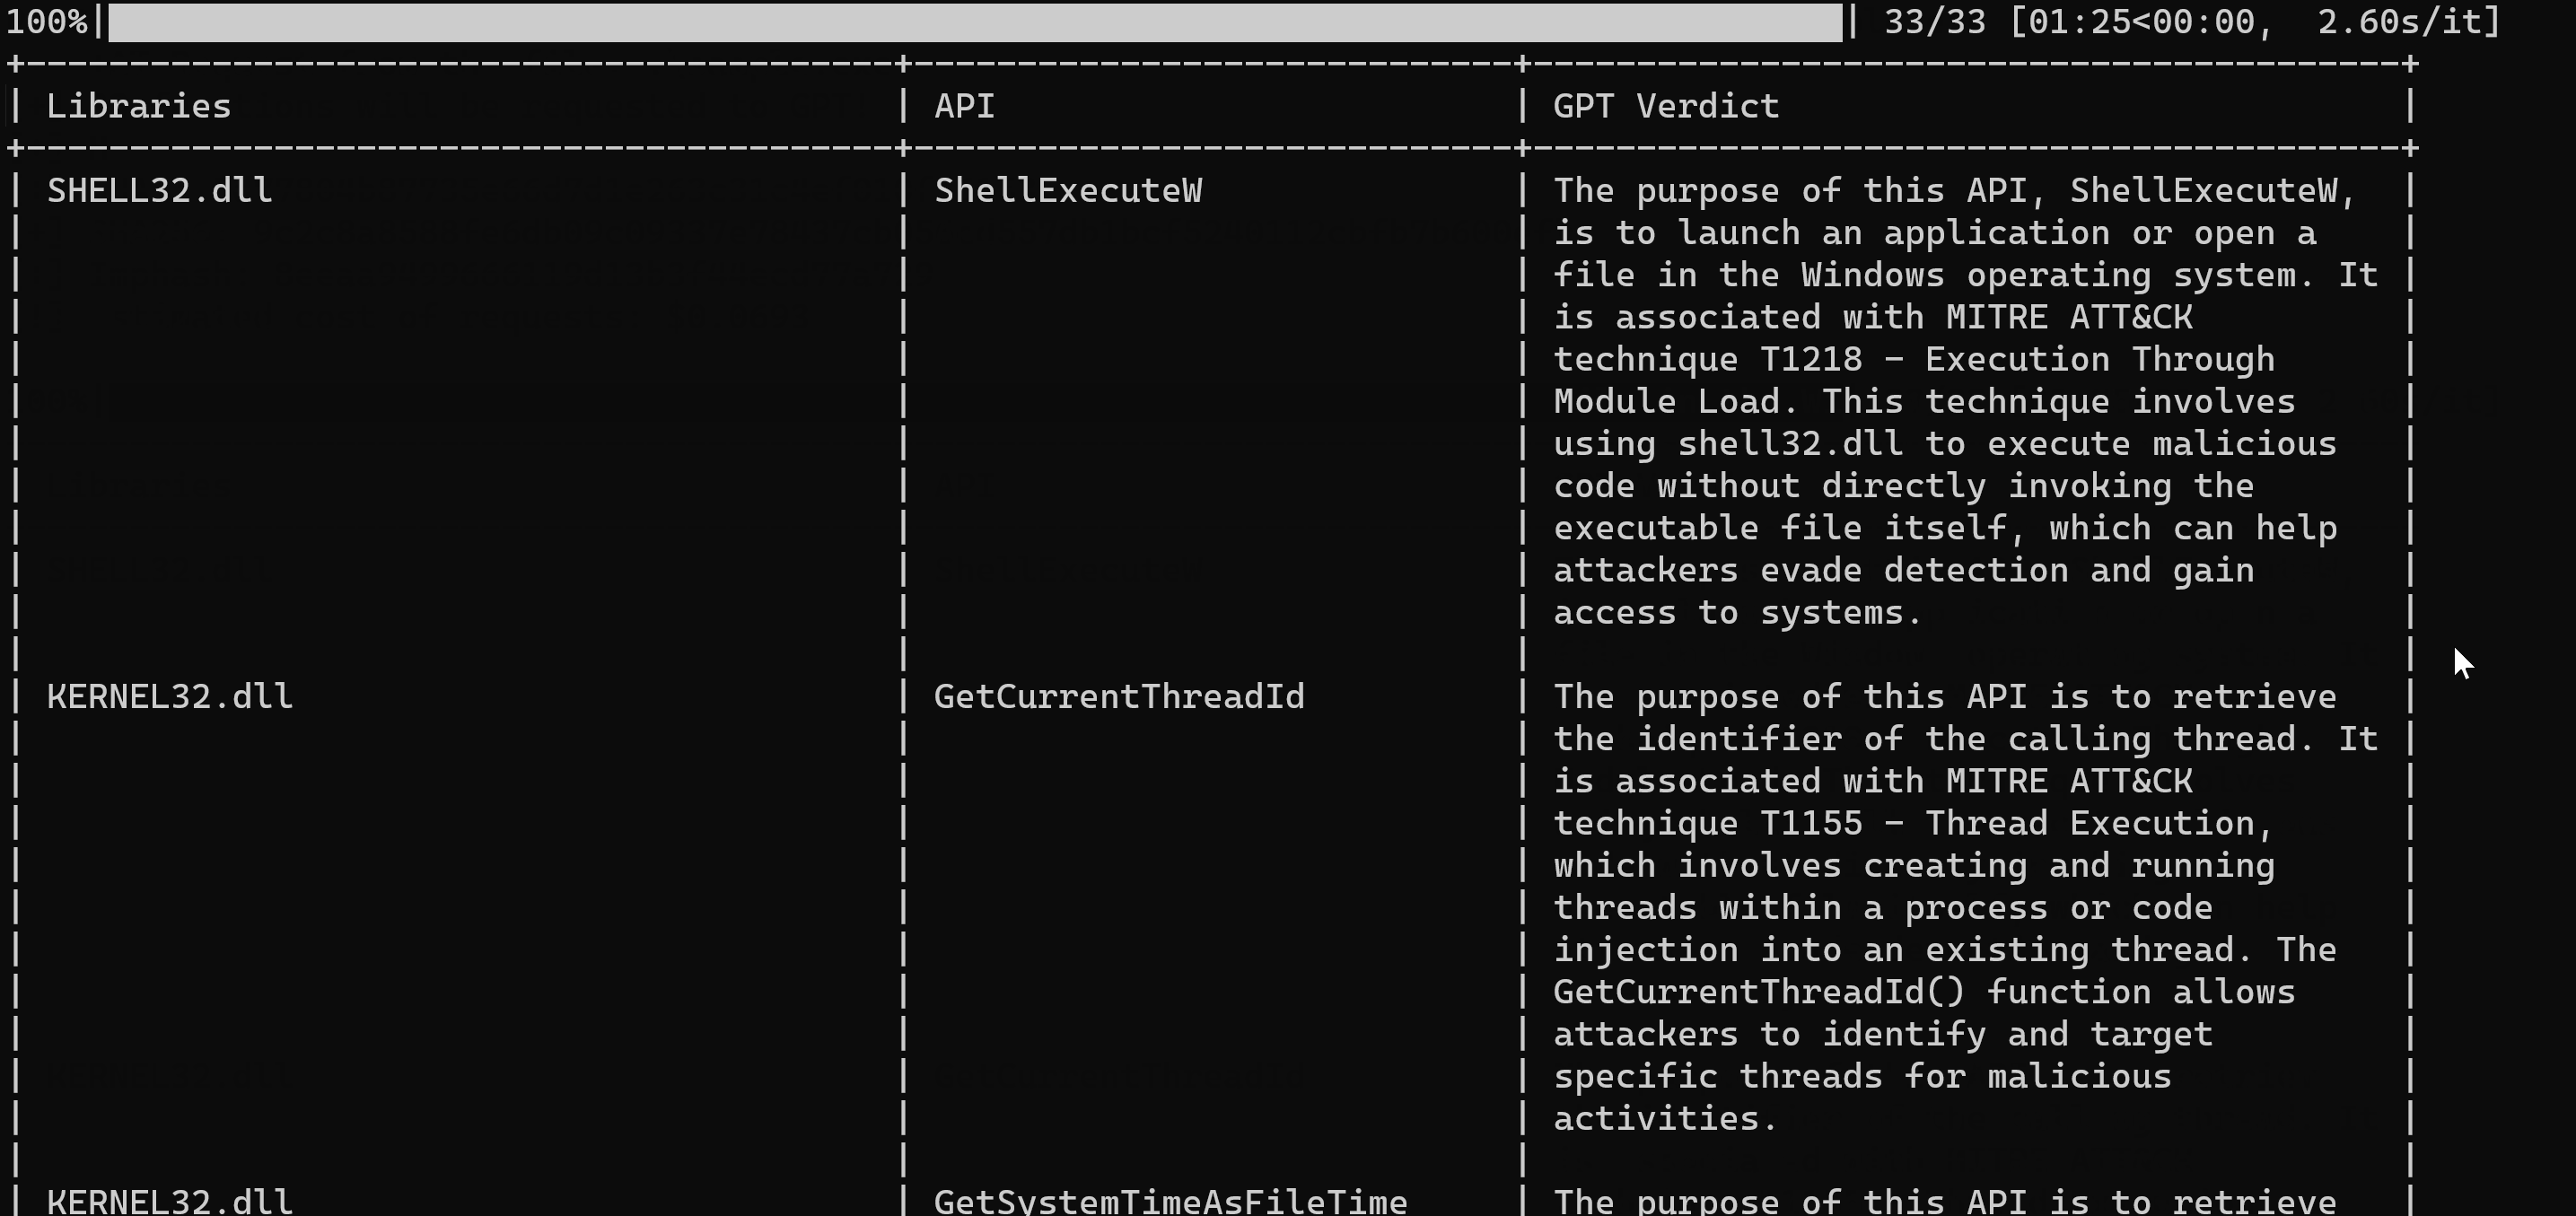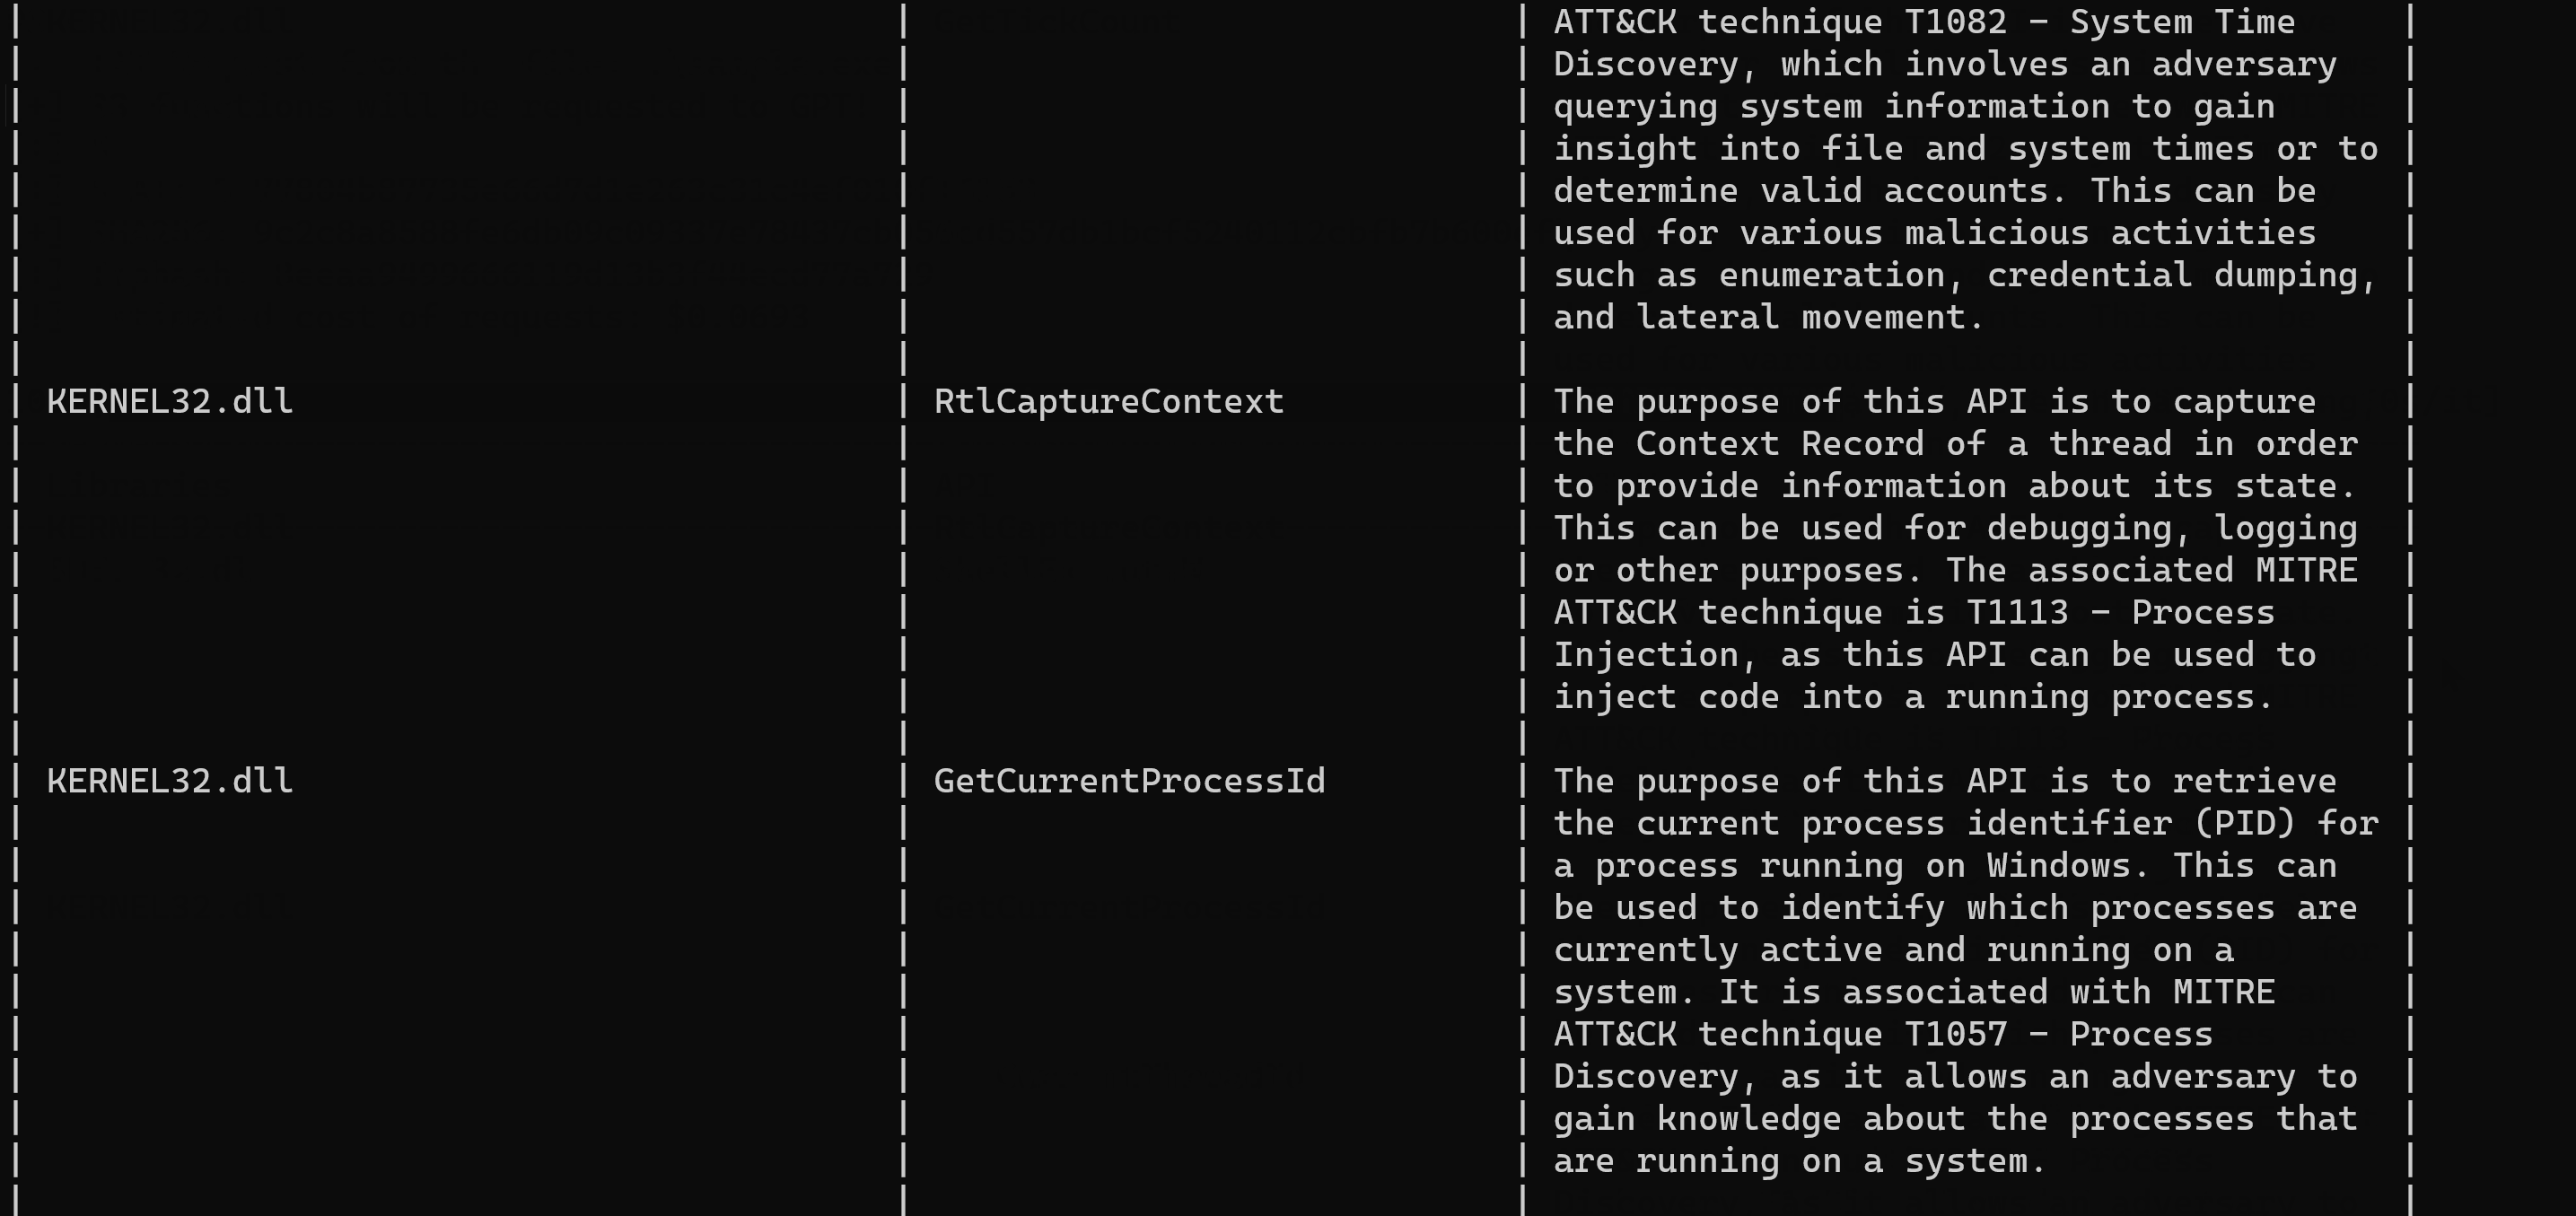 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
 netspooky/inhale
A malware analysis and classification tool.
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…








