#1
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
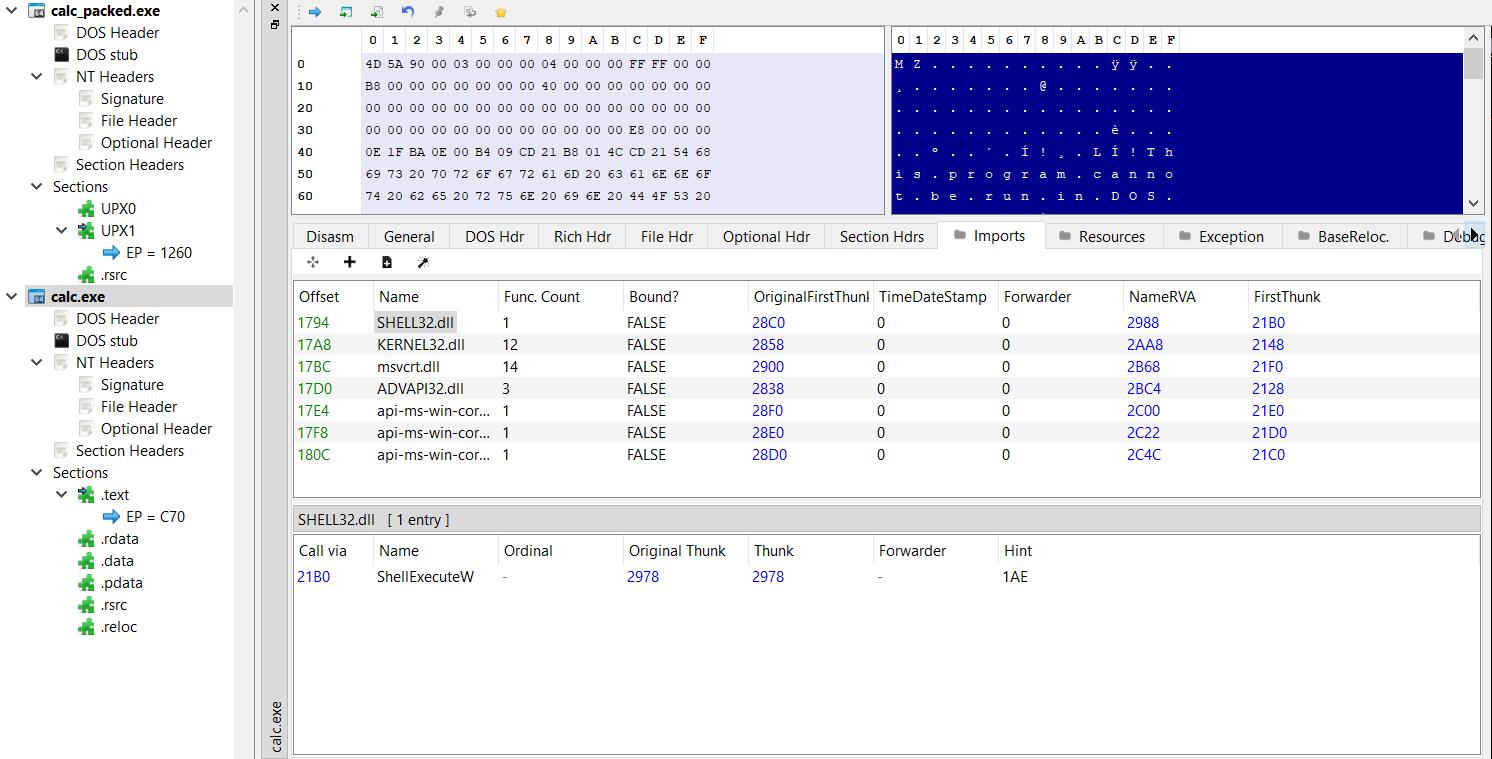 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.