
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Reverse Engineering — Page 75 | Kitploit
Categories

Reverse Engineering

Tools for decompiling, disassembling, and understanding malware internals and complex binaries.

Kitploit recommended
Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1 day ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k0 days ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k1 month ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k3 months ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k2 days ago
ImHex preview#6

ImHex

GitHubwerwolv/imhex
54.4k23 days ago
angr preview#7

angr

GitHubangr/angr
9.0k0 days ago
unicorn preview#8

unicorn

GitHubunicorn-engine/unicorn
9.2k8 months ago
capstone preview#9

capstone

GitHubcapstone-engine/capstone
8.9k7 days ago
keystone preview#10

keystone

GitHubkeystone-engine/keystone
2.7k3 months ago
NewestRelevanceMost popularRecently updated
1827 results
CVE-2020-0041-Pixel-3a preview

CVE-2020-0041-Pixel-3a

GitHubvaginessa/cve-2020-0041-pixel-3a

Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)
android-securityprivilege-escalationvulnerability-analysis+3
85 years ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
reverse-engineeringforensicsinformation-gathering+6
53 months ago
CVE-2026-32202 preview

CVE-2026-32202

GitHubvirus-or-not/cve-2026-32202

Generates LNK files with crafted _IDCONTROLW structures to research Windows Shell spoofing vulnerabilities CVE-2026-21510 and CVE-2026-32202,…
vulnerability-analysisexploitationreverse-engineering+2
86 months ago
cve-2026-28912 preview

cve-2026-28912

GitHubjvidhan/cve-2026-28912

Reverse engineering notes and a working PoC for the macOS PackageKit symlink-following bug (CVE-2026-28912), with disassembly diff of the 26.6 fix.
privilege-escalationstatic-analysisvulnerability-analysis+5
21 month ago
ghidra-mtk-loader preview

ghidra-mtk-loader

GitHubnccgroup/ghidra-mtk-loader

Ghidra loader for the MediaTek md1img modem firmware image format
embedded-systems-securityiot-securityreverse-engineering+3
45 months ago
nanocore_extractor preview

nanocore_extractor

GitHubjacobpimental/nanocore_extractor

Extracts nanocore sample from compile AutoIT script
dynamic-analysis-sandboxingreverse-engineeringforensics+2
67 years ago
cve-2026-1668-poc preview

cve-2026-1668-poc

GitHubwuyou6956-glitch/cve-2026-1668-poc

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
embedded-systems-securityiot-securityvulnerability-analysis+6
6 months ago
PixelSmash preview

PixelSmash

GitHubse1ims/pixelsmash

Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
memory-forensicsvulnerability-analysisexploitation+6
1 month ago
cve-2026-43687 preview

cve-2026-43687

GitHubjvidhan/cve-2026-43687

Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…

memory-forensicsvulnerability-analysisexploitation+4
1 month ago
secbox preview

secbox

GitHubyv1ing/secbox

Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
network-mappingvulnerability-analysismobile-app-pentesting+9
17 days ago
CVE-2019-11707-from-an-IonMonkey-type-confusion-to-SYSTEM- preview

CVE-2019-11707-from-an-IonMonkey-type-confusion-to-SYSTEM-

GitHubg4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

privilege-escalationvulnerability-analysisexploitation+6
22 days ago
CVE-2026-0006-step-2 preview

CVE-2026-0006-step-2

GitHubr3n3r0/cve-2026-0006-step-2

Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
android-securitymemory-forensicsexploitation+5
11 days ago
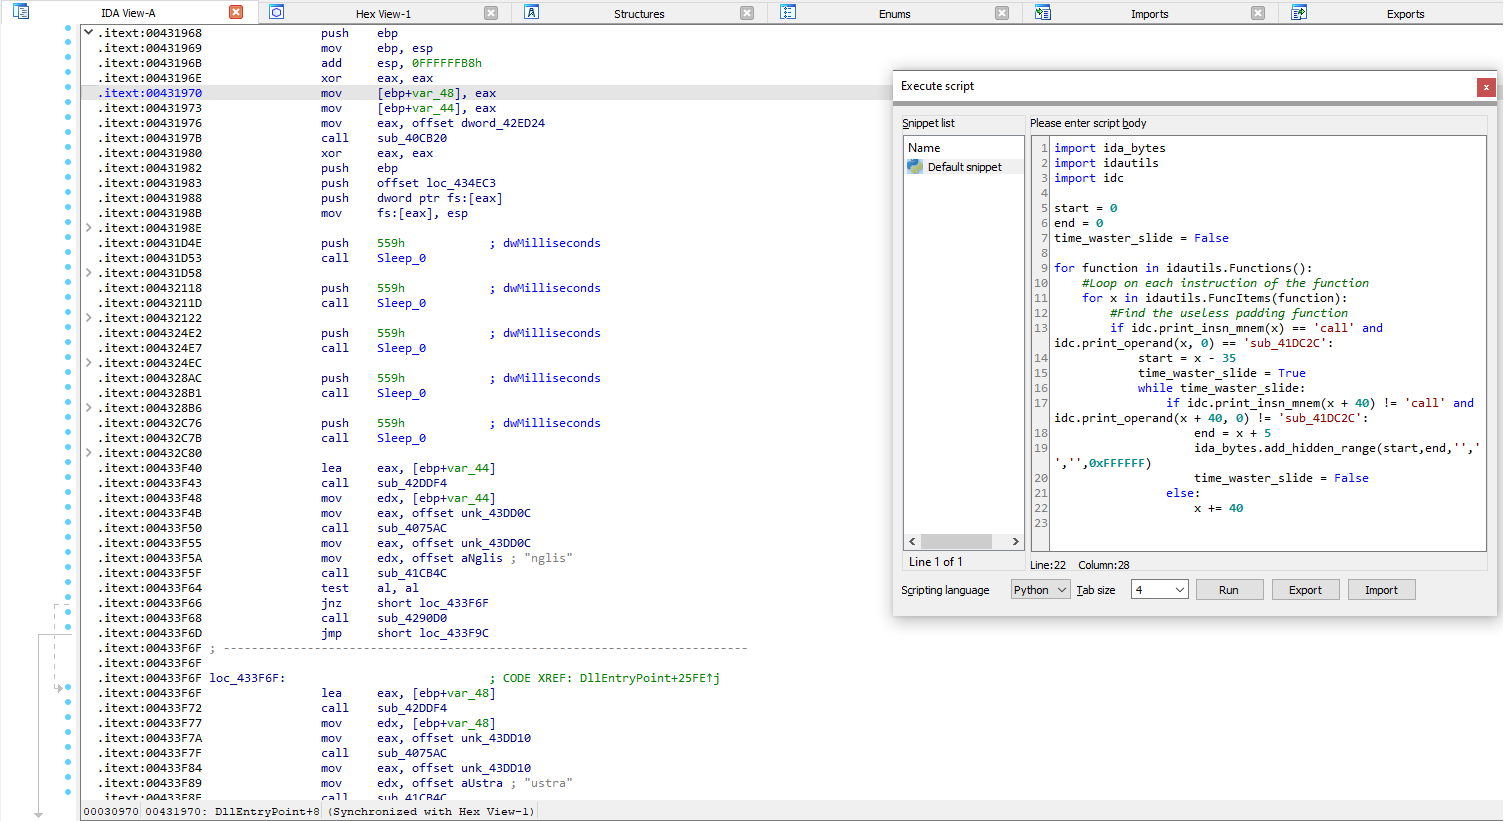
astaroth-deobfuscator preview

astaroth-deobfuscator

GitHubdodo-sec/astaroth-deobfuscator

IDA python script for deobfuscating Astaroth/Guildma injector DLL
static-analysisreverse-engineeringmalware-analysis+1
83 years ago
USB Spy preview

USB Spy

GitLabchristophe.duvernois/usb-spy

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
vulnerability-analysisexploitationreverse-engineering+6
33 months ago
rizin-notebook preview

rizin-notebook

GitHubindalok/rizin-notebook

A notebook where to writes notes while using Rizin & Cutter!
reverse-engineeringscripting-automationdebuggers+3
76 months ago
Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis preview

Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis

GitHubkaandemir993/agent-tesla-apc-injection-token-manipulation-registry-persistence-analysis

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…
privilege-escalationpersistence-mechanismsreverse-engineering+4
32 months ago
vbox-lsilogic-sas-config preview

vbox-lsilogic-sas-config

GitHubabraxas/vbox-lsilogic-sas-config

VirtualBox 7.2.20 - Critical - Local - Type confusion / arb R/W - SAS1068 CONFIG SCSI-SPI overlay
memory-forensicsvulnerability-analysisexploitation+4
3 days ago
s9180-rootmygalaxy preview

s9180-rootmygalaxy

GitHubdeancyl/s9180-rootmygalaxy

RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox


android-securityprivilege-escalationpersistence-mechanisms+5
24 days ago
Previous1…747576…100Next








