
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended

 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 xcracker000/cve-2024-56426
CVE-2024-56426 Exynos9830 Bootrom Exploit - SM-G985F
 turretsec/disclosure-thinkware-u3000
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 rizinorg/rizin-notebook
A notebook where to writes notes while using rizin!
 cyber-defence-campus/netgear_r6700v3_circled
Demonstrate some functionalities of Morion by generating an exploit for CVE-2022-27646 (stack buffer overflow on Netgear R6700v3 routers).
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 tekkenbugattii/linusware-source-code-internal
Reverse-engineered runtime engine for Roblox/Luau with VM hooking, opcode remapping, capability escalation, and UNC script environment for executing…
 mutur4/unisocbootroms
This is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694
 spiralbl0ck/cve-2022-3653
CVE-2022-3653 just the c++ component in Vulkan for later study
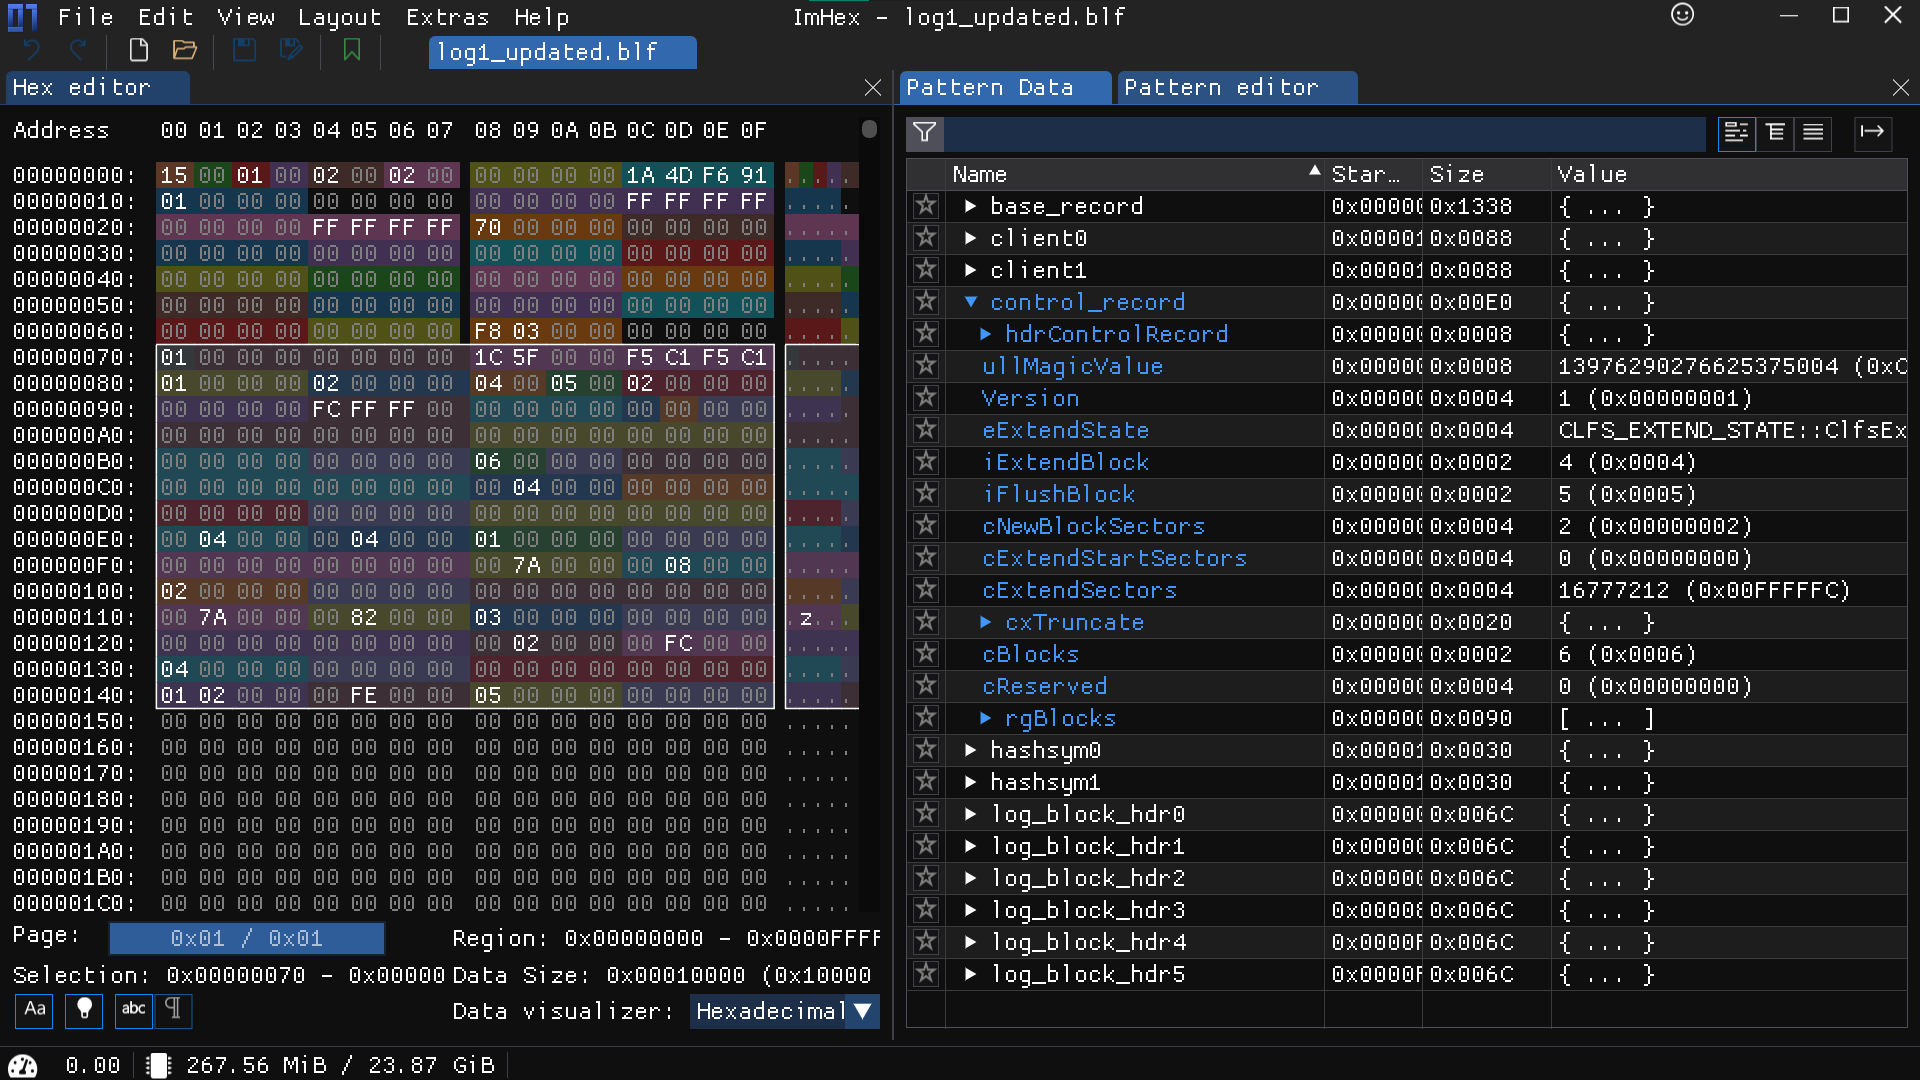 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 rohitberiwala/cve-2024-23222-coruna-exploit-kit-deobfuscated
Comprehensive deobfuscated research of the Coruna iOS exploit kit targeting CVE-2024-23222. Analysis of WebKit Type Confusion, PAC Bypass, and…








